GitGuardian is an end-to-end NHI security platform designed to help organizations strengthen their Non-Human Identity (NHI) security posture and address compliance standards and regulations. As attackers increasingly target NHIs, such as service accounts, service principals, and applications, protecting and managing these critical assets has become paramount. NHIs rely on “secrets” like API keys and certificates for authentication, and their rapid proliferation has led to significant…
$0
(for individuals or up to 25 devs)
Jitterbit
Score9.4 out of 10
N/A
Jitterbit is a cloud integration technology for cloud, social or mobile apps. It provides accessibility for
non-technical users, including easily creating API’s and data transformation scripts within the
integrations.
I do think it'll absolutely fit everyone who codes integrates with another platform or services. We all forget that one credentials one in a while, and especially those who managed public repository, it is important to keep an eye on accidentally committed credentials. While I think you don't really needs it for personal project, it's a nice to have, you don't want to waie up to 50k USD of sudden surcharge on resources you don't use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
This is a great tool for bringing data out of your locked, internal systems and getting it into the cloud. It meshes well with Salesforce and is fairly easy to use, helping the transition from other older, more complex tools into a more modern environment. It has lots of competition in this space and some are better than others, but if your data is straight forward and you know it well, Jitterbit will get the job done. If you are not as close or comfortable with your data and need to do some wildly complex migrations, there might be better packages out there for you.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
GitGuardian monitors every public or private GitHub commit ( that have GitGuardian installed) and event in real-time for secrets and sensitive data. In a leak scenario it immediately notifies us.
It uses sophisticated pattern matching techniques to detect credentials that cannot be strictly defined with a distinctive pattern (like unprefixed credentials)
It covers several API providers, database connection strings, private keys, certificates, usernames and passwords etc
GitGuardian have high True Positive Rate of around 91% and reduces alert fatigue with smart occurrences regrouping
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
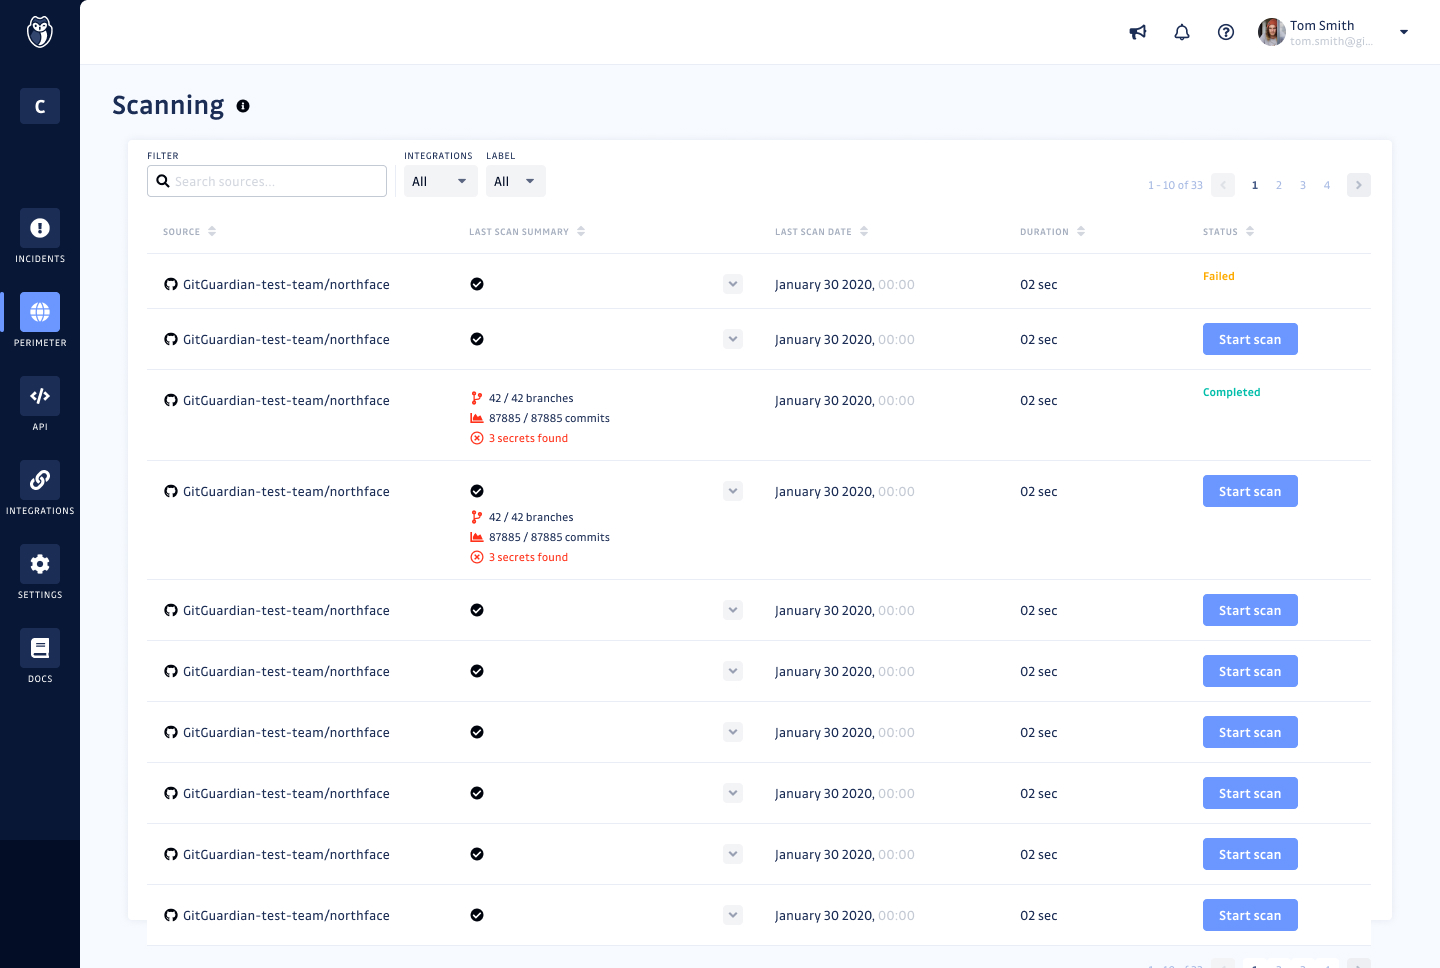
Improved user interface: It would be beneficial to have a more intuitive and user-friendly interface for Internal Monitoring on GitGuardian. This would make it easier for users to quickly access the data they need and understand the results of their scans.
Automated alerts: It would be helpful to have automated alerts when certain conditions are met, such as when a scan reveals sensitive data or when a new repository is created. This would help users stay informed and take action in a timely manner.
More detailed reports: Currently, Internal Monitoring reports are limited in terms of the depth of information they provide. It would be useful to have more detailed reports that include additional metrics, such as the number of repositories scanned and the types of sensitive data found.
Faster scan times: Scan times can be slow at times, making it difficult to stay on top of changes in repositories quickly. It would be beneficial to have faster scan times so that users can take action quickly when needed.
Migrating operations from QA to Production work well for initial deployment, however, when migrating an update to an existing job to production, sometimes certain project items are duplicated. This is not the end of the world... the duplicates can be removed, but would be nice if it was not required.
I have not found a way to trap under-the-covers SOAP errors (for example, when a query you are running against Salesforce takes too long). You get a warning error in the operation log that the job only pulled a "partial" file, but it does not fail.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have been evaluating other tools as a continuous improvement practice. I would like something that would be easier to use for a non-technical user. I work for a small organization and have no back-up for Jitterbit if something happens to me. We don't have the technically savvy employees to understand it.
I've evaluated quite a few other tools, like git-secrets, Git-leaks, scan, and maybe a few more. They're all great but quite surprisingly none of them detected Github OAuth Secrets for us. A lot of the FOSS tools out there focus on much simpler, generic secrets, which is good in itself but with GitGuardian, it was dead simple from day one. I just connected our Github Account and set up the gg-shield cli and that was all.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Evaluated Dell Boomi and Celigo as alternatives prior to purchasing Jitterbit. We went with Jitterbit at that time because we could handle all changes ourselves without any assistance from Jitterbit, and we liked their size and nimbleness. Dell Boomi was too big for us, and Celigo at that time did not have a self-service model. Every change had to go through them (although that has since changed). We were not in a position to be able to wait for someone to make changes for us given the rate of change within the business.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
GitGuardian Internal Monitoring has had a positive impact on our overall business objectives. By providing visibility into our code repositories and alerting us to potential security risks, we have been able to identify and mitigate security issues before they become a problem. This has allowed us to focus more on developing our product and less on responding to security incidents. We have also seen an increase in customer confidence in our product as a result of using GitGuardian Internal Monitoring, which has led to increased customer loyalty and retention. Overall, the ROI of using GitGuardian Internal Monitoring has been very positive for our business.
We have seen an increase in the security of our codebase, as well as an improvement in the speed and accuracy of our code reviews. This has enabled us to quickly identify and address any potential security issues before they become a problem. Additionally, we have seen an increase in our ROI as a result of using GitGuardian Internal Monitoring, as it has allowed us to save time and money by preventing costly security breaches.
The time it takes to connect systems has reduced by orders of magnitude. Previously, we would custom-develop connectors between various systems and they would all be managed by different vendors. With Jitterbit speed-to-deploy and the efficiency gained by managing all connections in one dashboard has been the greatest piece of the ROI.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info