The LogRhythm NextGen SIEM Platform, from LogRhythm in Boulder, Colorado, is security information and event management (SIEM) software which includes SOAR functionality via SmartResponse Automation Plugins (a RespondX feature), the DetectX security analytics module, and AnalytiX as a log management solution that centralizes log data, enriches it with contextual details and applies a consistent schema across all data types.
N/A
Splunk Observability Cloud
Score8.5 out of 10
N/A
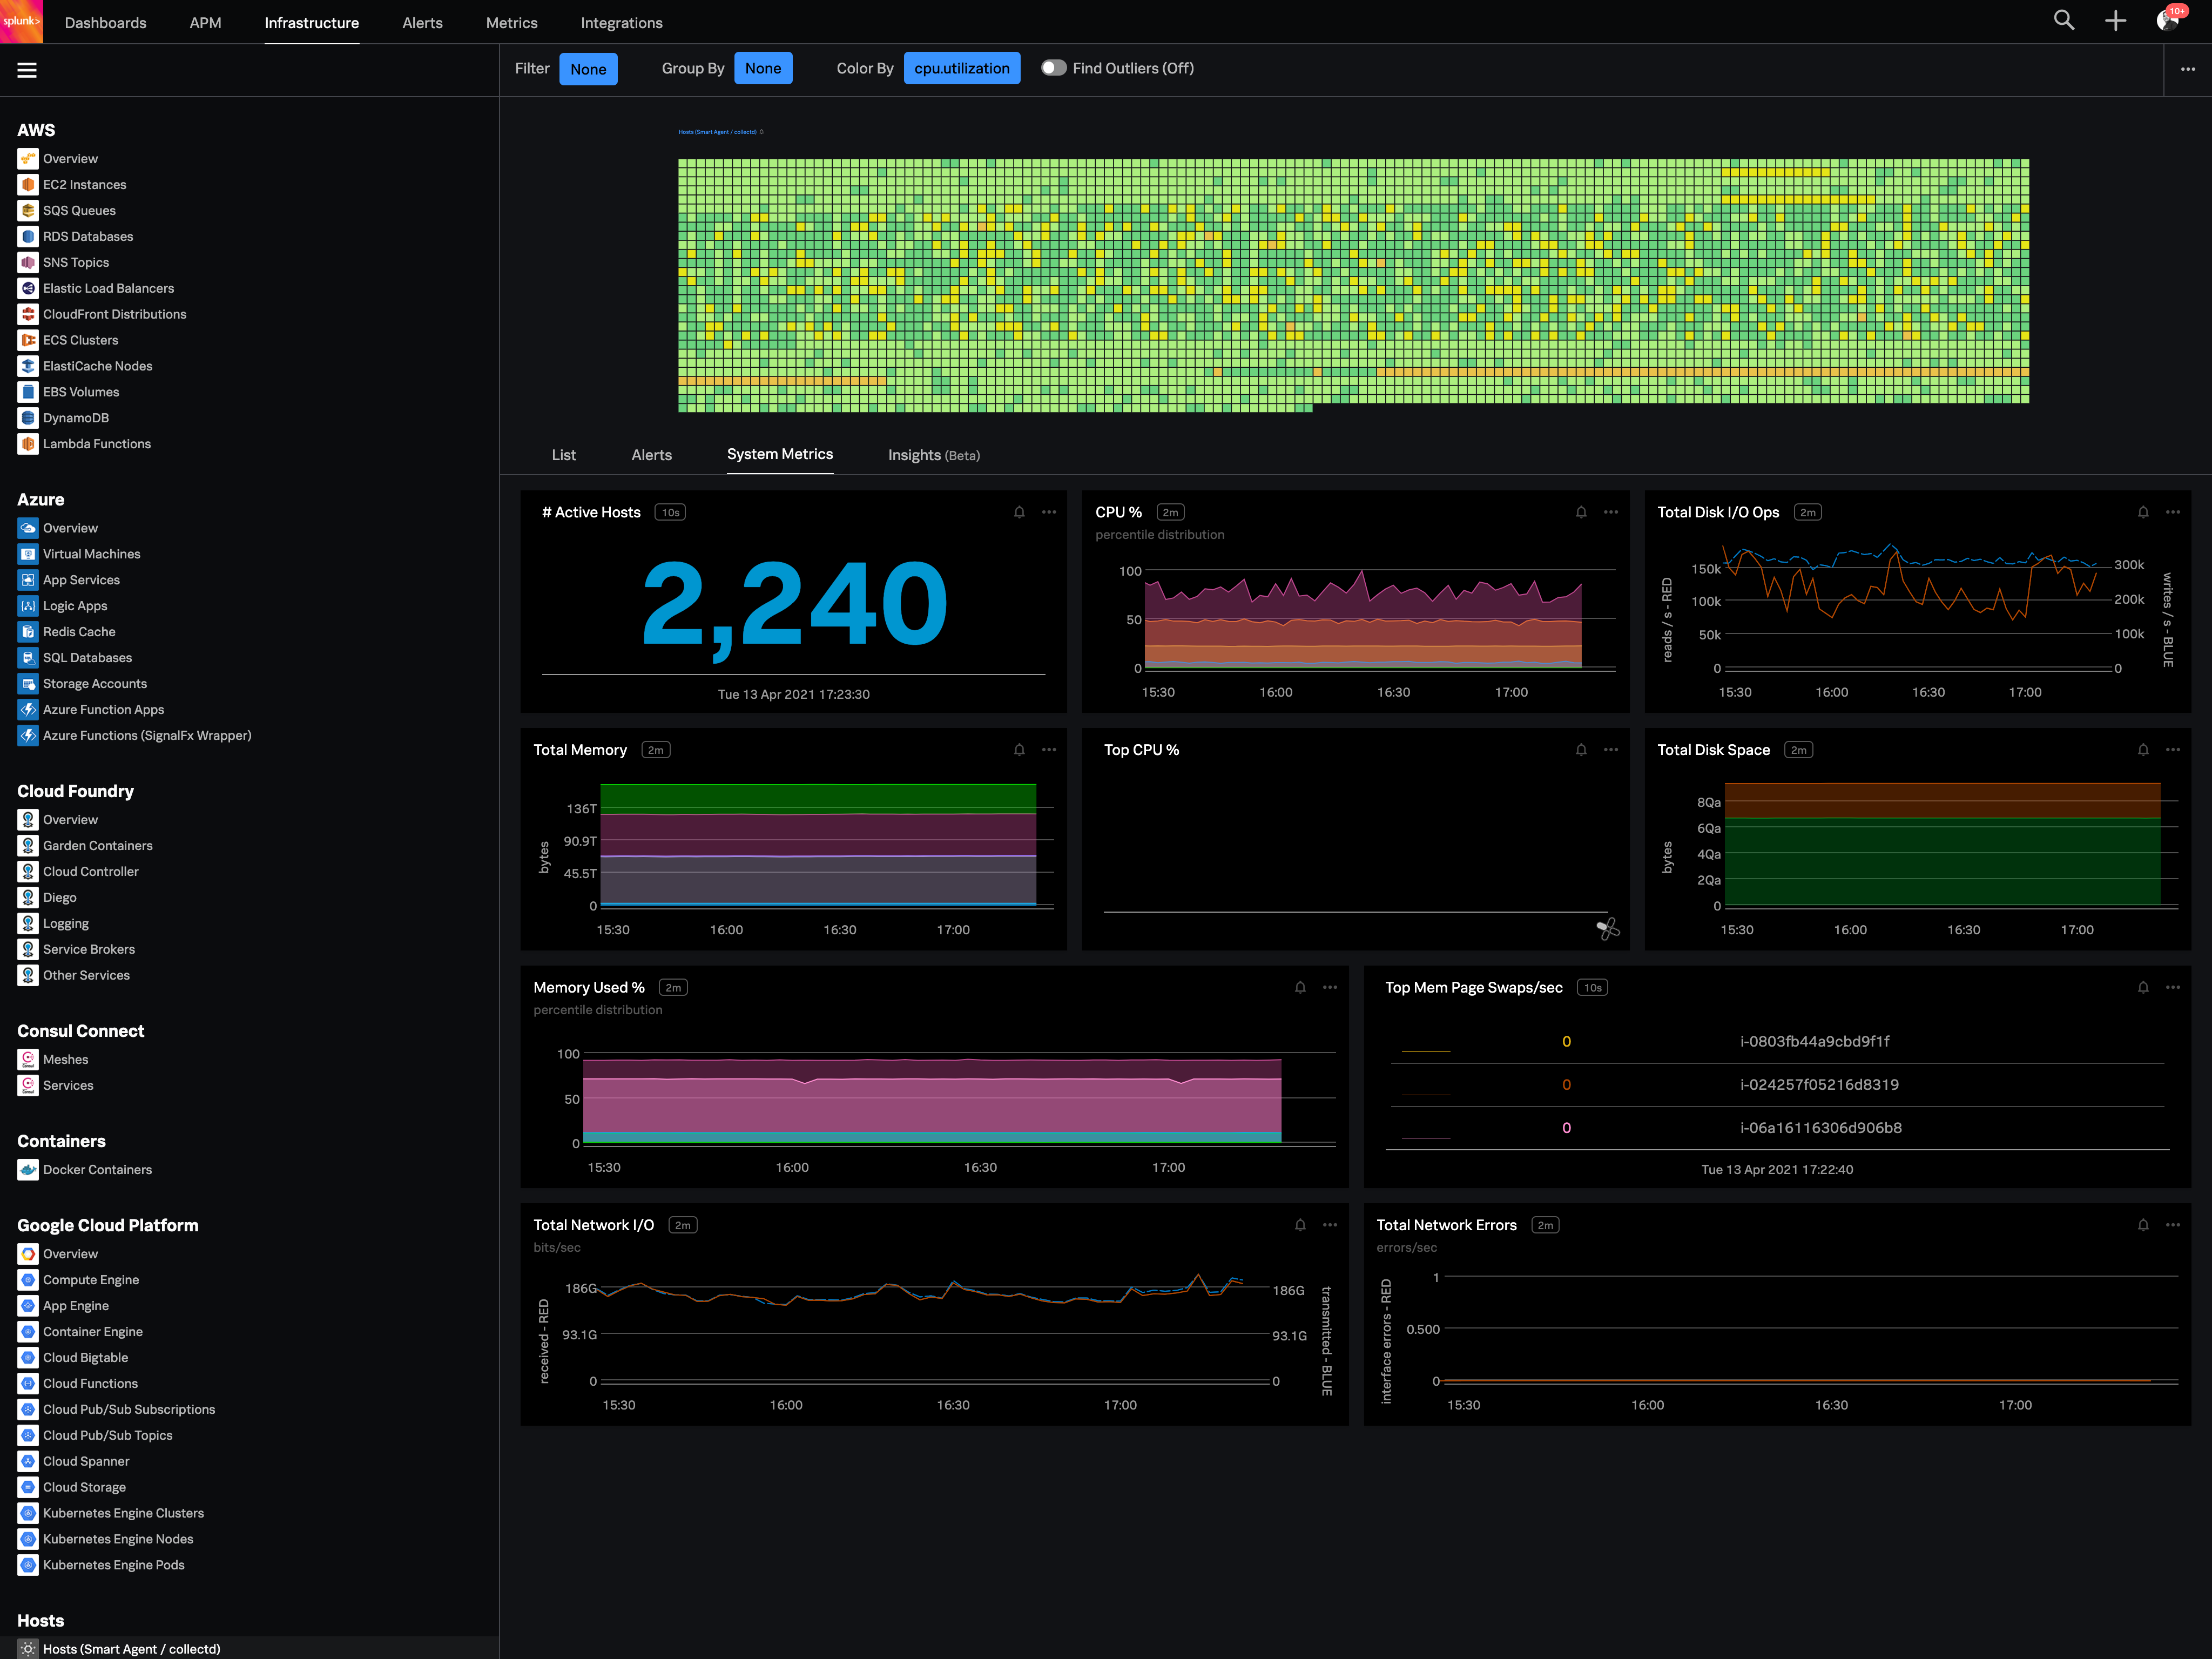
Splunk Observability Cloud aims to enable operational agility and better customer experience through real-time AI-driven streaming analytics allowing accurate alerts in seconds. It is designed to shorten MTTD and MTTR by providing real-time visibility into cloud infrastructure and services.
Having mostly worked with their on-premises solution, I think it's well-suited for small , medium, and even big organisations. I feel it might be less suited if the customer wants a SIEM with 100% uptime, as it goes down a lot. Or if they want to depend on customer support. I suggest that if you want to go with LR, you have to have your own experienced engineers to work on.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Its great if you need real-time visibility across complex or regulated environments. Also strong for hybrid or multi-cloud setups where uptime, observability and fast IR are required. It’s probably overkill for smaller teams or environments that don’t have constant changes or compliance reporting needs. It's expensive and has a steep learning curve. Also, in my opinion, do not get yourself into a consumption based model. Costs can certainly get out of control quickly.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
LogRhythm NextGen SIEM Platform has an alarm system that generates tickets based on the event and the way it has been configured in the LogRhythm console. Let's say we have a ticket for a malicious email attachment. The ticket will some information like the source of the log, the source IP, destination IP etc. It can be drilled down to obtain specific information like the recipient, source location, file attachment name, SHA hash of the file, source and destination port, time, mac address of the machine that downloaded it etc. This helps the analysts to go to the root of the cause and take actions easily without manually parsing them.
The second good thing about the LogRhythm NextGen SIEM Platform is that it is very easy to use with its well-structured interface. To use LogRhythm, an user barely require any technical skills. A little overview of IP, CIDR, hash, etc. is enough to get your hands on it. It requires no programming or coding skills, as everything is GUI based. It also provides a beautiful visualization dashboard. There is another beautiful feature that it provides for the classification of events, known as cases. Multiple users working on the same platform can create cases and add events to it. They also help to maintain future reference.
The third good feature is the search tool which is very powerful. For example, sometimes it is hard to find the users who downloaded a malware from the guest wireless of the institution and not the private network. The search tool helps us in searching the user by automatically correlating the MAC address from the current network logs and the previous logs as the MAC address is the same. It is highly scalable for parsing a large number of logs from various sources.
I particularly think this is one of the best software available for log parsing in an organization where non-technical users are working on incident response. This tool has a good amount of flexibility. However, it can only be configured with the LogRhythm NextGen SIEM Platform Console.
In terms of usability, as already mentioned, it is a very easy tool to use, with a GUI based interface.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first one is its Kubernetes container monitoring.
I really like this features because as we know how much K8s is vast and to manually monitor each part of the Kubernetes it takes so much time but Splunk Observability Cloud makes it easier. And even once we integrate K8s with Splunk Observability Cloud it gives us some prebuilt dashboards which gives holistic view of our Cluster and its nodes, pods, etc.
The dashbaord feature of Splunk Observability Cloud, it gives us full flexibility to customize our dashboard with a wide range of predefined chart types.
Now it also supports OTEL, which is a plus point for observability. As now everyone is moving towards Otel and in current market there are only few tools who supports OTEL based integrations, Splunk Observability Cloud is one out of them.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
LogRhythm absolutely needs to provide back end support for threat intelligence lists. Performing a linear search on massive lists of IPs on incoming web traffic can bring the SIEM to its knees.
LogRhythm should drop its entire code base for implementing lists and simply turn them into hash tables to avoid the excessive cost associated with referencing lists in rules. I haven't seen the code, but the performance suggests O(n).
The reporting feature is the worst of all SIEMs, luckily reports are not my primary service offering. LogRhythm should definitely revamp its reporting to be more intuitive.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
You can use table-like functionality to generate dashboards, but these queries are heavy on the system.
It could be easier to give insight into what type of line parsing is used for specific documents in a company-managed environment and/or show ways to gain the insights needed.
I would like to see ways to anonymize specific data for shared reports without pre-formatting this in a dashboard on which reports could be based.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
LogRhythm is focused on SIEM. That is their core business. Cost of operations, feature set and ease of use. The Log Rhythm support team is outstanding. Overall reliability is good. Reporting module needs some improvement and LR is promising that there will be significant improvements in future releases.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Good: Stable system with low error rate Easy to use for simple use cases Bad: UI is not very clear for complex usage Mobile view (when logged in from phone) is bad No library for .net
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
LogRhythm does a rather decent job of making the functionality advanced (allowing for advanced keyword & field searching, use of "AND" as well as "OR" statements in the search bar) while keeping it accessible (by not requiring a specific syntax to do quick searches). This combined with a user interface that has headings and labels that are intuitive is very helpful.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
When there is an issue, it’s a win if one can easily identify the root cause. To do the same, it should allow the user to dig deep with multiple data points and compare the data and identify the anomaly. In this use case, it’s good to drive from Splunk 011y.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
While LogRhythm support is generally quick to respond, the initial response is usually from a first line support engineer with general knowledge of the product. Any advanced or complex issues have always required the assistance of a higher tier of support, directly or indirectly. For a few occasions we actually used our PS hours to work on the issue.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
LogRhythm was simpler to set up and configure as well as extract information from. It also was less intrusive in terms of how many appliances were needed to implement. We were up and running within 5 hours to start accepting log sources. We selected LogRhythm as well since support is based in the USA in Colorado.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Splunk Infrastructure Monitoring provides far superior options for anybody using a complex hybrid multi-cloud environment and allows both your SOC and NOC to work together on the same data while driving their own insights. We found other products are still in the old world view of servers and agents residing together within a single data centre, but modern apps are no longer like this.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info