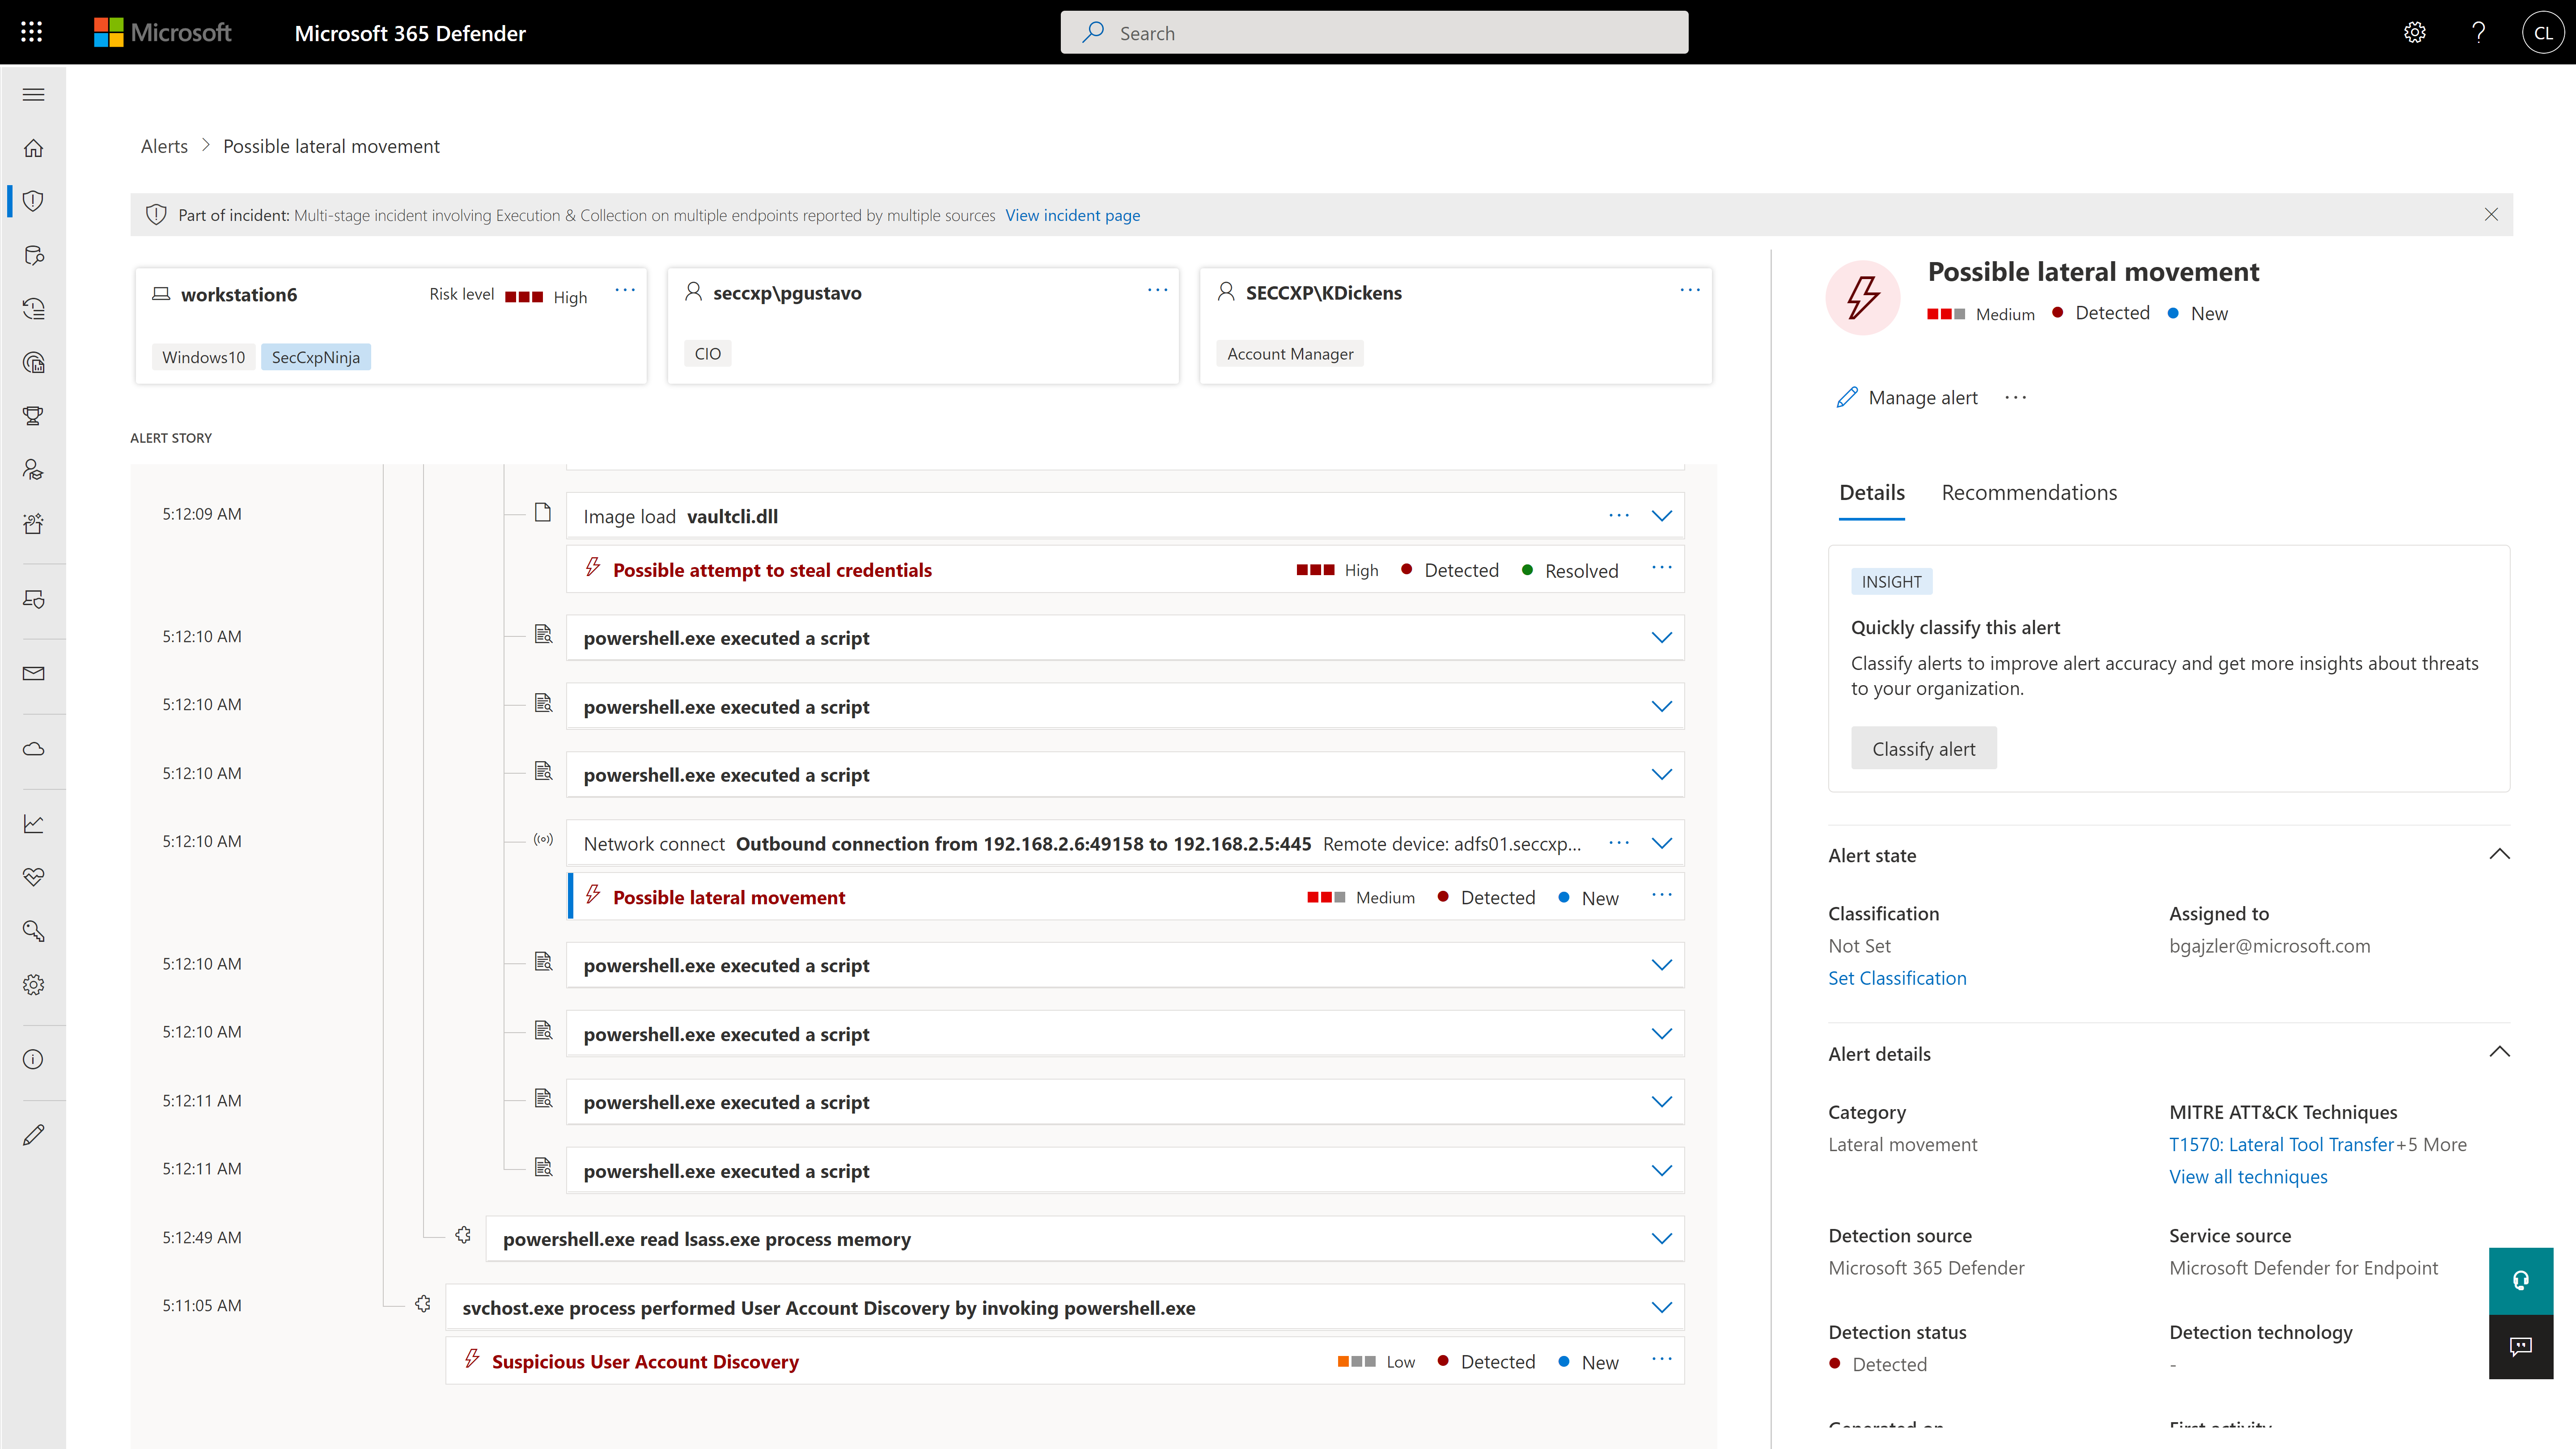
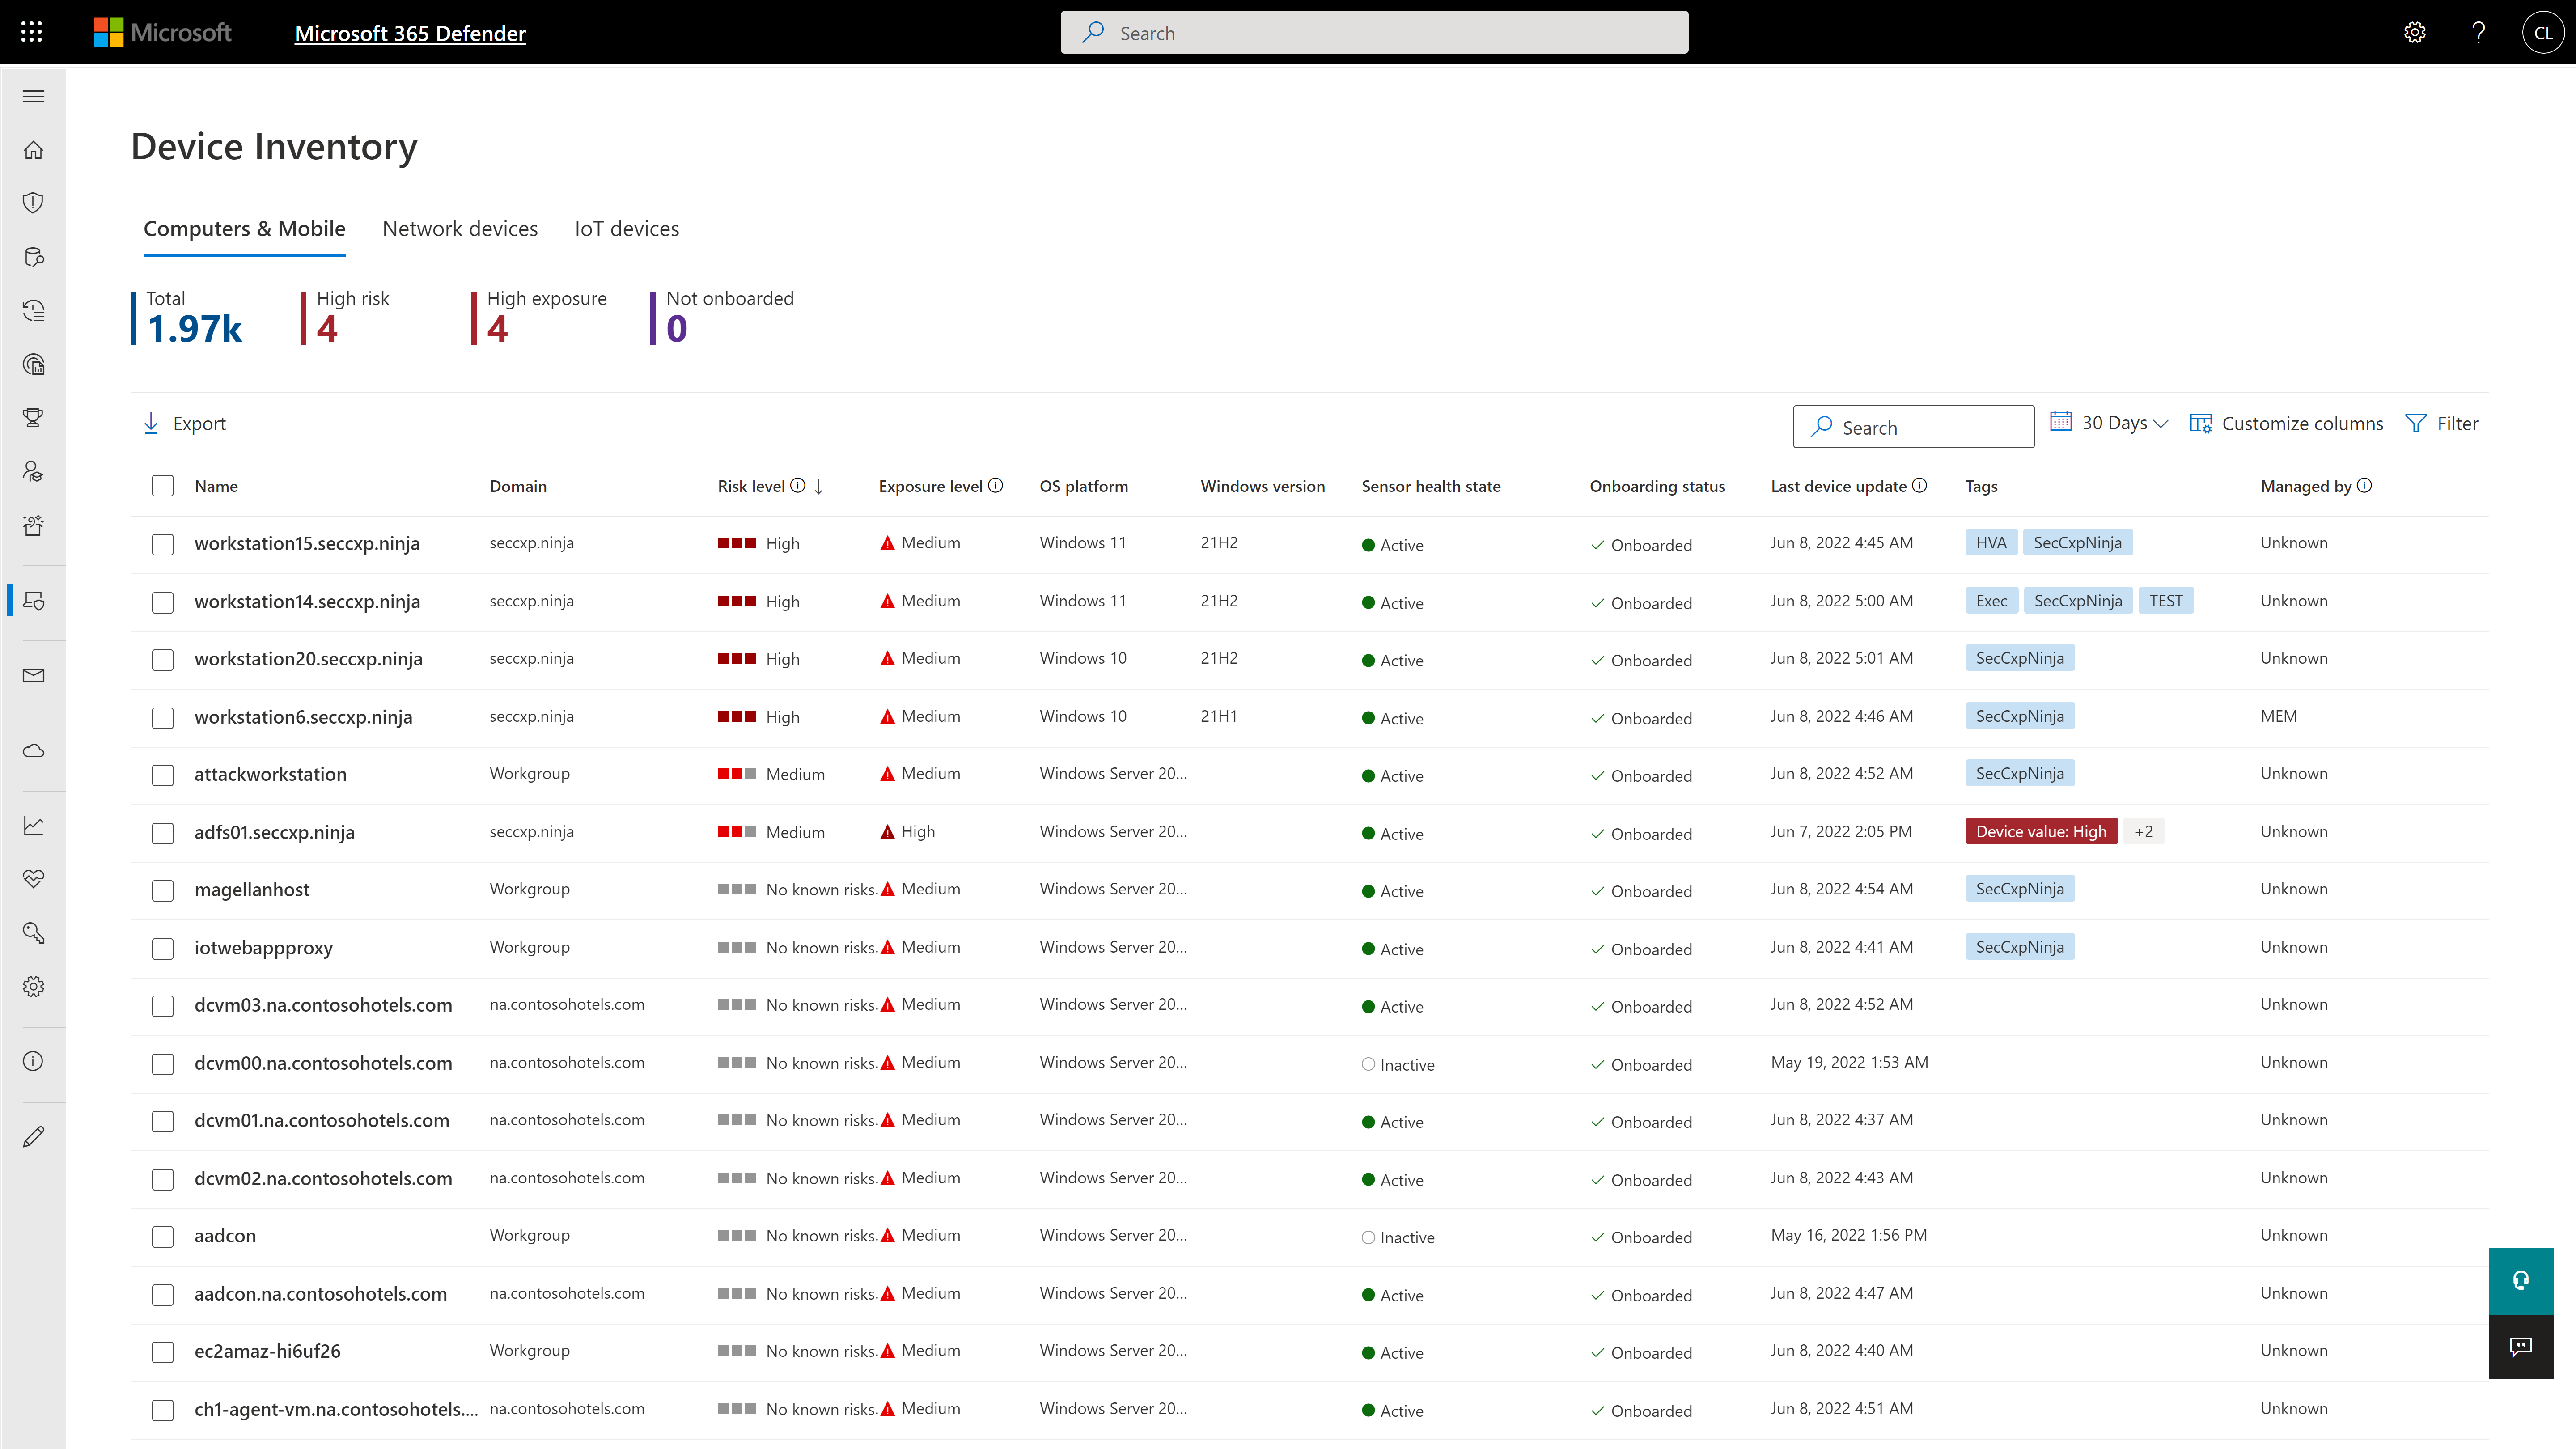
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
OneLogin by One Identity
Score9.4 out of 10
N/A
OneLogin is an identity and access management (IAM) product from One Identity since the October 2021 acquisition, featuring single sign-on (SSO), multi-factor authentication, provisioning, cloud directory, and more.
$4
per month per user
Pricing
Microsoft Defender for Endpoint
OneLogin by One Identity
Editions & Modules
Academic
$2.50
per user/per month
Standalone
$5.20
per user/per month
Advanced (bundle)
$4
per month per user
Professional (bundle)
$8
per month per user
Offerings
Pricing Offerings
Microsoft Defender for Endpoint
OneLogin by One Identity
Free Trial
Yes
Yes
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
—
Aside from the bundle options, OneLogin offers its services a la carte, and therefore these prices can vary depending on your business's needs.
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
OneLogin is very convenient. Users can register their own iPhone or Android to act as their authorization device, meaning they will likely always have access to the OneLogin security code. The OneLogin application then allows the users to hit a button instead of inputting the security code to validate their two-factor authorization. OneLogin is great for businesses who need to enforce secure access into their various systems and tools. By consolidating the security into a single login with security device two-factor authorization, it makes it safe and easy to manage.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Connects with a lot of different vendors, tools, and sites. It is also customizable to where you can add almost any site you are logging into. This makes it especially useful for team members who may use a tool that other team members within the company do not use.
It works. I've used a few keychain apps that work for a little while, or never work, and this app works 99.99% of the time. Only on one experience have I experienced issue access sites and that was due to user error.
It's easy to update passwords and usernames within the app. It allows password resets to be an easy process and lowers the time in updating items everywhere.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Lack of administrative APIs for creating or setting up new connectors: This prevents the automated integration to federations and requires manual setup rather than discovery-based automated setup.
Customization of the interface: The potential configuration of the interface are still limited at the moment (logo, primary and secondary colors, background). This prevents the usage of the platform as a communication medium or to organize the space in a more standard fashion (for our institution)
There are some limitations with using the apps provisioning APIs that can lead to some termination or provisioning actions not being completed
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
OneLogin is very easy to use. The most complicated part is the user setup and even that is not difficult. After everything is working, using it day to day is trivial. All you have to do is have the application ready on your phone and you can use a single set of login credentials to access all of your tools securely.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
There has never been an issue where I have needed to use the OneLogin support so it would be unfair to rate them anything other than a 10 on their ability to provide support. Like I said its a very basic platform that we use it for with no issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
OneLogin has a lesser cost as compared to other solutions. It also has a successful POC, partner expertise, integration with in-house and cloud-based apps, and provides restriction of access from unauthorized devices. It is a secure solution with industry-standard encryption, a good dashboard, and a cloud-based solution. In my opinion, there is not too much effort involved in the integration and it provides good OEM support.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info