Mimecast Awareness Training equips security teams to identify and reduce human-driven risk across their entire organization. The security awareness and human risk management solution works to continuously inspire awareness, transform behavior, and reduce the likelihood of security incidents caused by human error.
N/A
SonarQube
Score8.7 out of 10
N/A
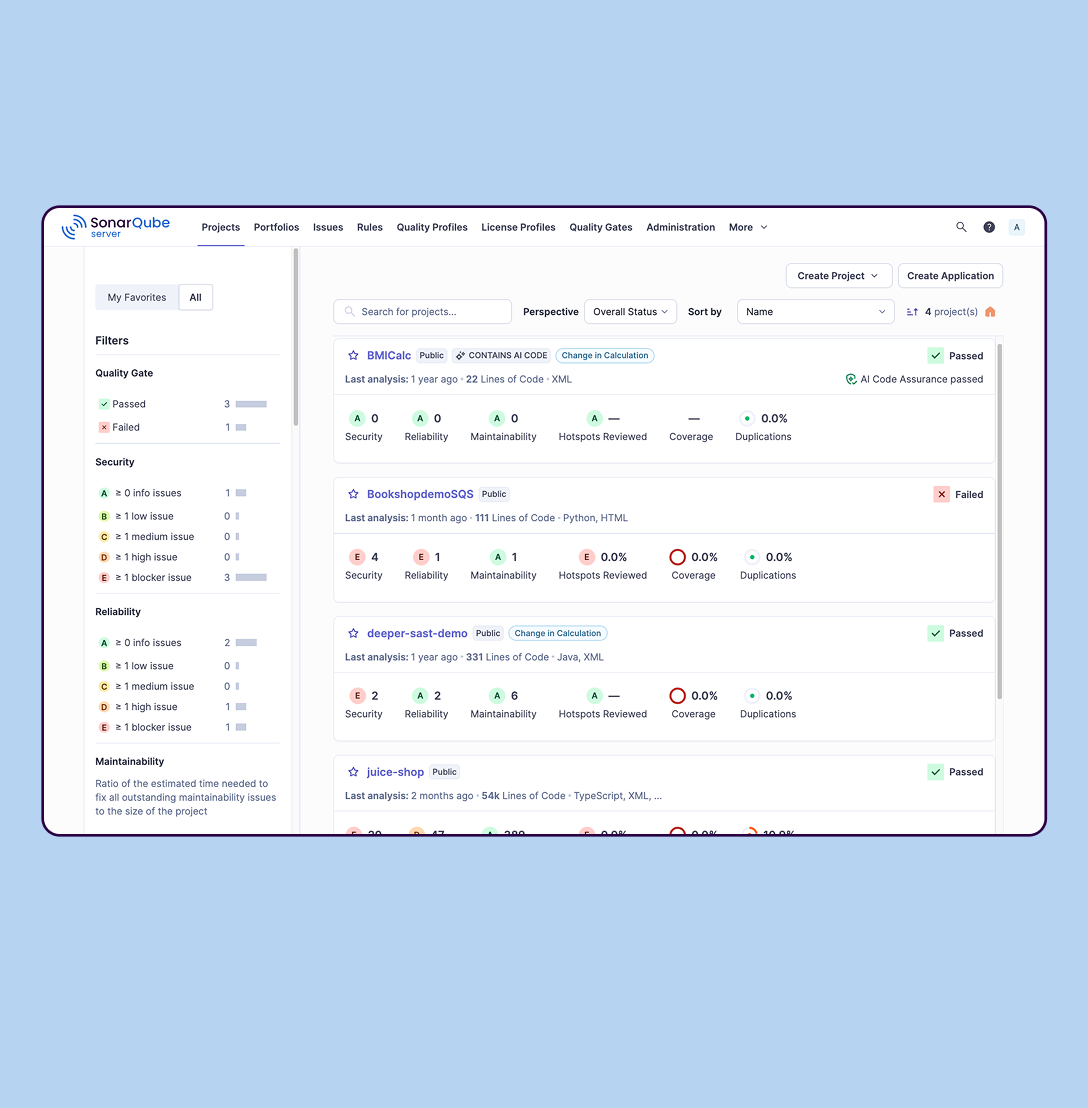
SonarQube is an automated code review solution, serving as the verification layer for code quality and SDLC security. SonarQube is used to ensure that code is secure, reliable, and maintainable. It is available through SaaS or self-managed deployment.
Staff is the single most significant danger to the cyber security posture of an organization. Before implementing Mimecast Awareness Training, staff had almost no awareness or concept of IT security or the potential risks. Staff attitudes have improved dramatically since introducing Awareness Training.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is excellent if you start using it at the beginning when developing a new system, in this situation you will be able to fix things before they become spread and expensive to correct. It’s a bit less suitable to use on existing code with bad design as it’s usually too expensive to fix everything and only allows you to ensure the situation doesn’t get worse.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
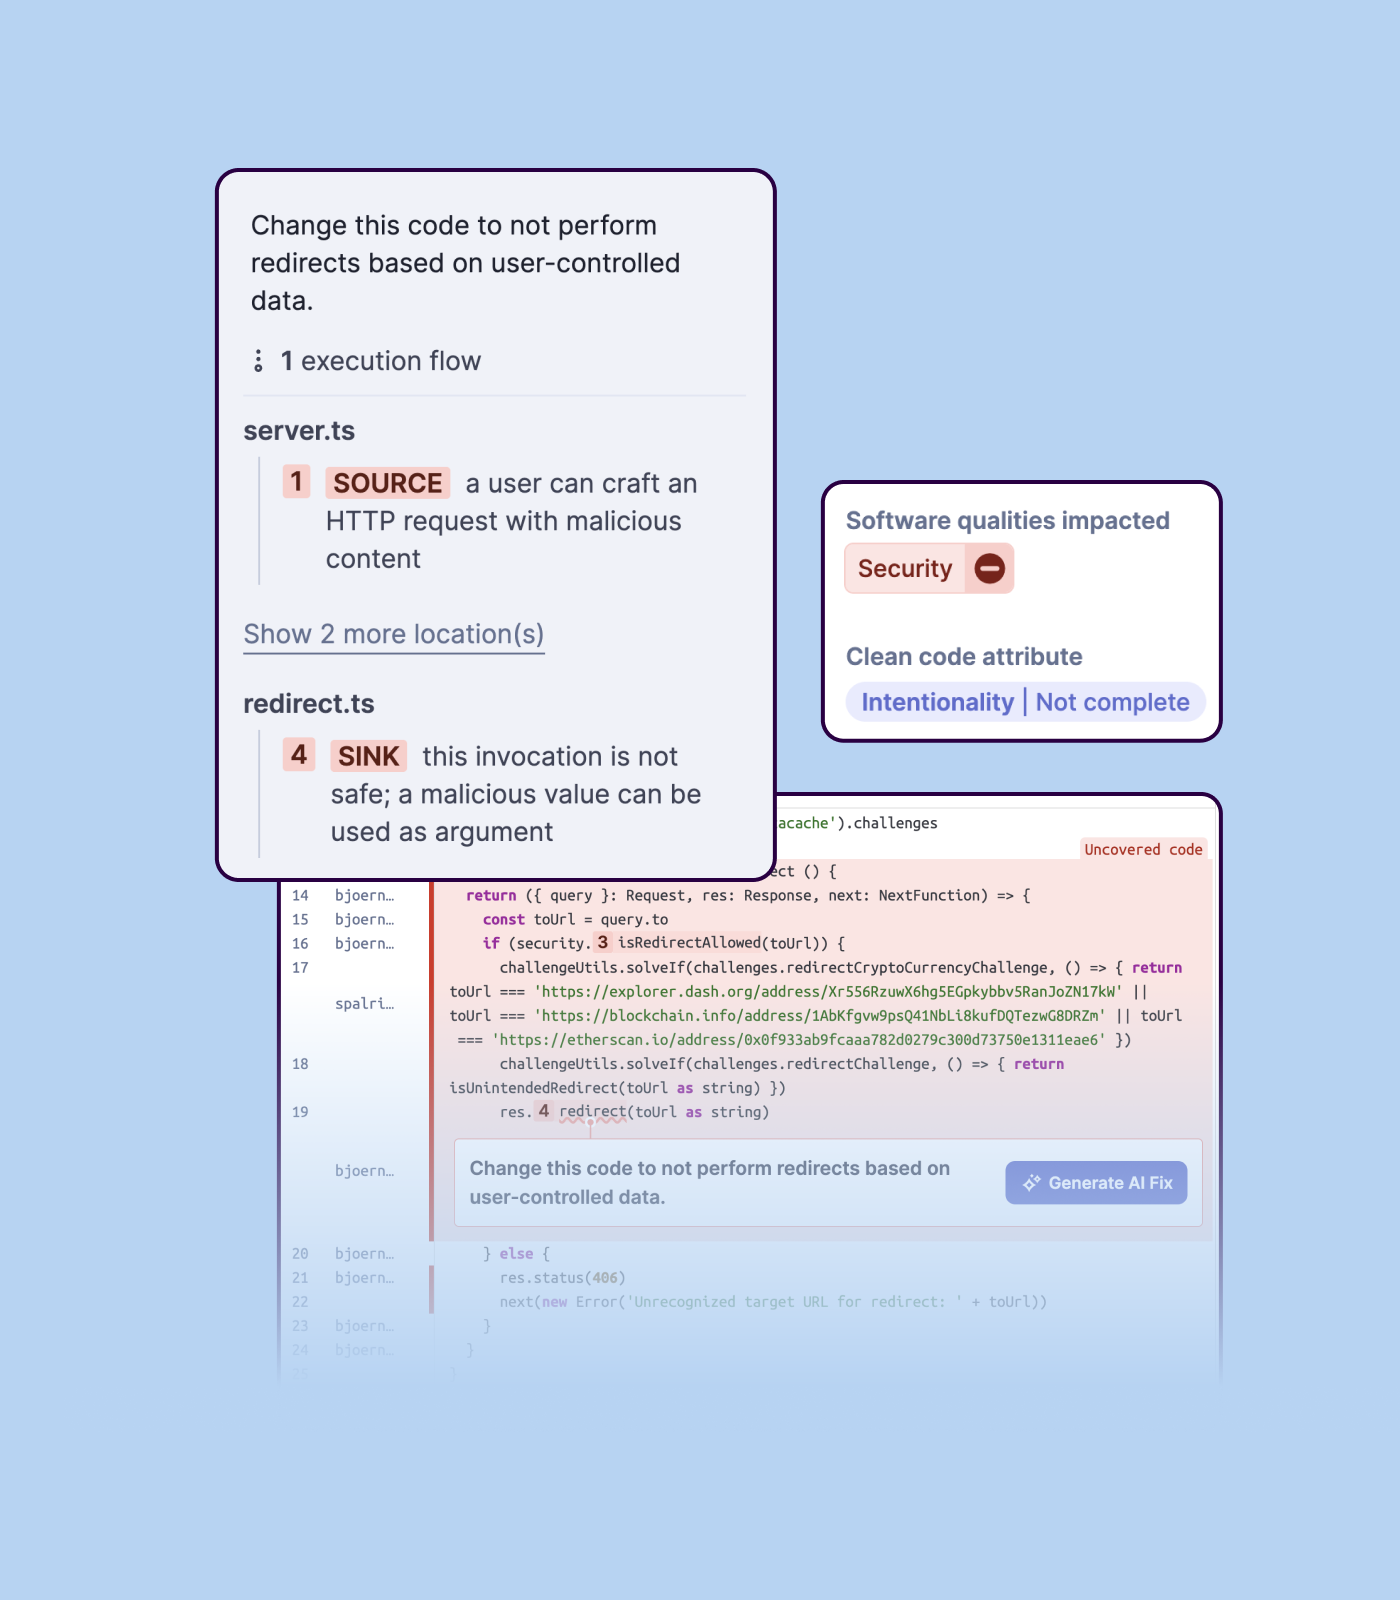
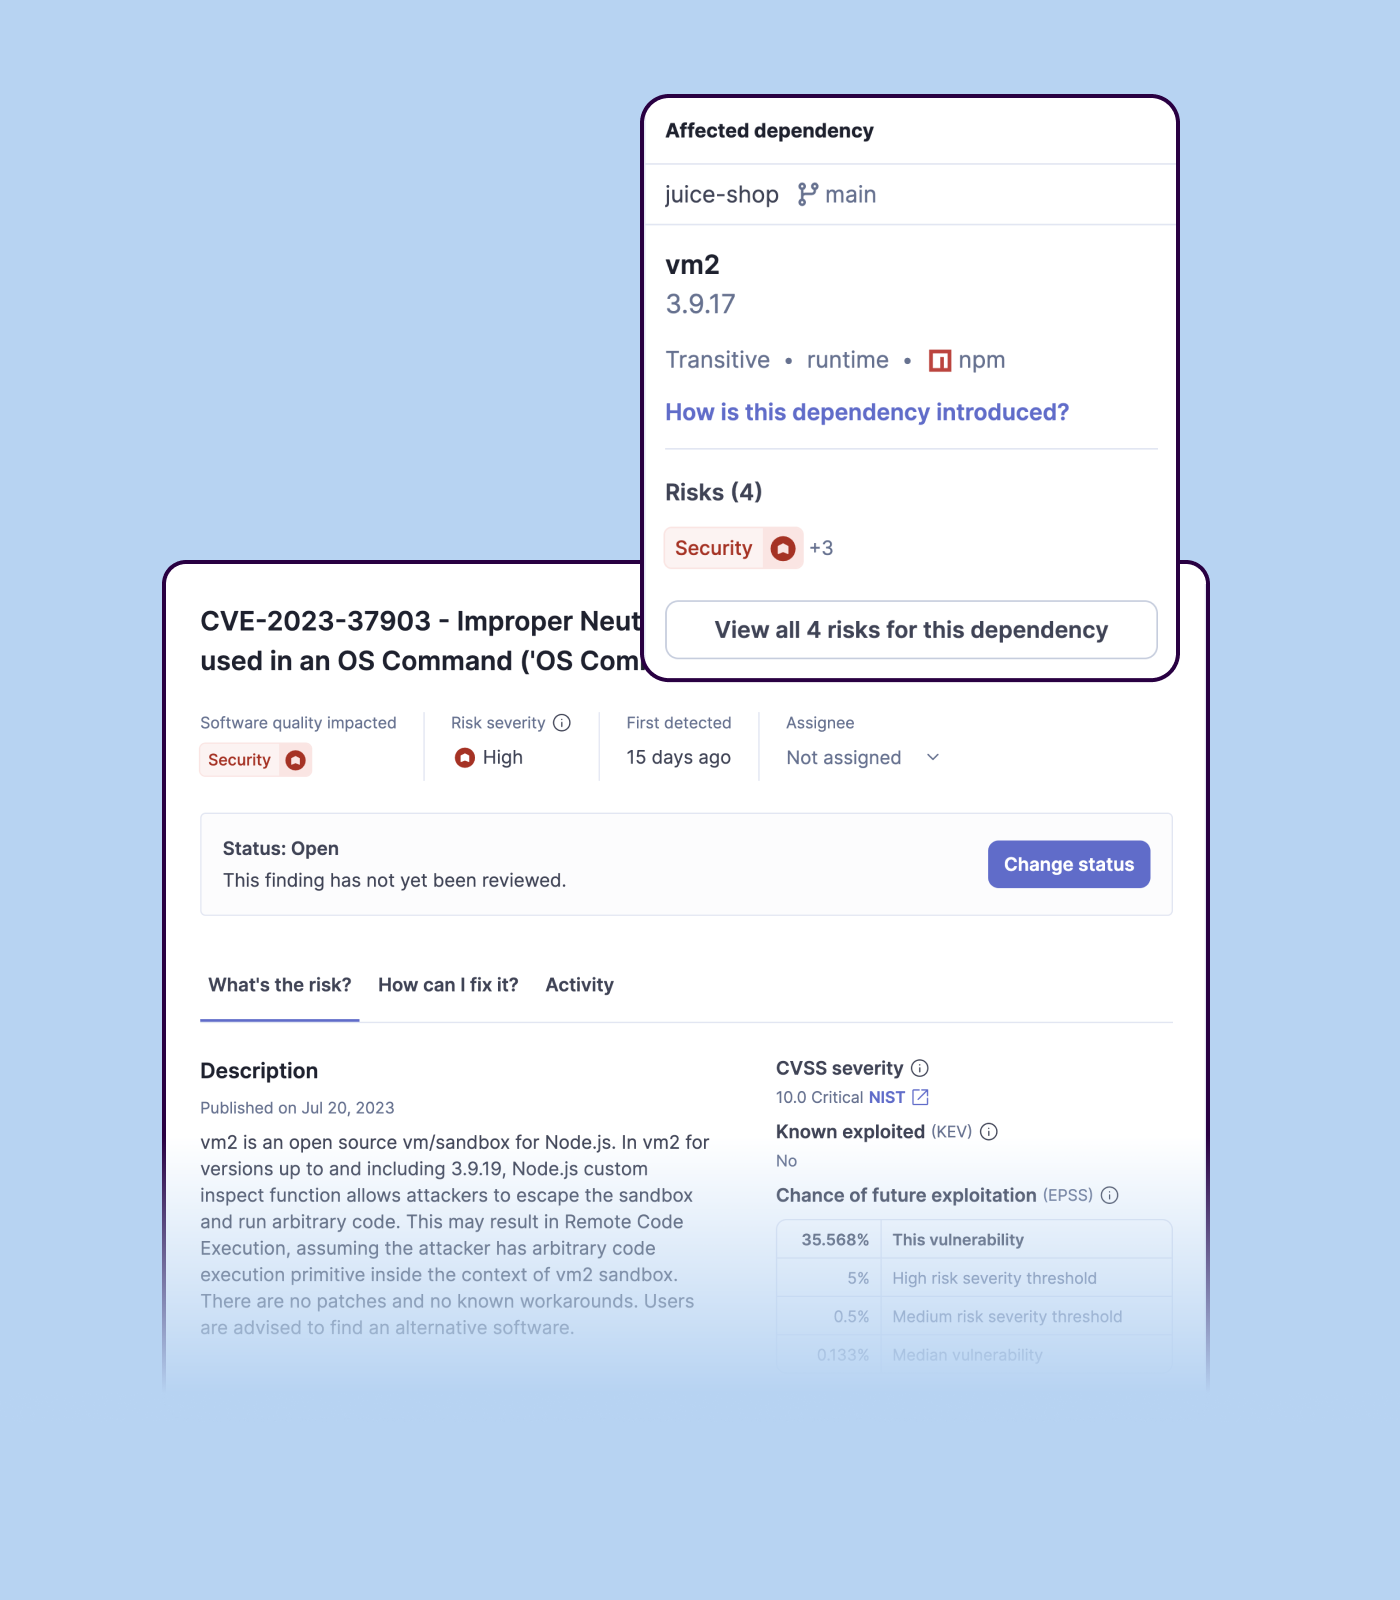
Detecting bugs and vulnerabilities: SonarQube can identify a wide range of bugs and vulnerabilities in code, such as null pointer exceptions, SQL injection, and cross-site scripting (XSS) attacks. It uses static analysis to analyze the code and identify potential issues, and it can also integrate with dynamic analysis tools to provide even more detailed analysis.
Measuring code quality: SonarQube can measure a wide range of code quality metrics, such as cyclomatic complexity, duplicated code, and code coverage. This can help teams understand the quality of their code and identify areas that need improvement.
Providing actionable insights: SonarQube provides detailed information about issues in the code, including the file and line number where the issue occurs and the severity of the issue. This makes it easy for developers to understand and address issues in the code.
Integrating with other tools: SonarQube can be integrated with a wide range of development tools and programming languages, such as Git, Maven, and Java. This allows teams to use SonarQube in their existing development workflow and take advantage of its powerful code analysis capabilities.
Managing technical debt: SonarQube provides metrics and insights on the technical debt on the codebase, enabling teams to better prioritize issues to improve the quality of the code.
Compliance with coding standards: SonarQube can check the code against industry standards like OWASP, CWE and more, making sure the code is compliant with security and coding standards.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Importing a new custom quality profile on SonarQube is a bit tricky, it can be made easier
Every second time when we want to rerun the server, we have to restart the whole system, otherwise, the server stops and closes automatically
When we generate a new report a second time and try to access the report, it shows details of the old report only and takes a lot of time to get updated with the details of the new and fresh report generated
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I’ve parked the slider at a solid 10 because the platform keeps proving its worth every quarter. Staff phishing‑click rates have plunged from double digits to low single digits, our audit team finally stopped chasing overdue modules, and—bonus—engagement surveys show people actually enjoy the bite‑sized, comedic flavoured content. The built‑in reporting lets me walk straight into the boardroom with clean metrics. Minimal admin, measurable behaviour change, and zero eye‑rolls from end‑users—hard to ask for more.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I pegged usability at a full‑blown 10 because even my least tech‑savvy colleagues—think “still double‑clicks web links” level—navigate the portal without ringing the help‑desk. Single‑sign‑on drops them straight into the next module, the interface looks like Netflix for cyber nerds, and the progress bar shouts “two minutes left” instead of burying them in menus. On the admin side, I spin up campaigns in three clicks, clone content on the fly, and the drag‑and‑drop scheduling means I can rejig a whole quarter’s plan during the time it takes the kettle to boil. Zero training manuals, zero grumbles, zero excuses—just smooth sailing from login to completion.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Its the best, hands down. Great, easy to use and on point content that injects some humour into the training makes it relevent whilst staying engaging. We have seen our engagement scores almost double since using Mimecast, with completion rates across the buisness above 90% compared to previous scores on less than 50%.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The product is quick and responsive. Emails alert the staff of new training content and provides a direct link to the training video. They watch, learn and than answer a brief question to test their knowledge. This feeds into the users risk profile in which additional training can be automatically applied based on a risk scores.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have had a couple of instances where we needed to contact customer support for our minecast cyber awareness training. The team were great and easy to deal with. The problem in itself was minor, and turned out to be our issues and understanding setup, however the mimecase team walked us through the issue and it was resolved exceptionally quick.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We we easily able to integrate the SonarQube steps into our TFS process via the Microsoft Marektplace, we didn't have the need to call SonarQube support. We've used their online documentation and community forum if we ran into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I gave implementation a rock‑solid 10 because, frankly, it was smoother than a servo sausage roll at 2 a.m. SSO clicked in on the first try, directory sync hoovered up all the user data without mangling job titles, and change comms went out on time—no “surprise training” backlash. Key insight: involve your internal comms or HR crew from day zero so the launch emails feel like a friendly nudge, not a phishing attempt. We also ran a pilot with our most cynical techs; their nit‑picks helped us tweak permissions before unleashing it on the masses. Finally, schedule the baseline phishing test after staff receive the kickoff memo—sounds obvious, but it spares you the angry “gotcha” emails and makes the resulting metrics actually meaningful.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Mimecast's content is much higher quality. KnowBe4's sales tactics are much more pushy. Customer service has been better with Mimecast in general, though Mimecast's UX/UI is a lot more confusing a less user-friendly to navigate than KnowBe4. It is difficult to group individuals together, let alone manage if the directory integration is not used.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is an open-source. It's a scalable product. The costs for this application, for the kind of job it does, are pretty descent. Pipeline scan is more secured in SonarQube. Its a very good tool and its support multiple languages. Its main core competency is of static code analysis and that is why SonarQube exists and it does it exceedingly well. The quality of scan on code convention, best practices, coding standards, unit test coverage etc makes them one of the best competent tool in the market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Honestly, the pricing model is about as painless as a public‑holiday Monday—straightforward per‑user cost, no sneaky “module packs” hiding in the fine print, and the nonprofit discount went down a treat. If I had to nit‑pick for the sake of continuous improvement, I’d love two tweaks:
Seat‑band granularity. The jump between tiers can feel like falling off a cliff when you’re hovering near the threshold; a smaller step (say, every 50 users) would soften the blow on fast‑growing teams.
Mid‑term seat reductions. We negotiated a generous +10 % buffer, but if headcount ever drops, a pro‑rata credit instead of waiting for renewal would be ace.
Minor quibbles, though—the value’s still a raging 10/10.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Mimecast Awareness Training is so easy to use, a child could set it up. One of the major benefits of the platform is its ability to easily prepare a years worth of content. As new users enter the organisation, its integration with Microsoft makes it easy to onboard the user and have then catch up on training.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I’m handing professional services a loud 10 because they rocked up like a pit‑crew at Bathurst and had us race‑ready in record time. Two half‑day workshops, and suddenly we’d nailed SSO, tuned the Azure AD connector, and had a fistful of custom phishing templates dripping with Aussie‑isms (Bunnings receipts, anyone?). Their consultant even whipped up a cheeky PowerShell script to clean up dodgy display‑name attributes, saving our sys‑ops hours of beard‑scratching. On top of that, they translated our dull “Information Handling” policy into bite‑sized language for the learner splash screens—legal loved it, staff actually read it. Zero scope creep, crystal‑clear handover docs, and follow‑up calls that felt more like mentoring than billable hours. Worth every cent.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive ROI from the standpoint of flagging several issues that would have otherwise likely been unaddressed and caused more time to be spent closer to launch
Slightly positive ROI from time-saving perspective (it's an automated check which is nice, but depending on the issues it finds, can take developers time to investigate and resolve)