Splunk Enterprise Security is an analytics-driven SIEM that helps to combat threats with actionable intelligence and advanced analytics at scale.
N/A
WatchGuard Endpoint Security
Score8.7 out of 10
N/A
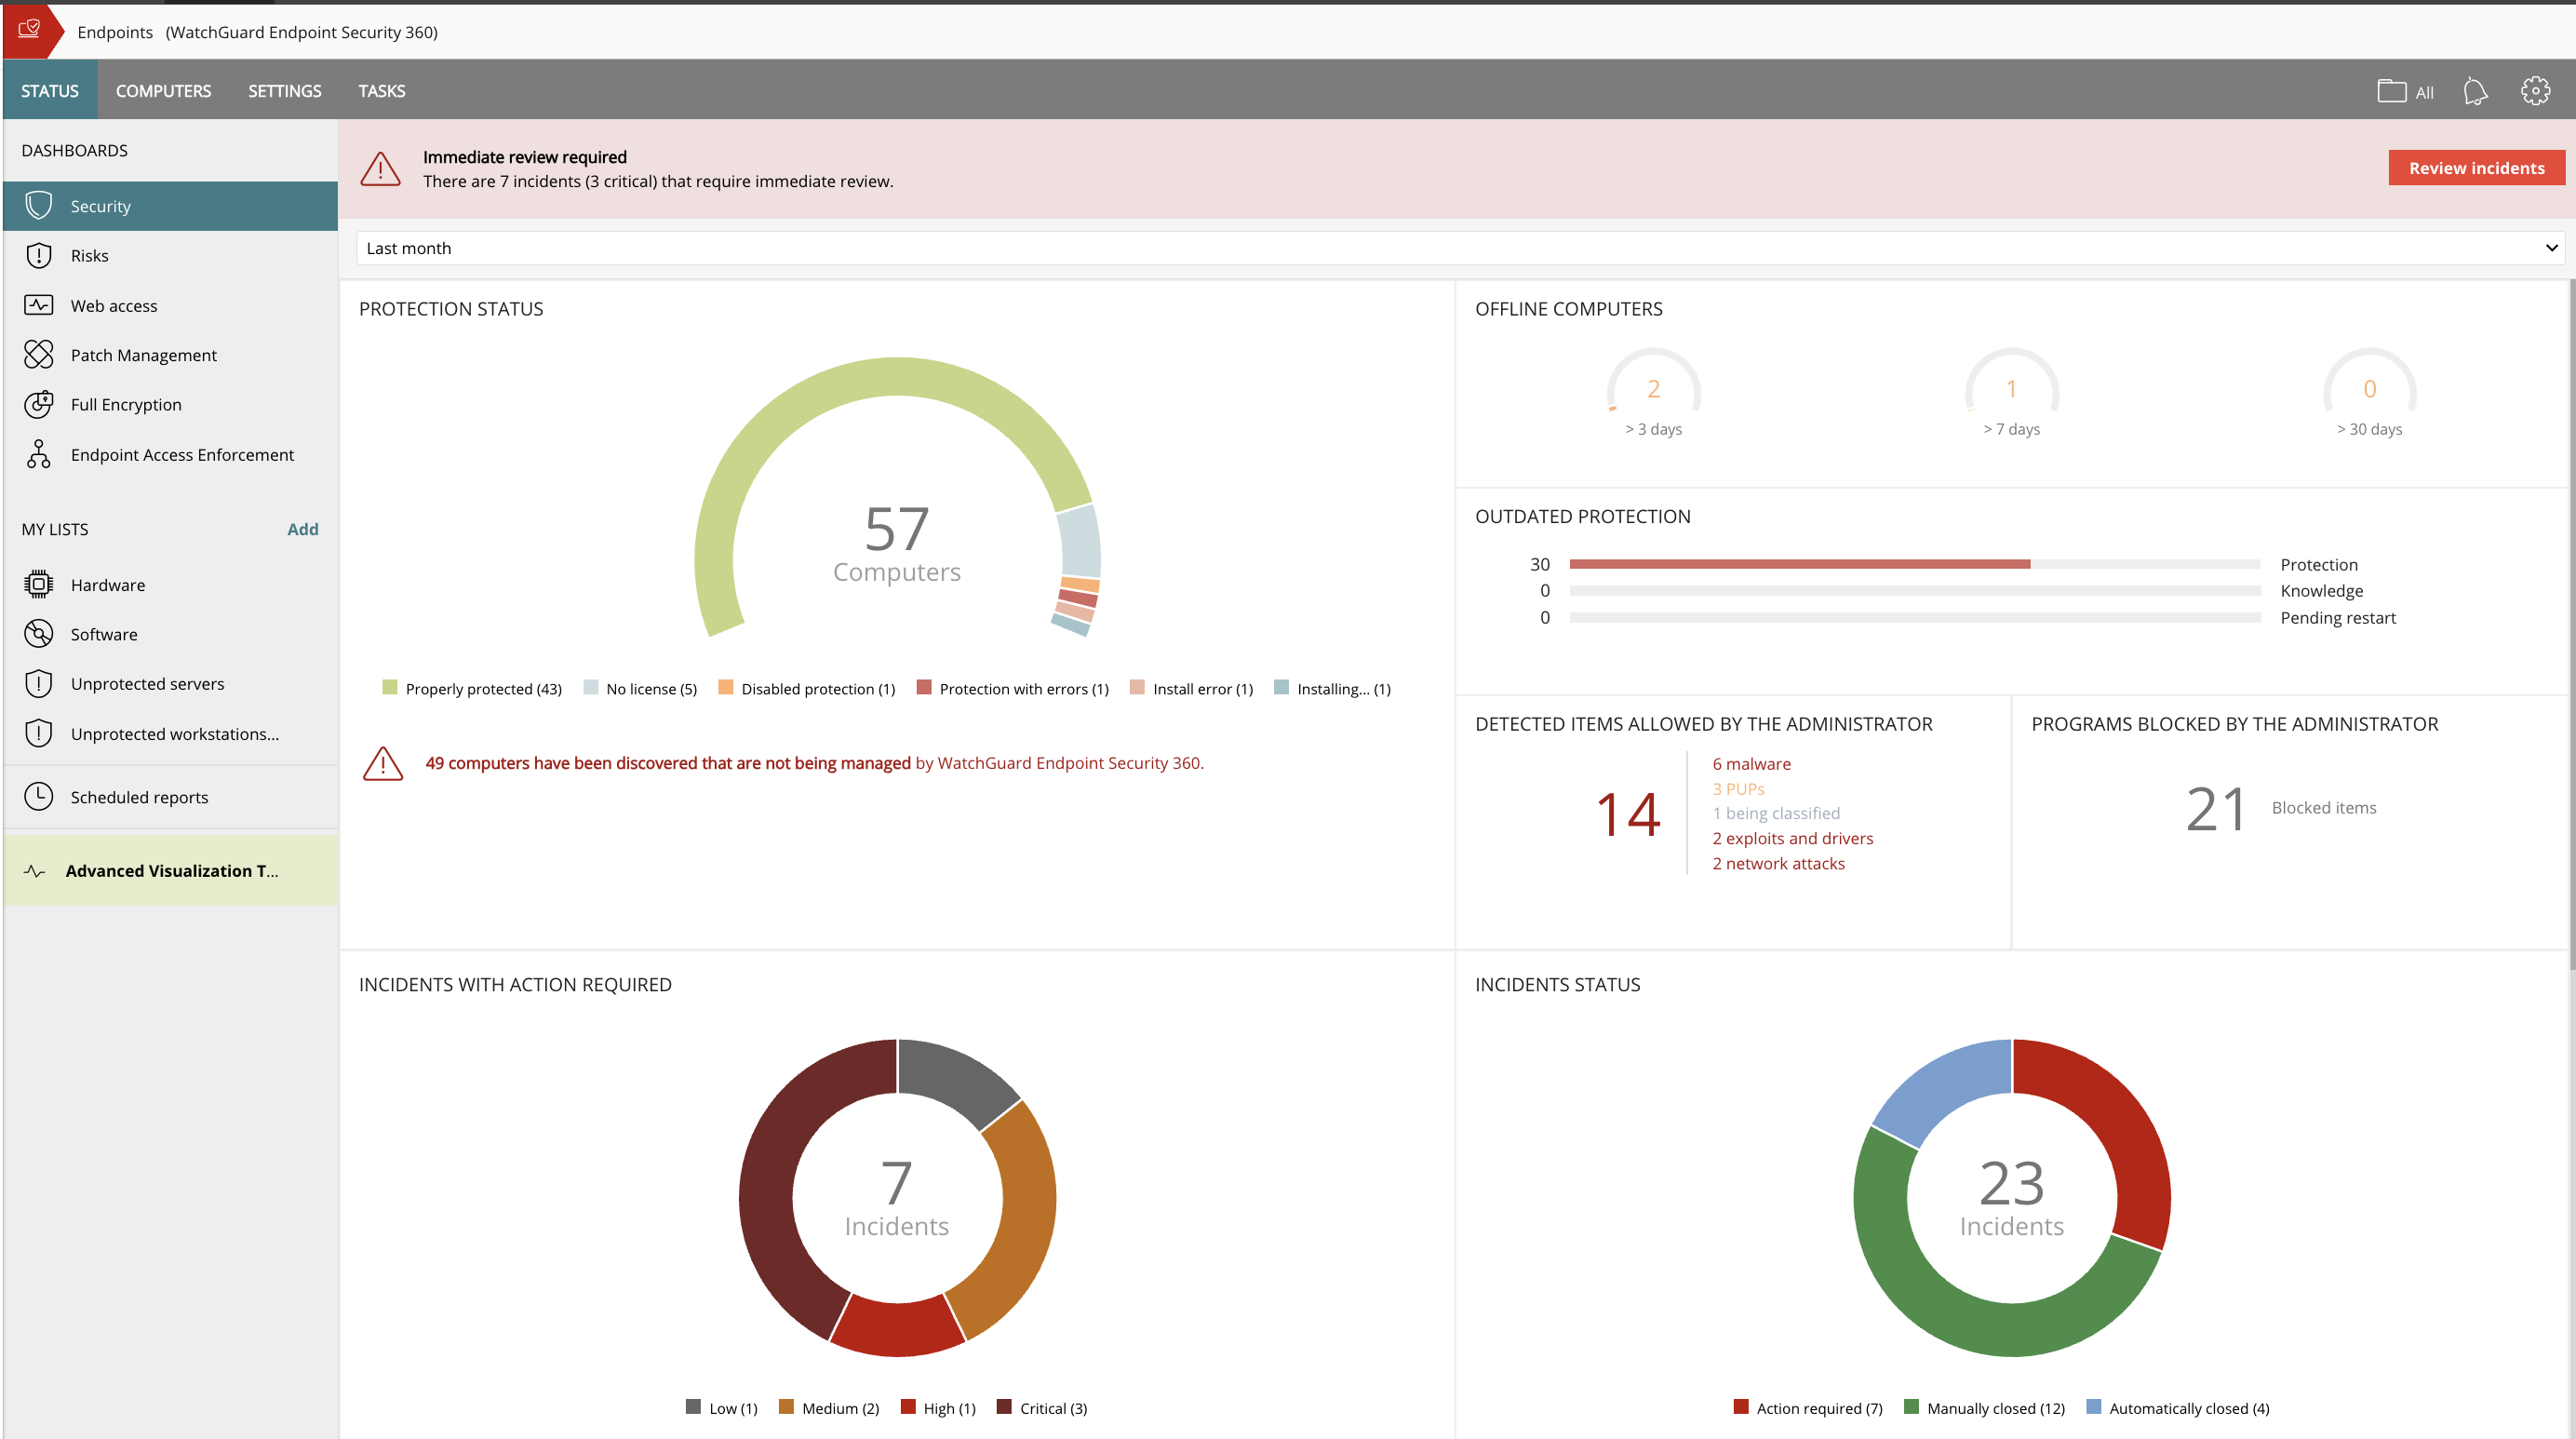
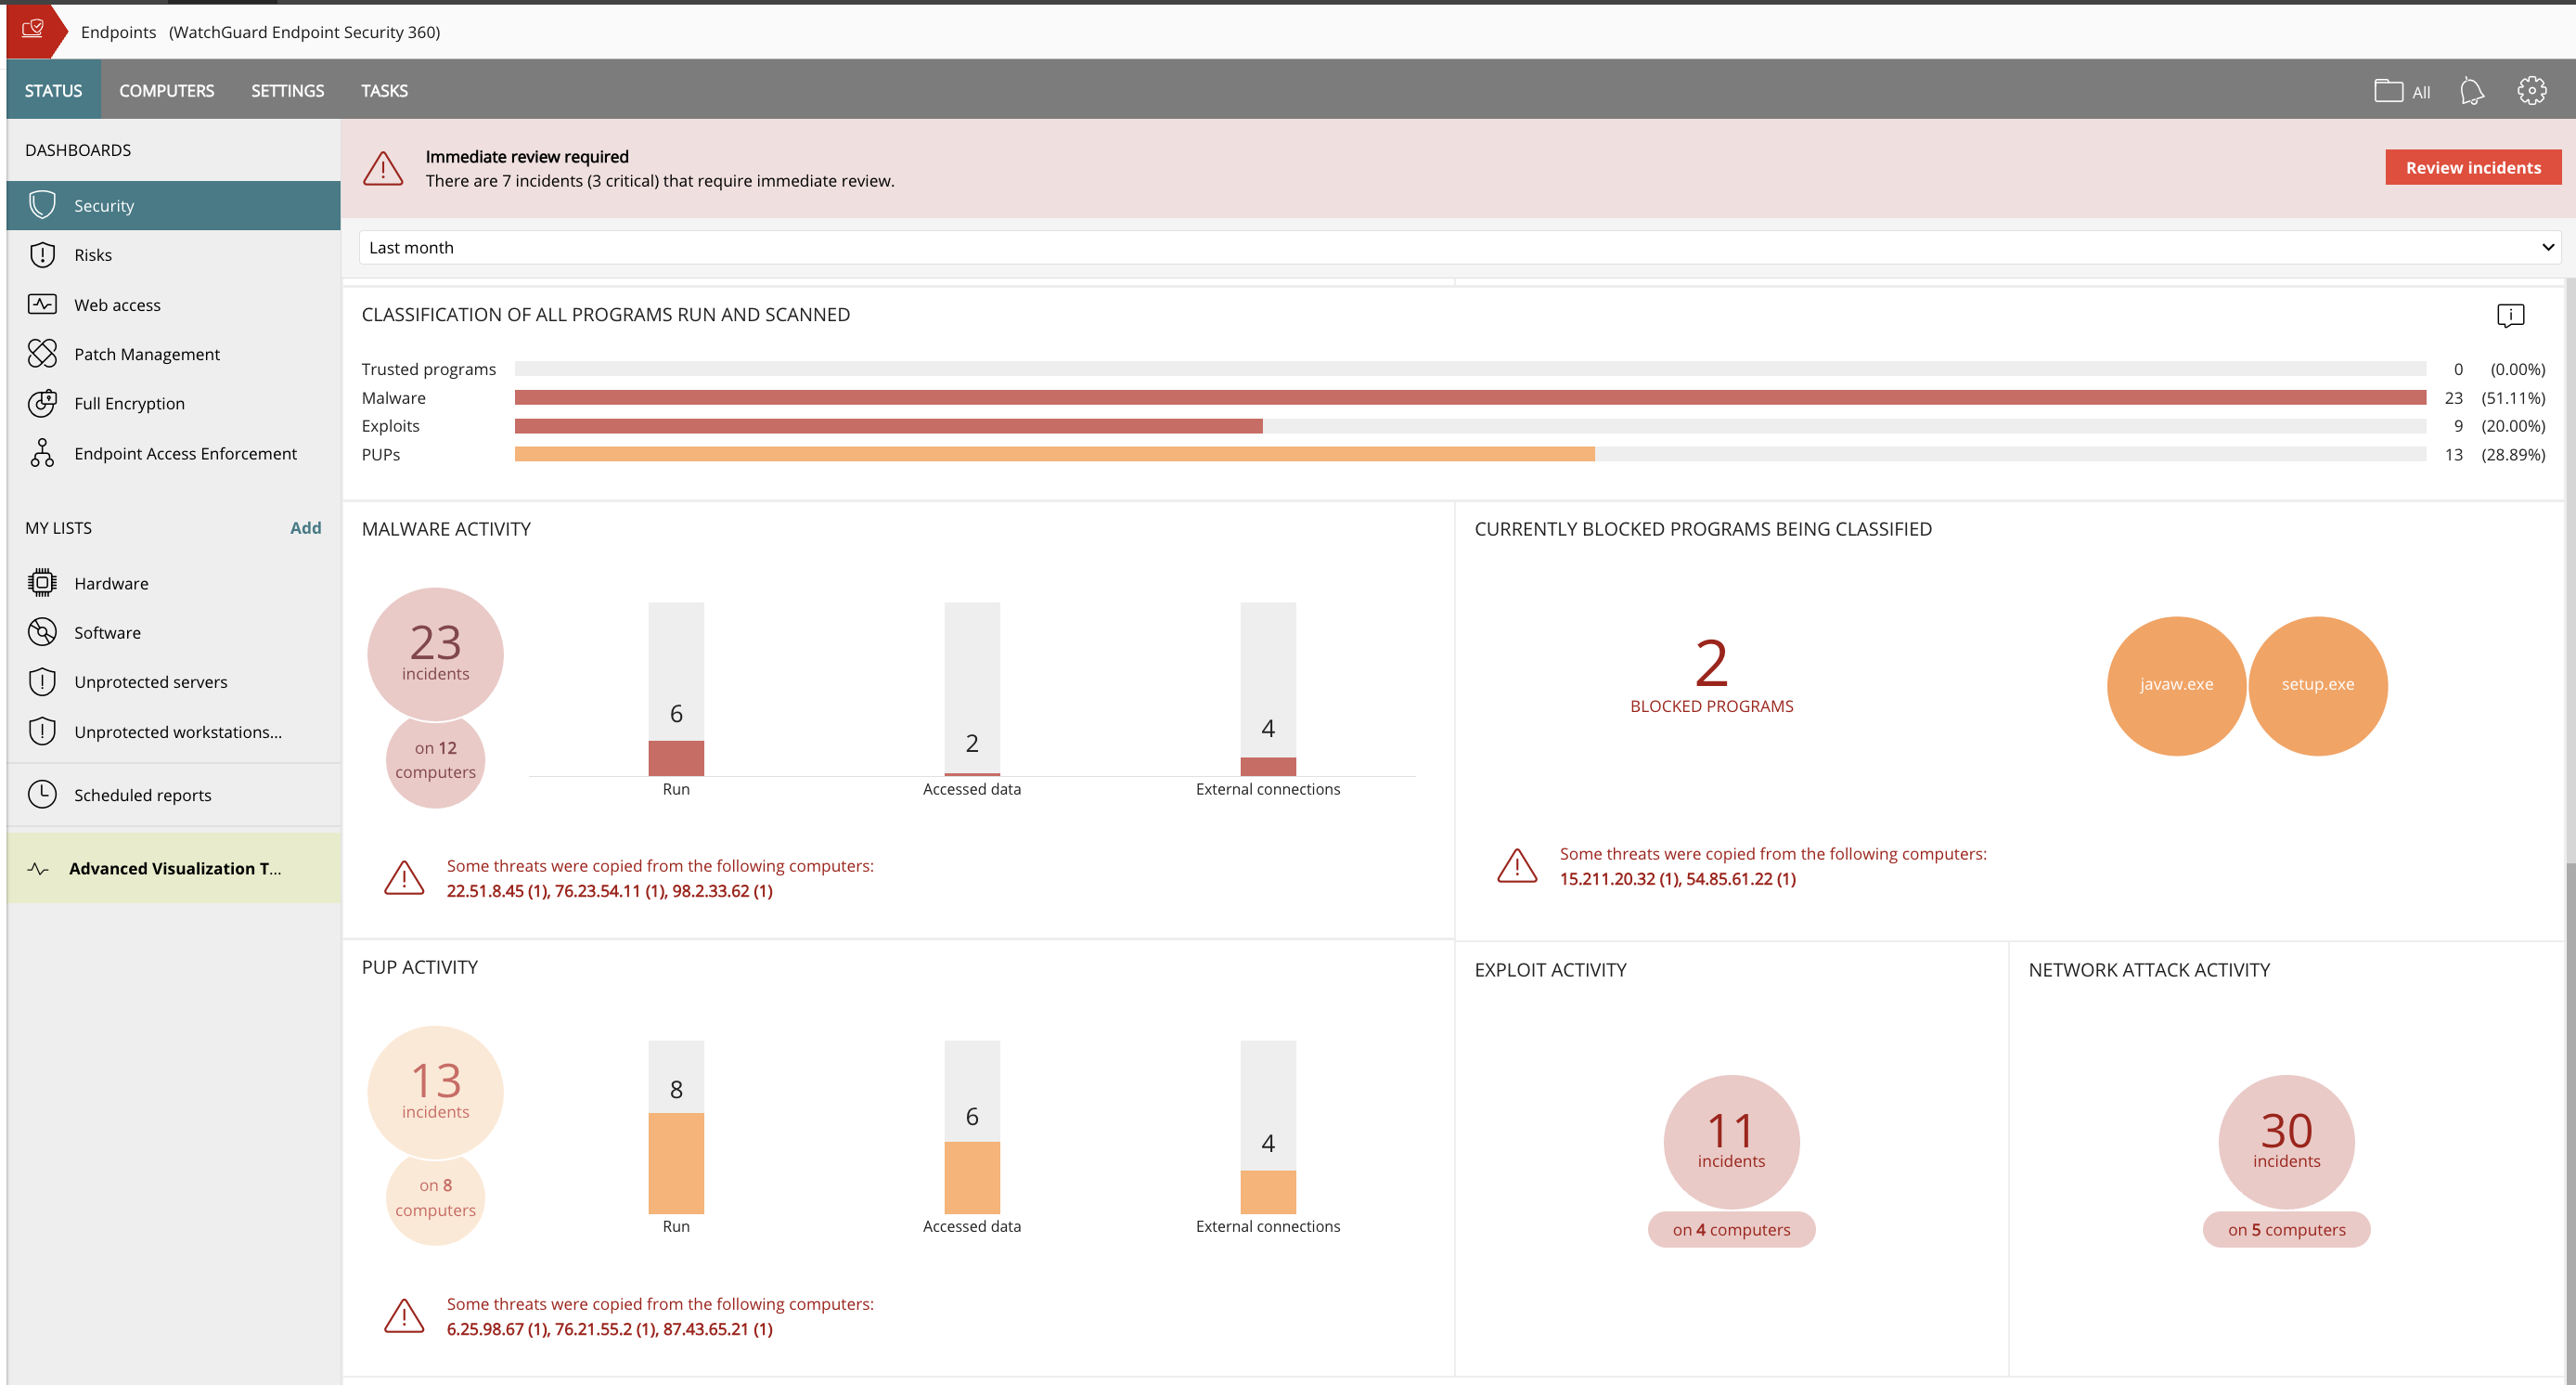
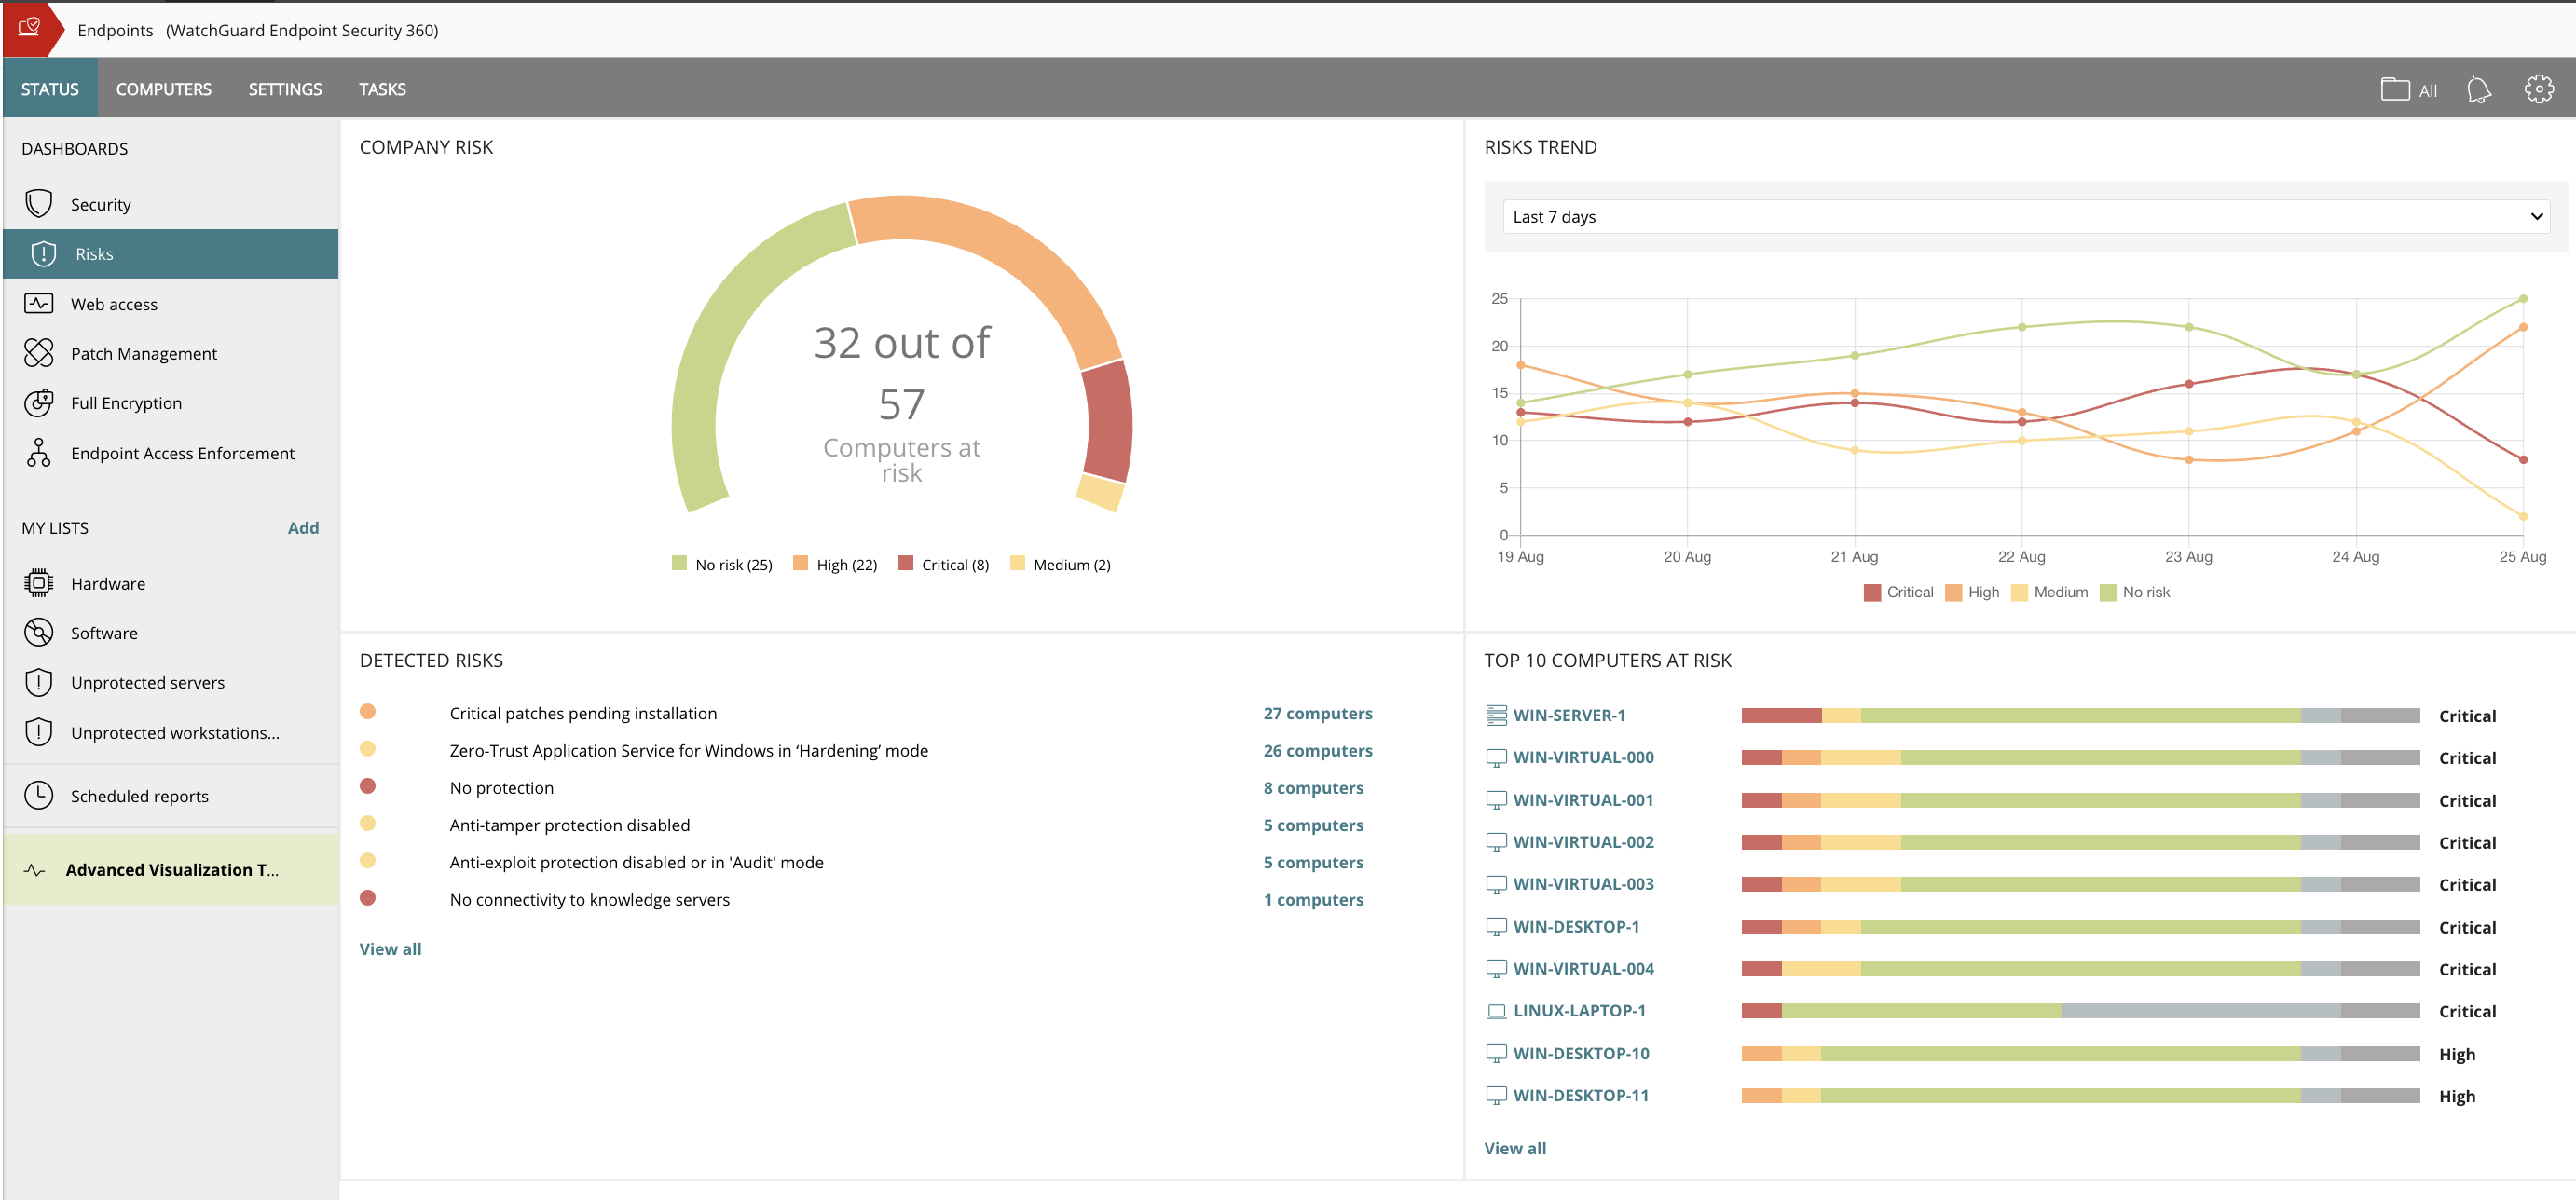
WatchGuard EPDR (formerly Panda Adaptive Defense 360) combines next-generation antivirus protection, endpoint detection and response (EDR), patch management, content filtering, email security, full disk encryption, and more, into one package. The platform touts a unique zero-trust security service that certifies the legitimacy and safety of all running applications thanks to a combination of automated, AI-driven processes and investigation services provided by a team of malware analysts.
Based on my experience, Splunk is a strong git for some environments and a poor match for others. The distinction is primarily based on infrastructure complexity and budget. It's perfect for large enterprises with a mix of on-prem/cloud infrastructure. It's not a perfect match for small teams with restricted resources.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I would recommend Watchguard Endpoint Security to organizations that are already using WatchGuard Firebox with the Total Security suite or those looking for an additional layer of endpoint protection. The bundled licensing provides strong value and makes it easy to extend protection from the network level to the endpoint. In our case, we primarily use it as a supplement to SentinelOne, and it integrates well in that role. The agent has been stable, the cloud management is straightforward, and it has not caused operational issues in our environment. For businesses that want added visibility and layered security alongside their primary endpoint solution, Watchguard Endpoint Security is a solid option.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Writes Powerful Queries: The queries that can be written using the Splunk Query Language are very powerful and highly customizable to meet every need. Ex: Writing queries to search the intersection of two different sources like Network and Endpoint Logs.
Offers Dashboard Abilities: Helps build complex panels for Dashboards in addition to providing several out-of-the-box panels. Ex: creating panels to calculate the performance of analysts in a given timezone.
Helpful Search Aids: It helps to set up complex custom alerts very easily. The interesting fields section is very helpful while threat hunting. Ex: It shows all the users and the frequency of each in a failed login event. The user list on the interesting fields is useful to look for suspicious logins.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Improved User Interface Customization: While the interface is generally intuitive, providing more options for users to customize their dashboards and views would enhance the overall user experience. Tailoring the interface to specific roles or use cases could be a valuable addition.
Simplified Alert Management: Streamlining the process of managing alerts, such as grouping or categorizing them based on severity or type, would make it easier for security teams to prioritize and respond to incidents effectively.
Expanded Threat Intelligence Feeds: Increasing the variety and sources of threat intelligence feeds available within ES would provide a broader context for identifying and mitigating emerging threats, ensuring a more comprehensive defense against evolving attack vectors.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
EndPoint has an optional feature for automatic and remote software updates on endpoints, a handy option for keeping computers up-to-date and secure. However, it is not used to install new software but only to update it. We believe that this part is instrumental, but it is somewhat incomplete.
Another drawback is that some complementary functions to the antivirus, such as the one above, are optional and require a separate subscription.
The implementation of EndPoint requires some planning, especially the time required to harden and learn the system. This is not critical and is typical for this type of system, but it is necessary to plan it well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The ease of use, pricing, support, reliability, and quality of the product. Panda / WatchGuard products are highly rated, priced right and easy to maintain. All of this make it very easy to renew and purchase new licenses for us and our clients.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Maintaining hundreds or even 1000+ SOC use cases is really difficult, considering that the Data sources may not always send the data. A module that detects data freshness issues and detect data format changes would be a great help. the main challenge today using Splunk Enterprise Security is making sure that the detection rules are still working properly given all the changes that occur in data source applications. Also, maintaining the data collects on tens of thousands of servers and more than 100k workstations is a real company IT challenge: the splunkbase forwarder may not support old OS anymore, while these are the most important to monitor. Moving to the Open Telemetry collector has become essential so that only 1 agent is required for both SIEM and application observability.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Easy and intuitive MSP management portal to manage all of your clients from a single pane of glass. Policies can be pushed down globally or individually based on needs. The client portal allows access to their tenant information and installs only which is nice if you are working with clients who might have an internal person or an IT team that also wants access to things to manage themself.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The software is 100% managed on a cloud platform that can be managed via an account even if they are not present within the company network where the software is installed, I even always opened the control panel on the browser of my smartphone to monitor the situation.I have never experienced any abnormal software crashes
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It takes a long time for items to load if you are just generally searching through logs. It is best to use the data models which load faster but can be strange in terms of what is coming from which logs where. Yes, you can look it up, but this also requires familiarity with where things are and how to look them up.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The only annoyance I complain, if we want to be picky, is the fact of the constant disconnections from the control panel.Every about 4 hours the account logs out even if I set the "remember this device" flag; having said that I have not noticed neither slowdowns nor conflicts with other software
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's good when it's responsive, but I've had times where I had to wait quite a while for a response. But these are typically the exceptions rather than the rule. When you do get a response it is always well-informed and appropriate. I would say they've been trending better over time with this.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I gave it a 10 because I compare it to air conditioning. I need it to work every day, 24/7. I need it to be reliable and not something that requires a ton of interaction from staff to make sure it works every day. In addition, I should be able to run other things at my house when the AC is on. Panda fits that description.
I experienced only on-line training, but the trainers were very professional and competent. Maybe it could be more useful if they also have an experience in projects because sometimes they didn't have a real project experience to communicate to the students. Anyway, it was very interesting and I learned many thing that's very difficoult (or maybe impossible!) to have by myself, aven if I have more than 10 years of Splunk activity experience.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It was very interesting and I learned many thing that's very difficoult (or maybe impossible!) to have by myself. The only problem was that, when I worked with the Splunk Professional Services, I found some difference between the training contents and the information from PS. In addition is required a long experience on Splunk Enterprise for the data ingestion part, in other words I'm able to work with ES because I'm worling on Splunk since 11 years, otherwise I'd some problem.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The training was very helpful. It demonstrated how to configure the service for initial install, items to monitor, and how to set up for ongoing protection. Hands on training is more helpful but this is a good starting point
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Implementation shouldn't present any problems in standard office environments. In environments with development teams, however, caution is needed. If zero trust is enabled, mechanisms must be in place to ensure that internal software isn't classified as a false positive (software certificate, exception folder, etc.)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Splunk enterprise is the only solution that we’ve been able to identify that provides risk based alerting, which allows our SOC to reduce analyst fatigue which would be a huge problem without it. Before RBA, there were thousands of alerts a day and it was impossible to review all of them
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We didn't spend much time looking into Symantec - but it was the software of choice for the district before I joined. That said, we were pretty easily talked into Watchguard Endpoint Security as we were already in the Watchguard world of products. Moving to their EDR just seemed to make sense for our organization
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
for my exterience, unit pricing and billing frequency are correct. As I already said, I hint to have more discount flexibility, expecially with new customers, because there are competitors less expensive and very aggressive that are dangerous. In addition the possibility to don't pay the license for the development period could be a very interesting feature for the final customers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
- 8 out of 10 and took 2 for the data pipeline and administration part. Even if you'd like to improve yourself or your team, you have to pay a lot of money and it could be more than GIAC education + cert. - Normalization for Data models and CPU-based searches can be a problem sometimes.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
With the implementation of watchguard (at the beginning Panda Endpoint, but it is the same) I was able to insert in the control panel all the unauthorized software previously installed by colleagues without any authorization from the various department heads.Now any licensed software goes into lockdown and can be unlocked from the control panel
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I had a fantastic experience with Splunk Professional Services: they worked with us in our last SON project (a SOC migration for a very large customer) and helped to build a multi tenent environment even if ES isn't a multi tenant platform. Th Splunk PS was a very professional and competent people, he is italian and was able to speak with our italian customers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have a 100% success rate on all our ES implementations due to the amazing documentation and Splunk enablement on the subject.
Our Splunk ES business has grown 100% YoY for the last 3 years.
In terms of long term management and maintenance, ES has been highly stable and predictable, reducing our overhead on costly services team for ad hoc maintenance work.
By committing to go all in on Watchguard Advanced EPDR across our whole client base, we maximized our price position - enabling us to offer the best endpoint security at a price better than what lesser competitive products cost.
Leveraging Watchguard Endpoint Security as part of our unified platform strategy provides better integrated security, managed through Watchguard's cloud architecture. This significantly reduces our cost to deploy, manage, and support our client's. Our improved security offering, better delivery, and stronger price position has helped us achieve 56% growth in our managed services business over the past 18-months.
Organizations that have disparate cyber security products often require specialists for each solution in their stack. Watchguard provides outstanding training resources that equip our entire technical staff - significantly improving our service delivery while lowering our overall cost of business.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info