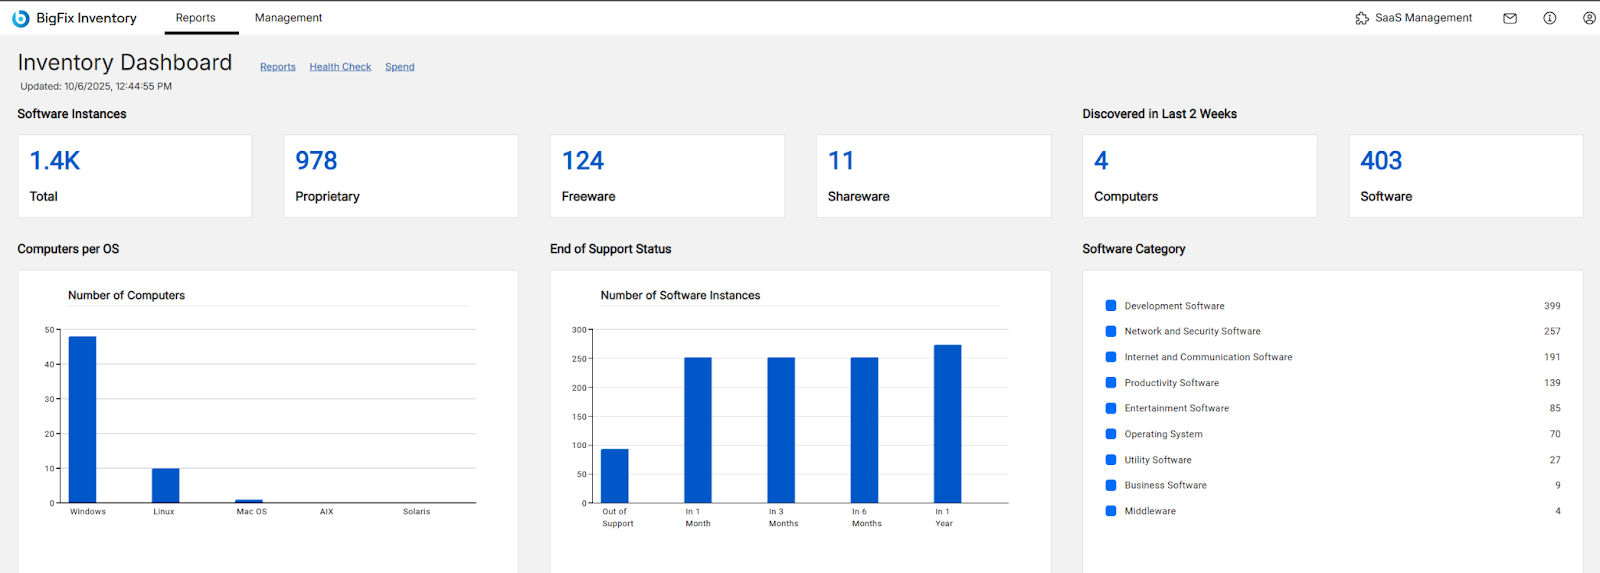
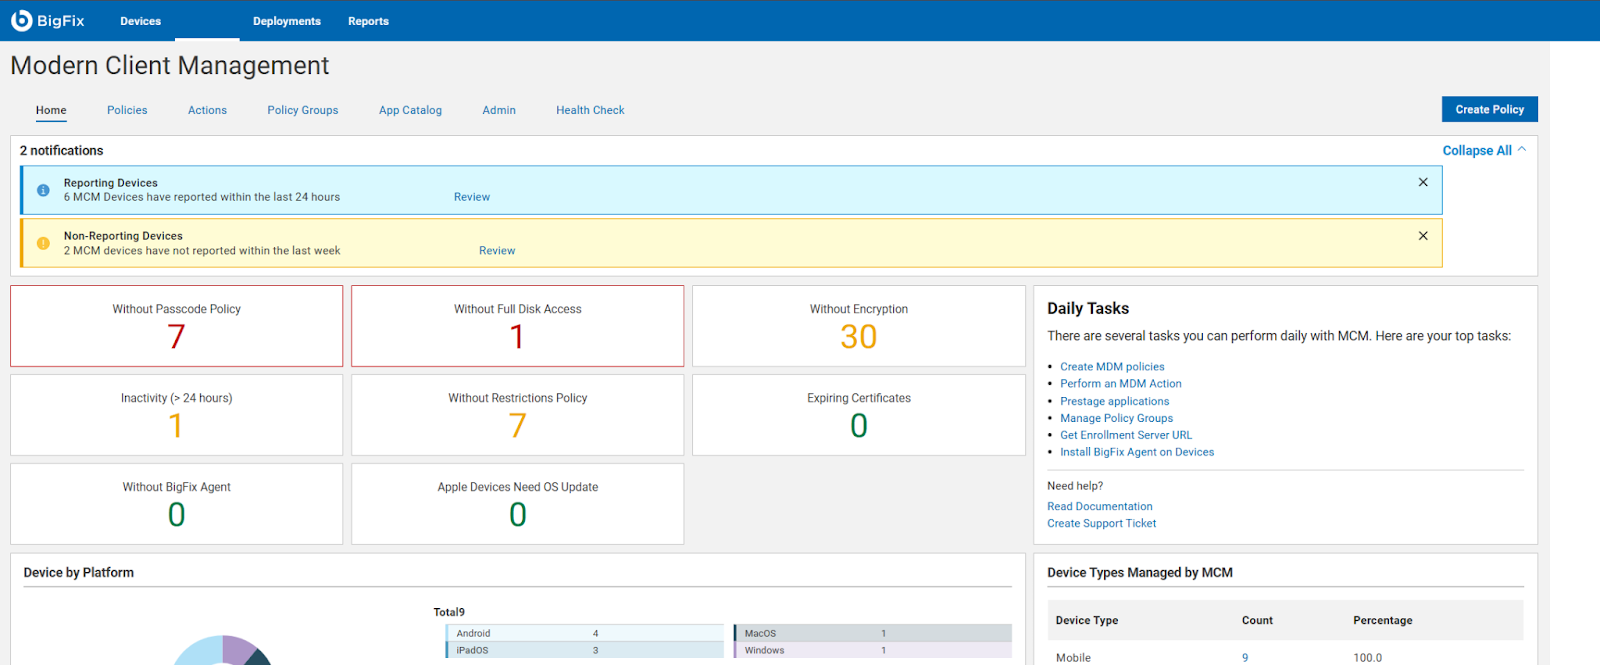
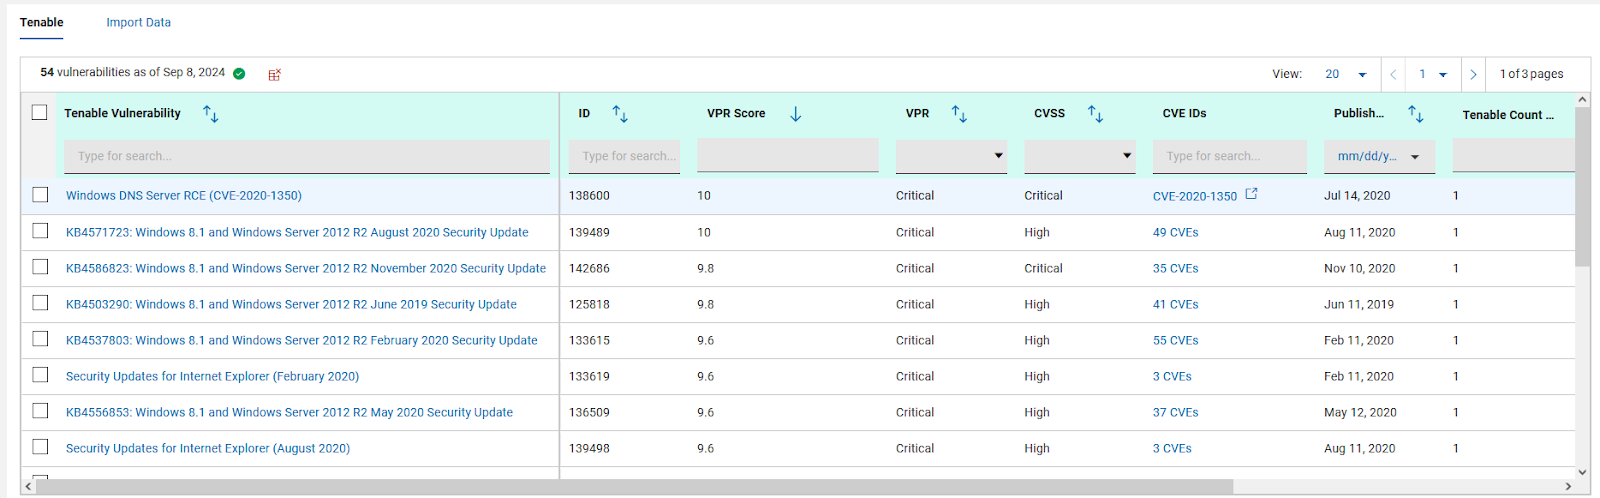
BigFix, now supported by HCL Technologies since the acquisition of BigFix from IBM in 2018, is an endpoint management solution providing endpoint visibility and IT asset discovery, automated endpoint patching (BigFix Lifecycle and BigFix Patch) policy enforcement (BigFix Compliance), and software asset discovery for licensed and unlicensed software (BigFix Inventory).
N/A
Huntress
Score9.5 out of 10
N/A
Huntress is a security platform that surfaces hidden threats, vulnerabilities, and exploits.
The platform helps IT resellers protect their customers from persistent footholds, ransomware and other attacks.
N/A
SentinelOne Singularity
Score9 out of 10
N/A
SentinelOne is endpoint security software, from the company of the same name with offices in North America and Israel, presenting a combined antivirus and EDR solution.
Chief Technology Officer in Information Technology at DNA Solutions and Consulting (Information Technology & Services, 11-50 employees)
Chose Huntress
Easier to add and remove the agent from PCs. In our experience, others are horrendous to try to remove when a customer leaves. The UI is superior through its simplicity. For us, deployment was also much easier than BlackPoint or SentinelOne. Webroot was easy to install, but …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Huntress
To be honest, I haven't run into anything like Huntress. It's not a threat protection platform and it doesn't simply look for configuration changes. It is a unique product that starts with searching for footholds and grew into educating the user base on what cybersecurity is …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
EVP in Information Technology at Solis Security, Inc. (Information Technology & Services, 51-200 employees)
Chose Huntress
This is a difficult question because Huntress really doesn't compete with other products per se. There are EDR products that tout the same capabilities as Huntress, so if you were to compare just those features, you would still see Huntress as a winner because they are …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
CIO (Chief Information Officer) in Information Technology at MicroAge (Information Technology & Services, 11-50 employees)
Chose Huntress
Firstly from a business model, [VMware] Carbon Black [Cloud Managed Detection] was not outfitted for the MSP where Huntress is very MSP-friendly from an affordably easy point to entry to value for money licensing. Carbon Black TS is not bad in anyway, well, that we found, but …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Patch Management for Diverse Devices: HCL BigFix is ideal for organizations with a diverse range of devices, including laptops, desktops, cloud, virtual machines, and mobile devices. Its endpoint management functionality enables seamless patching across various operating systems such as Windows, MacOS, ChromeOS, and Linux.
Comprehensive Patch Management: With HCL BigFix, organizations can achieve comprehensive patch management across their IT infrastructures. It ensures that all endpoints, regardless of the operating system, receive timely and secure patches, reducing vulnerabilities and enhancing overall security.
Troubleshooting and Monitoring: HCL BigFix excels in providing a dashboard that effectively displays problematic and functional machines. This feature allows IT teams to quickly identify and address issues, improving overall troubleshooting efficiency. However, there are some scenarios where HCL BigFix may be less appropriate or areas for improvement: 1. Coverage Expansion: It is important for HCL BigFix to continue expanding its coverage to include all possible resources installed within the IT infrastructure. Ensuring comprehensive coverage can enhance its effectiveness. 2.On-Site and OS Upgrades: Optimizing the process of on-site and operating system upgrades can help streamline the deployment process further. Improvements in this area would contribute to a smoother and more efficient upgrade experience. 3.Communication Speed: Enhancing the speed of communication between the HCL BigFix agent and the server can help improve the overall responsiveness and efficiency of the solution.
Pricing Optimization: Adjusting the pricing of HCL BigFix to be more cost-effective would make it more accessible and attractive to organizations of different sizes and budgets.
Huntress is great for a managed service provider to provide a better cybersecurity stack to their endpoints/customers. Some smaller clients cannot afford high-priced SOC services but require SOC-level protection. Along with a couple of other layers of security, Huntress provides peace of mind for the MSP that if a threat were to arise, they would be notified with specific instructions for dealing with that threat.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It works extremely well for investigating the root cause analysis of events because you can see so much detail into what was happening before, after, and around the detective incident. A weak point would be when the AI gets a little over-aggressive or doesn’t quite understand the use case for specific tools. Our RMM tool was detected as a pup.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Using the latest industry knowledge of threats that have been ongoing, but not previously known and projecting it back in time against their installed endpoints to identify machines that are vulnerable or breached and when it these events occurred
Very quiet. If they alert, it is a thing.
Very good at remediation.
They communicate extremely well when it matters.
While there are the most extensive products more often than not they are the first to alert us to a threat.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We dropped SentinelOne in favor of Huntress because the UI was much more simplistic for the tier 1 techs to maintain. It beats the old web design model of three clicks to where you want to go. It is very intuitive. No one needs training to figure out how to navigate its console.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
There are some minor issues with the platform that can be mildly frustrating, but the overall performance, peace of mind, and ROI make it worth using. The management console is intuitive and easy to learn, the endpoint clients are simple but give IT professionals enough data to make management easy and simple
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Their support is good and quick to respond. The one issue we faced was when a non-protection issue arose there was a lot of dancing around trying to figure things out. This was frustrating as it took significantly longer to figure out issues. Lots of repetitive log gathers, screen caps, uninstalls that never seemed to resolve issues. Eventually, the product would be updated and the issue seemed to be resolved, but seemed to be the only solution.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have significantly enhanced our ability to patch desktops, including laptops, desktop, cloud, virtual machines and other mobile devices used by end-users. BigFix's endpoint management functionality allows us to seamlessly patch a wide range of operating systems, such as Windows, MacOS, ChromeOS, and Linux systems, ensuring comprehensive patch management across IT infrastructures. We have established a track record of delivering secure and hassle-free patching solutions to our clients
Firstly from a business model, [VMware] Carbon Black [Cloud Managed Detection] was not outfitted for the MSP where Huntress is very MSP-friendly from an affordably easy point to entry to value for money licensing. Carbon Black TS is not bad in anyway, well, that we found, but Huntress is a new layer of security that fits between the OS and AV layers to provide additional information, monitoring, and detection. With Huntress backing the MSP, [it] sure does help as well.
SentinelOne had all of the major features that we were looking for. The other products either required too much administrative attention or were lacking key features. For example, one could be uninstalled by the end user. We required that the installation be password protected to protect against end user disabling or uninstalling. One product required manual intervention for all remediation which put to high a burden on limited staff. All products are always being revised so these may no longer be issues but they had a significant impact on our decision.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SentinelOne has already proved its value by stopping attacks that would have gone otherwise unnoticed until much later in their infection process.
The Vigilance team has provided quick response to threats that were not easily contained via the automated response SentinelOne's agents provide. This has given us a significant piece of mind.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info