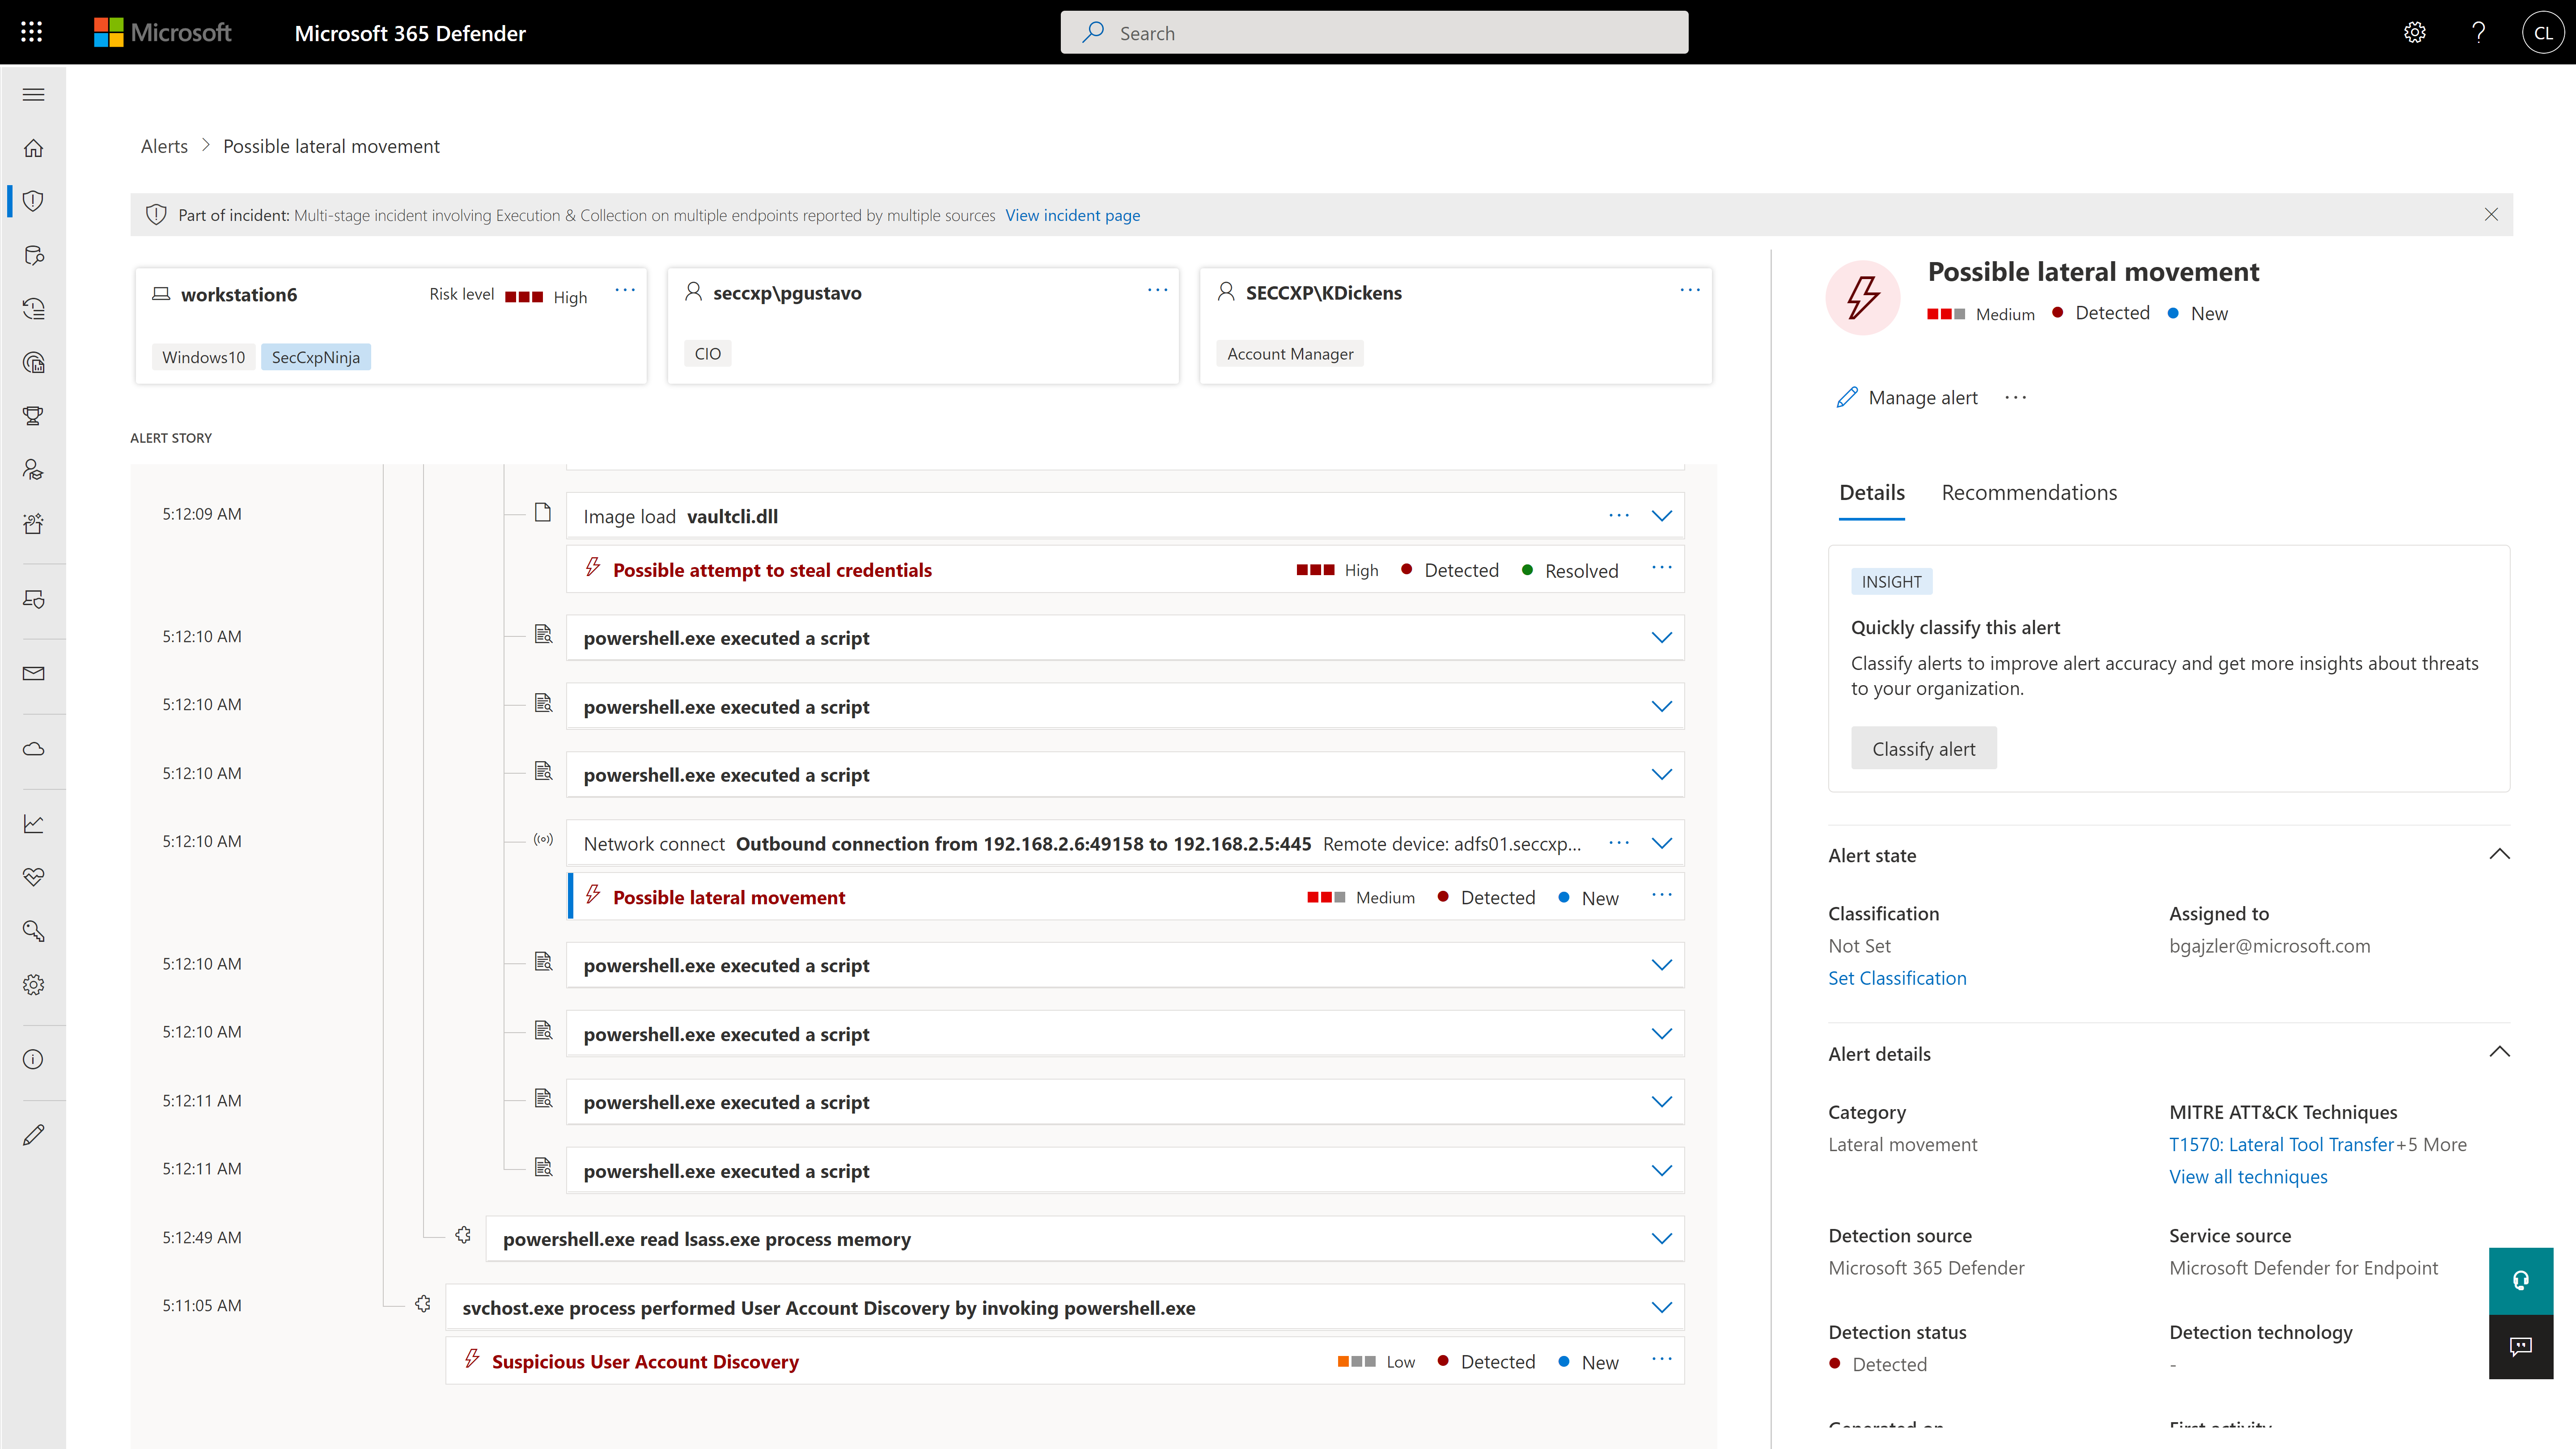
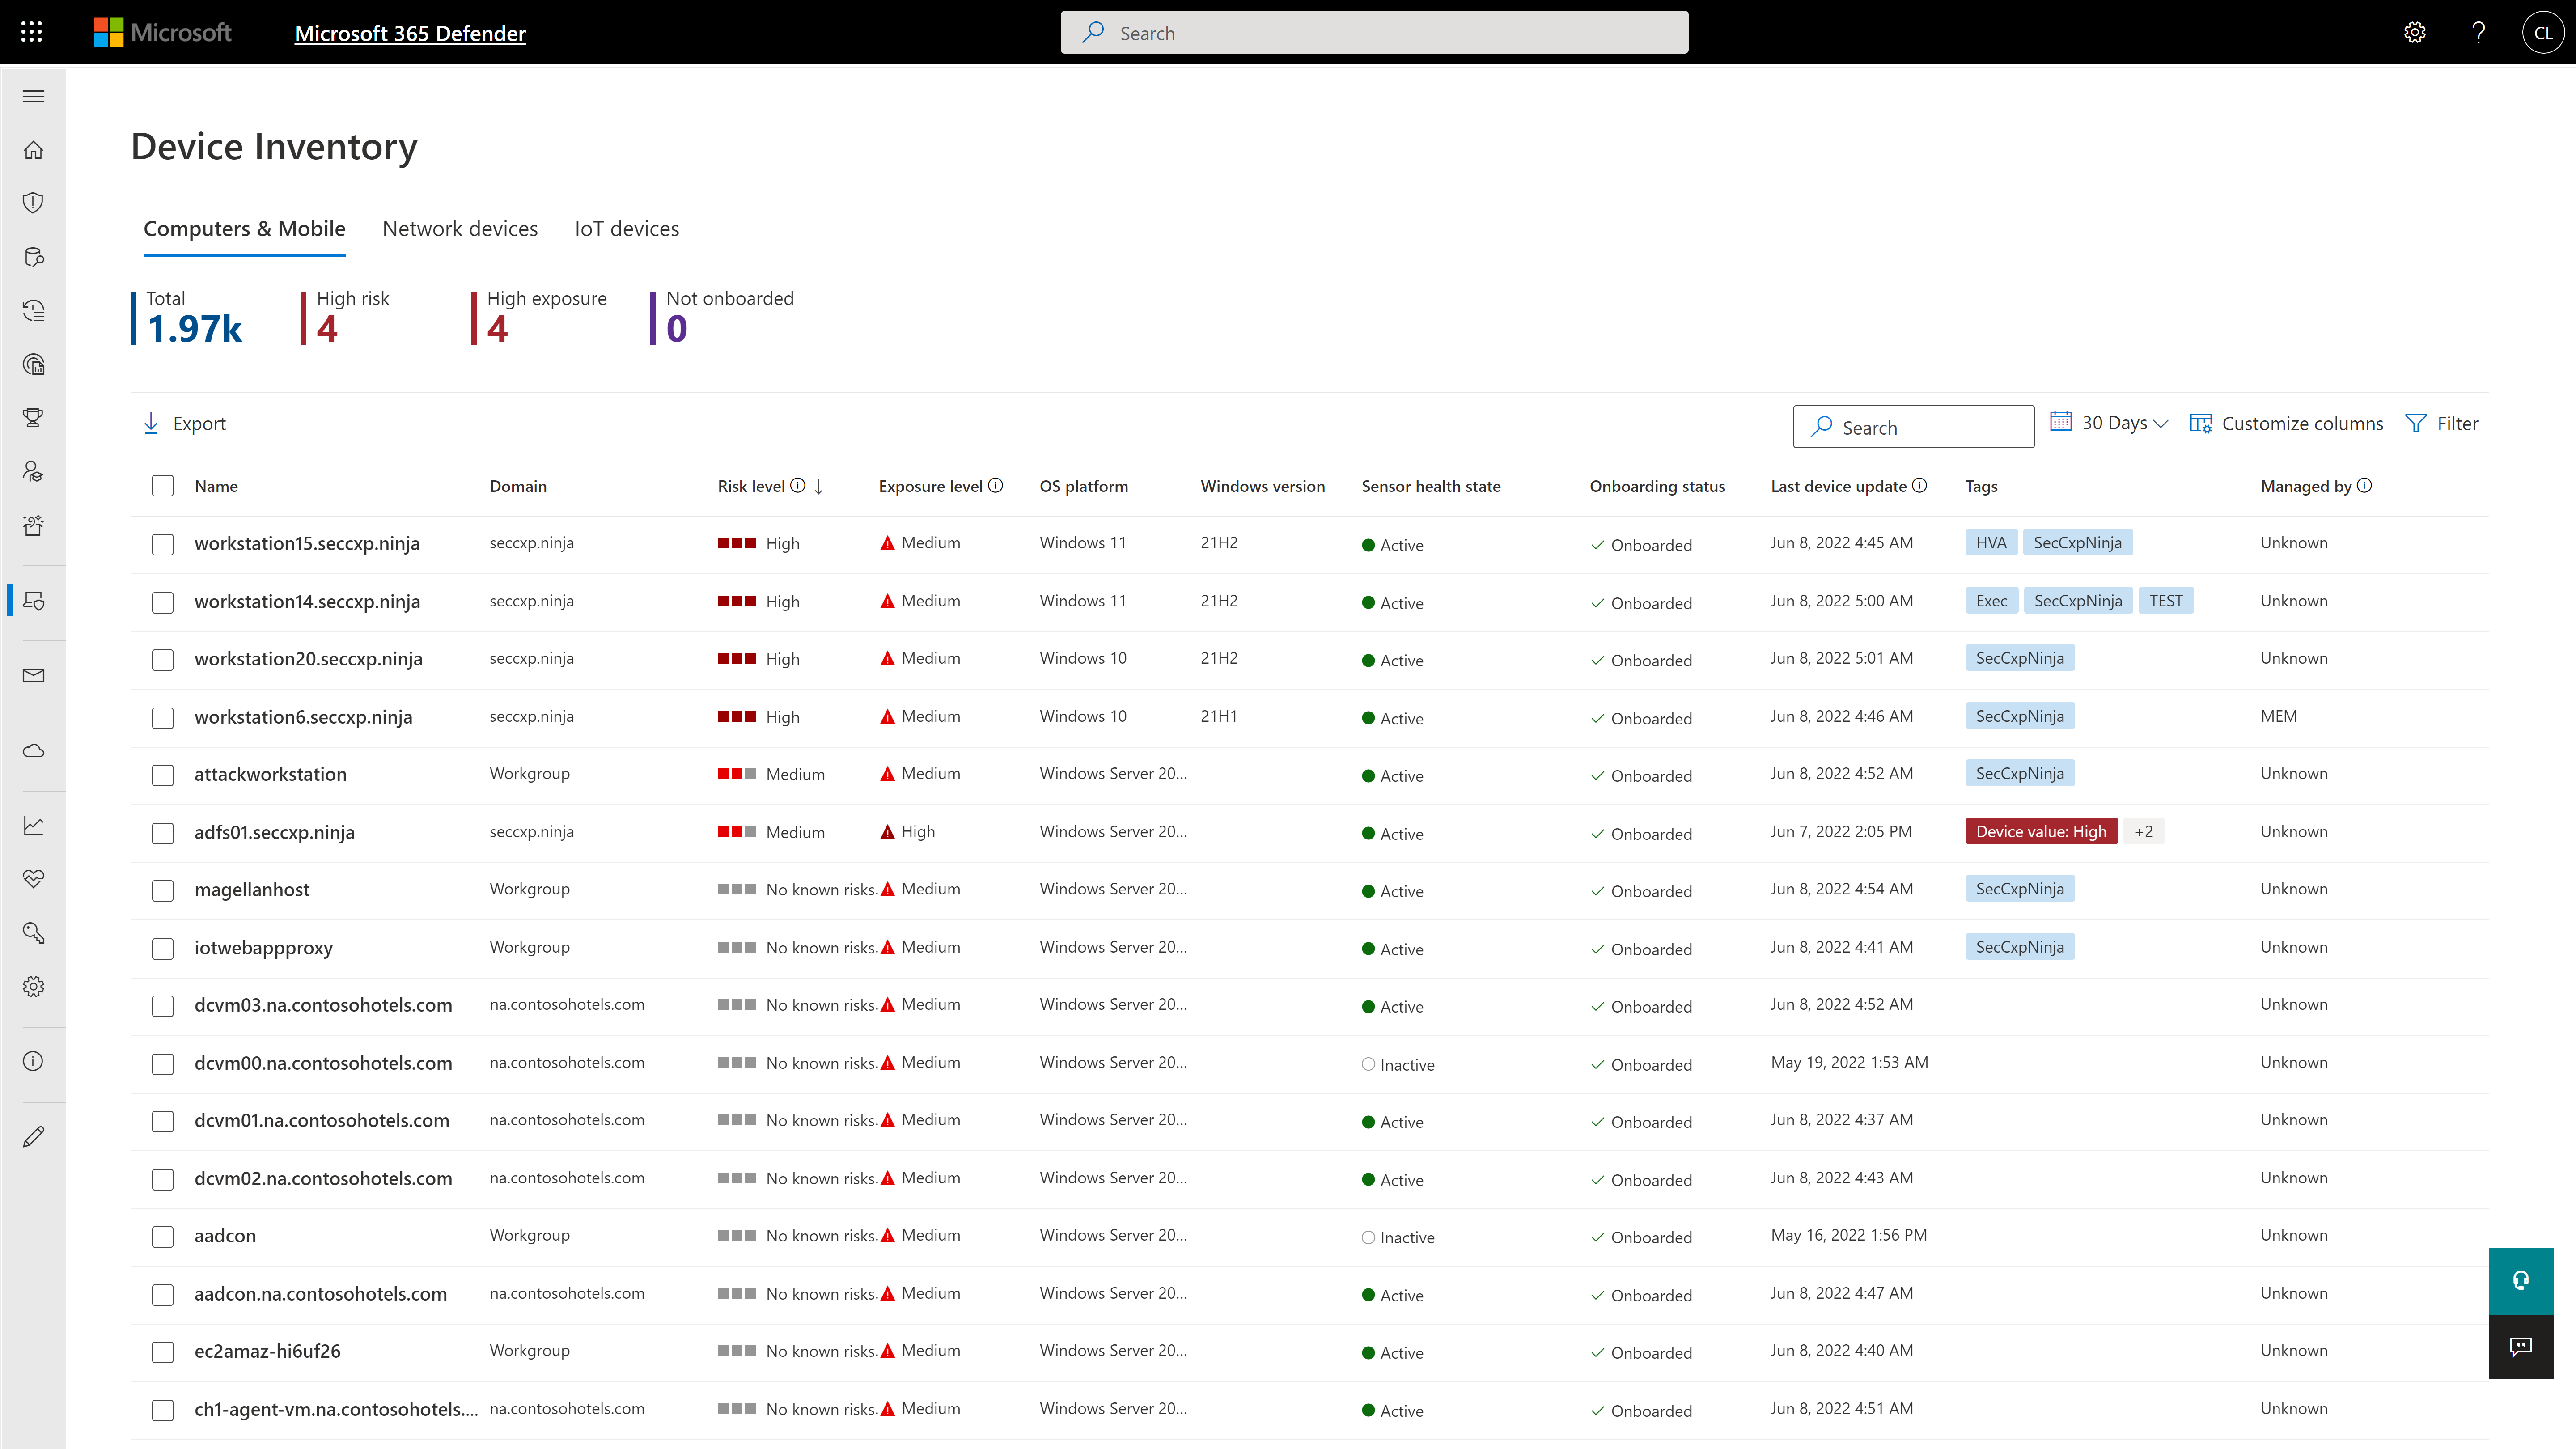
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Proofpoint Security Awareness Training
Score10 out of 10
N/A
Proofpoint Security Awareness Training (formerly ThreatSim from Wombat Security) is a cloud-based training platform that simulates threat scenarios (e.g. phishing) and also provides assessment testing developed by Wombat Technologies, which was acquired by Proofpoint in March 2018.
The "Managed Service" (a dedicated ProofPoint Account Rep c/w weekly status calls) significantly reduces the resource demand on the area within your company managing the program. The KnowBe4 Platform does all the same stuff (Training Modules, Reports, ThreatSim Tools), but you …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Perfect for regular (monthly) training of staff versus a "one and done" annual assignment on Cyber Security. Allows for a greater number of topics to be covered and for creating a "culture" of security awareness among all Staff throughout the entire company. NOT a replacement for IT Security Certifications amongst your technical staff (CISSPs & GSLCs on staff are a must have). Your Proofpoint Account Rep does most of the heavy lifting, but the program still requires "care and feeding" (resources) within your organization - preparing monthly user lists for training assignments and preparing reports for leadership on participation & progress
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The lack of a user rating on "cyber risk" is proving to be an immense difficulty. As we are looking at how to better hold our employees accountable as well as provide increased learning opportunities for those who need it most, it is becoming cumbersome--especially given the fact this is starting to become the standard for Security Awareness companies. The lack of this is resulting in a manual process vs being able to automate and moderate, thus taking up time and resources, which are always at a scarcity. It can also be cumbersome to look across the tools to see how a particular user is doing, vs being able to view all of their data in one space.
If you are a marketer, the editors for the Phishing Templates and Teachable Moments are quite frustrating. They feel out of date and clunky, as well as not featuring an auto-save, so you could lose the templates you are building. At this point, I have actually started to work in other email creation editors and learning HTML, to better customize and then moving all of the code into the editor. It has thus far proven to be less of a headache. I also do not believe the average user is working on branding their program, creating consistency for easy of navigation, and including additional resources in their teachable moments in the way we currently are. However, as more social science backgrounds continue to enter security awareness, I believe this will move towards the norm.
Some of the reporting numbers for Simulated Phishing could be better. For example, telling me how many people acknowledged the teachable moment out of the full email campaign is less meaningful than knowing how many people acknowledged it, from those who actually triggered/were shown the teachable moment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We have a good relationship with our vendor/Proofpoint, which I believe is needed to be successful in Security Awareness and using tools like this
The package/service as a whole is incredibly helpful
The integrations with Proofpoint's Trap is one of the most valuable things we could do. It turns your entire email user base into members of IT security, to be on the look out to report cyber attacks, and have them pulled out of everyone's email if the email is condemed/found malicious.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Overall, PSAT is integral to what we do. PSAT is a helpful tool to help us improve our employees ability to recognize, report, and respond to phishing. It works for us to use a longterm partner, who is incredibly helpful/supportive, and also bringing Proofpoint's greater cybersecurity & attack intelligence into PSAT. Honestly, we are pretty happy and would make the choice to go with PSAT again (we evaluated the major players in the space via Gartner's Magic Quadrant). The team behind the products are excellent and the product of itself is both intuitive and expansive. This combination allows us to reach our 10k+ employees who are located in over 20 countries
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Proofpoint support has always been above average. A lot of companies provide a customer service manager for your account but few have proved as connected as Proofpoint. The CSM was able to give us a good start with the product and checked in periodically. I found them always helpful with any questions and very knowledgeable about the platform.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
All three products have the pros and cons. Since we use other Proofpoint products, TAP, TRAP, etc. the integration with PSAT is much better. The other products do not integrate with TRAP nearly as well as PSAT.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positively made our staff more aware of current phishing threats.
Gives our staff a sense of accomplishment when they recognize a phishing email.
Helped reinforce our values in the mandatory Information Security training each employee takes (for example, they are already aware of the signs of a phishing email before they take the training).
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info