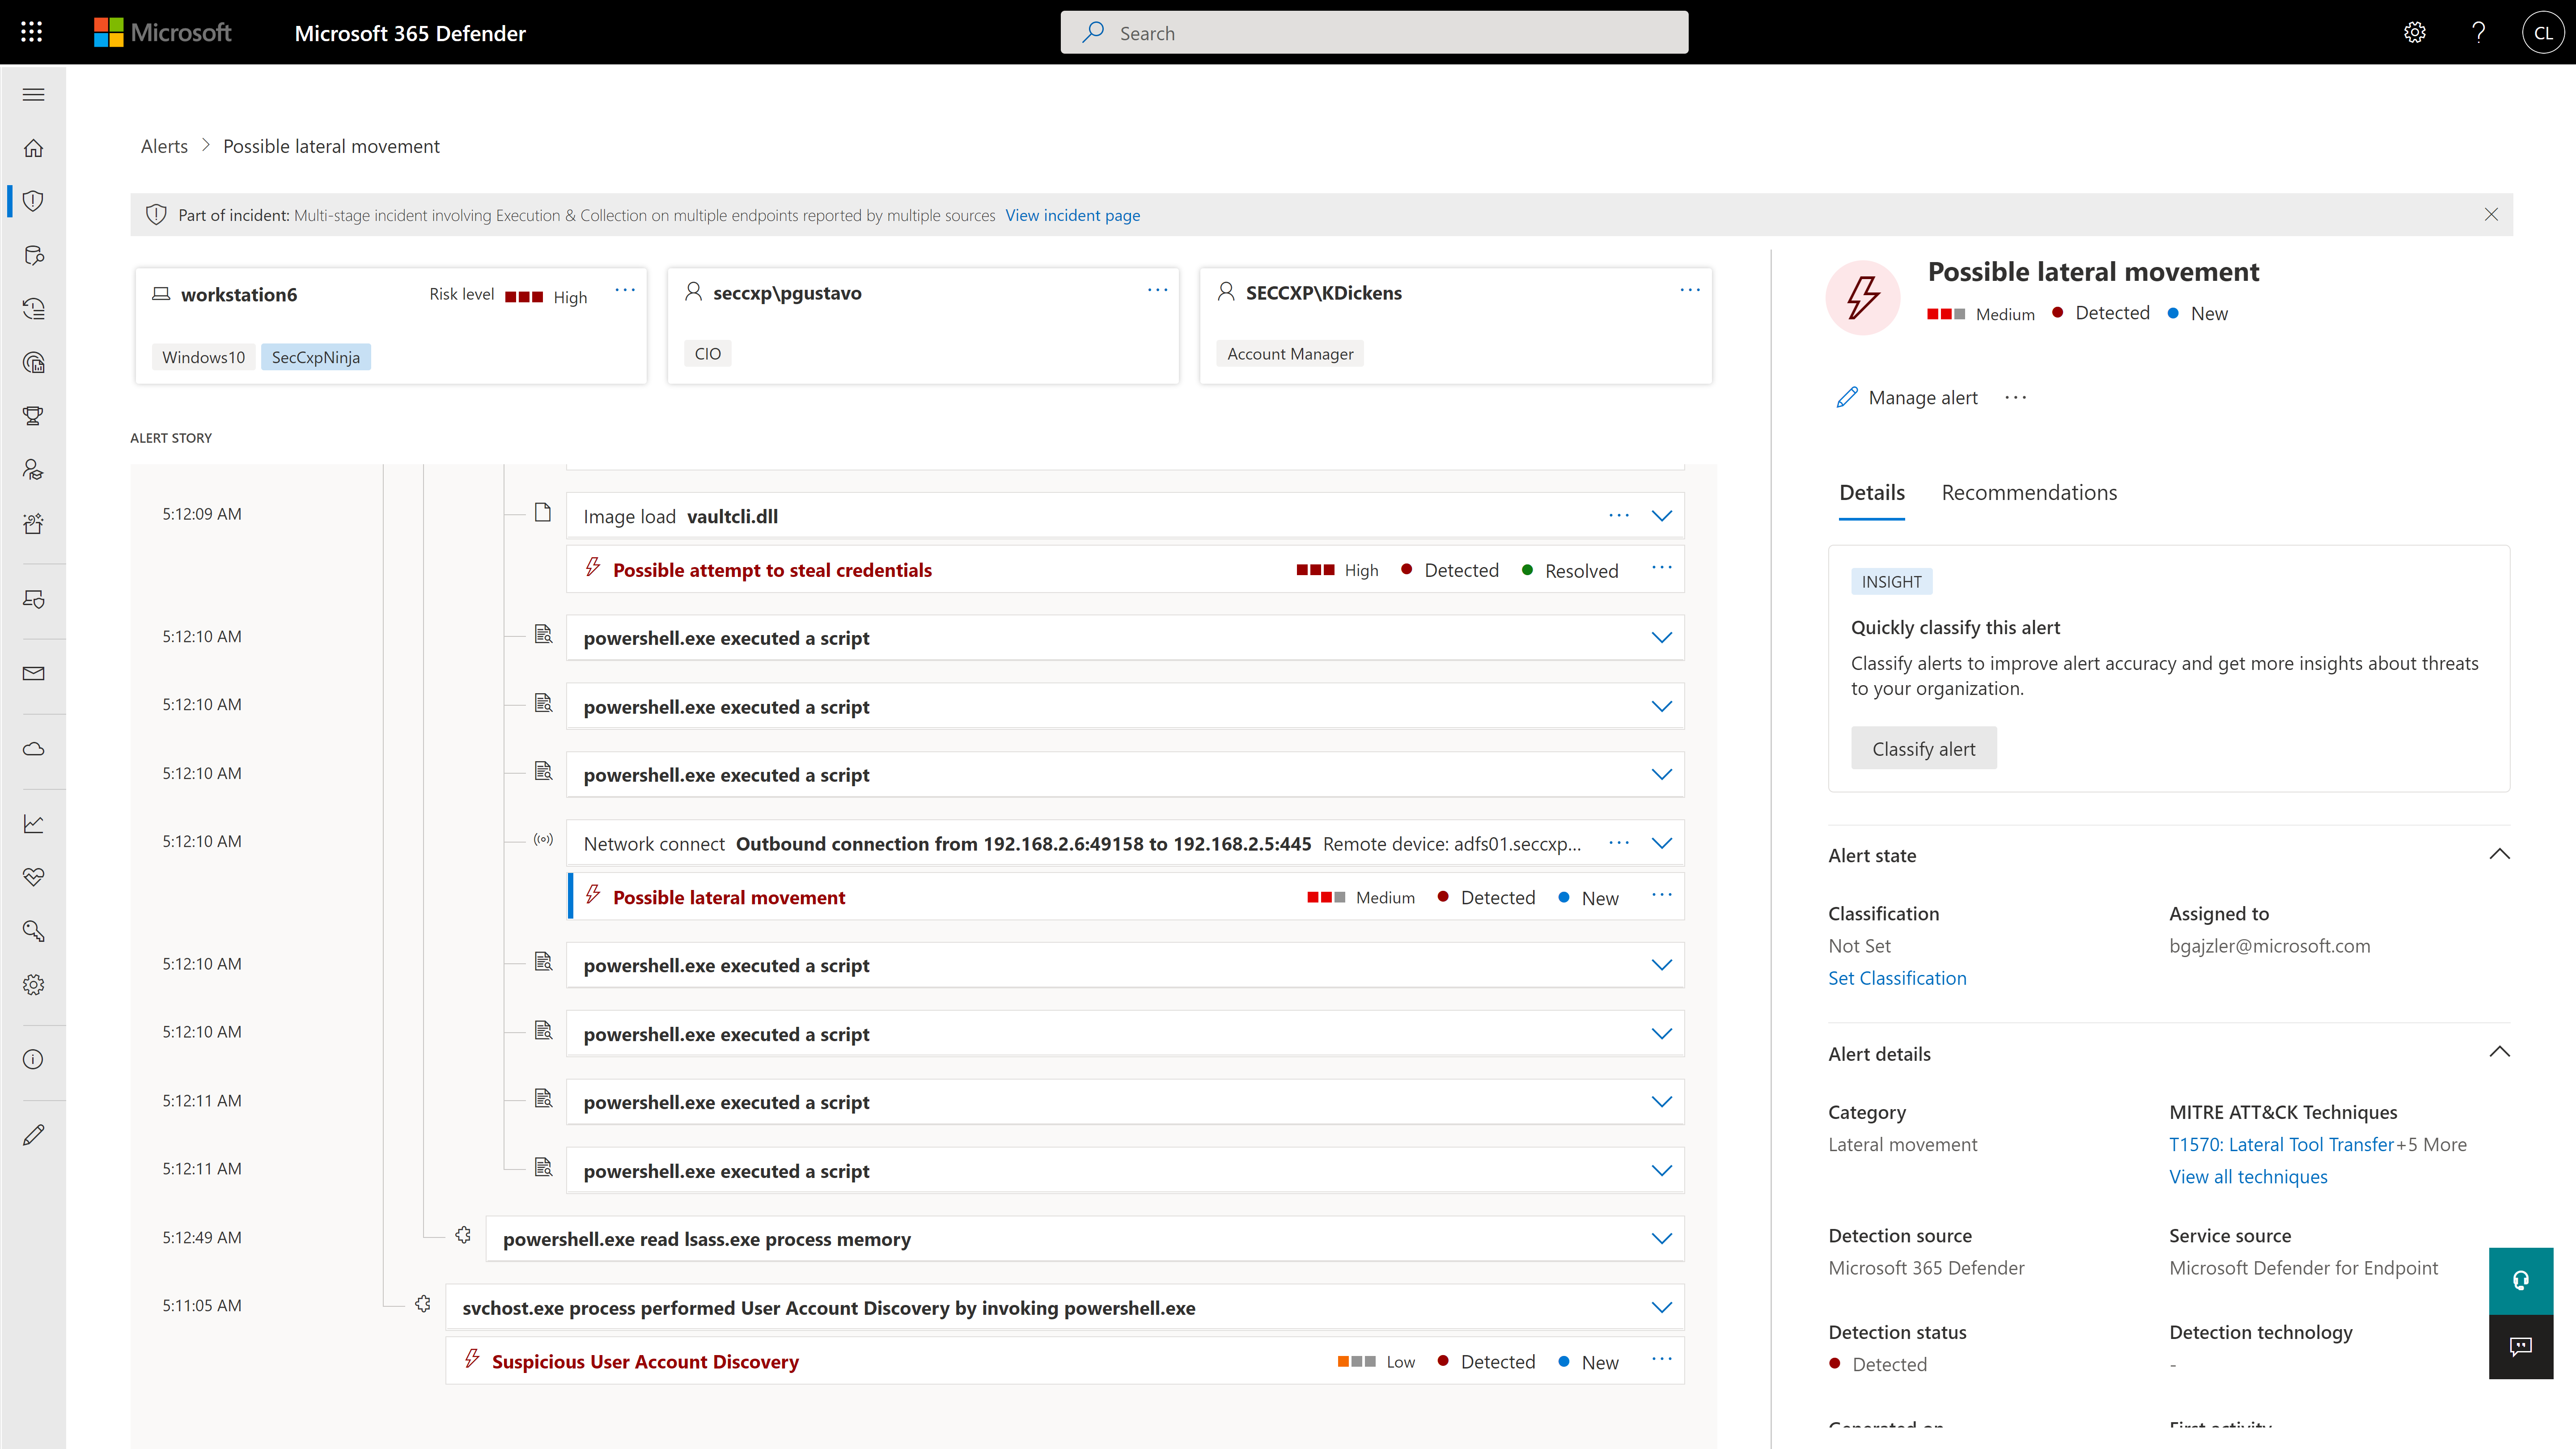
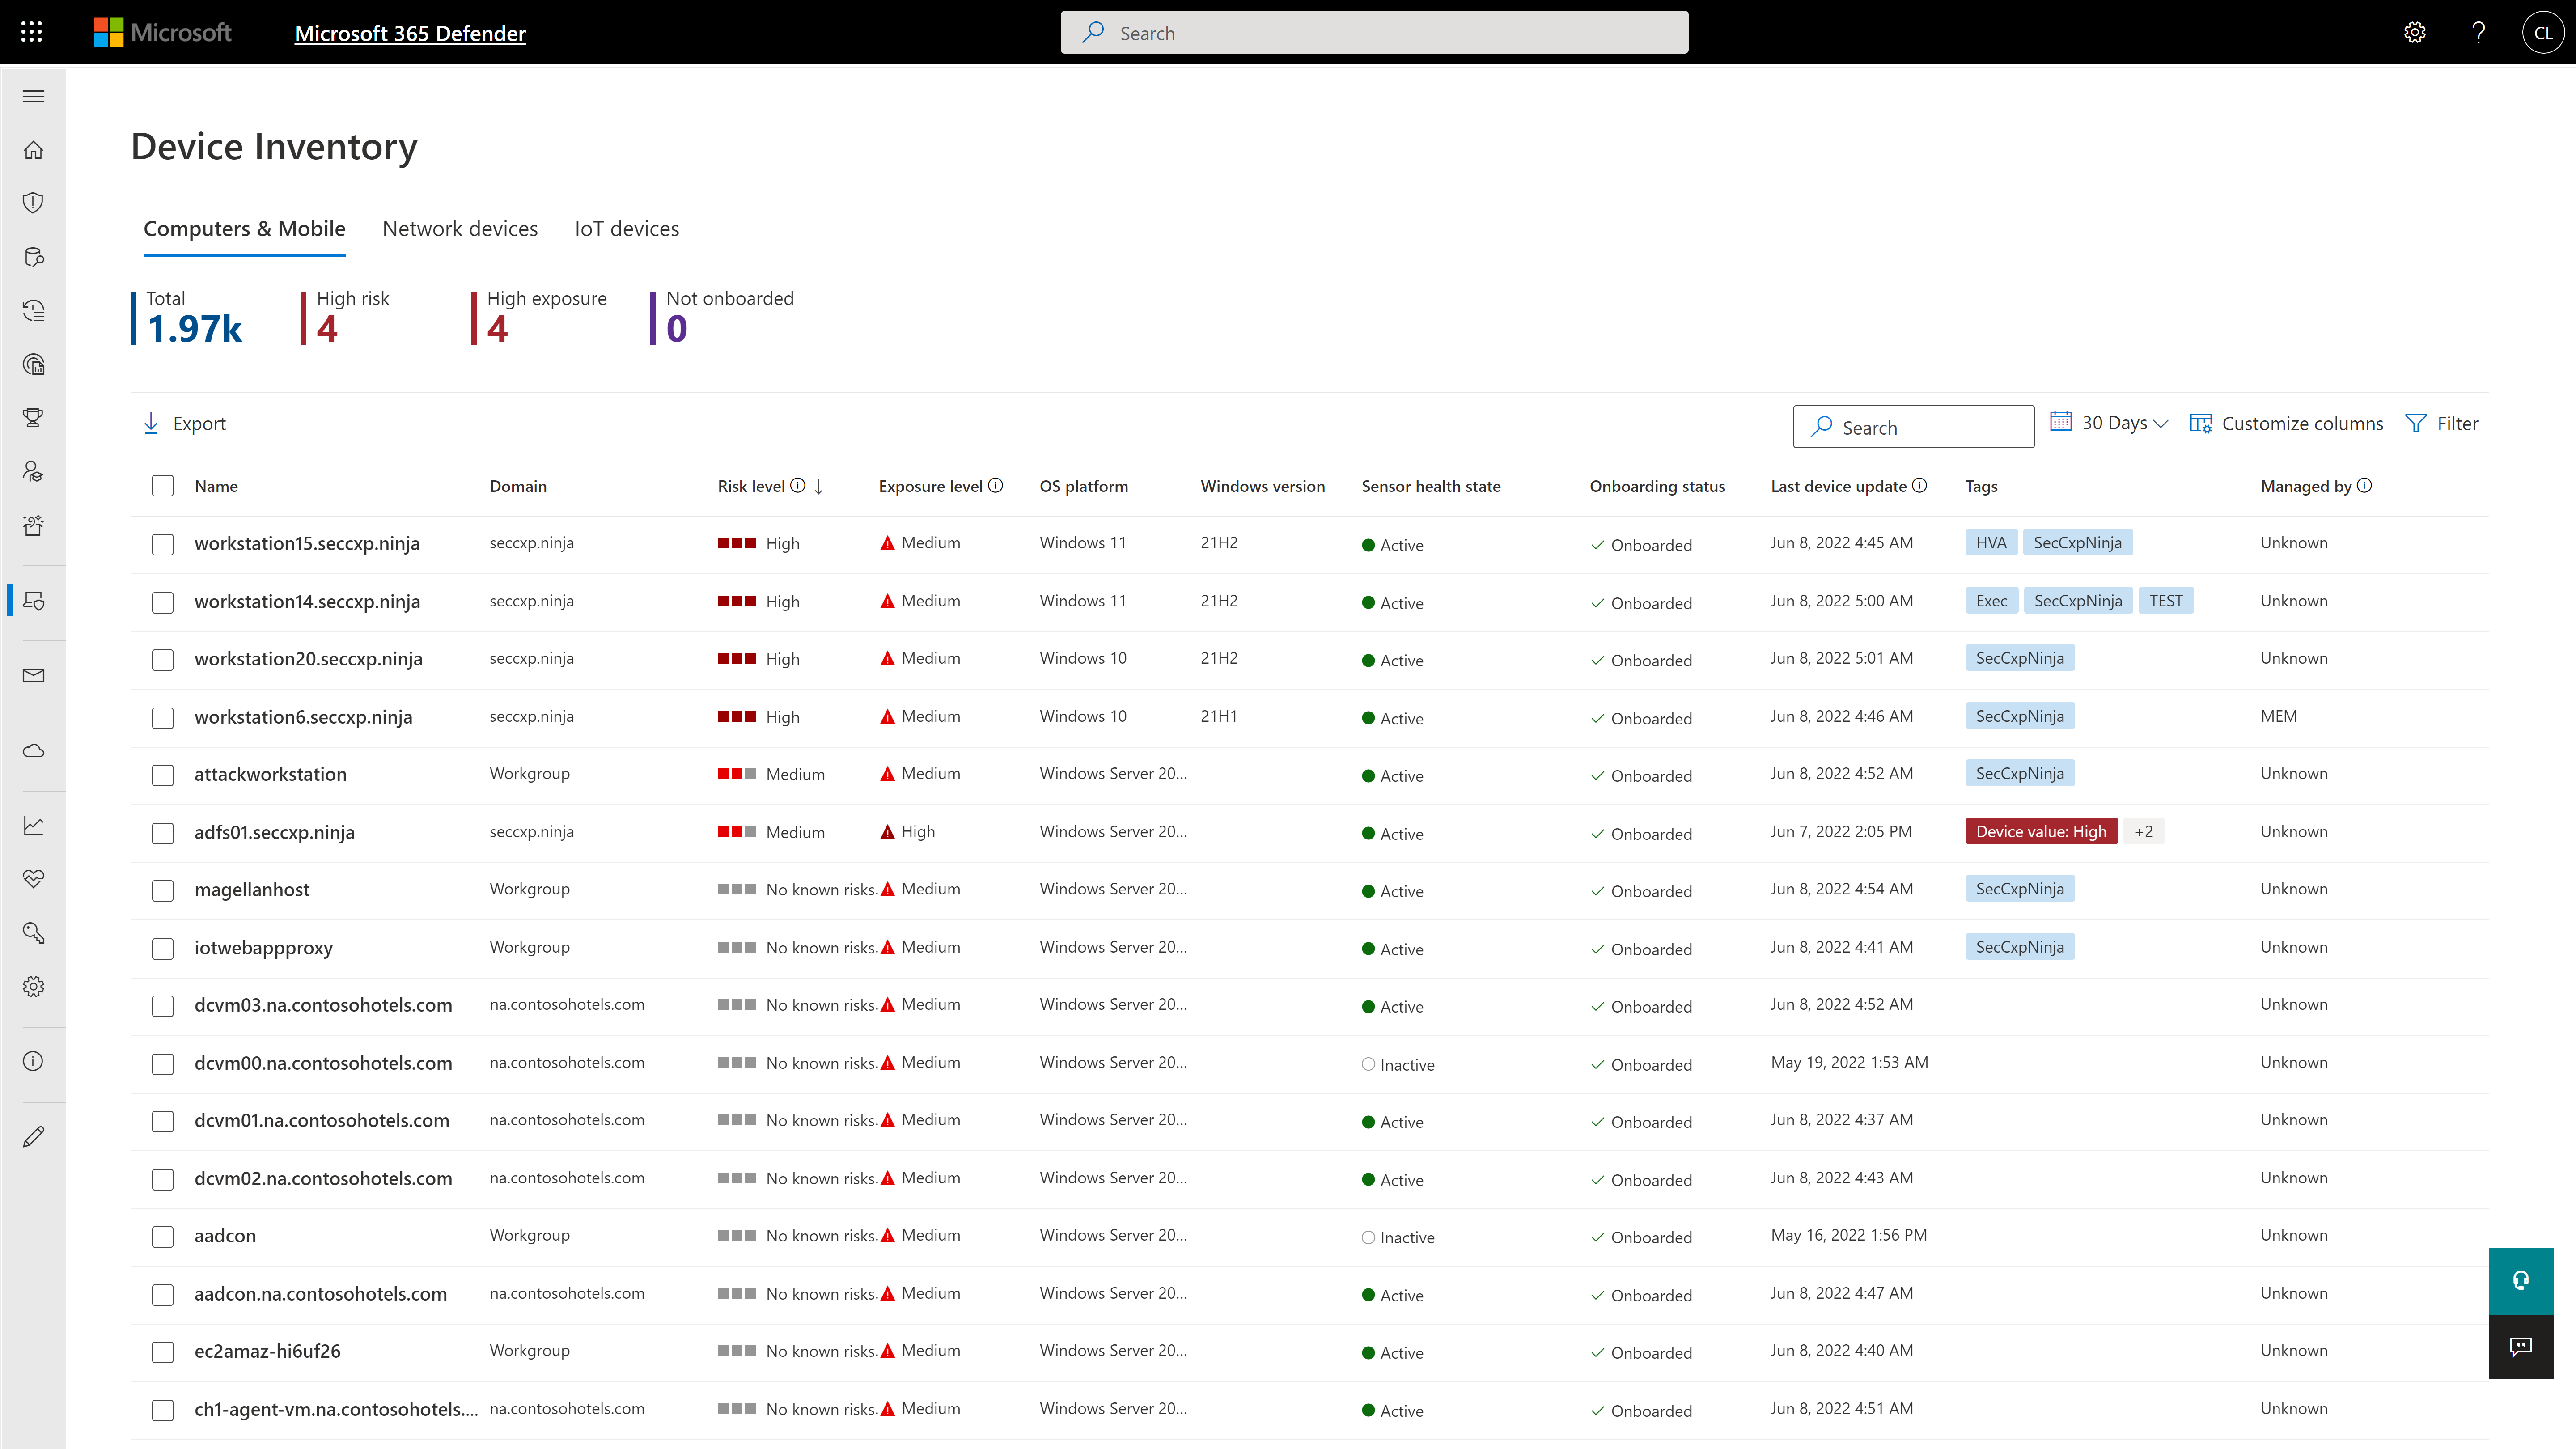
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Webroot Antivirus
Score9.3 out of 10
N/A
Webroot Security Complete (formerly under the brand name SecureAnywhere) is a suite of antivirus, multi-endpoint security and Internet security solutions available for home offices, and possibly small businesses with limited security needs.
Microsoft Defender for Endpoint is the most cost effective solution considering our Microsoft 365 licensing status. While many 3rd party solutions are great and have been used over the years, in the non-profit world, cost is a huge driving factor of items. Coupled with …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Senior Engineer in Information Technology at Network Configurations (Information Technology & Services, 51-200 employees)
Chose Microsoft Defender for Endpoint
For me personally, I can not really compare the two against each other, as they are both really good. For us as a business specializing in MS products, it is a logical choice to have followed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender for Endpoint
We used to use Symantec's Endpoint Detection and Response Solution, and so that's actually what we replaced with Defender for Endpoint. So it's just lightyears ahead of that one. So personally, I've also used Webroot in the past for an antivirus solution and Kaspersky and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender for Endpoint
As compared to some of the other products we have used in our organization over the years, Windows Defender has been a lot better at not using a lot of system resources when running on the clients. A lot of other commercial threat protection products on the market today, tend …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Webroot SecureAnywhere is a good solution for those wanting to protect their endpoints from viruses and malware. It also works great for MSPS as you can manage all clients in a single portal. You have the option for DNS protection and web browser filtering as well. This would also work well in any small business.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Webroot checks all search result links and delivers warnings or approvals to users. This means Webroot is thorough and assists to keep users familiar with any potential problem sites.
Webroot is easily activated as a Chrome or browser extension to ensure ease of access.
Webroot monitors activity and will send updates to the IT department to keep them privy of any potential problems.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Webroot could do a better job of working on their integration partnerships with companies like LabTech (now known as Automate). Many times we make it through 2 or 3 levels of support before one of the parties says "oh well you need to talk to LabTech about this" or vice versa. That can be frustrating for partners when trying to understand and resolve issues between the two applications.
Cryptolocker/ransomware is a hot topic and I will say that Webroot has provided us with adequate protection when we first started using in 2014. I understand the complexities and challenges AV companies face with new threats being created everyday. I do want to point out that there have been instances where Webroot has not been able to stop one of those types of attacks. After talking with support - it was clear that they had no good answer as to why that particular threat was not stopped and quarantined.
Support for the enterprise side of Webroot can be daunting at times. Response times are hit or miss depending on the severity of the issue. Sometimes you get a great support engineer who will go above and beyond - sometimes I ask myself how this person is even employed with the lack of communication skills or actual interest in helping resolve partner issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It's easy to renew with Webroot, their support is very attentive and highly available. However if you do choose to change products, they even provide means of removing the software from your endpoints via the admin portal which is very convenient.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
There is nothing perfect in this world, but Webroot Antivirus + Internet Security Complete (SecureAnywhere) is easy to use in comparison to others. Also Webroot tech support is only a phone call away. There have been several times I ran into an issue, but tech support as there to help resolve the issue.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have not had to use Webroot support much over the years. The one or two times we did we were referred to online documentation and in a somewhat condescending manner in one case and in another case, the support person did not demonstrate much knowledge of their product and referred us to the user community for support.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
While we consider alternatives from time to time when putting together our budget, we haven't felt the need to thoroughly test a competitor since webroot has been working well for us and we are comfortable with the pricing.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Ease of implementation across various devices is easy and efficient regardless of scale. Whether it is 5 devices or 500 the product continually proves its the best in its class.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It has had a mostly positive impact as we have not had any breaches.
The only negative impact has been when Webroot Antivirus + Internet Security Complete (SecureAnywhere) changed something on their end that caused one of our business applications to not be usable by end-users. That cost our business a fair amount as it took 4 days before it could be used again.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info