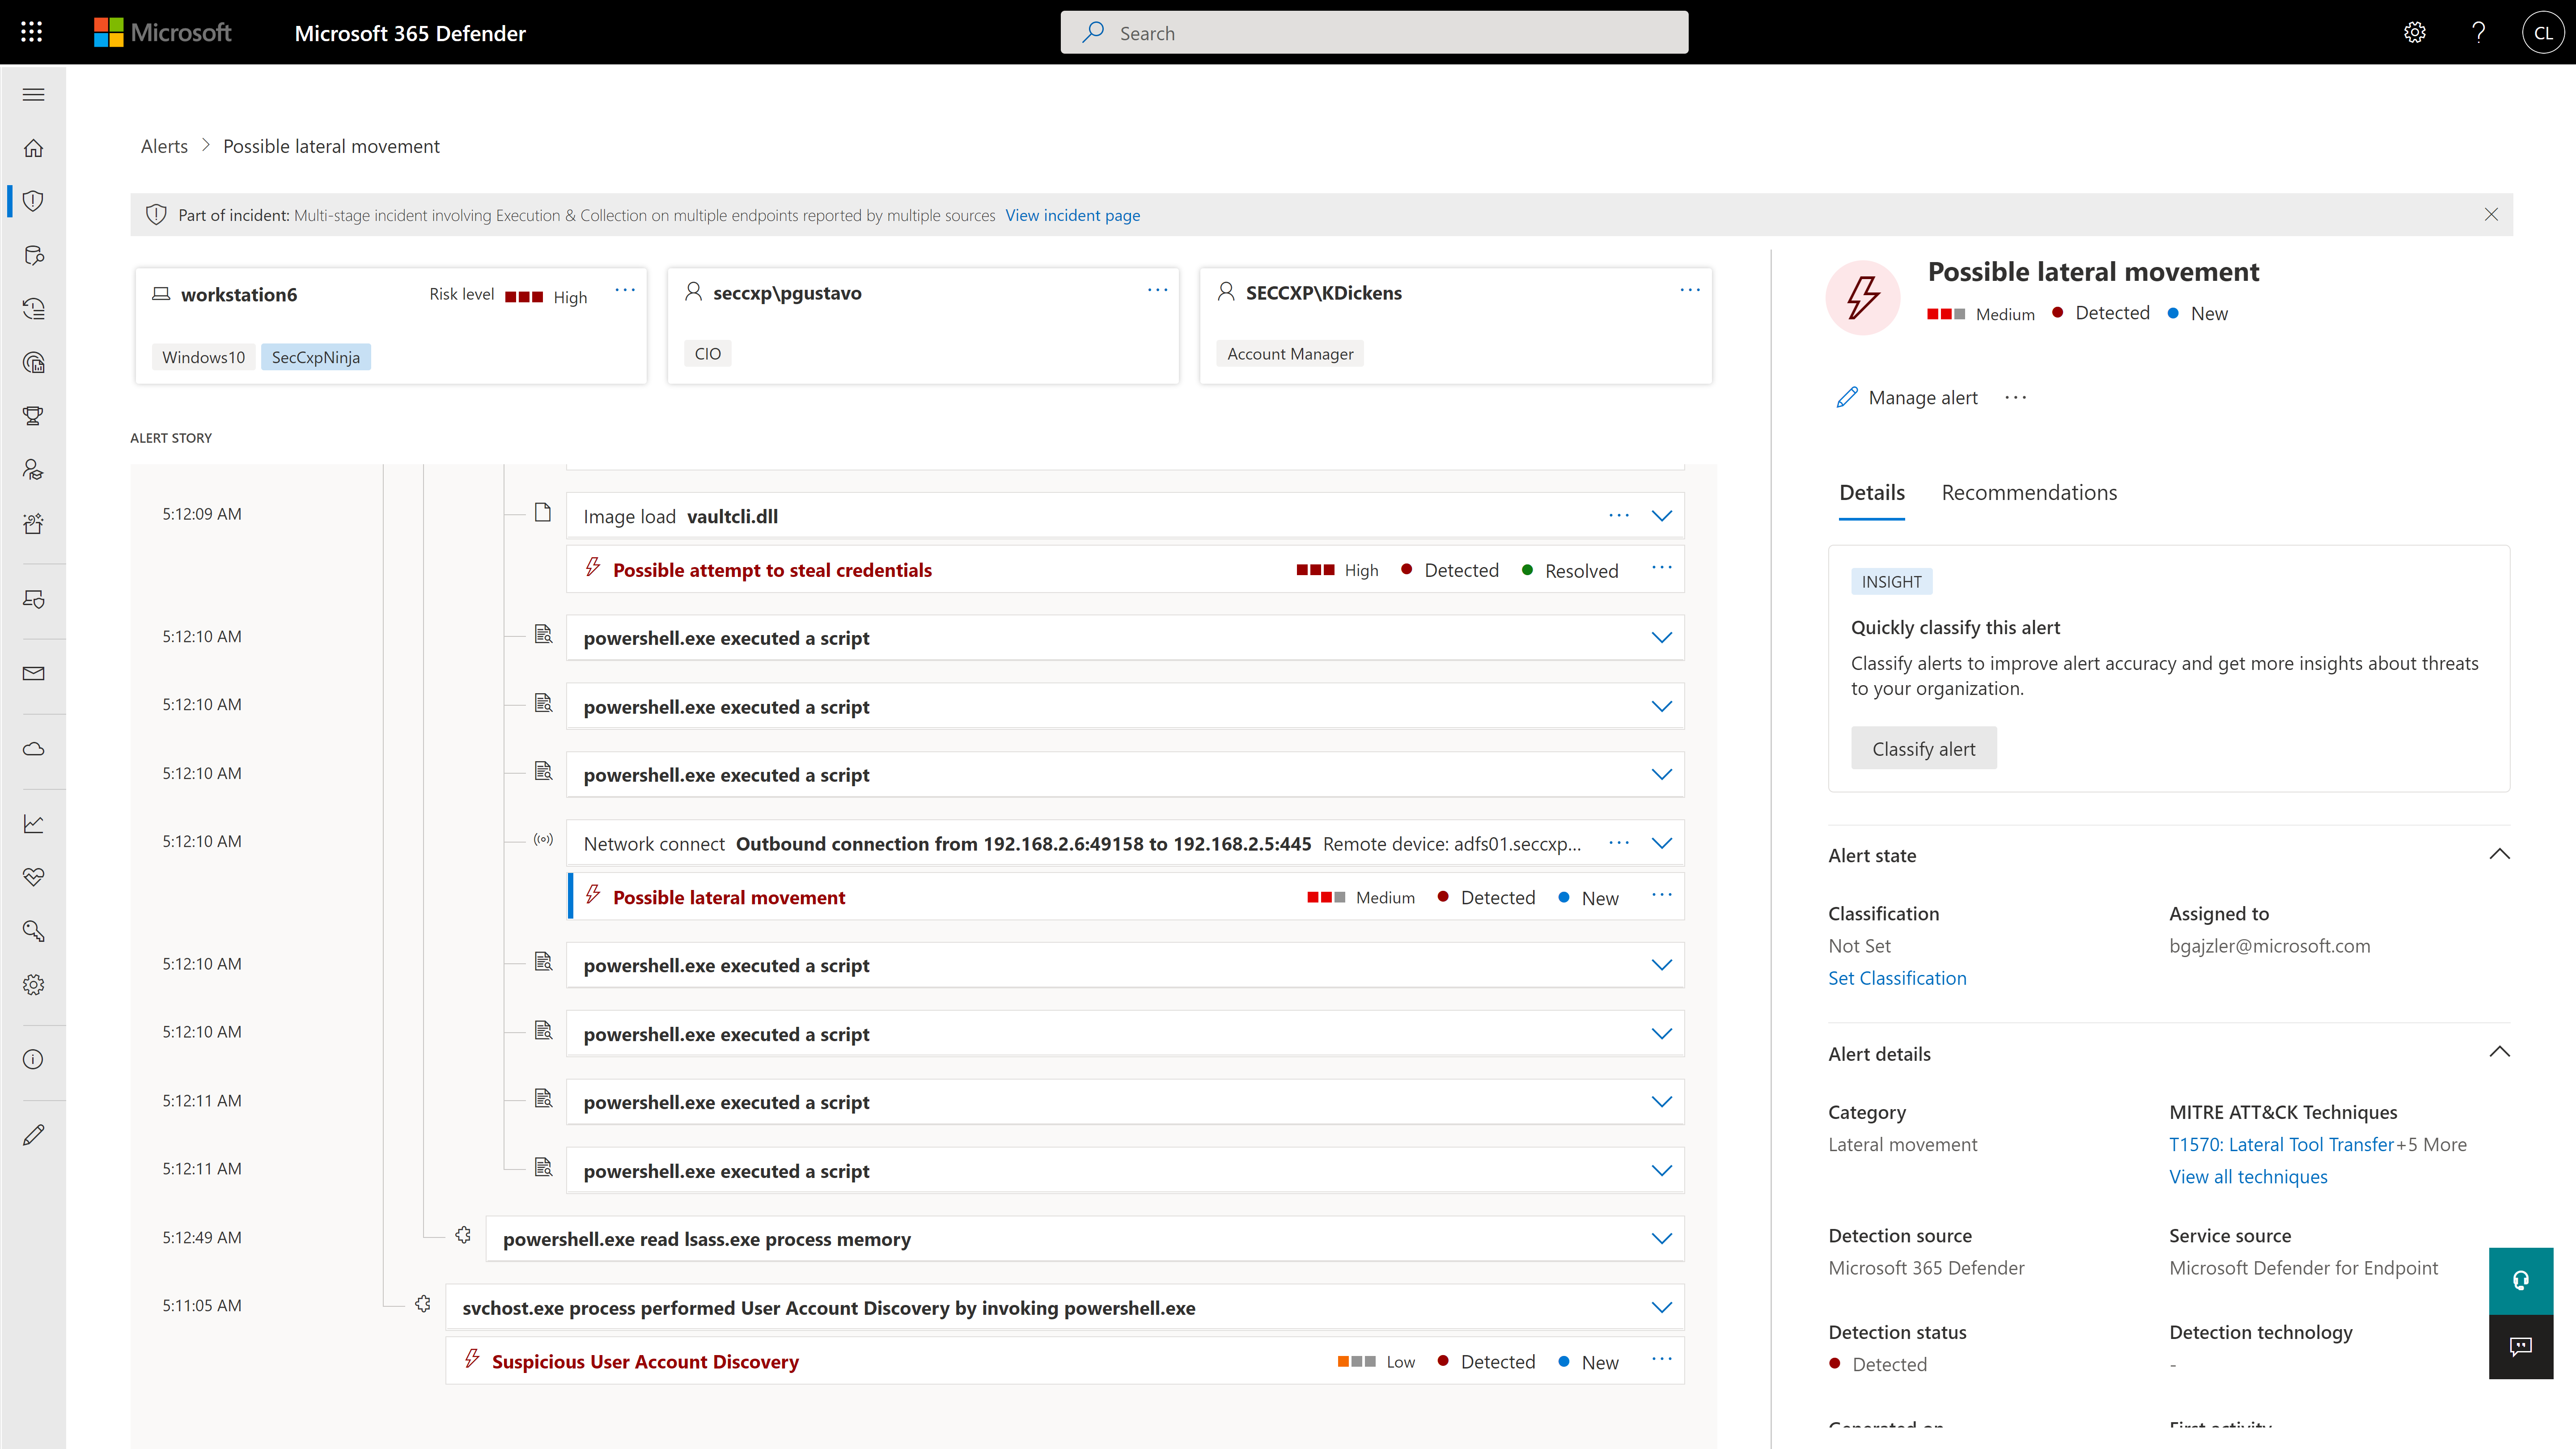
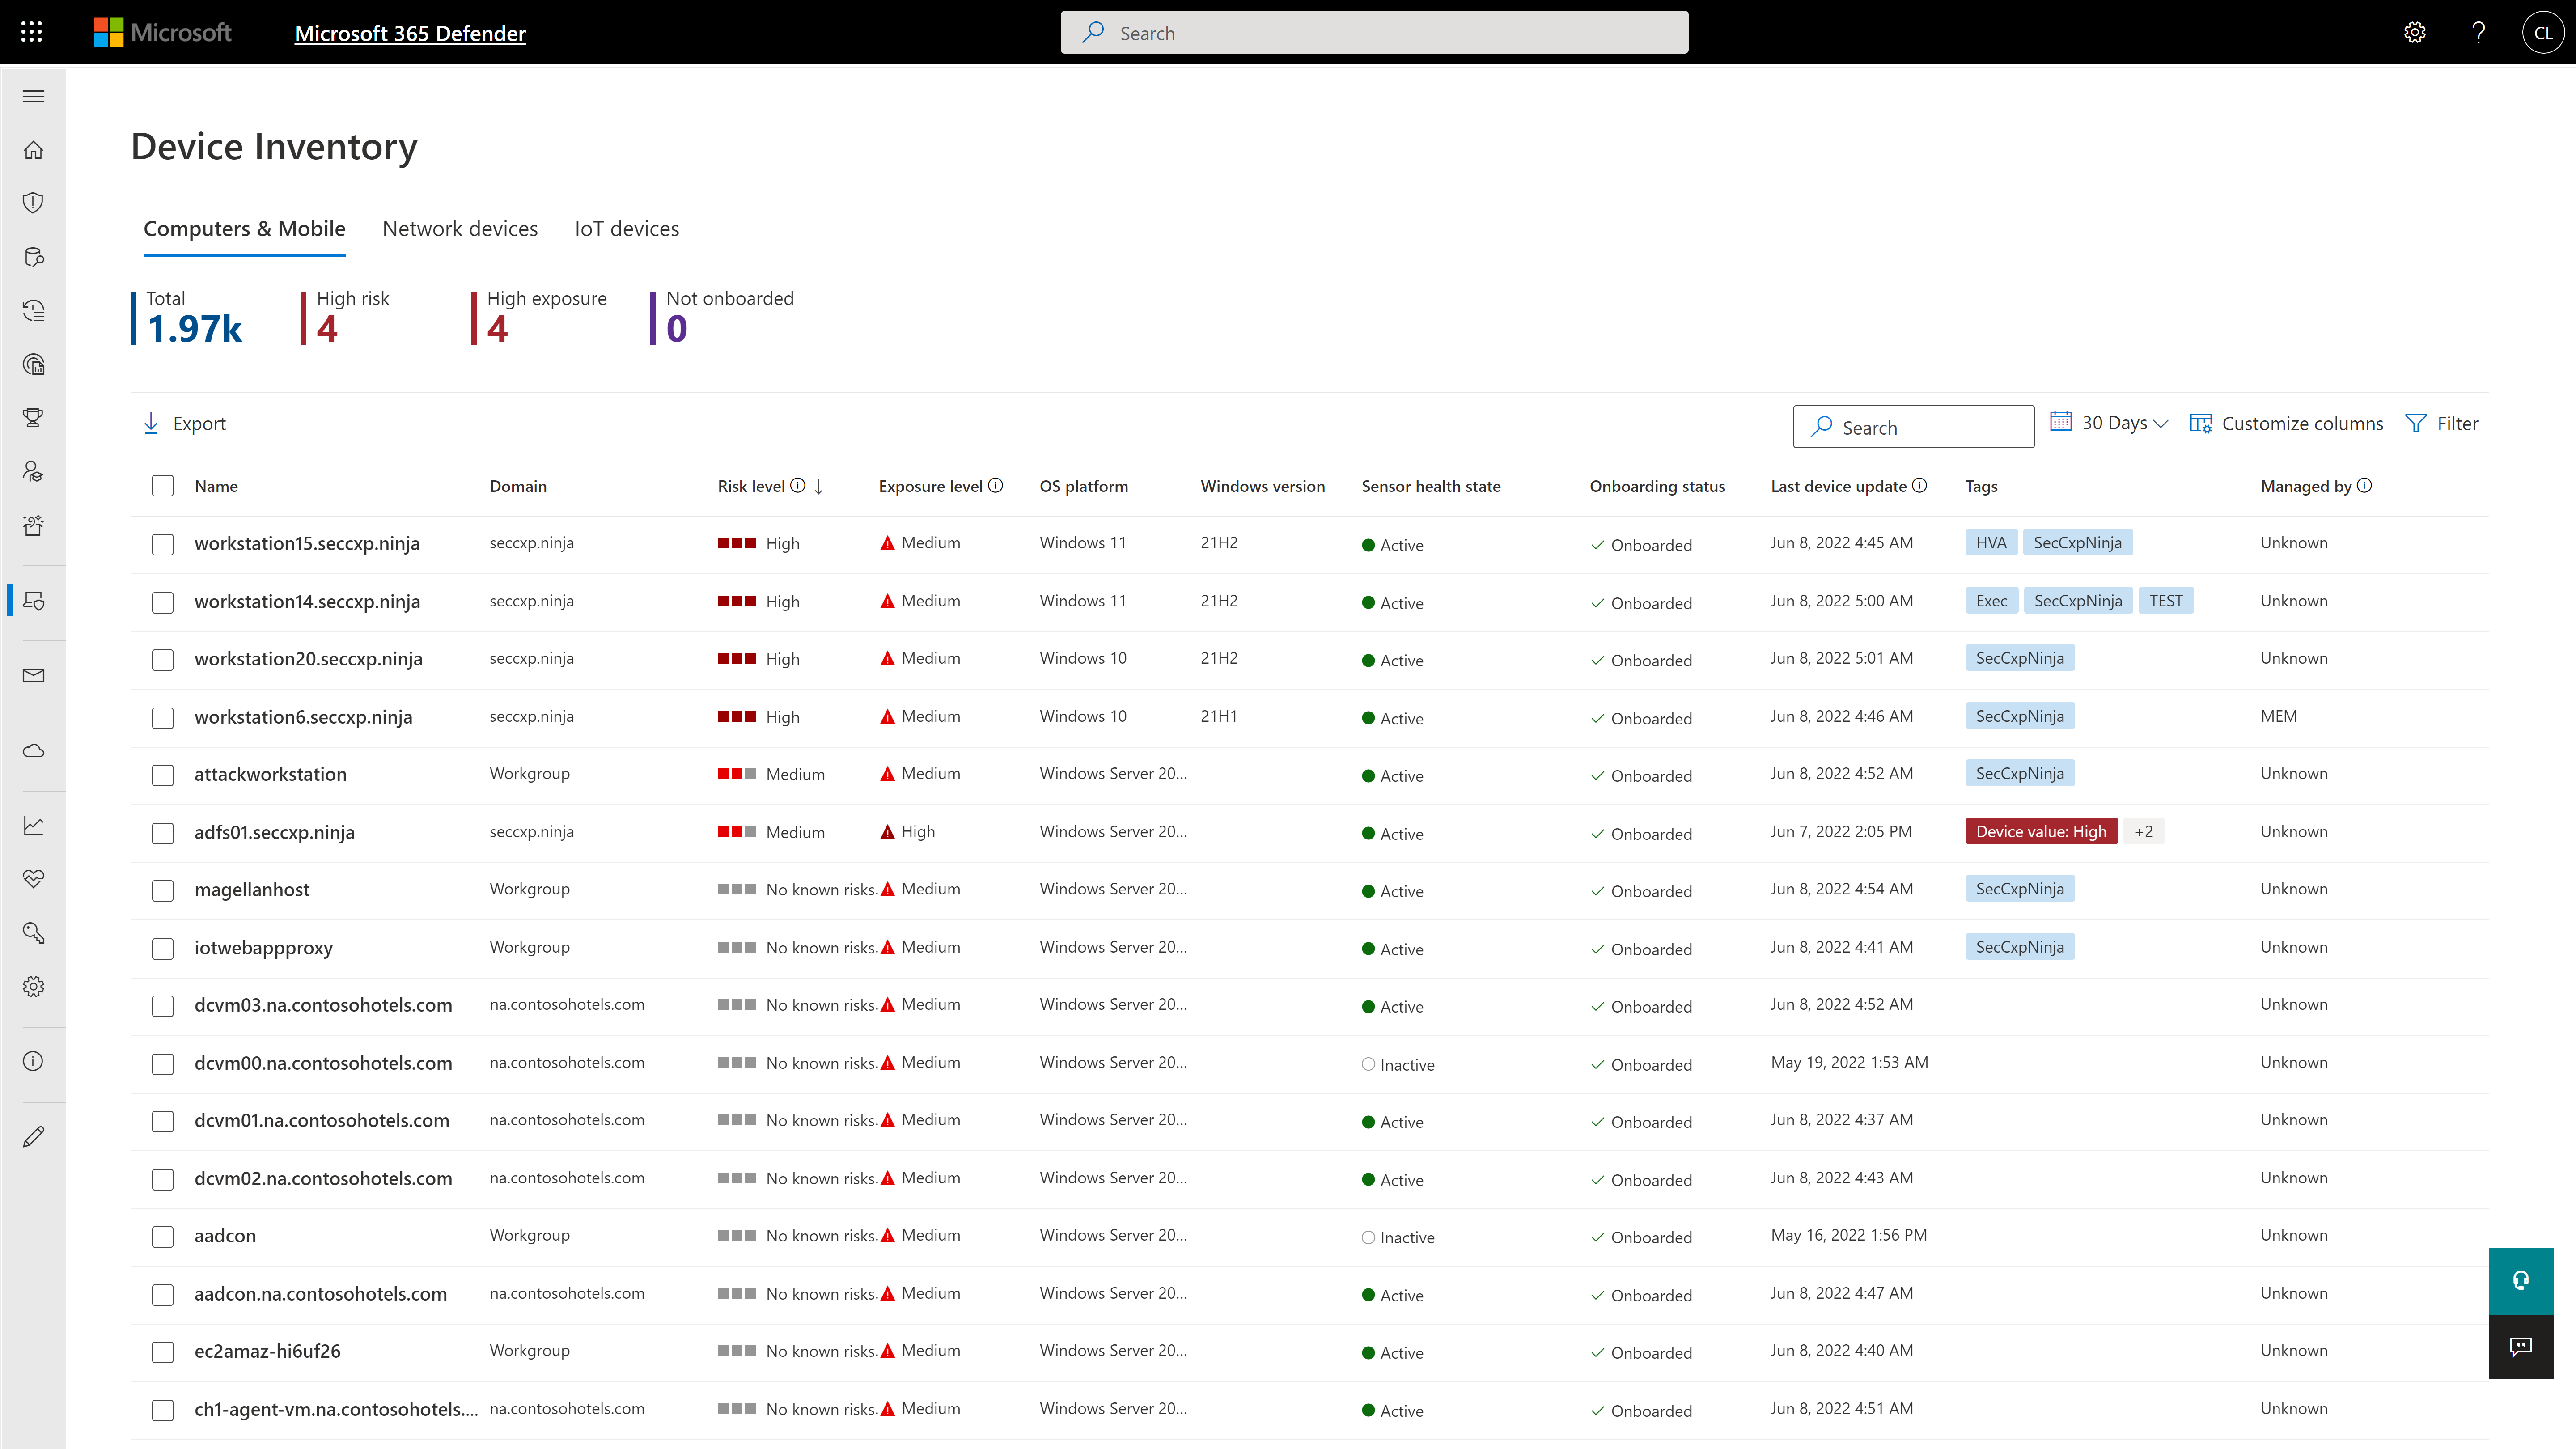
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Symantec Endpoint Security
Score8.7 out of 10
N/A
Symantec Endpoint Protection is the company's flagship antivirus / endpoint security product.
$29.99
per year 100-249 devices
Pricing
Microsoft Defender for Endpoint
Symantec Endpoint Security
Editions & Modules
Academic
$2.50
per user/per month
Standalone
$5.20
per user/per month
Endpoint Security, Initial Hybrid Subscription License With Support
$29.99
1 year 100-249 devices
Symantec Endpoint Security Enterprise, Initial Hybrid Subscription License with Support
$34.99
1 year 1-99 devices
Endpoint Security, Initial Hybrid Subscription License With Support
$90.99
3 years 100-249 devices
Symantec Endpoint Security Enterprise, Initial Hybrid Subscription License with Support
$99.99
3 years 1-99 devices
Symantec Endpoint Security Complete, Initial Hybrid Subscription License with Support
Associate Director - Practice Lead, Network and Systems Engineering in Engineering at Arcadis (Computer & Network Security, 10,001+ employees)
Chose Microsoft Defender for Endpoint
Enterprise Endpoint Protection: Microsoft Defender for Endpoint is well suited for large organizations with numerous endpoints, such as desktops, laptops, and servers, as it provides centralized management and monitoring of security across the entire network. Microsoft …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Mostly it runs smoothly on host without impacting performance as other AVs like Symantec's impacts performance issue of host. Also because it's still a good product overall price range. Can upgrade to EDR solution with not much difficulty & onboarding on tool is not that …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
We used to use Symantec's Endpoint Detection and Response Solution, and so that's actually what we replaced with Defender for Endpoint. So it's just lightyears ahead of that one. So personally, I've also used Webroot in the past for an antivirus solution and Kaspersky and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender for Endpoint
As we are using 90% of Windows devices and laptops in our organisation we figured out that Microsoft Defender for Endpoint is a better solution for us as compared to above solutions mentioned. It is very easy and convenient to use this solution with Windows devices. The …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
As compared to some of the other products we have used in our organization over the years, Windows Defender has been a lot better at not using a lot of system resources when running on the clients. A lot of other commercial threat protection products on the market today, tend …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Broadcom
Verified User
Chose Symantec Endpoint Security
In comparison with Microsoft Defender for Endpoint Symantec Endpoint Security has, in my opinion, more scalable file inspection/spyware/antivirus settings. Plus it is more stable in a multi-OS user environment. But it also has numerous issues with itself and related Symantec …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Systems Administrator, Core Infrastructure & Microsoft Systems in Information Technology at Cancer Research UK (Non-Profit Organization Management, 1001-5000 employees)
Chose Symantec Endpoint Security
Symantec Endpoint Protection really shines against its competitors when it comes to centralized management. It falls a little short when it comes to cloud deployments.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Symantec Endpoint Security is a well-rounded product that provides a significant amount of functionality and covers many of our endpoint needs without needing to resort to multiple vendors that might clash in unpredictable ways when ultimately deployed to the endpoints in our estate. The default policies are adequate and tuning these requires some time as with all similar EDR products but the product is flexible enough to allow very granular whitelisting/blacklisting which is great. Low resource requirements are also fantastic and we've not had many complaints from developers who were getting slowed down when compiling complex code with other previous solutions.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The system should have a better ability to auto repair, if an item is malfunctioning it should auto reinstall.
The cloud platform and the server do not talk well to each other and it would be great to get the same data on both platforms, this may be due to version though.
It seems the whitelisting on the cloud platform could use some work.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The rating reflects Symantec Endpoint Security's ability to balance enterprise grade security with user-friendly workflows or advanced configurations require extra effort. For most organizations, the streamlined management and robust automation justify the high score. Management GUI is old fashined and need to be improve. Older devices may experience slowdowns during full scans without careful configuration.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We've used it for years and the software is easy to use. The dashboard is easy to read, and you can easily figure out where to go to troubleshoot or deploy software. Symantec is there for emergencies like backup restoration or file retrieval. It's pretty low maintenance. Symantec is there when your IT infrastructure needs it
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Support is completely awful! You can never get anyone to help if you can even find a number to call. The support web portal is a joke and their response time if you're even able to submit a ticket is ridiculously slow.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Symantec Endpoint Security offers very similar features to the above products, they all do the same thing in terms of protecting your endpoints against cybersecurity threats. Installation wise the products all install from a central management system and report back to this for central reporting. Ultimately we choose Symantec as the reseller was able to offer additional incentives which made their pricing very competitive.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info