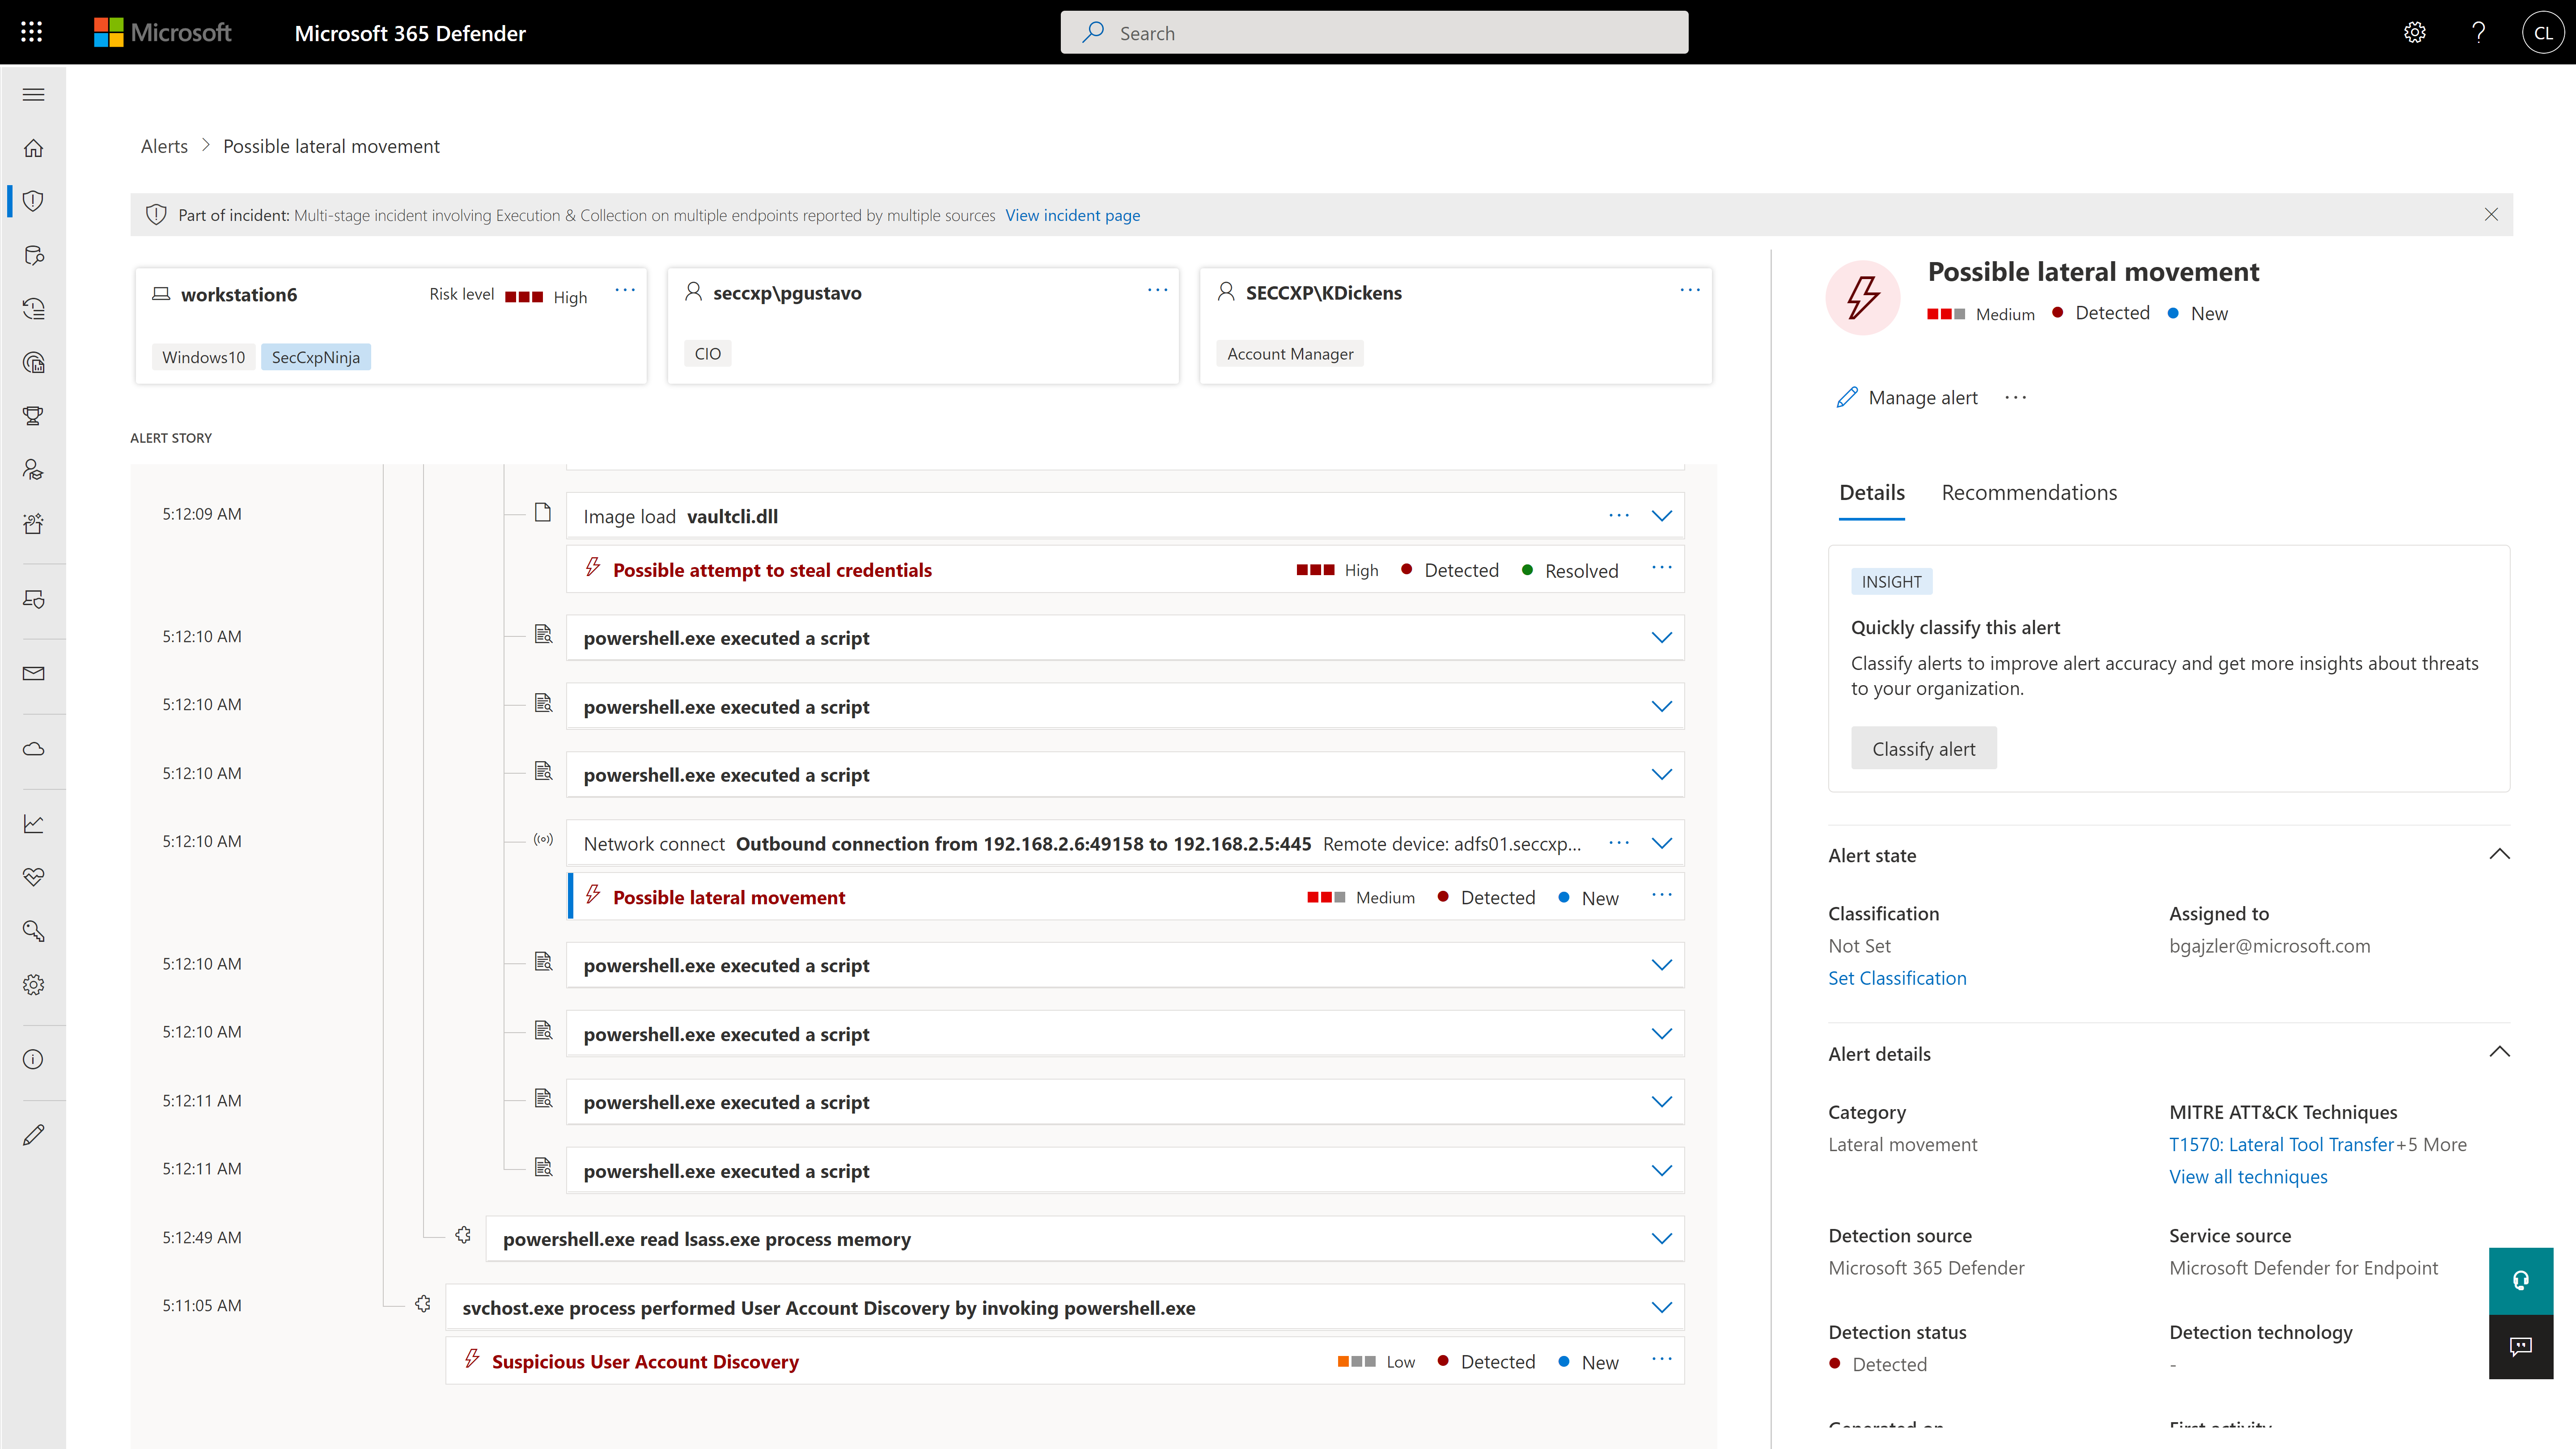
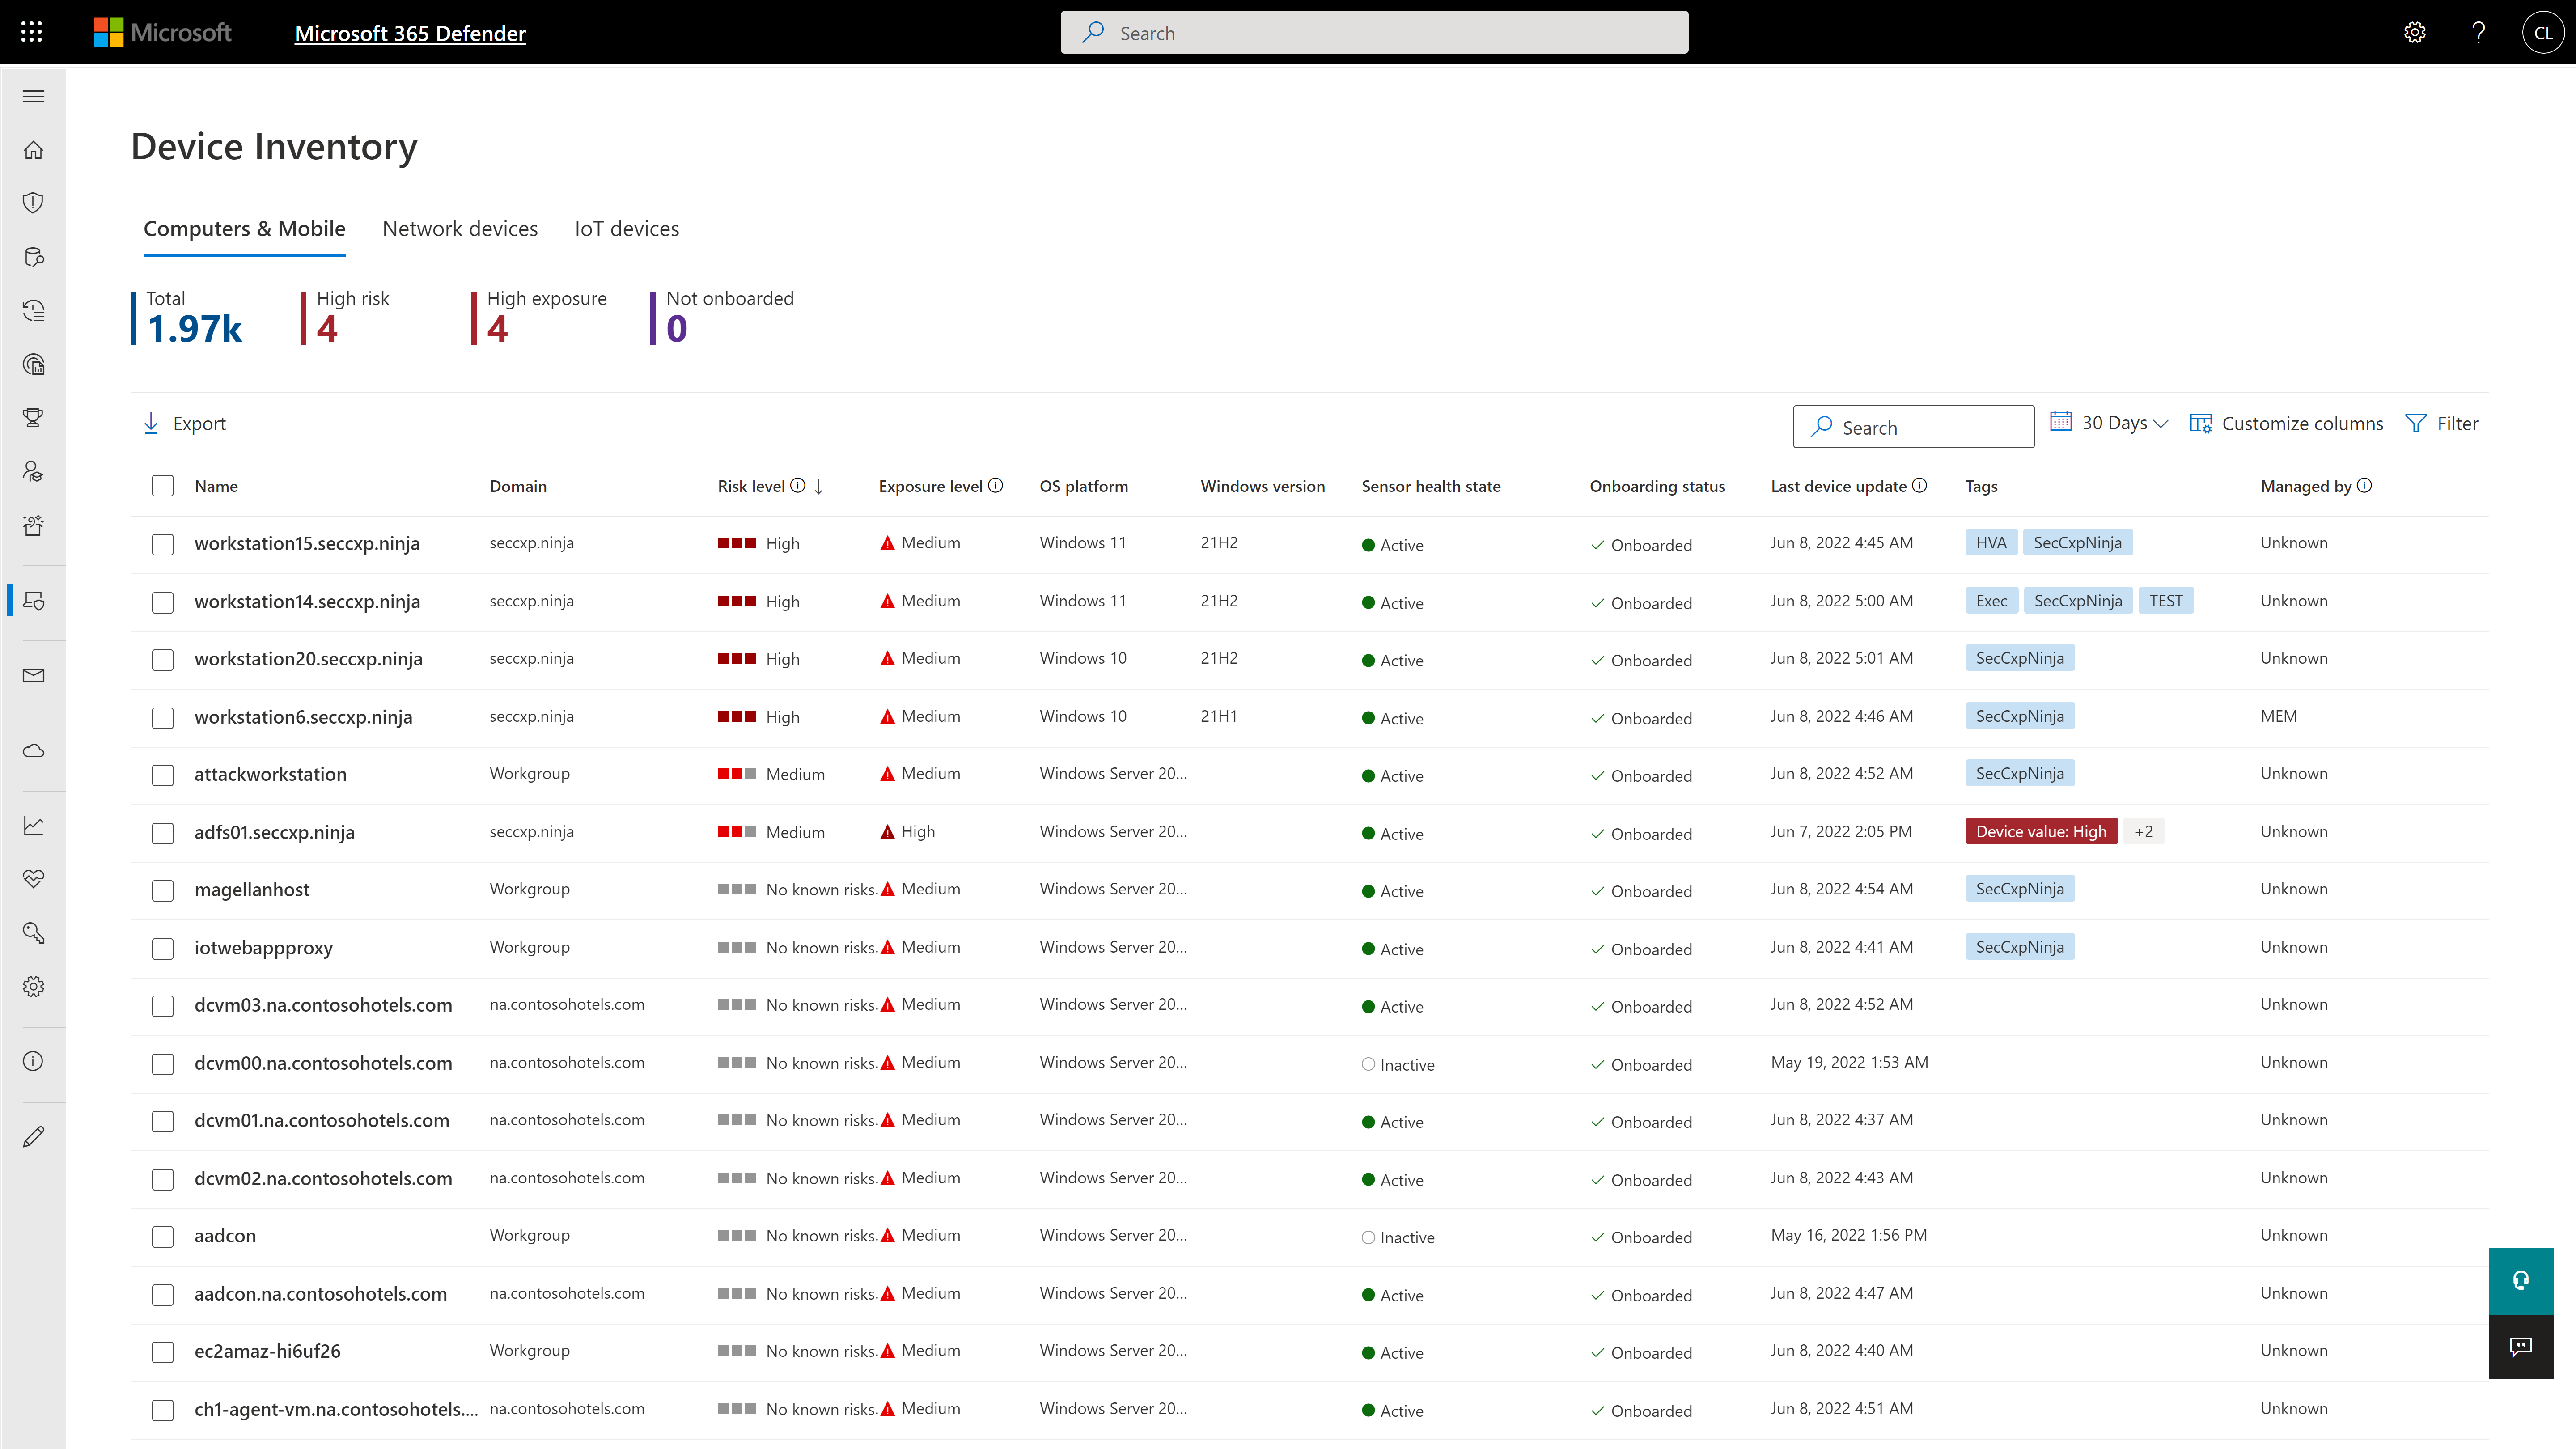
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Microsoft Defender XDR
Score8.7 out of 10
N/A
Microsoft 365 Defender combines SIEM and XDR capabilities for Microsoft 365 environments, encompassing threat detection, post-breach detection, automated investigation, and response for endpoints. Additionally, it protects cloud apps, emails and documents, and employee identities.
N/A
WatchGuard Endpoint Security
Score8.7 out of 10
N/A
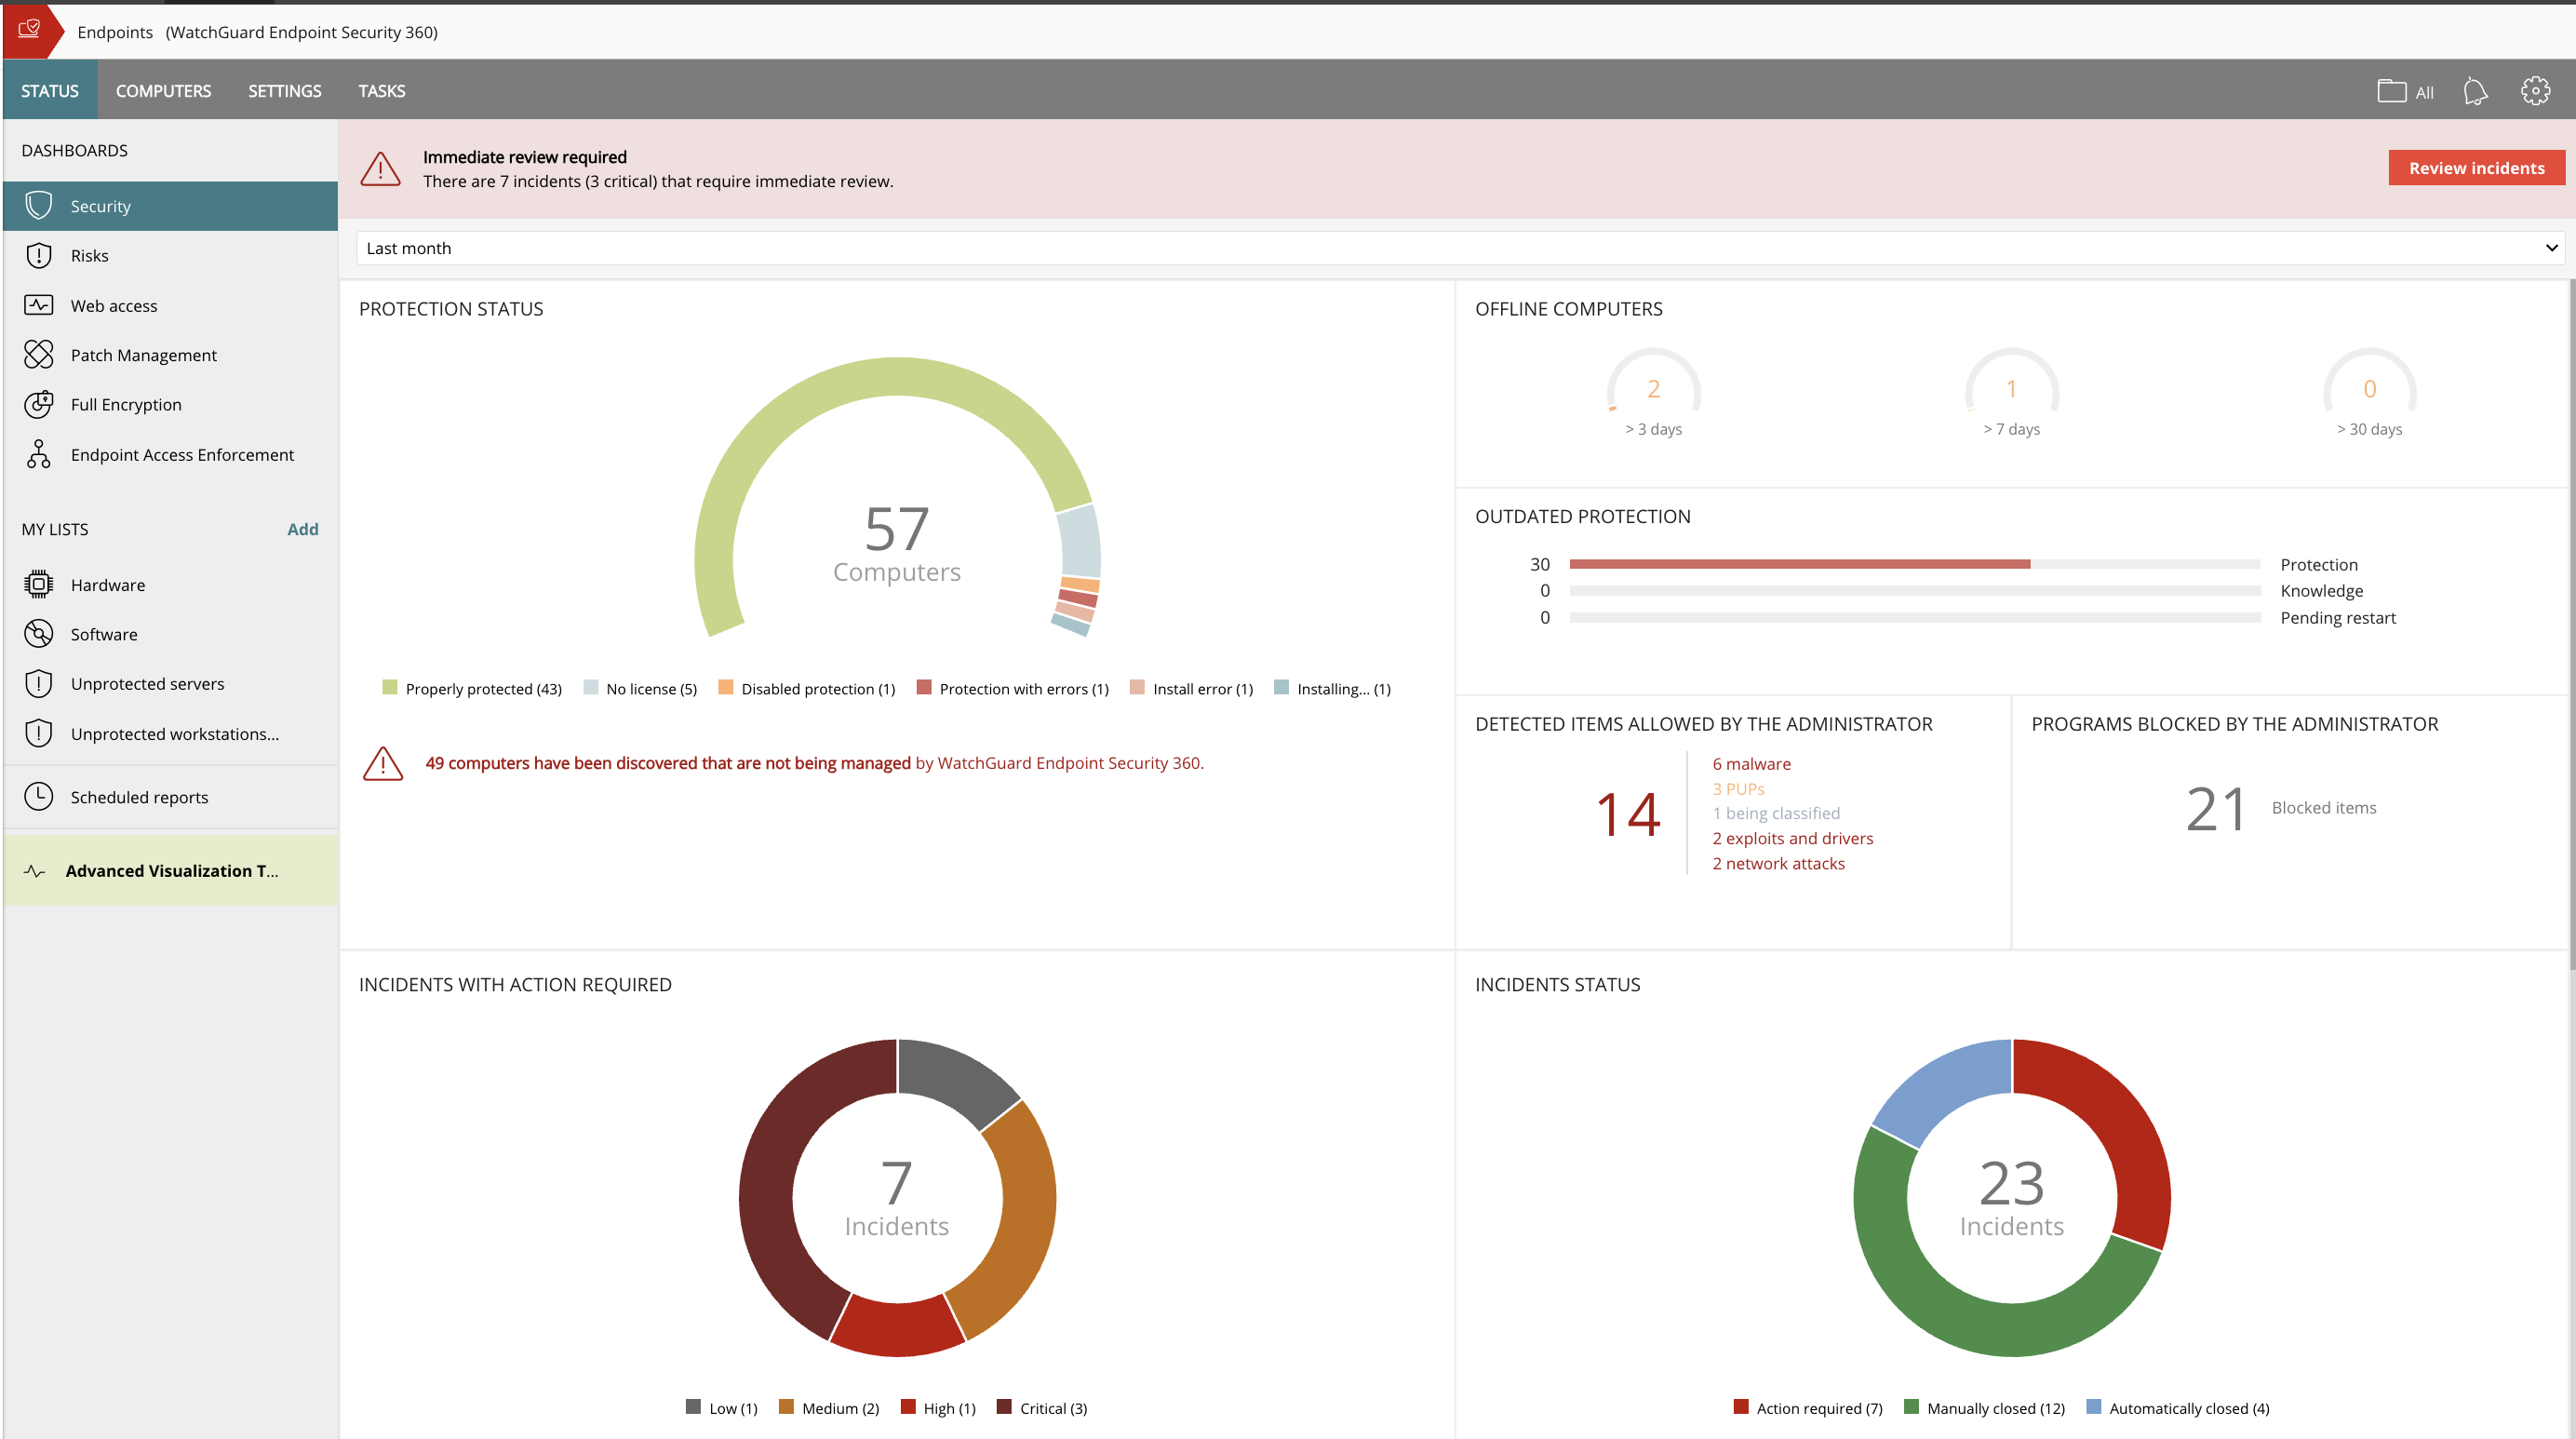
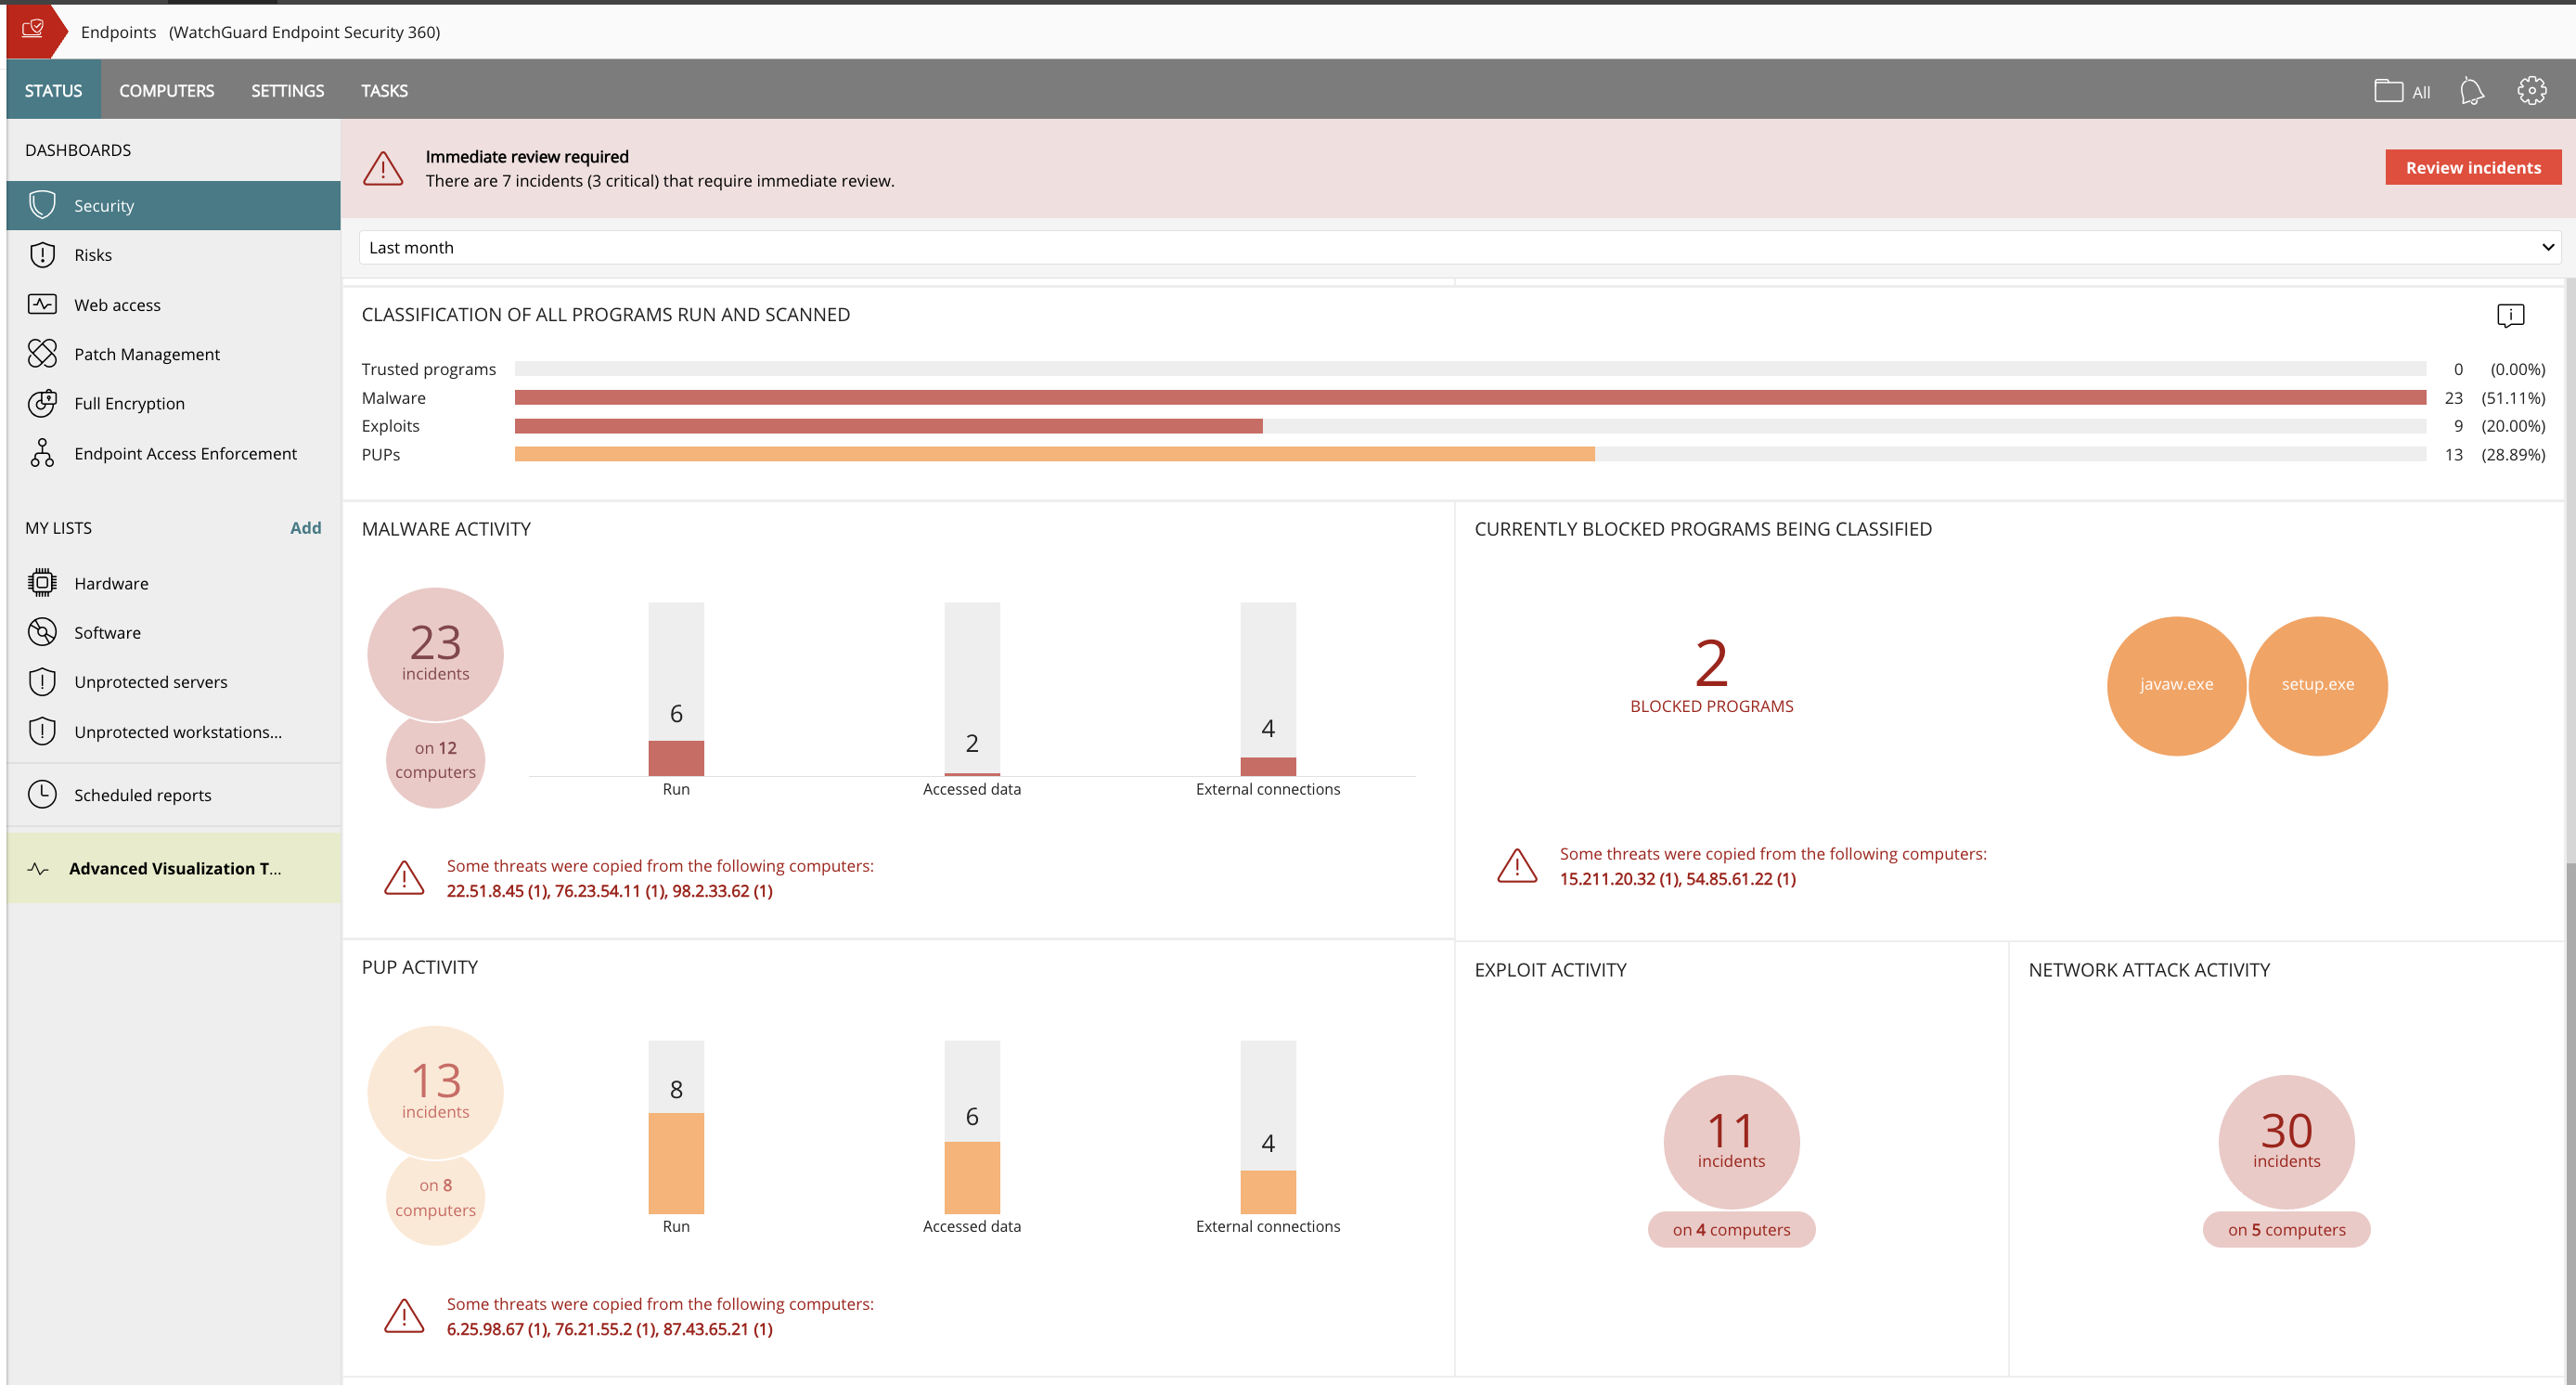
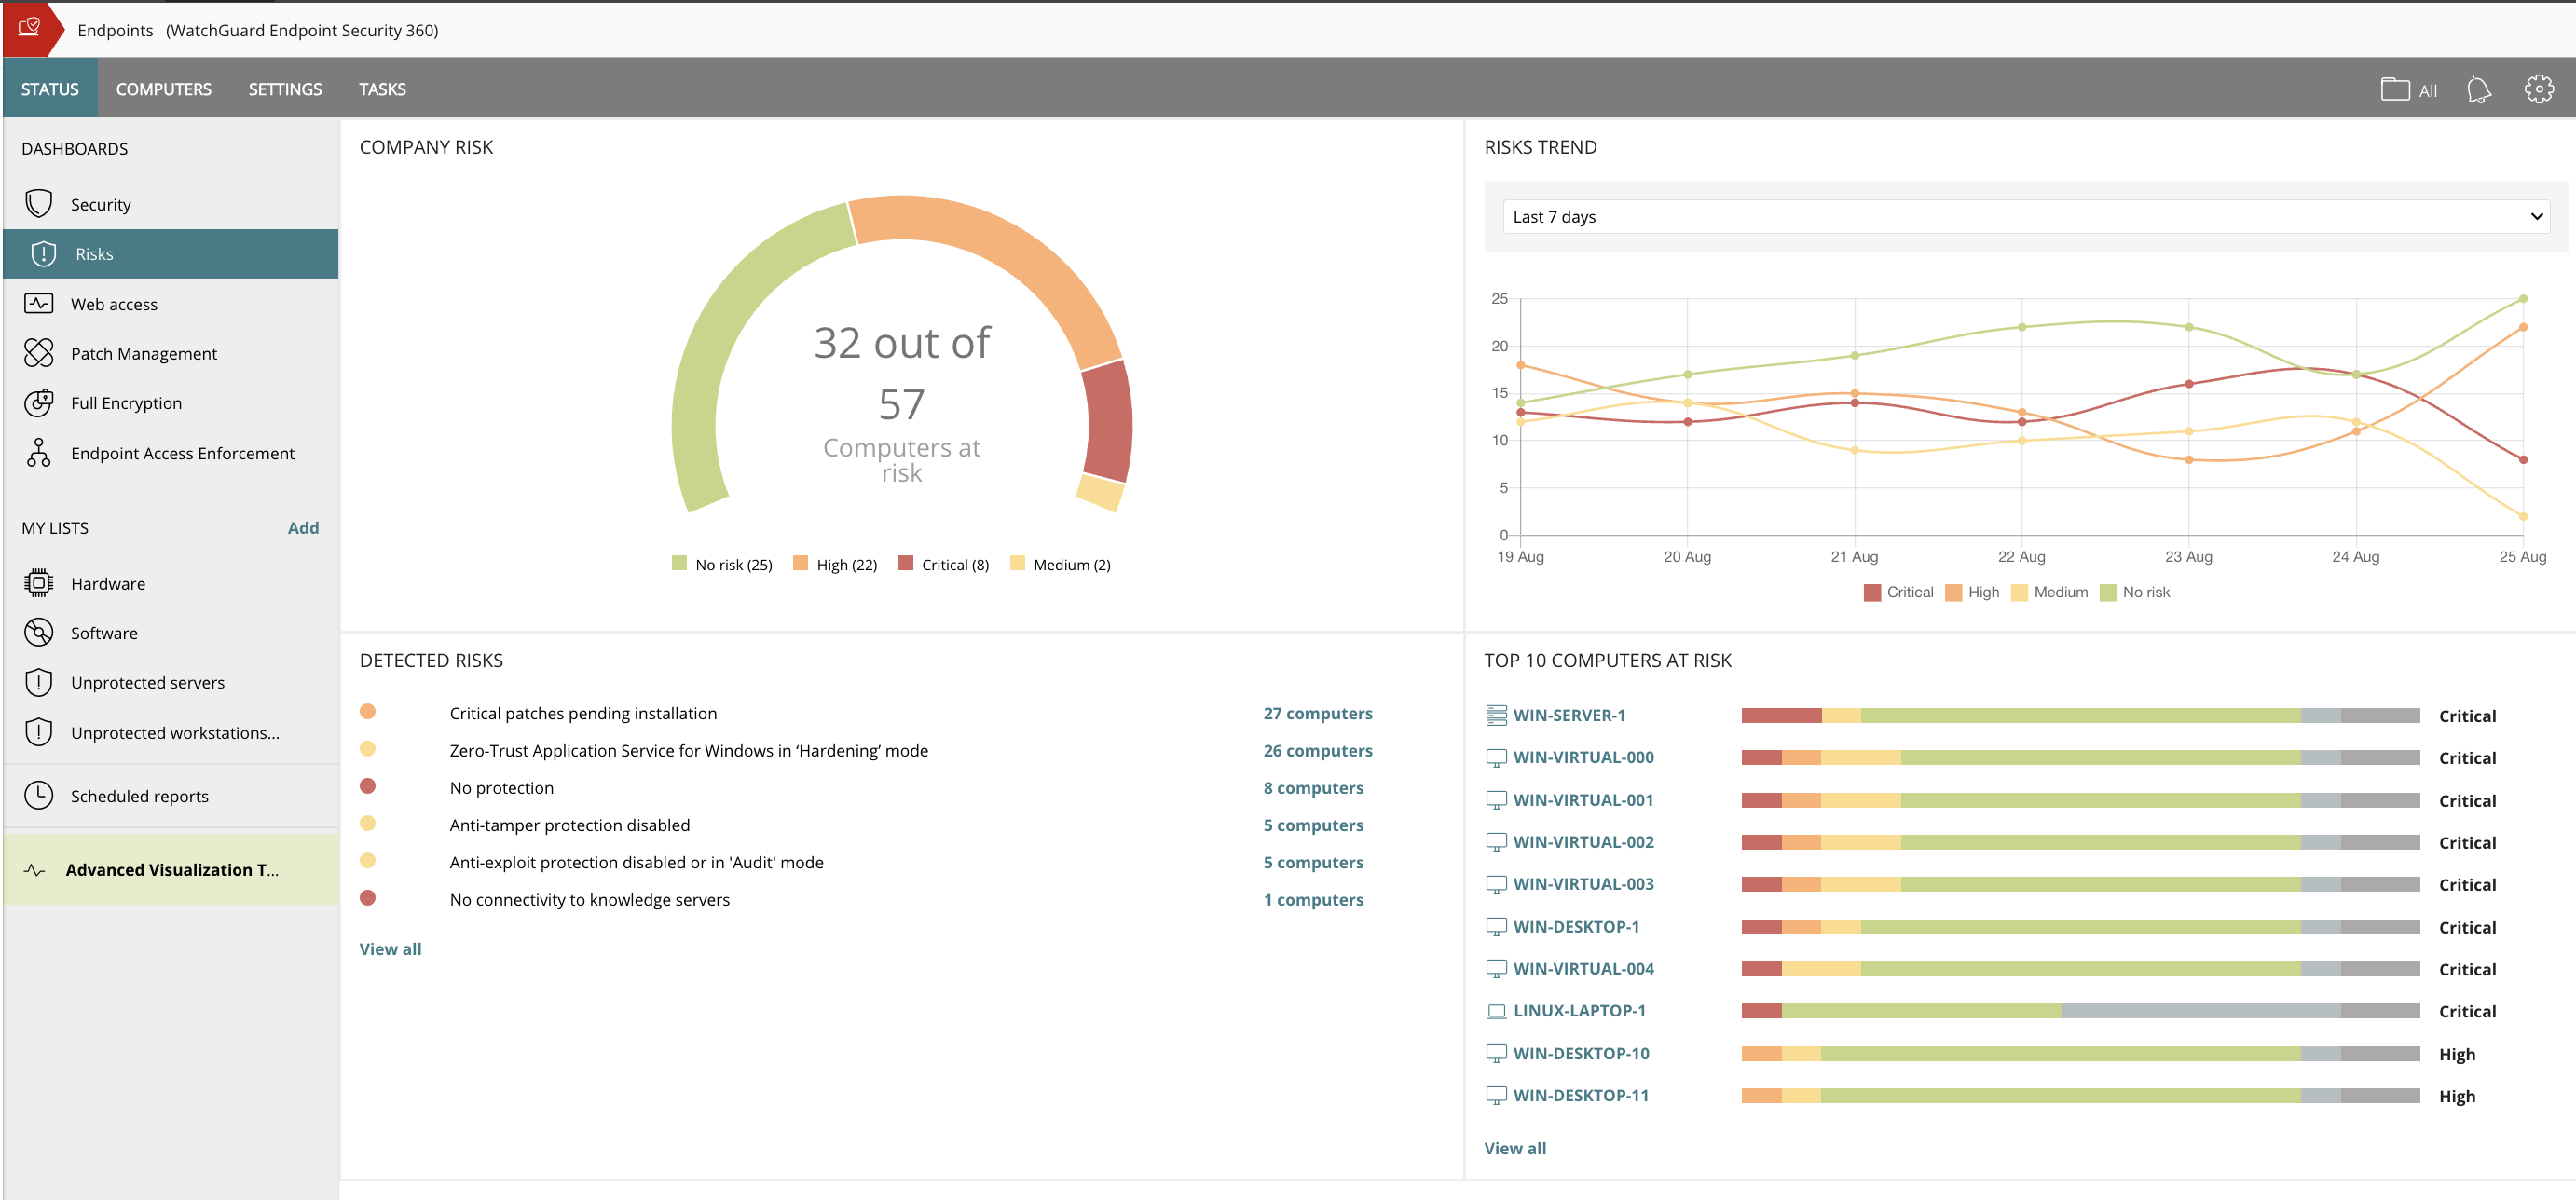
WatchGuard EPDR (formerly Panda Adaptive Defense 360) combines next-generation antivirus protection, endpoint detection and response (EDR), patch management, content filtering, email security, full disk encryption, and more, into one package. The platform touts a unique zero-trust security service that certifies the legitimacy and safety of all running applications thanks to a combination of automated, AI-driven processes and investigation services provided by a team of malware analysts.
We use Defender in the cloud. We are currently using Defender in the cloud and also evaluating the XDR solution for programmatic. It's just arguments, the defense in depth. You have Defender Endpoint and then you have what you have in the cloud as well, so it's just augmenting …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
At the time, Microsoft Defender for Endpoint was a comparable selection with SentinelOne, but won on one important consideration for Educational Use, cost. Microsoft Defender for Endpoint was including in our Microsoft Enterprise agreement meaning that there was no additional …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Panda Adaptive Defense, in combination with Panda Systems Management, was a pretty big and powerful suite of AV software. However, the AV is pretty traditional, all things considered. ATP will always have a slight advantage due to its ability to seamlessly integrate with the …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Owner in Information Technology at AZXnetworks (Computer Networking, 51-200 employees)
Chose WatchGuard Endpoint Security
We used Kaspersky for all of our clients for many years. It was a good platform, but Panda Adaptive Defense works better and is easier to manage. Adaptive Defense 360 classifies the network environment first and will only allow trusted applications in the future upon review and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose WatchGuard Endpoint Security
It is more usable for companies which are not in Cloud, it is easier to manage, integration for different departments are better
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
CEO in Corporate at Gratopp.it (Information Technology & Services, 1-10 employees)
Chose WatchGuard Endpoint Security
For a long time, the centralized administration and the pool licenses were our intention to use [Adaptive Defense 360 / WatchGuard EPDR]. At the moment, the blocking against unknown programs and whitelisting of common programs are the main parts to use [Adaptive Defense 360 / …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose WatchGuard Endpoint Security
The other software that we've been testing doesn't have the complete stop of execution of unknown software.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
In our experience, Microsoft Defender XDR has been fantastic for phishing and account compromise scenarios, Endpoint Security, Automated threat detection and response and just generally giving a great overview through their dashboard, meaning the IT team doesn't need to switch between multiple tools to understand the full scope of an incident. In mostly remote organization like ours, it really helps to keep on top of any potential threats that we don't have the opportunity to spot in person. While it works great for us in a mostly Microsoft 365 environment, I can see how it would be less appropriate in an organization that is less integrated in the Microsoft ecosystem or uses a large number of third party tools.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I would recommend Watchguard Endpoint Security to organizations that are already using WatchGuard Firebox with the Total Security suite or those looking for an additional layer of endpoint protection. The bundled licensing provides strong value and makes it easy to extend protection from the network level to the endpoint. In our case, we primarily use it as a supplement to SentinelOne, and it integrates well in that role. The agent has been stable, the cloud management is straightforward, and it has not caused operational issues in our environment. For businesses that want added visibility and layered security alongside their primary endpoint solution, Watchguard Endpoint Security is a solid option.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One of the greatest strength of Microsoft Defender XDR has the ability to convey alert and signal in the closing point, email, identity and cloud applications in an event. Instead of obtaining isolated alert from each tool, Microsoft Defender XDR consolidates them in a full attack story, which helps the security teams to understand the scope and impact of a danger very fast.
If a user clicks on the fishing link, Microsoft Defender XDR automatically can associate malicious emails with lateral movement efforts, suspected sine-in, and endpoint activity-to protect against hours of manual probes.
The defender uses AI-powered automation for investigating and treatment of Microsoft Defender XDR events. It can separate the infected closing points, can cancel the compromised tokens, or remove malicious email - without the need for human intervention.
When malware is detected on a device, the defender can separate the device, kill malicious processes, and automatically flag the same files throughout the environment, which can spread.
Because it is integrated deeply with Microsoft 365 defender, Entra ID (Azure Ad), Intune, and PurView, the defender provides native safety in the XDR Microsoft Stack. It simplifies deployment and maintenance, offering deep visibility in user activity and cloud data.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Improved algorithms to minimize false positives in threat detection, reducing the impact on security teams and preventing unnecessary investigations into non-threatening incidents.
Advanced User-Friendly Interface:
Streamlined and intuitive user interface for the centralized dashboard, making it more accessible for security professionals with varying levels of expertise.
Greater Third-Party Integration:
Increased compatibility and integration capabilities with a broader range of third-party security tools
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
EndPoint has an optional feature for automatic and remote software updates on endpoints, a handy option for keeping computers up-to-date and secure. However, it is not used to install new software but only to update it. We believe that this part is instrumental, but it is somewhat incomplete.
Another drawback is that some complementary functions to the antivirus, such as the one above, are optional and require a separate subscription.
The implementation of EndPoint requires some planning, especially the time required to harden and learn the system. This is not critical and is typical for this type of system, but it is necessary to plan it well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We are pleased with the product and have no plans to look for alternatives. We are deeply invested in Microsoft ecosystem and Defender XDR provides seamless integration to other Microsoft products. For academic institution pricing is also quite affordable. In the contrary, we hope to extend the scope of the product for our entire environment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The ease of use, pricing, support, reliability, and quality of the product. Panda / WatchGuard products are highly rated, priced right and easy to maintain. All of this make it very easy to renew and purchase new licenses for us and our clients.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Once configured, it's very usable for any security team or IT Analyst. It'll give you everything you need to know in a single consolidated dashboard, and while you can certainly dive deeper with a very feature rich platform, generally it's very usable. I gave it an 8 as some of the advanced features do have a very strong learning curve, while routine tasks are quite straightforward, some of the features such as threat hunting, custom detections and automated response workflows do have a bit of a learning curve and will require some research and experience to get to grips with
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Easy and intuitive MSP management portal to manage all of your clients from a single pane of glass. Policies can be pushed down globally or individually based on needs. The client portal allows access to their tenant information and installs only which is nice if you are working with clients who might have an internal person or an IT team that also wants access to things to manage themself.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
In our experience there has been very little downtime for Microsot Defender XDR. For us there hasn’t been any single incident where we needed the product and it was not available.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The software is 100% managed on a cloud platform that can be managed via an account even if they are not present within the company network where the software is installed, I even always opened the control panel on the browser of my smartphone to monitor the situation.I have never experienced any abnormal software crashes
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Most of the time the product is as responsive as you might expect from cloud product. Occasionly the product is little slugish, this has been at most a slight irritation. Reports generate quickly ennough for our needs. We also not have found that Defender XDR slows down systems that it is integrated with
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The only annoyance I complain, if we want to be picky, is the fact of the constant disconnections from the control panel.Every about 4 hours the account logs out even if I set the "remember this device" flag; having said that I have not noticed neither slowdowns nor conflicts with other software
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Their support throughout our onboarding of the product was fabulous. They not only took the time to carefully explain to teams not as well equipped with the lingo but explained to the tech team how to teach the other teams to be successful. They never once seemed impatient or annoyed with basic questions and didn’t pretend to know something when they needed to research an answer
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I gave it a 10 because I compare it to air conditioning. I need it to work every day, 24/7. I need it to be reliable and not something that requires a ton of interaction from staff to make sure it works every day. In addition, I should be able to run other things at my house when the AC is on. Panda fits that description.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Microsoft Provides a good training for the Microsoft 365 Defender and has a good learning paths to learn and take the exams and get your Certifications.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The training was very helpful. It demonstrated how to configure the service for initial install, items to monitor, and how to set up for ongoing protection. Hands on training is more helpful but this is a good starting point
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
seemless and almost transparent. can be deployed by script if needed so every endpoint on our system get's it. if you have intune it gets dumped on the the endpoint by policy so nothing escapes it
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Implementation shouldn't present any problems in standard office environments. In environments with development teams, however, caution is needed. If zero trust is enabled, mechanisms must be in place to ensure that internal software isn't classified as a false positive (software certificate, exception folder, etc.)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Our product in that area, for instance as a security platform and for us it is for the moment really bad point. We started to move in that direction that there is that disconnect from the client management. So if there is some action that needs to be executed detected by security team, there is not an easy way to make that available to the team that is responsible for managing the identities as users, as the devices
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We didn't spend much time looking into Symantec - but it was the software of choice for the district before I joined. That said, we were pretty easily talked into Watchguard Endpoint Security as we were already in the Watchguard world of products. Moving to their EDR just seemed to make sense for our organization
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Azure cloud provides techical power to scale the product for whole organization. From organizational point of view scaling Defender XDR for various IT teams needs good collaboration and clear norms that all teams must agree to and follow.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
With the implementation of watchguard (at the beginning Panda Endpoint, but it is the same) I was able to insert in the control panel all the unauthorized software previously installed by colleagues without any authorization from the various department heads.Now any licensed software goes into lockdown and can be unlocked from the control panel
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
By committing to go all in on Watchguard Advanced EPDR across our whole client base, we maximized our price position - enabling us to offer the best endpoint security at a price better than what lesser competitive products cost.
Leveraging Watchguard Endpoint Security as part of our unified platform strategy provides better integrated security, managed through Watchguard's cloud architecture. This significantly reduces our cost to deploy, manage, and support our client's. Our improved security offering, better delivery, and stronger price position has helped us achieve 56% growth in our managed services business over the past 18-months.
Organizations that have disparate cyber security products often require specialists for each solution in their stack. Watchguard provides outstanding training resources that equip our entire technical staff - significantly improving our service delivery while lowering our overall cost of business.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info