GFI LanGuard is software used to manage and maintain end-point protection across a network. It provides visibility into all the elements in the network, helping to assess where there may be potential vulnerabilities, and enables the administrator to patch them. It is a patch management and network auditing solution.
N/A
Malwarebytes
Score8.8 out of 10
N/A
Malwarebytes is a antimalware application for home and small businesses, which blocks viruses, malware, hackers, viruses, and malicious websites.
$119.99
per year 3 devices
Sophos Intercept X
Score8.9 out of 10
N/A
Sophos Endpoint Protection (Sophos EPP) with Intercept X is an endpoint security product providing an antivirus / antimalware solution that when upgraded with Intercept X or Intercept X Advanced provides advanced threat detection and EDR capabilities.
$28
per year per user
Pricing
GFI LanGuard
Malwarebytes
Sophos Intercept X
Editions & Modules
No answers on this topic
Teams - Sole proprietor
$119.99
per year 3 devices
Teams - Boutique business
$399.99
per year 10 devices
Teams - Small office
$799.99
per year 20 devices
Intercept X Advanced
$28
per year per user
Intercept X Advanced with XDR
$48
per year per user
Sophos Managed Threat Response
$79
per year per user
Offerings
Pricing Offerings
GFI LanGuard
Malwarebytes
Sophos Intercept X
Free Trial
Yes
No
No
Free/Freemium Version
No
No
No
Premium Consulting/Integration Services
No
No
No
Entry-level Setup Fee
No setup fee
No setup fee
No setup fee
Additional Details
—
All plans include a 60-day money back guarantee. 1st year discount available for the Small office plan.
Pricing is for a 3-year commitment. Government and Education pricing available.
Director Of Information Technology in Information Technology at Alicart Restaurant Group (Food & Beverages, 201-500 employees)
Chose Malwarebytes
I found Sophos to be more resource intensive, scans take longer and affect the end user experience more. Building policies and customizations is not as intuitive with Sophos.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Information Technology and Web Support Specialist in Information Technology at Tax Executives Institute (Non-Profit Organization Management, 11-50 employees)
Chose Malwarebytes
We found Malwarebytes to be much easier to use than Kaspersky. I also think that Malwarebytes is better supported and has a better reputation for protecting its clients. We found the interface of Malwarebytes to be more intuitive. We also liked the central server software to …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Senior Associate in Information Technology at Stir Architecture (Architecture & Planning, 11-50 employees)
Chose Malwarebytes
When compared to Microsoft built-in Windows Defender, Malwarebytes edges it out because it's in the business of detecting malware and not working with the operating system. Malwarebytes is constantly updating its definition files to make sure all potential worms are caught …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Senior Web Developer in Engineering at WebpageFX (Information Technology and Services, 51-200 employees)
Chose Malwarebytes
Malwarebytes has an effective free version (some of the others do, some don't). Malwarebytes has a slightly different focus on the type of malware it looks for. As opposed to picking one winner, I would suggest selecting a well-reviewed paid AV, and possibly supplementing …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Systems Support Engineer in Information Technology at College of William & Mary (Higher Education, 1001-5000 employees)
Chose Sophos Intercept X
I preferred the management console of Malwarebytes Endpoint Protection and the deployment capabilities of both were very similar. However, it was not my decision to make on which product to implement. I was only a tester of the product and reported back my preferences. …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Sophos Intercept X
Sophos Intercept X is one of the industry leaders for a reason. Apart from integration issues, Sophos Intercept X stands above the rest when it comes to protection and usability. I have used at least 30 different antiviruses, antimalware, and antiransomeware programs and none …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
IT Specialist in Information Technology at Zoom Drain (Consumer Services, 51-200 employees)
Chose Sophos Intercept X
Sophos Intercept X is easy to manage and deploy under your business. I think it is comparable to BitDefend with the ability to send out deployment via email or directly add it to the computer. I have noticed that Bitdefender seems to eat a lot of resources during its scans …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Sophos Intercept X
Trend Micro offered similar protection, however at the time did not offer EDR as a solution. The big benefit to Trend Micro was the capability to push out the installation of the agent to assets within the Trend Micro console, eliminating the need for a GPO or deployment …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Information Technology and Web Support Specialist in Information Technology at Tax Executives Institute (Non-Profit Organization Management, 11-50 employees)
Chose Sophos Intercept X
We used to use Symantec Endpoint Protection. At the time we were using it (it may very well be different by now), it required a bit more maintenance and we were constantly having issues with definitions not being downloaded as well as issues updating the software itself. We …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
IT Support Specialist in Information Technology at Loenbro (Construction, 501-1000 employees)
Chose Sophos Intercept X
Sophos's shields are more powerful than both McAfee's and Symantec's while using less system resources doing its active scans. It does use more power while performing a manual scan than either, but nothing that cripples the system or leaves it unusable while it is running. The …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Systems Engineer in Information Technology at NativeX (Marketing and Advertising, 51-200 employees)
Chose Sophos Intercept X
I did not have an influence on the purchase of Sophos. However, from past experience with other antivirus products, Sophos doesn't seem to bog down the systems. It scans the second a file is touched, and is great at quarantining harmful files before they can become a problem. …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
-To track the vulnerability level of a windows network. -To push windows and other application updates from a central location. -Produce reports to highlight work being done to protect a network. In some organizations, you may have to prove for audit reasons you are enforcing policies put into place around cyber-security. This software can help you track work done on an ongoing basis for such purposes.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Now, I gave it that rating because it's a handy tool for diagnosing issues. Quarantining them, and most of the time, it does fix the problem. Though with rootkits, it's been hit or miss, and sometimes perfectly valid software gets flagged erroneously. However, once you've run it, it tends to run continuously, consuming far too many resources and being a real pain to uninstall, sometimes even causing issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
To be frank, this product is fairly expensive. So I would recommend this to companies that are mid-sized or larger to condone the cost of the purchase. It does save me a significant amount of time in my day - being able to glance at the dashboard and see if there are any outstanding issues that require my attention, as not much digging must be done to accomplish this. So for our company, with a short-staffed IT department, it's incredibly helpful to us. We also qualify for Educational pricing which brings the cost down - which helps tremendously
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Low system resources, it does not slow down the whole computer when scanning or when real-time protection is enabled
Quick and frequent updates, usually people hate updating, but for malware/viruses, you want to be updated as possible. It takes less than 15 seconds and usually does it automatically. They usually send a few updates a day as they find more.
Protection features actually work when visiting known bad websites. The page will be blocked and nothing will be downloaded. It may not be what the user wants, but it's what the user needs (as the user can't know every bad website)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sophos Intercept X is great at preventing malware infections and rolling back their effects. I have seen this happen hundreds of times since we installed it
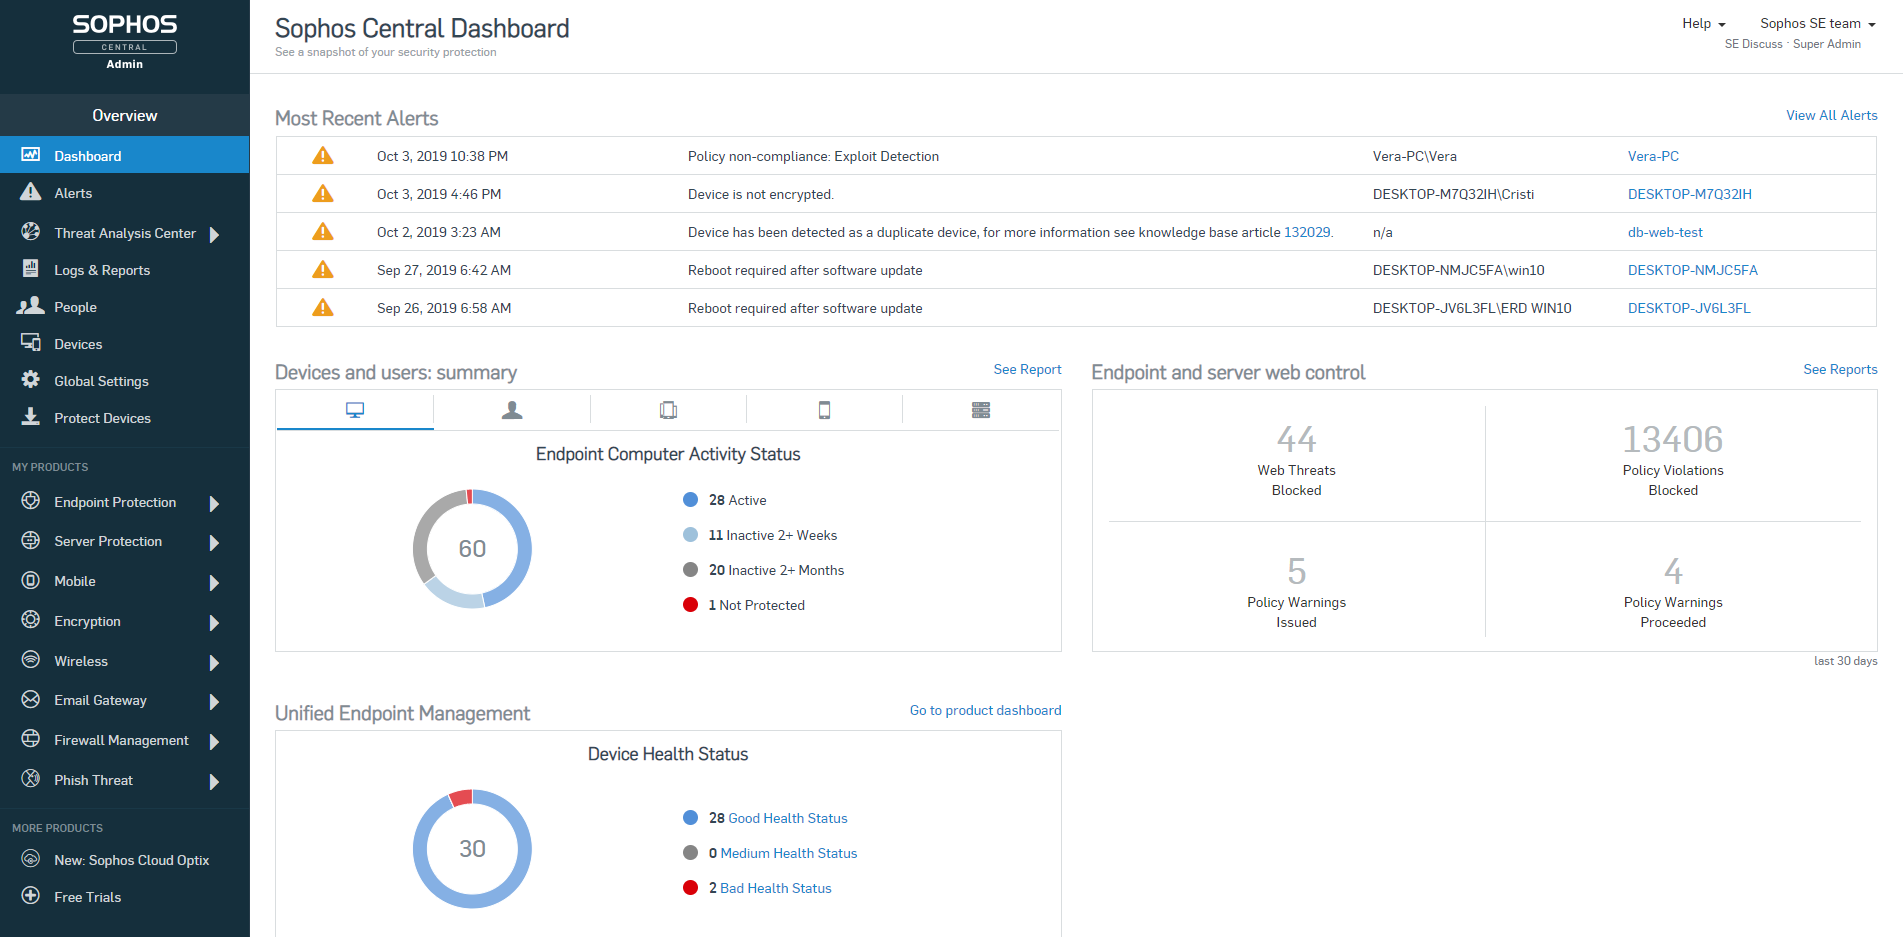
When combined with Sophos Central, you have an easy to use dashboard where you can manage all installations from a single pane of glass.
It's easy to deploy on machines and stays updated.
Good reporting features including alerts sent to the admin if there's ever something wrong with it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It could be a bit of information overload which some things are shown can become noise. Maybe different levels of "security" for lack of a better term may be better where you have a summary vs detailed level when it comes to rating the vulnerability of the entire network.
I find I sometimes have issues with PCs on a different network accessed across a VPN where timeouts often occur with very large updates. This aspect can be improved.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One of the main things that malwarebytes is missing as a company, is phone support for its clients. All support questions has to go thru email only. This is not acceptable for issues that needs to be resolved quickly.
There is an issue when installing the client on a machine, it has a set amount of time where the software can register with the management server. The issue with this is, with machines that are over a wide area network, slow connection speeds can cause the software not to register. When that happens, it never re attempts to register in the future.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sophos OOTB policies are very strict and they don't offer anything less strict without you creating new custom policies. I'm sure this is deliberate because the product starts you out in the safest way possible but it means that you will have lots of calls to your tech support desk when you first deploy it unless you do somewhat extensive testing beforehand.
Sophos Intercept X is currently broken (at least the DLP component) by having secure boot turned on in the UEFI/BIOS. If any user wants to be able to write data to a USB drive or floppy from their PC (yes we still have a couple users who need to use floppies) we have to turn off secure boot on their PC, even if the DLP policy for that user/PC combination specifies that the user and PC are allowed to write to USB/floppy. This would be a very serious problem if it weren't for the fact that we have very few users who need to write files to USB. For us it's OK but I bet it would be a deal-breaker for others.
I don't see a whole lot of evidence that Intercept X is any different than any other anti-virus, so maybe their admin alerts just don't clearly identify when they have identified a zero-day threat or maybe we just haven't had any zero-day threats.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The last time we renewed Malwarebytes, we renewed for a 3 year renewal. That should describe the confidence we have in the product. Plus the cost savings impact year after year.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Usability-wise, it's pretty good, and it gets the job done. But once that's finished, the nags, the pop-ups, and the fact that it slows older systems down recklessly really cost it rating points. It becomes a clutter, and one of the first things we check when we receive reports that a PC is slow is whether it's running malware. Once we uninstall it, the PC is usually easily 40-50% faster. That's too much in the way of resources for something that wants to always run in the background.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The usability has never been a problem. Sophos Intercept X is a program you can install and let protect your company without much intervention. Apart from a few policies, Sophos will keep you protected better than most any product on the market. Sophos Intercept X works quite well when you are looking to "tighten your grip" on user's access to websites, programs, and add-ons.
I only tried to access there support once and it was a relatively pain-free process. They also have a lot of documentation available online which can be used to learn and tailor the software to suit your needs. It just takes time and effort to plan, execute and monitor going forward.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The Malwarebytes customer support team is awesome! They really go above and beyond to help you with whatever issue you may experience. It is not that we need to contact their support team often, but the few times we did, we would speak to someone who knew what they were talking about and able to solve our problem. It is a comfort knowing that aside from a great product, you are getting a reliable support structure.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Most of the support reps are fantastic. There have been a few though that have had to be escalated via Account Manager when they haven't followed up but this is a rare instance, and often followed up by the Support Manager for APAC.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
WSUS was the other alternative I considered but I believe GFI takes updates, reporting, and functionality to a different level for an enterprise/medium-size business environment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Avast and Norton's products were part of the testing for us but the cost was very high for them and the products were not light on the machine. They took up a lot of memory and slowed the computers down. Malwarebytes although may lack some feature, is a very light software.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Webroot Endpoint Protection is not even in the same league as Sophos Intercept-X. I have tested and compared both sides by side, run simulations and it's not even close. Plus the Sophos central management is so much better. Easier to view user activities and apply policies and remediate threats. Sophos is the clear winner between these two products.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Certainty. It allows you to know where on your network needs attention.
Peace of mind. As security professionals, we can only put the necessary things in place to prevent malicious persons from exploiting a network. The software allows you to know whether or not your risk of exploitation is high or low. and if high what to do with it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive Impact: Have not had to remediate malware/virus infections since installed.
Positive impact: As far as browsing goes, we can boldly go where no man has gone before. No, really, I am confident when I am clicking on search engine results that if something get past my trained eye, Malwarebytes will pick of the slack.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Once our technical and commercial areas got certified, the ROI over the time spent, is great. Actual customers, and/or new ones with other tools, feel safe and advised, once they get in touch with us.
When Sophos EndPoint is being compared against Web Management Tools (competitors), we have failed to deliver, nevertheless, there is a version of Sophos Central (Cloud) which achieves this requirement at 100% and more, since is Cloud Based (on AWS).
We are grateful to be on Sophos "Radar" as a Platinum Partner, and "The Americas" valued partner, we have seen our business grow, thanks to this kind of technology, throughout the years.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info