CrowdStrike offers the Falcon Endpoint Protection suite, an antivirus and endpoint protection system emphasizing threat detection, machine learning malware detection, and signature free updating. Additionally the available Falcon Spotlight module delivers vulnerability assessment with no performance impact, no additional agents, hardware, scheduled scans, firewall exceptions or admin credentials.
$59.99
per endpoint/month (minimum number of endpoints applies)
Microsoft Defender for Endpoint
Score8.8 out of 10
N/A
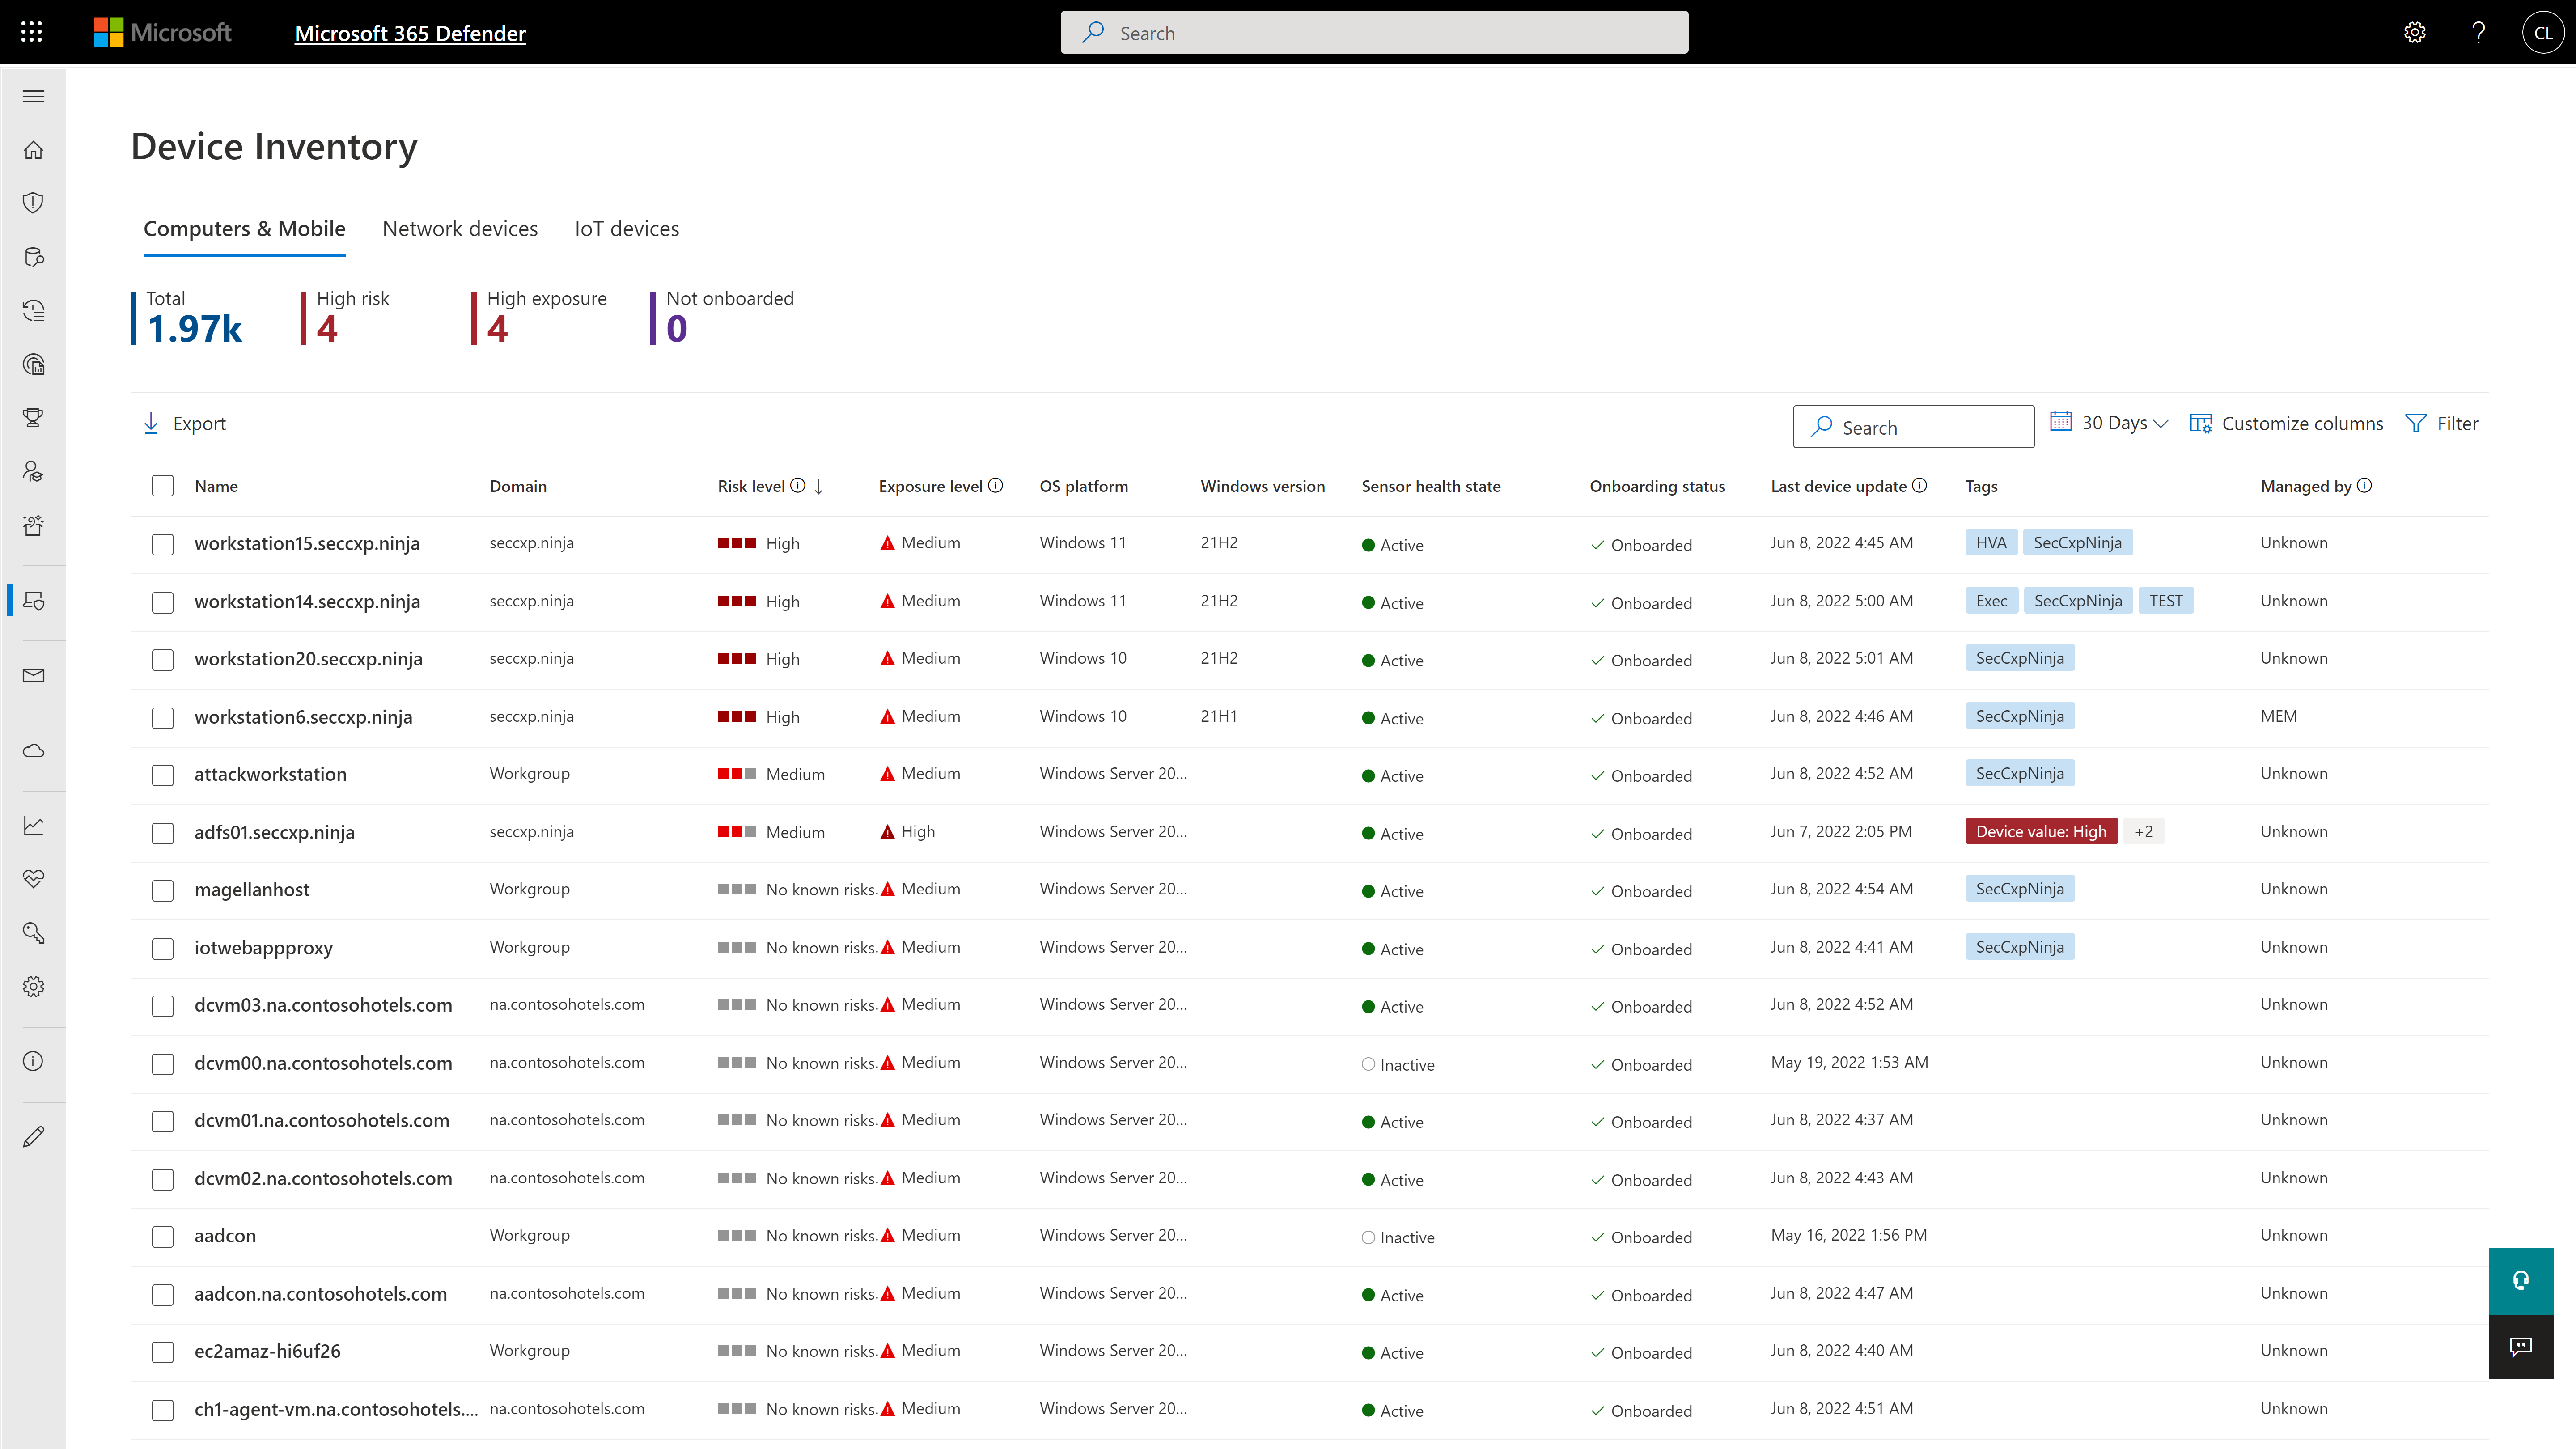
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Microsoft Defender XDR
Score8.7 out of 10
N/A
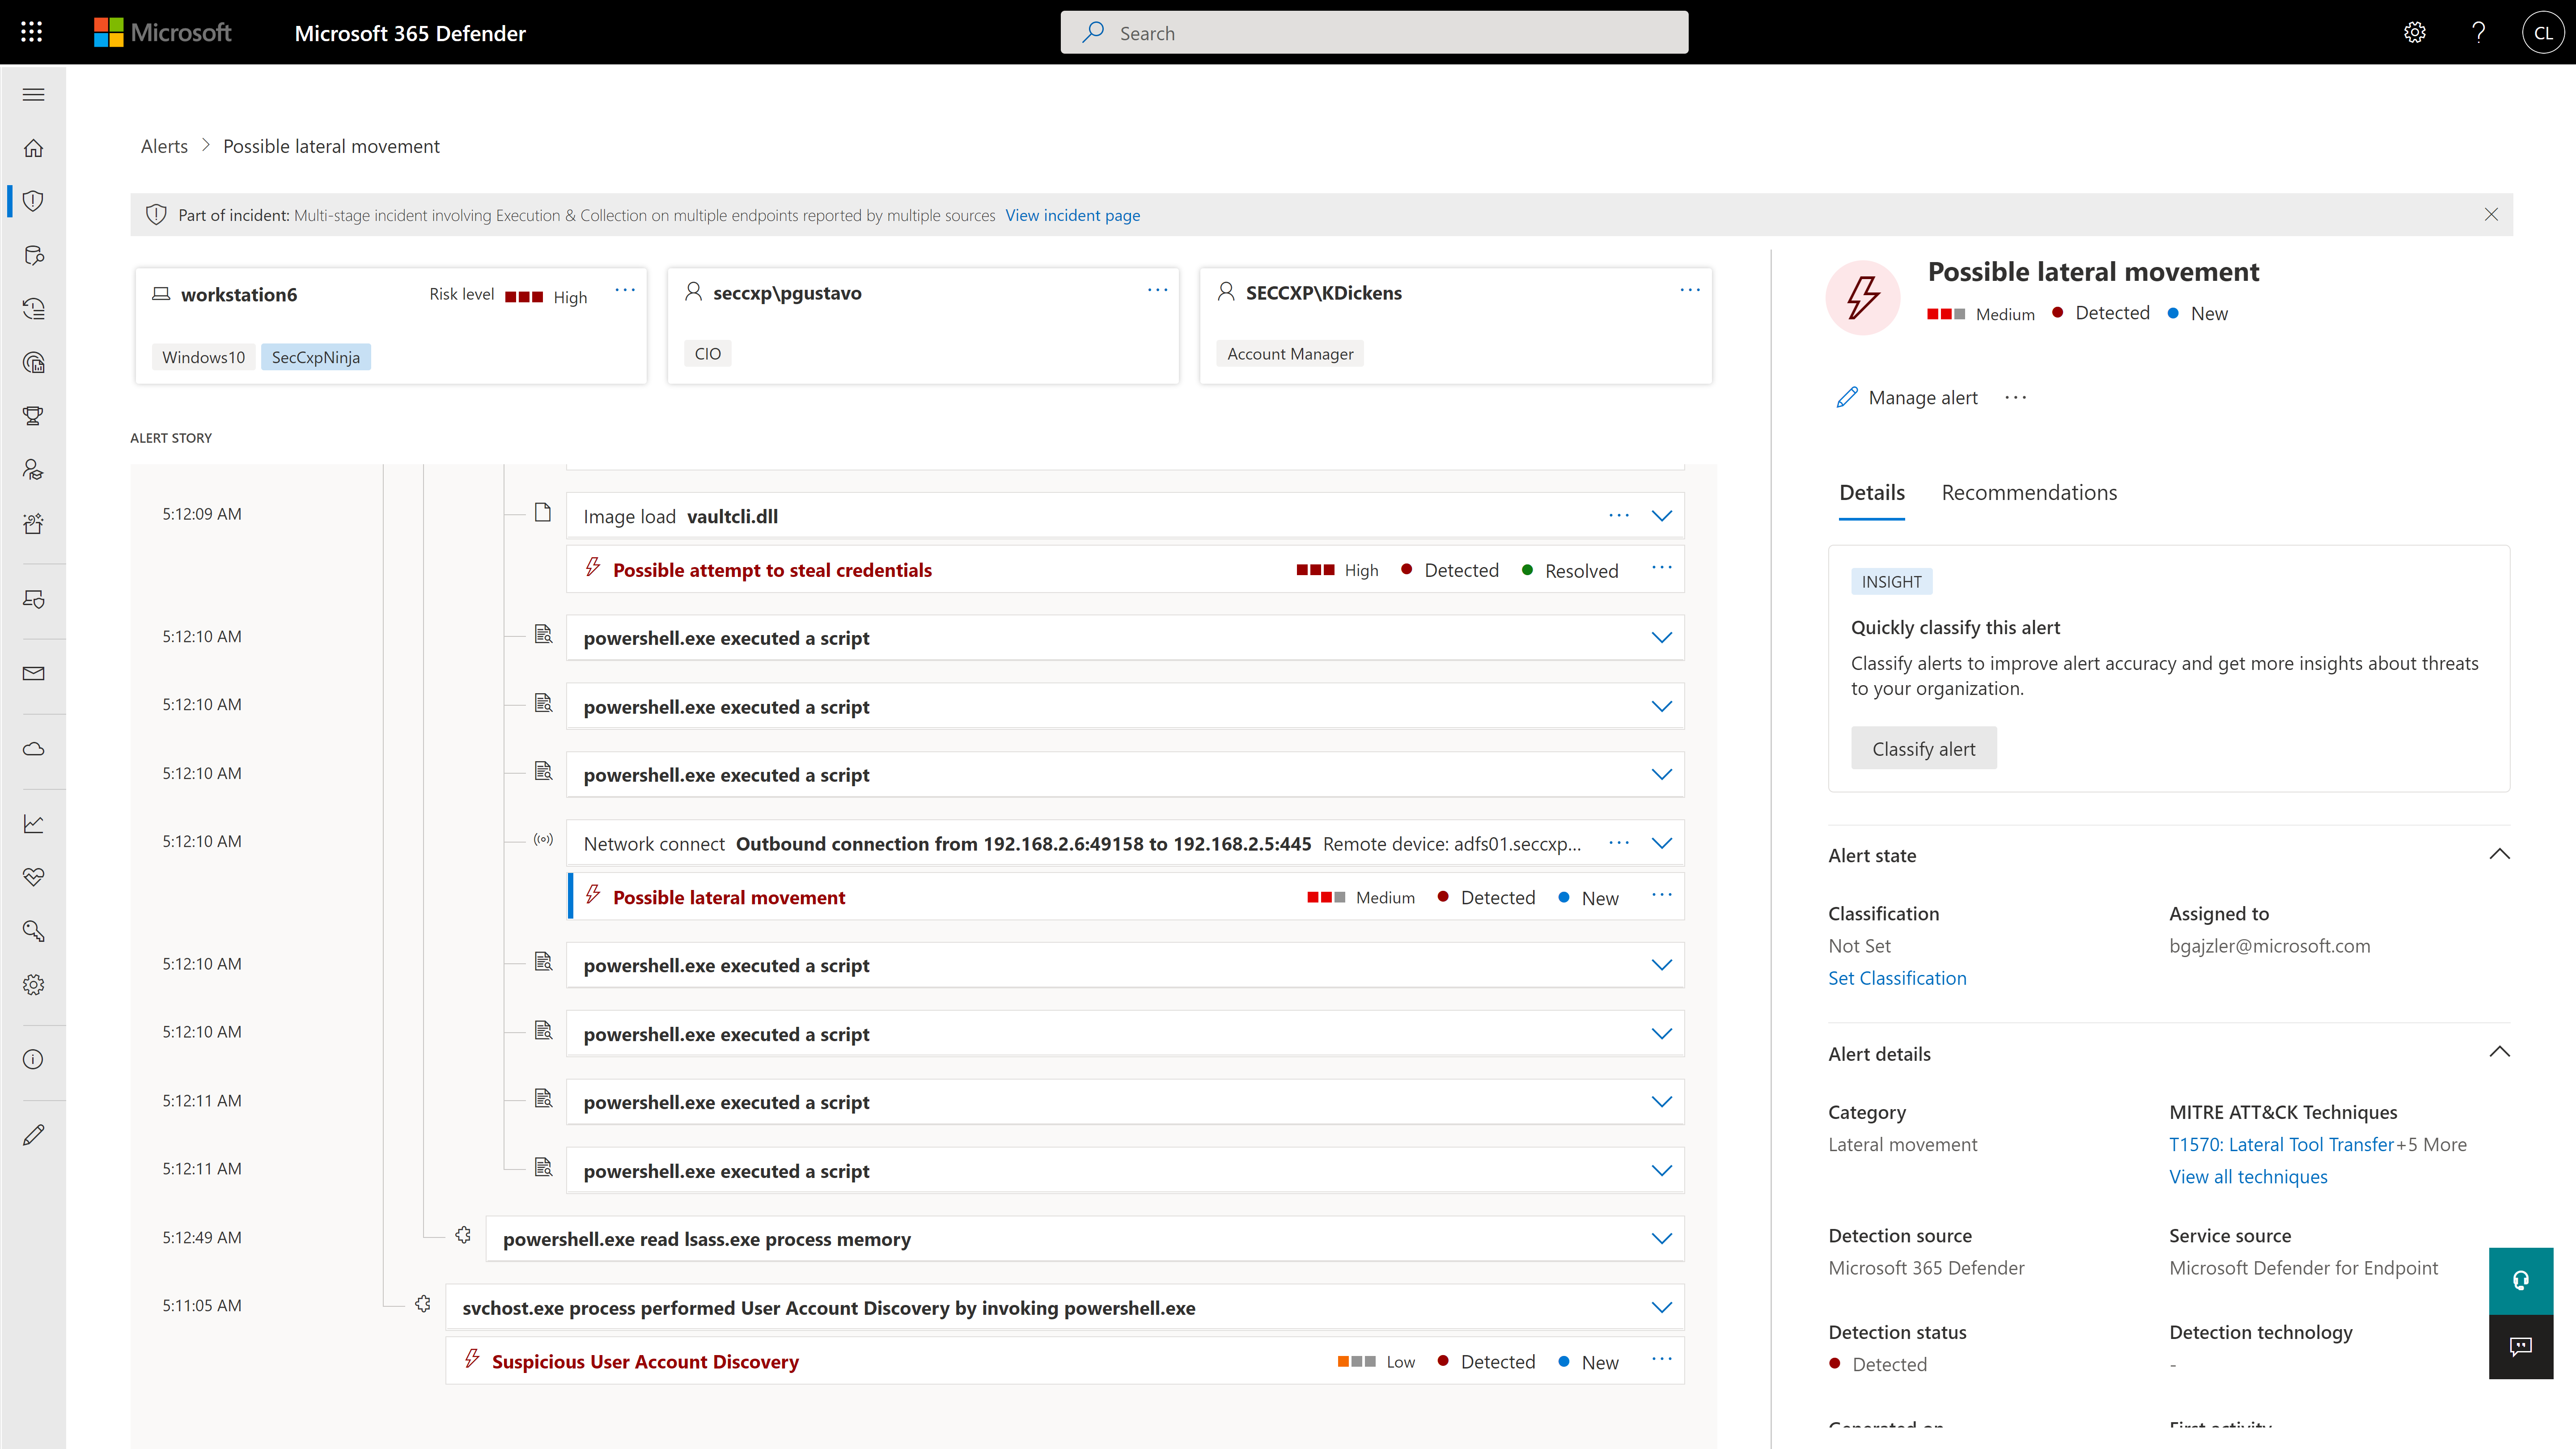
Microsoft 365 Defender combines SIEM and XDR capabilities for Microsoft 365 environments, encompassing threat detection, post-breach detection, automated investigation, and response for endpoints. Additionally, it protects cloud apps, emails and documents, and employee identities.
N/A
Pricing
CrowdStrike Falcon
Microsoft Defender for Endpoint
Microsoft Defender XDR
Editions & Modules
Falcon Go (Small Business)
$59.99
per endpoint/month (minimum number of endpoints applies)
Falcon Go (Small Business)
$59.99
Falcon Pro
$99.99
per endpoint/month (for 5-250 endpoints, billed annually)
Falcon Enterprise
$184.99
per endpoint/month (minimum number of endpoints applies)
In my opinion, CrowdStrike Falcon provides superior detection and prevention capabilities over Jamf Protect. At the time we purchased (2017) CrowdStrike Falcon was more advanced than SentinelOne and Microsoft Defender for Endpoint.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose CrowdStrike Falcon
The POC they did for us convinced us of everything we could achieve with CrowdStrike Falcon and how advanced the integration with other solutions was.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose CrowdStrike Falcon
CrowdStrike Falcon is way ahead of Symantec, and covers features that defender XDR doesn't, even if you purchase all the addons. I think the only real competitors are Sentinel One, maybe Palo Alto or Huntress, or Carbon Black.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose CrowdStrike Falcon
CrowdStrike Falcon is an industry leader in this sector and is superior in its low overhead agent, having minimal impact on end-users. We plan to migrate our macOS fleet when our existing contract expires.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose CrowdStrike Falcon
It is superior on the following two: Advanced threat detection because AI and ML can analyze vast amounts of data to identify subtle patterns that might indicate malicious activity, even zero-day attacks (previously unknown threats).Reduced false positives because it can help …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose CrowdStrike Falcon
At the time of purchase CrowdStrike provided the best featureset and value proposition for the organisation. The cloud first nature of the product and the mix of heuristic and behaviour based detection technologies was better than anything else that we looked at.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Team Lead Cyber Security in Information Technology at Lahore University of Management Sciences (LUMS) (Higher Education, 1001-5000 employees)
Chose CrowdStrike Falcon
It was the easiest to deploy and manage, while the dashboard was also very clear and precise in terms of useful information. Another major reason in selection CrowdStrike Falcon was its AI and ML detection capabilities which really impressed us during evaluation. Other tools …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose CrowdStrike Falcon
CrowdStrike Falcon provides a single solution to complex problems along with the ability to contain a machine and remotely execute programs using admin dashboard and administrator capabilities
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose CrowdStrike Falcon
The logs analysis is very easy to use as it uses splunk in the backend. The automated SOAR features helps to save time and response on the incidents. The threat intelligence is very up-to-date with the recent cyber attacks.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose CrowdStrike Falcon
Since CrowdStrike is a cloud-native platform, it reduces the need to maintain many servers on-premise and worldwide architecture. McAfee uses very high CPU and RAM resources on endpoints and servers. Identity protection feature is a huge step towards zero trust implementation.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose CrowdStrike Falcon
CrowdStrike Falcon Endpoint certainly comes in with a slight price premium compared to other offerings, but when you're talking about your last line of defense against malware it's well worth it. From a feature perspective, many players offer similar feature sets but what sets …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Principal Incident Responder (Sr.) in Corporate at Verizon (Security & Investigations, 10,001+ employees)
Chose CrowdStrike Falcon
I was not part of the selection process; however after speaking with the team that did make the call, the following where the key scenarios or features that ultimately made the decision.
The number one decision from the support team was the client deployment and management of …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft
Verified User
Chose Microsoft Defender for Endpoint
We moved on from Microsoft Defender for Endpoint to a different product, CrowdStrike Falcon. And it does a lot better at detecting threats and stopping them.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Senior Cyber Security Consultant in Information Technology at LTIMindtree (Information Technology & Services, 5001-10,000 employees)
Chose Microsoft Defender for Endpoint
CrowdStrike Falcon is also a good solution for endpoint protection which offer EDR Soultion, threat hunting and AI driven threat protection. Sophos Intercept X combines next-gen antivirus with advanced EDR capabilities with its deep learning technology, exploit prevention, and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
CrowdStrike Falcon, and Sentinel One are other big ones that we use a bit. Cisco Secure Endpoint we've evaluated as well. Cisco Secure Endpoint capability-wise doesn't match up to Defender, SentinelOne, and CrowdStrike both do, but the cost profiles are a bit higher. So most of …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
SentinelOne, Hunters. There's been some other ones. I can't remember. Those are the most recent ones, though. CrowdStrike is the other one. For what I use it for right now, it's been fine. I haven't had anything I've needed more advanced than that. CrowdStrike and some of …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft has always been a secondary, aside from one company I've worked at. And the honest truth is that it's already on the endpoint and already part of the Microsoft stack in most companies; it's already there. I don't have to worry about deploying it. It's very effective …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender for Endpoint
So five years ago, when we were looking at all the different antivirus and endpoint protection, we looked at CrowdStrike, Palo Alto, put together a package with Google, and then a few other small startups in that area.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender for Endpoint
When building up policies, being independent is much easier compared to CrowdStrike, I would say.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender for Endpoint
Say licensing and cost primarily. And from our evaluation and our use cases, Microsoft Defender for Endpoint did relatively the same thing.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint is the most cost effective solution considering our Microsoft 365 licensing status. While many 3rd party solutions are great and have been used over the years, in the non-profit world, cost is a huge driving factor of items. Coupled with …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint is on par or exceeds the competitor products and provides an enterprise grade EDR solution. Based on the savings by bundling Microsoft products under the E5 license and the benefits it provides; it is an excellent choice for customers looking for …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Crowdstrike is the more feature complete product but licensing model and cost does not work well with the small business model. ESET PROTECT is considerably more complicated from a licensing perspective but once operational is a fine product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
We use Microsoft Defender for Endpoint along with Crowdstrike on some of our critical systems as it enhances the protection we have for our environment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cybersecurity Director in Information Technology at Impresoft 4ward (Information Technology & Services, 501-1000 employees)
Chose Microsoft Defender for Endpoint
We previously used CrowdStrike on our servers. However, the seamless integration of Microsoft Defender (MD) with XDR and the entire Microsoft ecosystem led us to choose Microsoft Defender for Endpoint (MDE).
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Lead Engineer in Information Technology at Rohde-Schwarz (Information Technology & Services, 5001-10,000 employees)
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint is more advantageous in our windows heavy infrastructure and it was unparalled in the ease of integration with windows endpoints. Security breaches, system crashes and outages with other competitors like Crowdstrike made it easier for us to go …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint is unique for its effortless deployment into the Microsoft ecosystem, where it taps the broadest set of threat intelligence from more than 1.5 billion endpoints. Its state-of-the-art AI-powered automated investigation and remediation minimize …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
CrowdStrike and SentinelOne. CrowdStrike, you have to deploy it, but it's the defender, it's already baked into the operating system. Same thing with SentinelOne.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Easier to integrate, less hidden fees, easier to maintain, and easier to update. Support is much better on the Microsoft side than CrowdStrike.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
We use Defender in the cloud. We are currently using Defender in the cloud and also evaluating the XDR solution for programmatic. It's just arguments, the defense in depth. You have Defender Endpoint and then you have what you have in the cloud as well, so it's just augmenting …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
I have worked with CrowdStrike and Carbon Black. Because of the performance in Linux environments.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint stacks up well against it competitors. It detects malicious files faster than other tools like CrowdStrike.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Associate Director - Practice Lead, Network and Systems Engineering in Engineering at Arcadis (Computer & Network Security, 10,001+ employees)
Chose Microsoft Defender for Endpoint
Enterprise Endpoint Protection: Microsoft Defender for Endpoint is well suited for large organizations with numerous endpoints, such as desktops, laptops, and servers, as it provides centralized management and monitoring of security across the entire network. Microsoft …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Microsoft
Verified User
Chose Microsoft Defender XDR
Microsoft Defender XDR is included with M365, so it's part of the budget.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Computer and Information Systems Manager in Information Technology at Housing Authority of the Cherokee Nation (Government Administration, 201-500 employees)
Chose Microsoft Defender XDR
Microsoft Defender XDR is deeply integrated with Microsoft 365 services, offering a single pane of glass for endpoints, email, identity and cloud apps. The competitors require additional connectors for Microsoft workloads. Microsoft Defender XDR is highly cost-effective, …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender XDR
What we like in Microsoft Defender for XDR: Native Integration with Microsoft 365 and Azure Easier license model
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender XDR
We chose Microsoft Defender XDR for the ability to correlament the dangers in the Microsoft Ecosystem, Strong Automation, and email, Identification, Estruction, Establishment Points and Cloud Apps in the same platform. This gave us the end-to-end visibility without the need to …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Manager at Puget System (Computer Hardware, 51-200 employees)
Chose Microsoft Defender XDR
We saw CrowdStrike but Microsoft Defender XDR was already in our computer. It was cheaper too cause we had Micrsoft license. CrowdStrike look cool but had many buttons and hard to read. My team like Microsoft Defender XDR because it looks same like other Microsoft thing. We …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender XDR
We have a microsoft ecosystem and we can easily implement Microsoft Defender XDR in a breeze. Using few option, we can actually start logging and managing all the data.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender XDR
I've used Trend Micro, but it's not exactly the same because Trend Micro is equivalent to one of the parts of Defender XDR, which is Defender for Endpoint. But Trend Micro has also a portal that combines all the incidents like Defender XDR, but I think the Microsoft one is much …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender XDR
Well, we're actually evaluating the other products now. We had selected Defender XDR because at the time we just got a good deal on it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender XDR
beats cylance protect, crowstrike is solid but at a costly product cannot use kapersky due to embargo norton not good enough now
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender XDR
As already stated, the main advantage of Defender is being able to use a single console to manage it and all the other 365 applications. I can state that it provides a more effective protection than Bitdefender MDR and Trend Micro Apex One while I consider CrowdStrike on the …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender XDR
Both of these tools fill up each other gaps, sometimes one catches what other does not (from EDR perspective).
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender XDR
Microsoft 365 is easier to use and offers brooder capability in the Microsoft cloud.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Crowdstrike is a unified platform for monitoring endpoint devices, whether they're workstations, servers, cloud-native machines, or even mobile devices. It uses AI/ML to monitor anomalies and suspicious behavior, including zero-day attacks. It is suitable for large organizations but may be costlier or less appropriate for smaller organizations, those who want an on-prem EDR setup, and those who need custom scanning based on compliance requirements.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
In our experience, Microsoft Defender XDR has been fantastic for phishing and account compromise scenarios, Endpoint Security, Automated threat detection and response and just generally giving a great overview through their dashboard, meaning the IT team doesn't need to switch between multiple tools to understand the full scope of an incident. In mostly remote organization like ours, it really helps to keep on top of any potential threats that we don't have the opportunity to spot in person. While it works great for us in a mostly Microsoft 365 environment, I can see how it would be less appropriate in an organization that is less integrated in the Microsoft ecosystem or uses a large number of third party tools.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One of the greatest strength of Microsoft Defender XDR has the ability to convey alert and signal in the closing point, email, identity and cloud applications in an event. Instead of obtaining isolated alert from each tool, Microsoft Defender XDR consolidates them in a full attack story, which helps the security teams to understand the scope and impact of a danger very fast.
If a user clicks on the fishing link, Microsoft Defender XDR automatically can associate malicious emails with lateral movement efforts, suspected sine-in, and endpoint activity-to protect against hours of manual probes.
The defender uses AI-powered automation for investigating and treatment of Microsoft Defender XDR events. It can separate the infected closing points, can cancel the compromised tokens, or remove malicious email - without the need for human intervention.
When malware is detected on a device, the defender can separate the device, kill malicious processes, and automatically flag the same files throughout the environment, which can spread.
Because it is integrated deeply with Microsoft 365 defender, Entra ID (Azure Ad), Intune, and PurView, the defender provides native safety in the XDR Microsoft Stack. It simplifies deployment and maintenance, offering deep visibility in user activity and cloud data.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Improved algorithms to minimize false positives in threat detection, reducing the impact on security teams and preventing unnecessary investigations into non-threatening incidents.
Advanced User-Friendly Interface:
Streamlined and intuitive user interface for the centralized dashboard, making it more accessible for security professionals with varying levels of expertise.
Greater Third-Party Integration:
Increased compatibility and integration capabilities with a broader range of third-party security tools
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Crowdstrike has a large suite of tools built for helping the engineers triage and respond to security event whenever identified. The ability to customize the security policies and implement more granular policies to different devices based on the functionality is unmatched. Crowdstrike provides so much of ability in a decent budget which ascertains the value for money or ROI.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We are pleased with the product and have no plans to look for alternatives. We are deeply invested in Microsoft ecosystem and Defender XDR provides seamless integration to other Microsoft products. For academic institution pricing is also quite affordable. In the contrary, we hope to extend the scope of the product for our entire environment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I think it is a complete and very trustful XDR platform, with very few False Positives. It is very well supported by highly skilled professionals on all levels: from pre-sales engineers, Customer Account Managers and support engineers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Once configured, it's very usable for any security team or IT Analyst. It'll give you everything you need to know in a single consolidated dashboard, and while you can certainly dive deeper with a very feature rich platform, generally it's very usable. I gave it an 8 as some of the advanced features do have a very strong learning curve, while routine tasks are quite straightforward, some of the features such as threat hunting, custom detections and automated response workflows do have a bit of a learning curve and will require some research and experience to get to grips with
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
In our experience there has been very little downtime for Microsot Defender XDR. For us there hasn’t been any single incident where we needed the product and it was not available.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Most of the time the product is as responsive as you might expect from cloud product. Occasionly the product is little slugish, this has been at most a slight irritation. Reports generate quickly ennough for our needs. We also not have found that Defender XDR slows down systems that it is integrated with
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Any time we need to engage the Crowdstrike Falcon Complete Team, their response is switch, thorough, and they are sure to not close out any request until the customer confirms that they have provided an acceptable resolution. If I ever need anything from the account team related to the product, I also get a response from them within minutes typically to address my question. Top notch customer service!
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Their support throughout our onboarding of the product was fabulous. They not only took the time to carefully explain to teams not as well equipped with the lingo but explained to the tech team how to teach the other teams to be successful. They never once seemed impatient or annoyed with basic questions and didn’t pretend to know something when they needed to research an answer
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
There is limited amount of learning that can be completed in an in-person training available. In my opinion, the self-paced learning provided by Falcon portal is more useful over in-person training. The support from Falcon is great and useful to overcome difficulties, if any.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The training provided by Crowdstrike Falcon is complete in terms of the depth of technical knowledge and teaches the users about going through with the platform. There are lots of jargons for different tools that Crowdstrike Falcon has and this training teaches them all which helps in managing the platform better. Plus, the regular knowledge checks are also very helpful for the end user.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Provides a good training for the Microsoft 365 Defender and has a good learning paths to learn and take the exams and get your Certifications.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
seemless and almost transparent. can be deployed by script if needed so every endpoint on our system get's it. if you have intune it gets dumped on the the endpoint by policy so nothing escapes it
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It was just a legacy AV program onboarded during initial setup days. As the org. As it expanded, its threat landscape also grew, and we needed a next-gen solution to protect against evolving threat vectors. Falcon EDR was the one that solved all these in a single place.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Our product in that area, for instance as a security platform and for us it is for the moment really bad point. We started to move in that direction that there is that disconnect from the client management. So if there is some action that needs to be executed detected by security team, there is not an easy way to make that available to the team that is responsible for managing the identities as users, as the devices
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Azure cloud provides techical power to scale the product for whole organization. From organizational point of view scaling Defender XDR for various IT teams needs good collaboration and clear norms that all teams must agree to and follow.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
CrowdStrike Falcon's proactive threat mitigation has significantly reduced the risk of successful cyber attacks, resulting in tangible savings related to potential data breaches or system compromises.
The cloud-native architecture and automated features have improved operational efficiency.
The platform's real-time visibility and threat hunting capabilities have drastically improved incident response times.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info