

What is WatchGuard Cloud Detection & Response?
WatchGuard Cloud Detection & Response (CloudDR) is a cloud security service for managed service providers (MSPs). It monitors software-as-a-service (SaaS) applications and cloud accounts for configuration weaknesses, compliance gaps, unapproved applications, risky integrations, and identity-based threats.
Key Capabilities
- Identity Threat Detection and Response: CloudDR applies named threat rules (Credential Stuffing, Mass Data Download, MFA Enforcement Disabled, and others) to account activity, each mapped to MITRE ATT&CK techniques.
- Cloud Configuration Monitoring: The service continuously evaluates cloud application settings for security gaps and configuration drift.
- Compliance Framework Scoring: Findings are scored against nine frameworks: CIS Controls, SOC 2, HIPAA, GDPR, ISO 27001:2022, NIST SP 800-53, NIST CSF, CSA STAR, and PCI DSS.
- Shadow IT and Shadow AI Discovery: CloudDR identifies unapproved cloud applications, AI services, OAuth connections, and integrations, and rates each discovered vendor with a Trust Score covering security posture, certifications, supply chain, and CVE exposure.
- Automated Remediation: Five response actions (Report the Threat, Disable or Delete Actor's Account, Remove Privileged Access, Revoke All Active Sessions) run individually, automatically, or in bulk; full action set on Microsoft and Atlassian.
- Multi-Tenant Management: Centralized visibility across customer accounts, with standardized workflows and reporting.
Audience & Use Cases
- Audience: MSP security teams, analysts, and technicians managing multiple customer environments.
- Use Cases: Continuous monitoring, compromised-account investigation, compliance assessment, Shadow IT discovery, and remediation across tenants.
Technical Specifications
- Delivery Model: Agentless, with option to add the FireCloud Agent for endpoint visibility
- Management Model: Centralized, multi-tenant administration
- Data Refresh: Findings within 30 minutes of approval; data syncs every 24 hours, up to 48 for some applications
- Supported Environments: Microsoft 365, Entra ID, Google Workspace, Okta, OneLogin, Duo, Atlassian, other SaaS applications, and custom integrations
- MSP Integrations: ConnectWise PSA and HaloPSA, cloud and on-premises
- Operational Context: Extends endpoint, network, and identity security into cloud applications
Categories & Use Cases


Screenshots

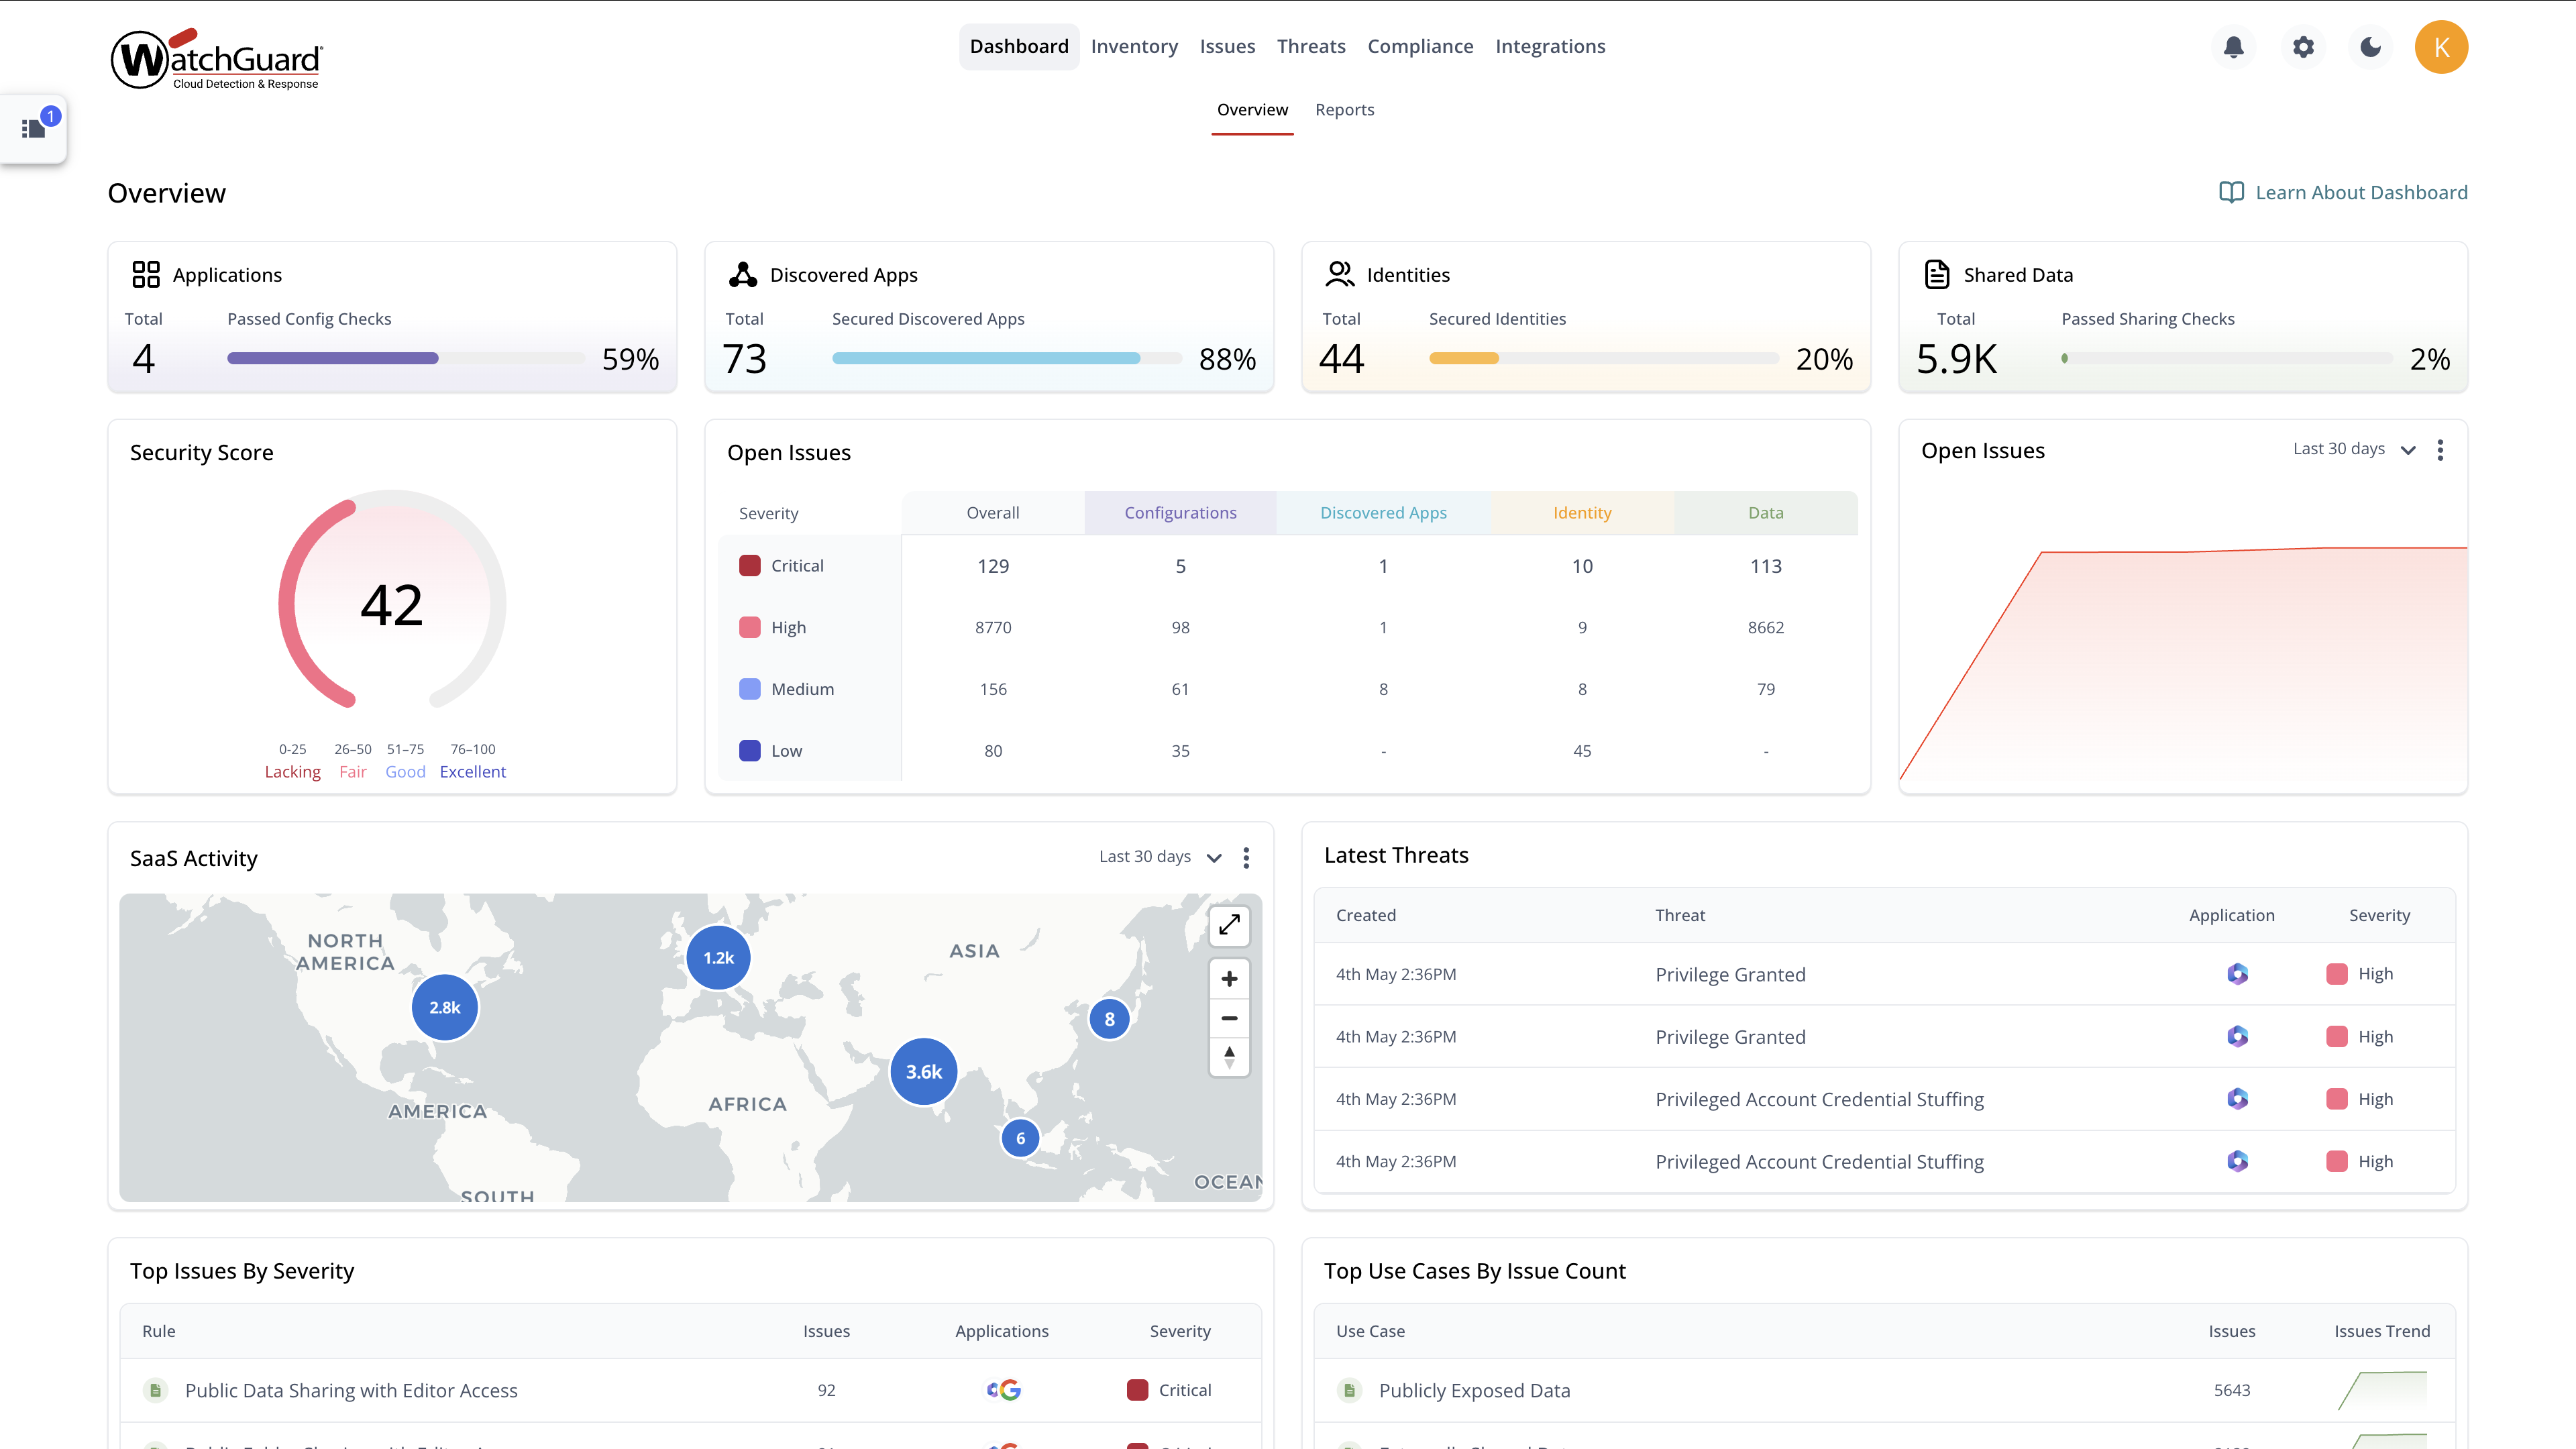


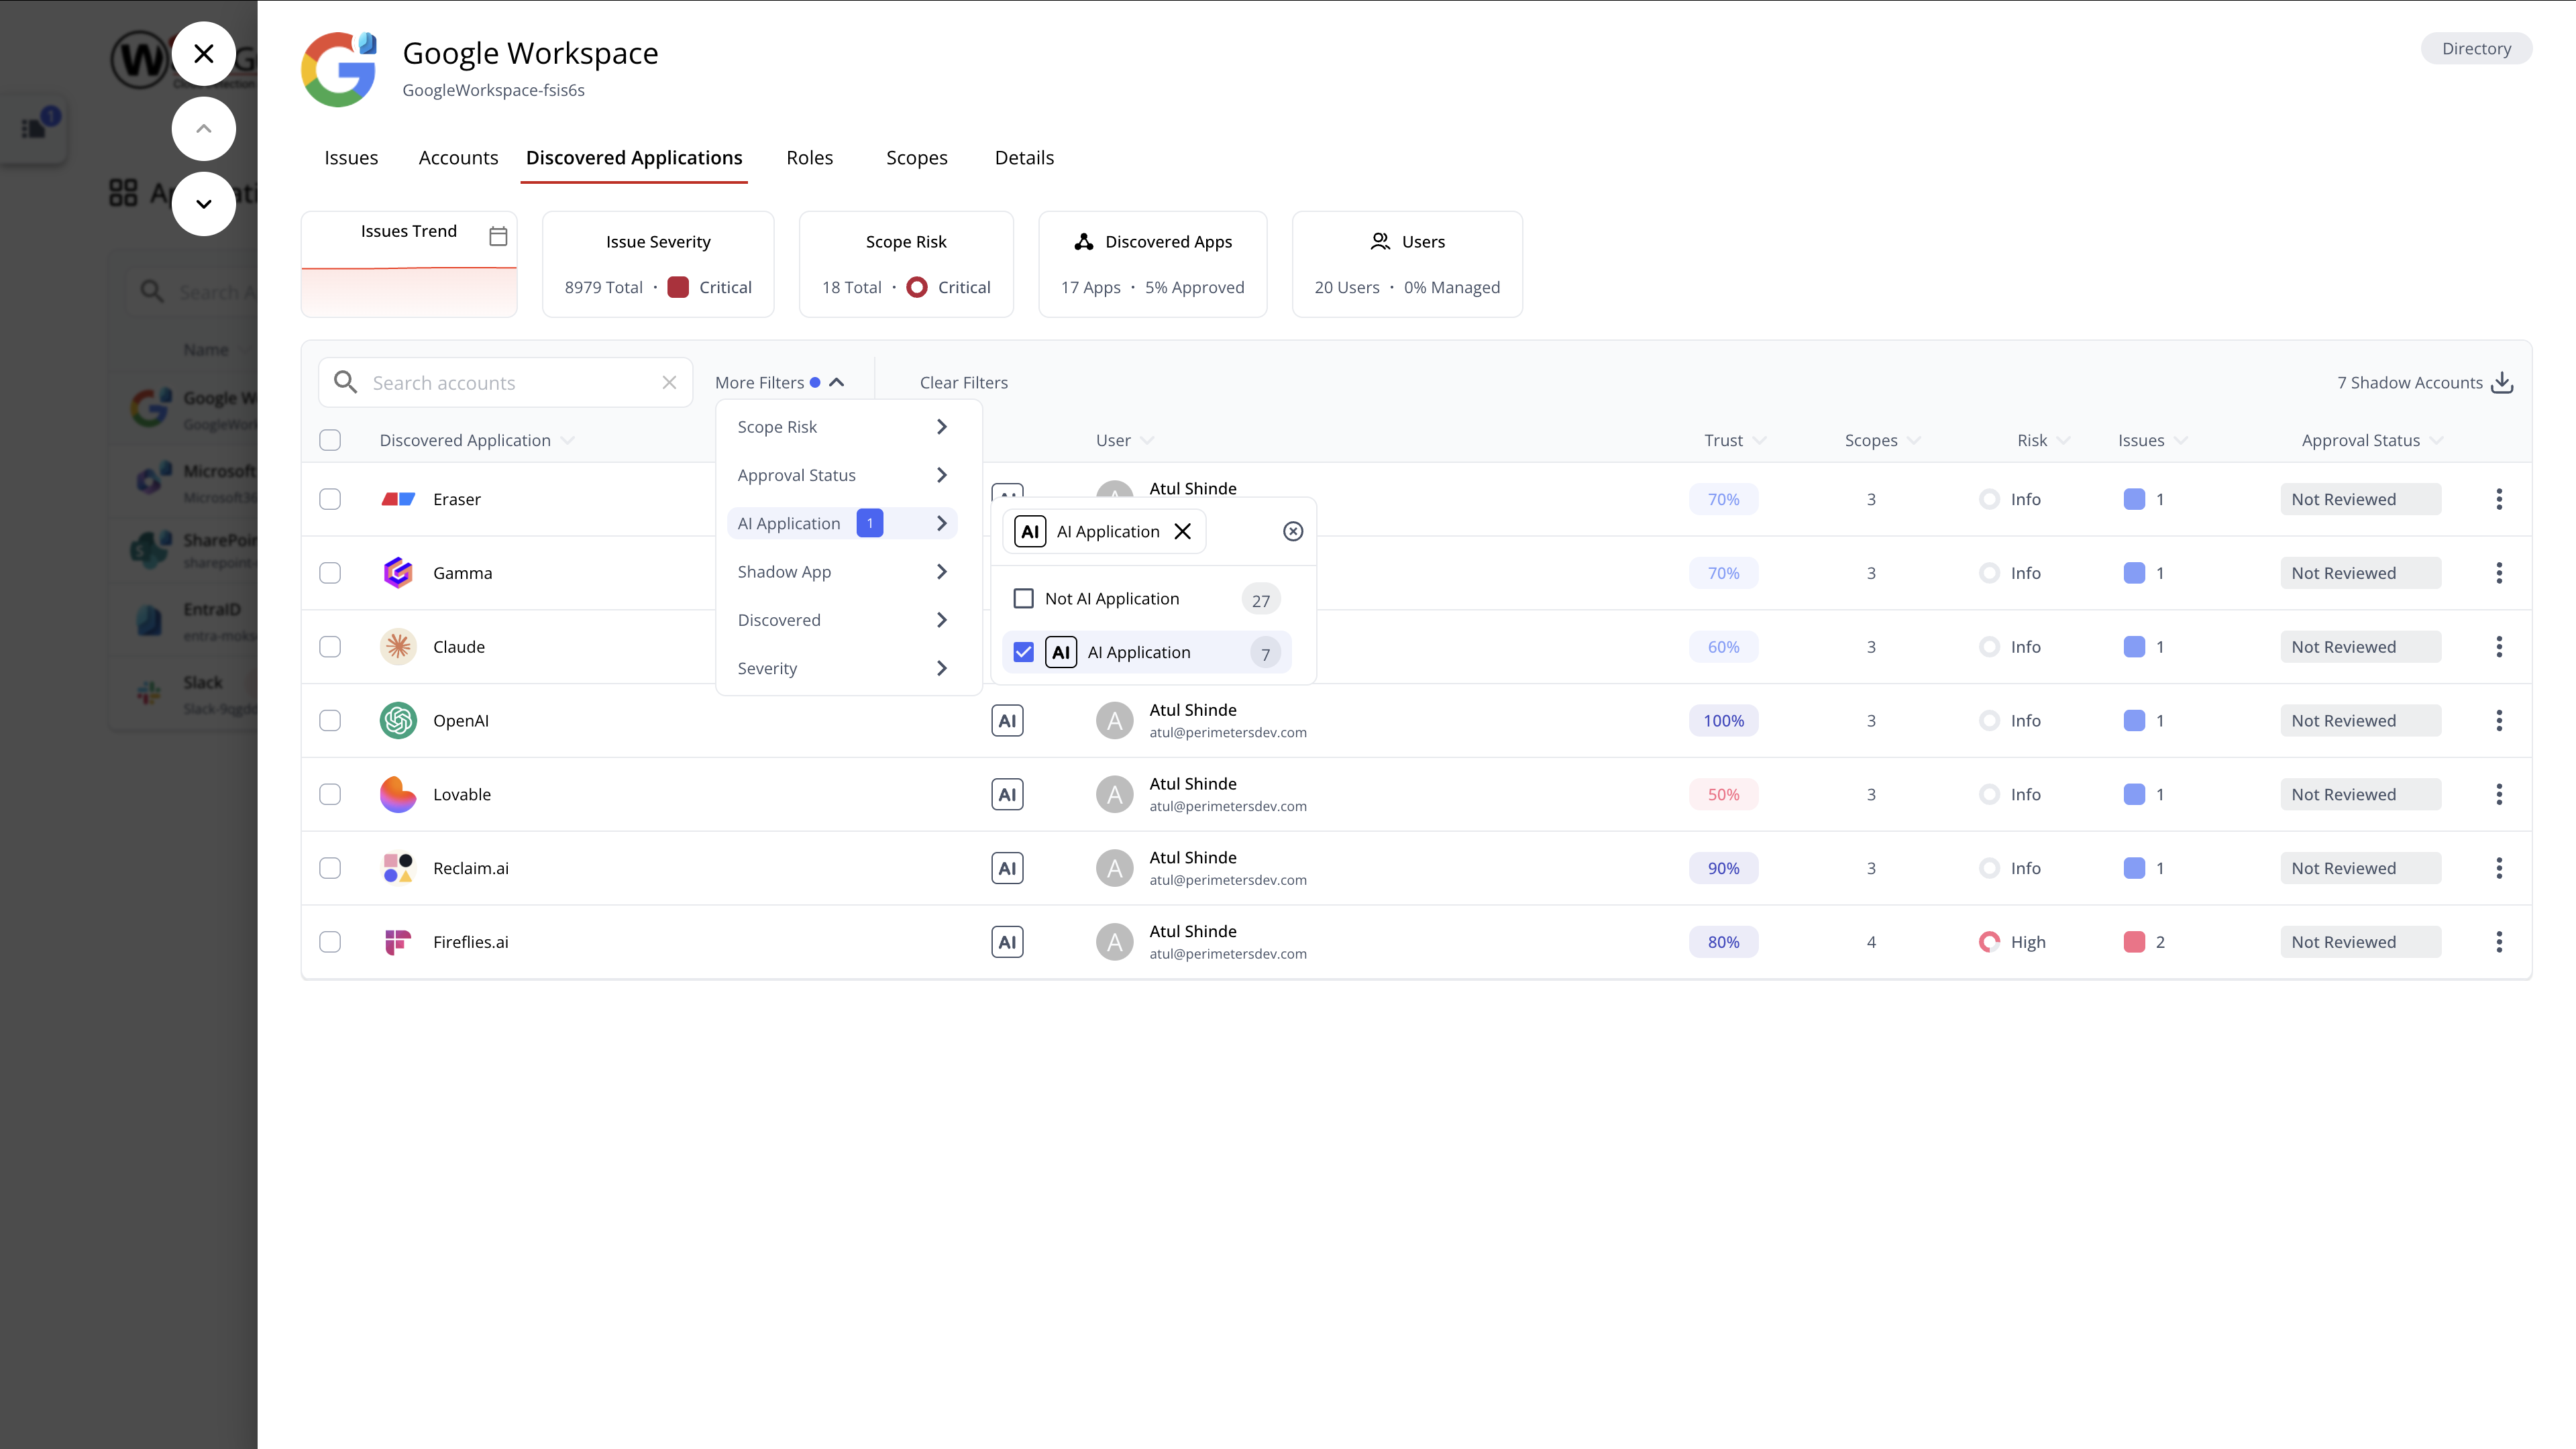
1 / 6
Screenshot of Shadow IT Dashboard
Technical Details
| Deployment Types | SaaS |
|---|---|
| Mobile Application | No |
| Supported Countries | Global |
| Supported Languages | English |
FAQs
What is WatchGuard Cloud Detection & Response?
WatchGuard Cloud Detection & Response (CloudDR) is a cloud security service designed for managed service providers (MSPs) that protect customer environments. The service monitors software-as-a-service (SaaS) applications and cloud accounts for configuration weaknesses, unapproved applications, risky integrations, and identity-based threats.
What are WatchGuard Cloud Detection & Response's top competitors?
Augmentt, Huntress, and SaaS Alerts are common alternatives for WatchGuard Cloud Detection & Response.