Cisco Secure Endpoint is a comprehensive, cloud-managed endpoint security solution designed to protect devices from advanced malware and cyber threats throughout the entire attack lifecycle—before, during, and after an attack. It offers powerful prevention capabilities to identify and stop threats before they compromise your systems, using multifaceted techniques including risk-based vulnerability management and posture assessments. The solution provides deep visibility and advanced detection…
N/A
Microsoft Defender for Endpoint
Score8.8 out of 10
N/A
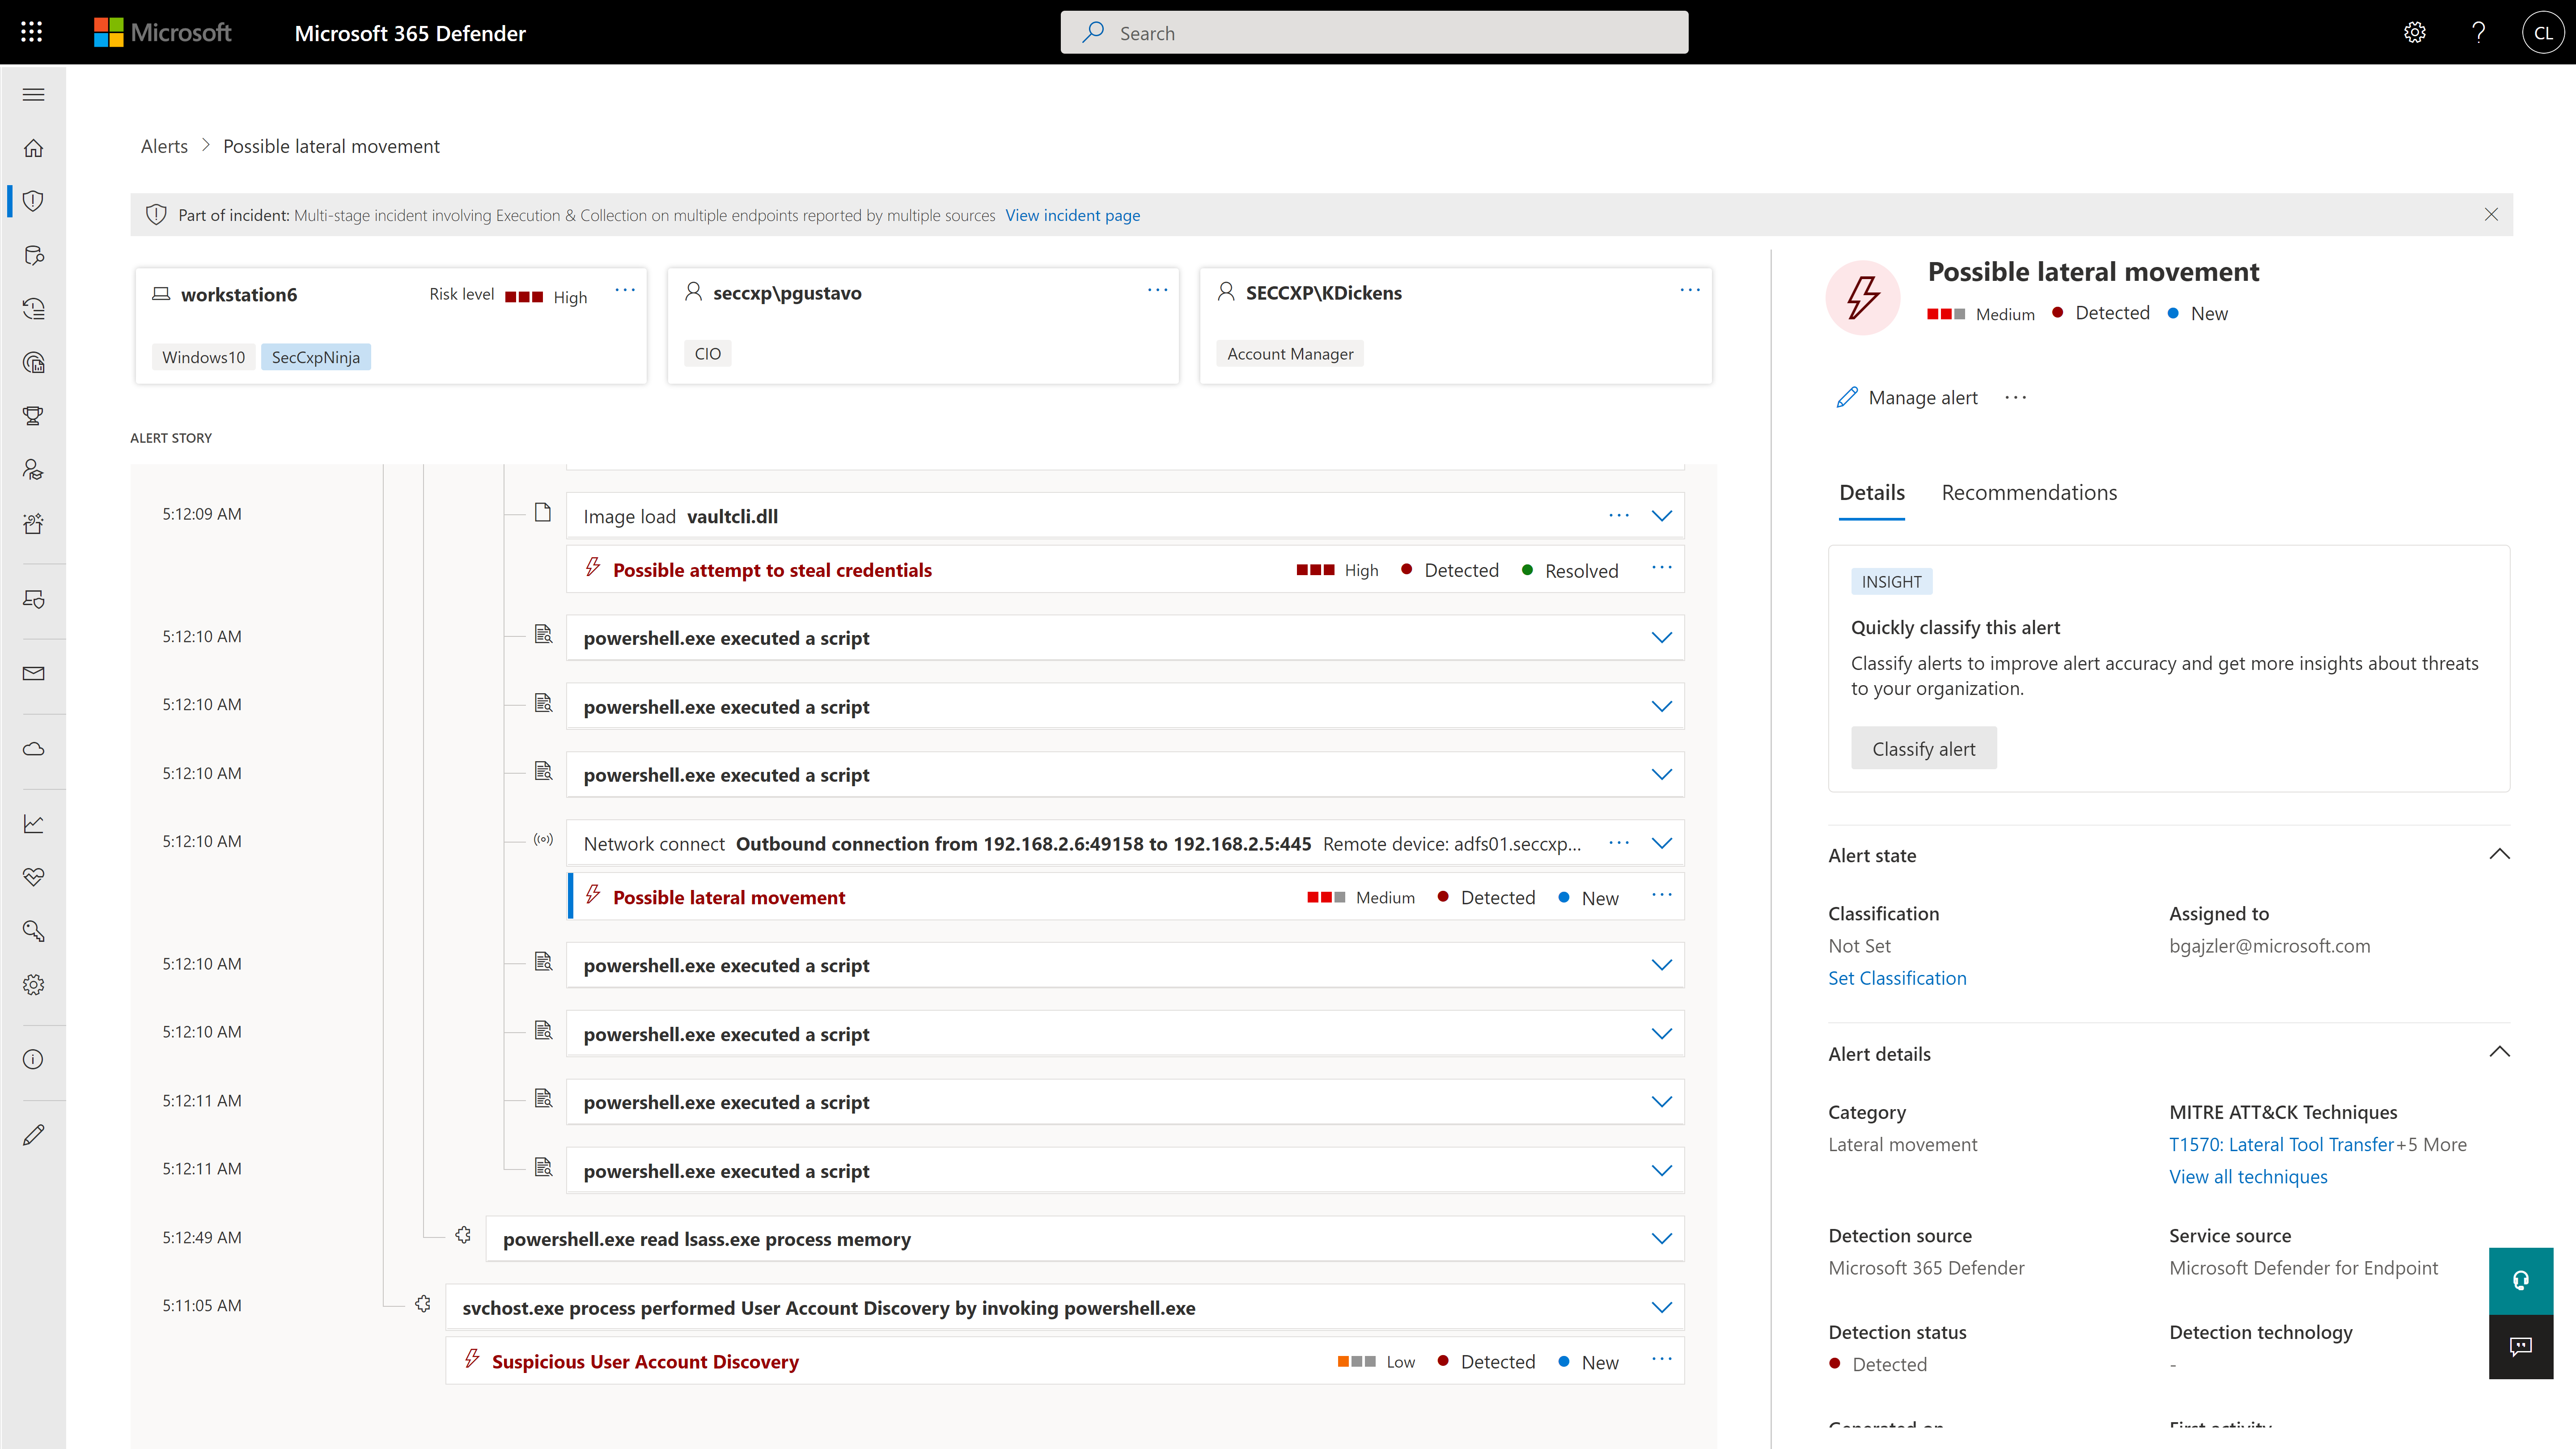
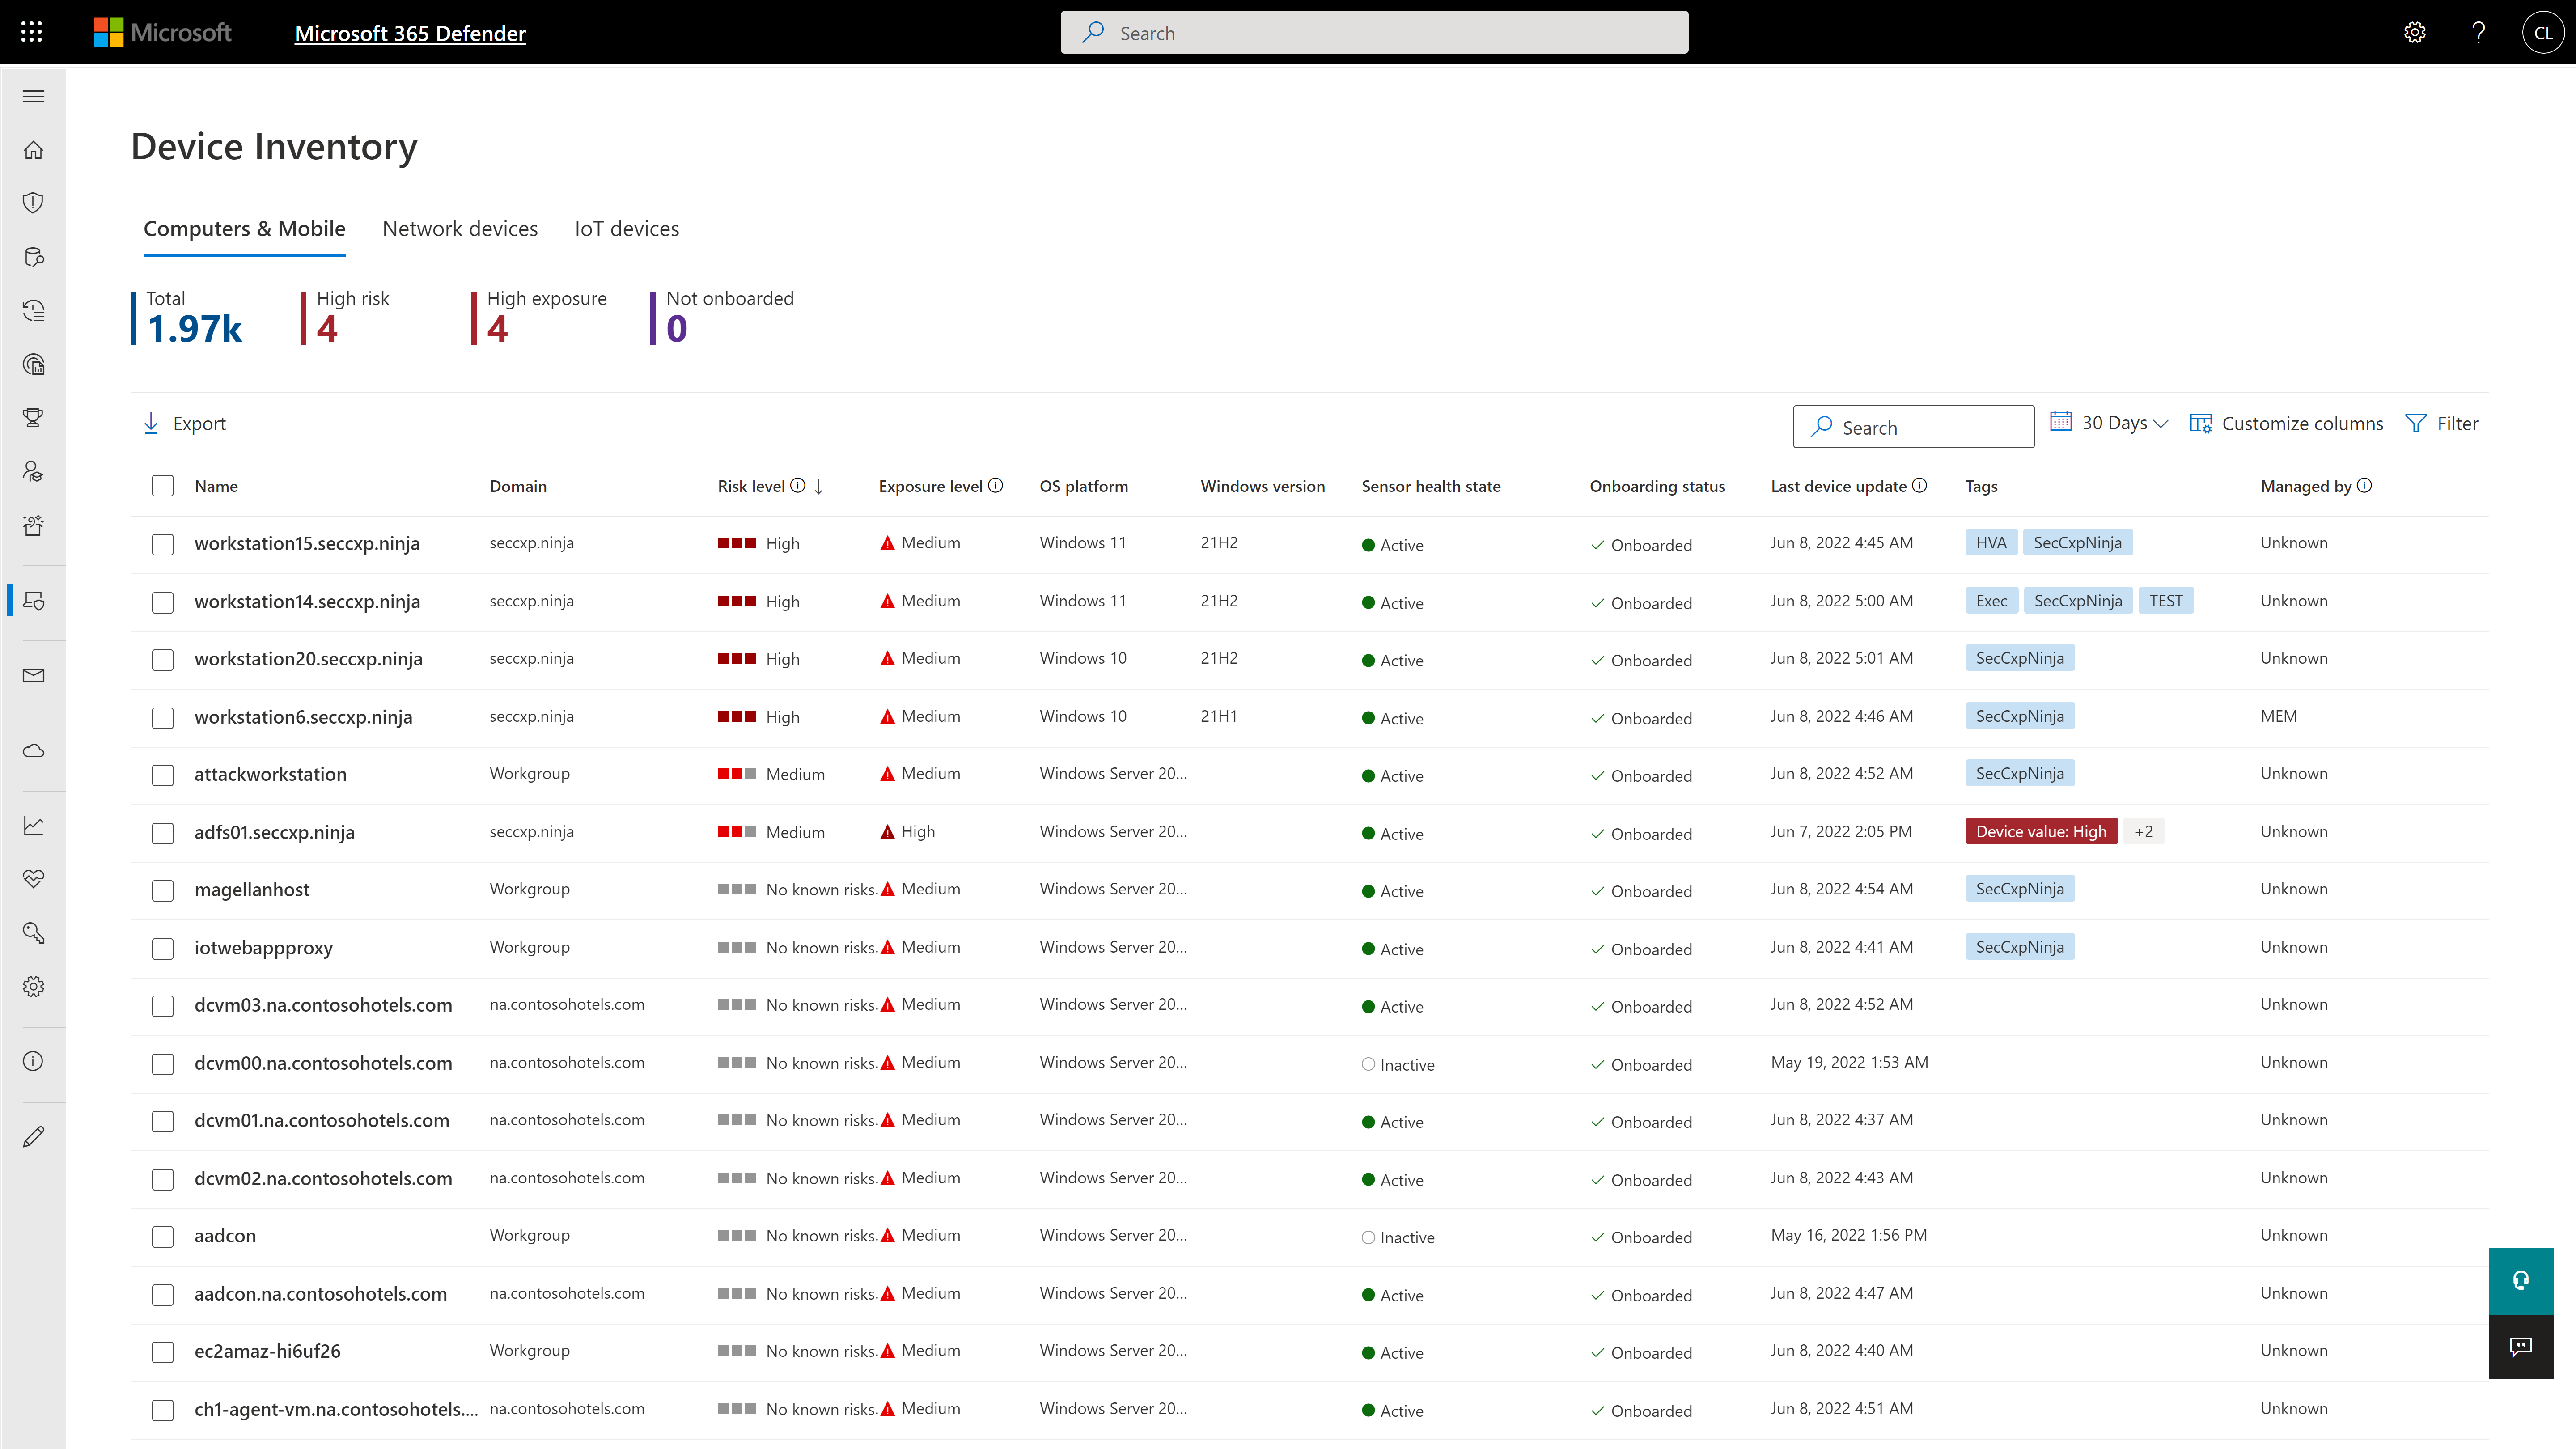
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
WatchGuard Endpoint Security
Score8.7 out of 10
N/A
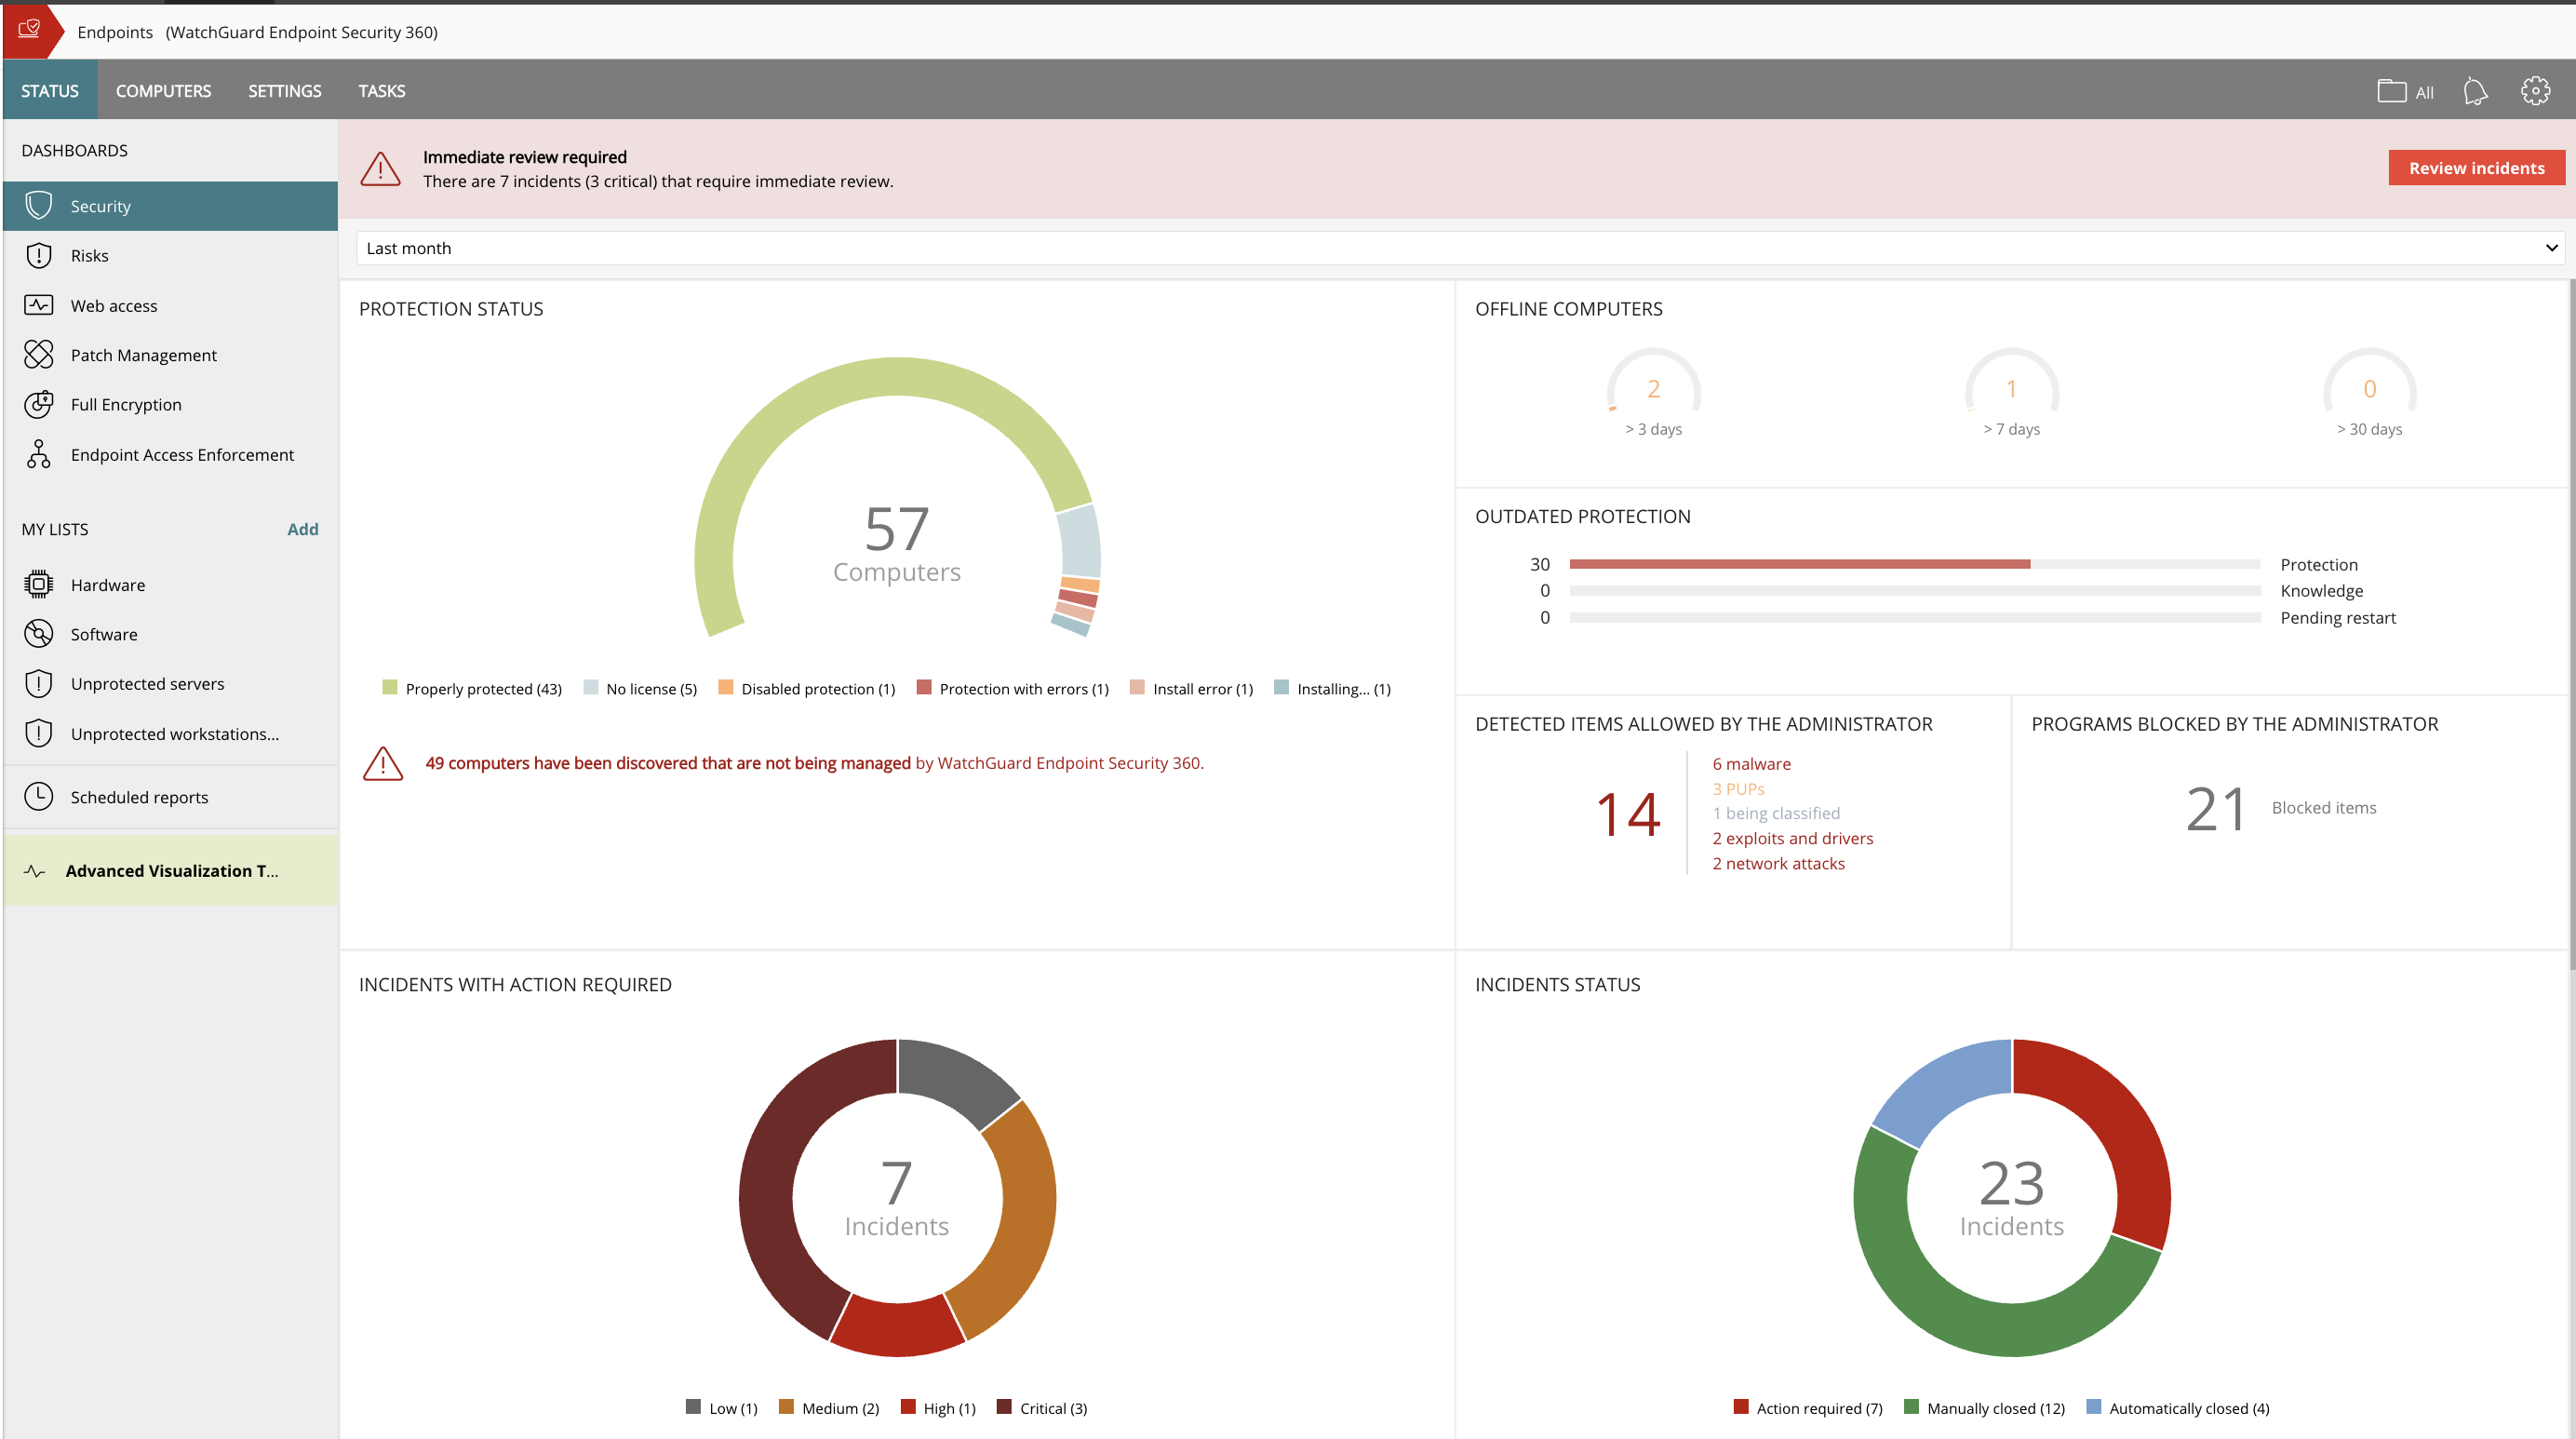
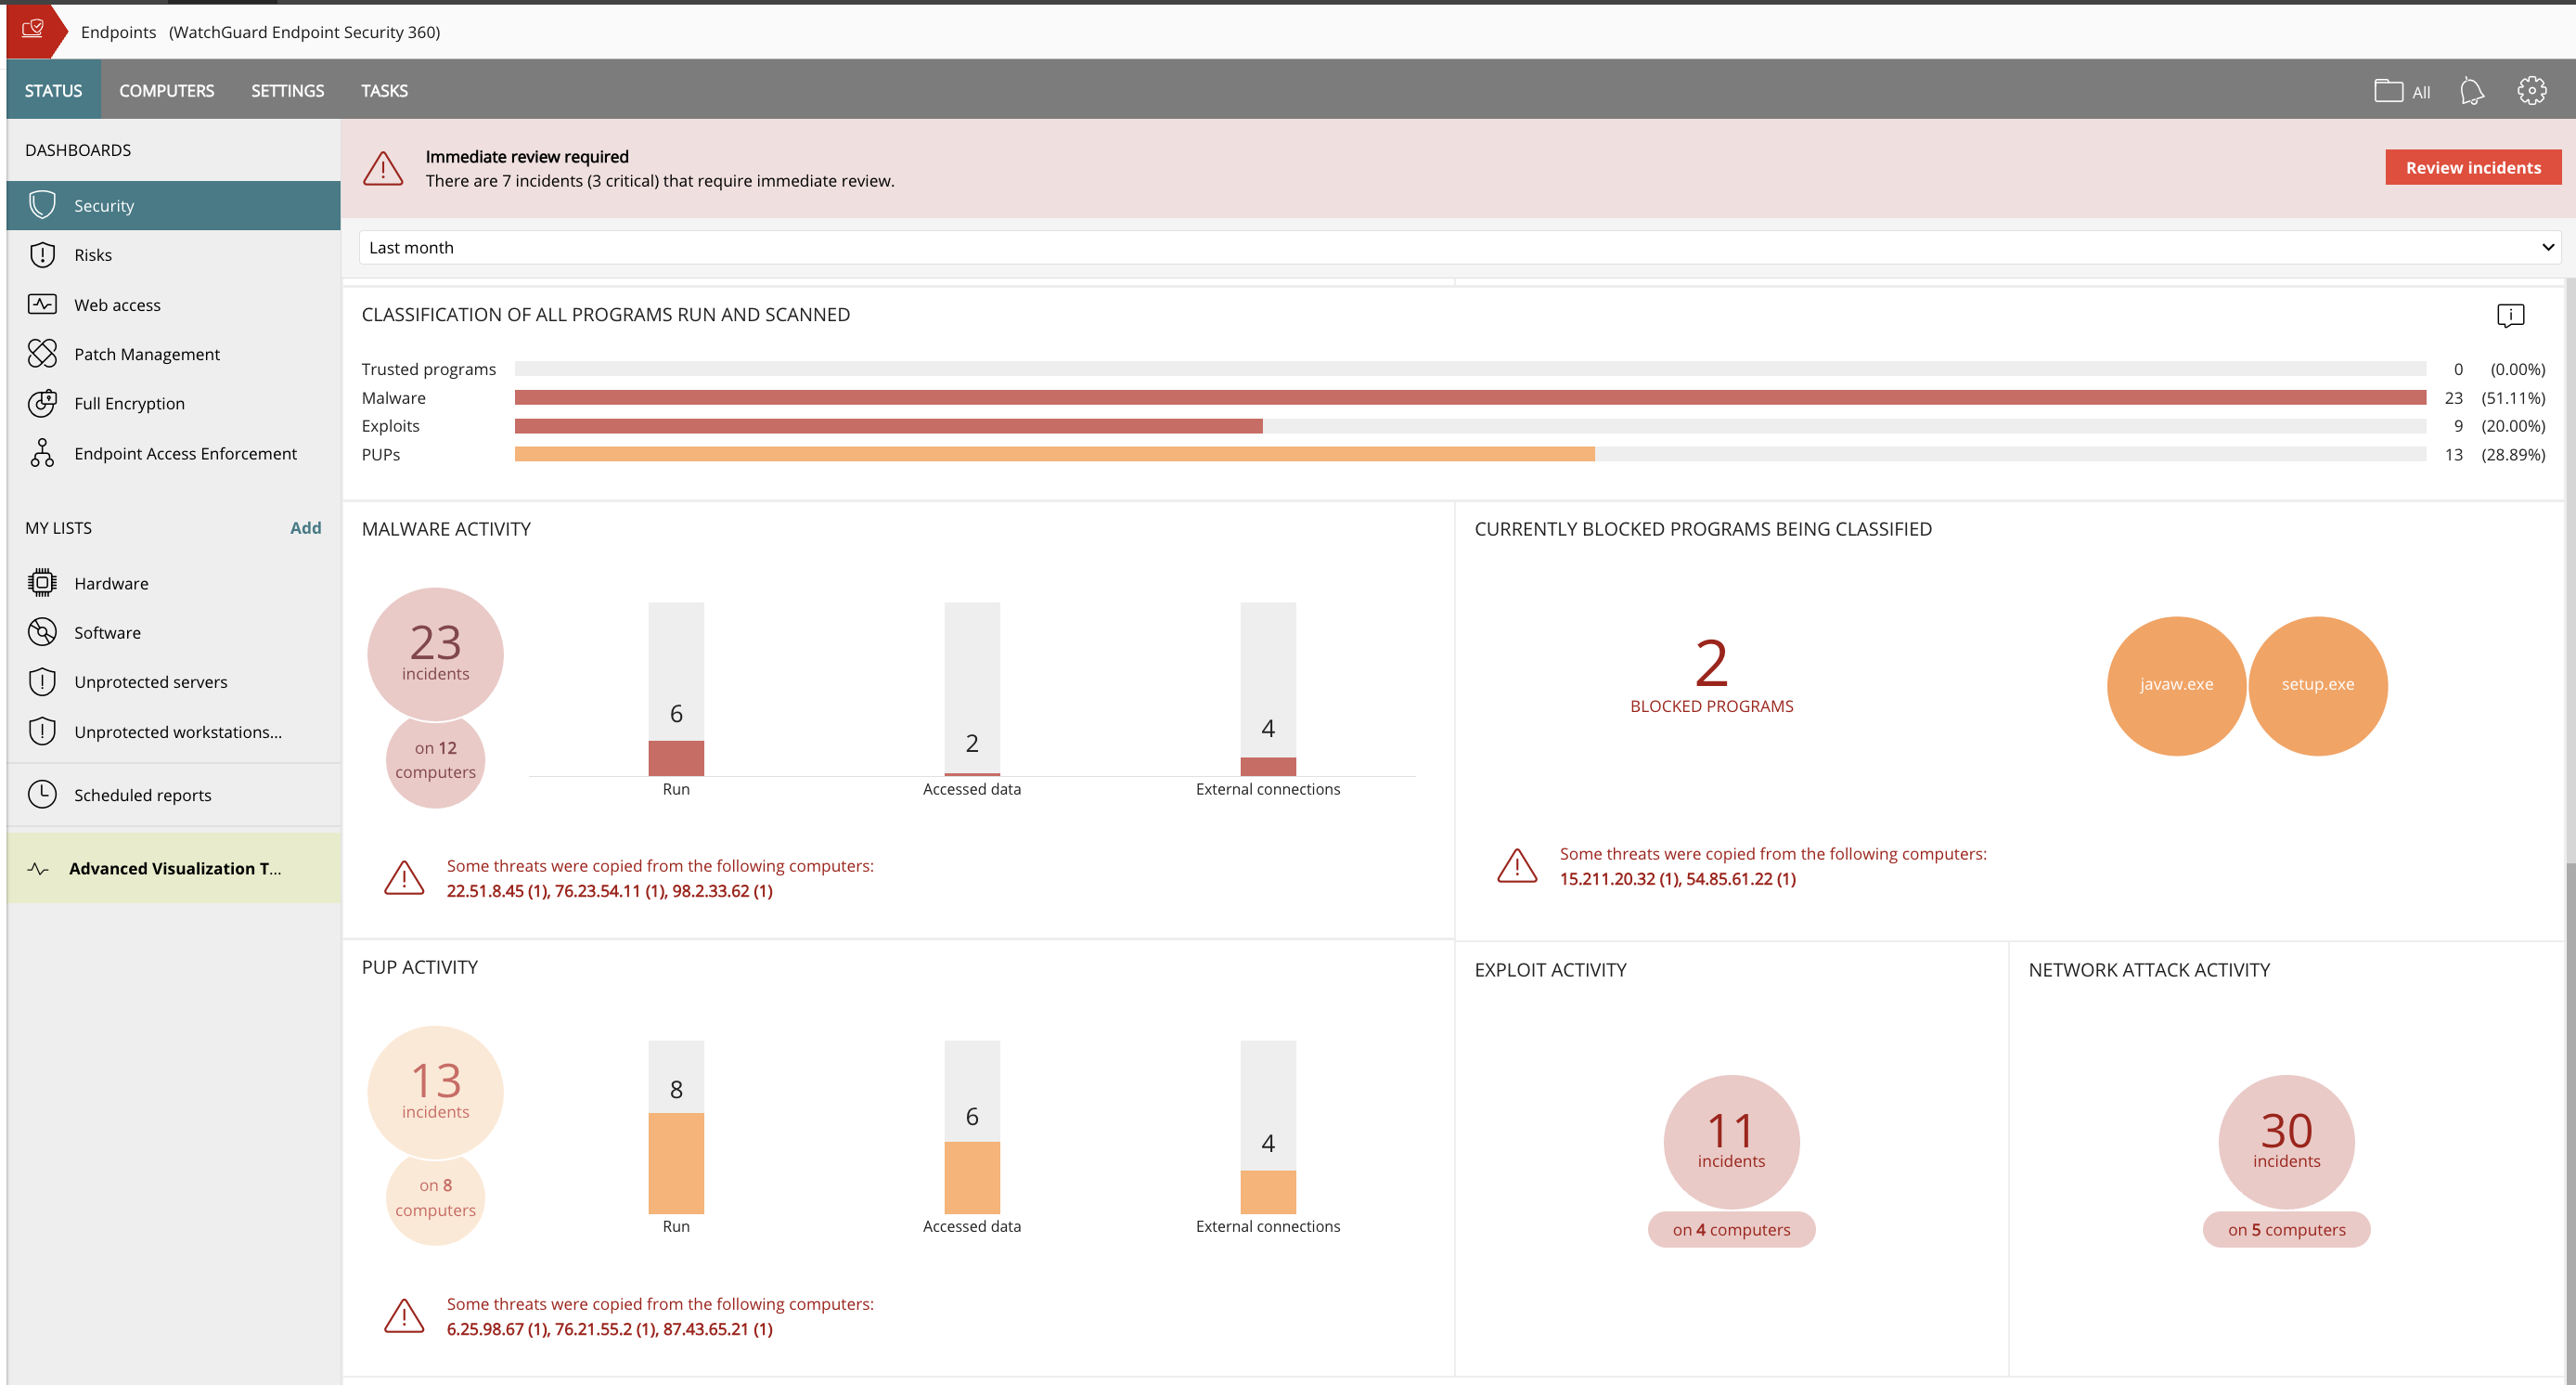
WatchGuard EPDR (formerly Panda Adaptive Defense 360) combines next-generation antivirus protection, endpoint detection and response (EDR), patch management, content filtering, email security, full disk encryption, and more, into one package. The platform touts a unique zero-trust security service that certifies the legitimacy and safety of all running applications thanks to a combination of automated, AI-driven processes and investigation services provided by a team of malware analysts.
Cisco Secure Endpoint provides better overall support and detection compared to other products used. Strong visibility and a strong range of tools when researching an issue to find either information or resolution. Dashboards are also a lot cleaner than most products and easier …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Cisco Secure Endpoint
I was not part of the selection process but know this was purchased on a suite of tools. We get so much more from MDE, CSE doesn’t compare.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
IT Security Manager in Information Technology at RS&H Inc. (Design, 1001-5000 employees)
Chose Cisco Secure Endpoint
Cisco Secure Endpoint is an advanced EDR solution that is highly effective and scalable. Our experience previously with MalwareBytes and Microsoft Defender was not horrible, but these products were not as effective and did not integrate well with our other security products to …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Microsoft
Verified User
Chose Microsoft Defender for Endpoint
CrowdStrike Falcon, and Sentinel One are other big ones that we use a bit. Cisco Secure Endpoint we've evaluated as well. Cisco Secure Endpoint capability-wise doesn't match up to Defender, SentinelOne, and CrowdStrike both do, but the cost profiles are a bit higher. So most of …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint consistently showed better user experiences during scans due to the reduced amount of resources used on each system compared to our previous endpoint protection solutions. However, the main reason we chose Microsoft Defender for Endpoint is …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint offers strong integration with Microsoft 365 and Azure services, which provide a unified security experience. While McAfee Trellix is known for solid antivirus, Microsoft Defender excels in integration in the ecosystem.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint has the best integration for us in our (mostly) Windows environment. Also we are using M365 E3 so this already included Microsoft Defender for Endpoint P1. The extra cost for Defender for Endpoint P2 is definitely worth it. You need to see these …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Panda Adaptive Defense, in combination with Panda Systems Management, was a pretty big and powerful suite of AV software. However, the AV is pretty traditional, all things considered. ATP will always have a slight advantage due to its ability to seamlessly integrate with the …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Owner in Information Technology at AZXnetworks (Computer Networking, 51-200 employees)
Chose WatchGuard Endpoint Security
We used Kaspersky for all of our clients for many years. It was a good platform, but Panda Adaptive Defense works better and is easier to manage. Adaptive Defense 360 classifies the network environment first and will only allow trusted applications in the future upon review and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose WatchGuard Endpoint Security
It is more usable for companies which are not in Cloud, it is easier to manage, integration for different departments are better
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
CEO in Corporate at Gratopp.it (Information Technology & Services, 1-10 employees)
Chose WatchGuard Endpoint Security
For a long time, the centralized administration and the pool licenses were our intention to use [Adaptive Defense 360 / WatchGuard EPDR]. At the moment, the blocking against unknown programs and whitelisting of common programs are the main parts to use [Adaptive Defense 360 / …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose WatchGuard Endpoint Security
The other software that we've been testing doesn't have the complete stop of execution of unknown software.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
To handle modern cyber threats such as malware, ransomware, and other known and unknown threats, Cisco Secure Endpoint is a handy option because it is EDR-capable, always updated, and effectively hunts for threats and blocks them before they cause harm to the business. It is reliable, and I recommend it because it has always protected our business from cyber threats.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
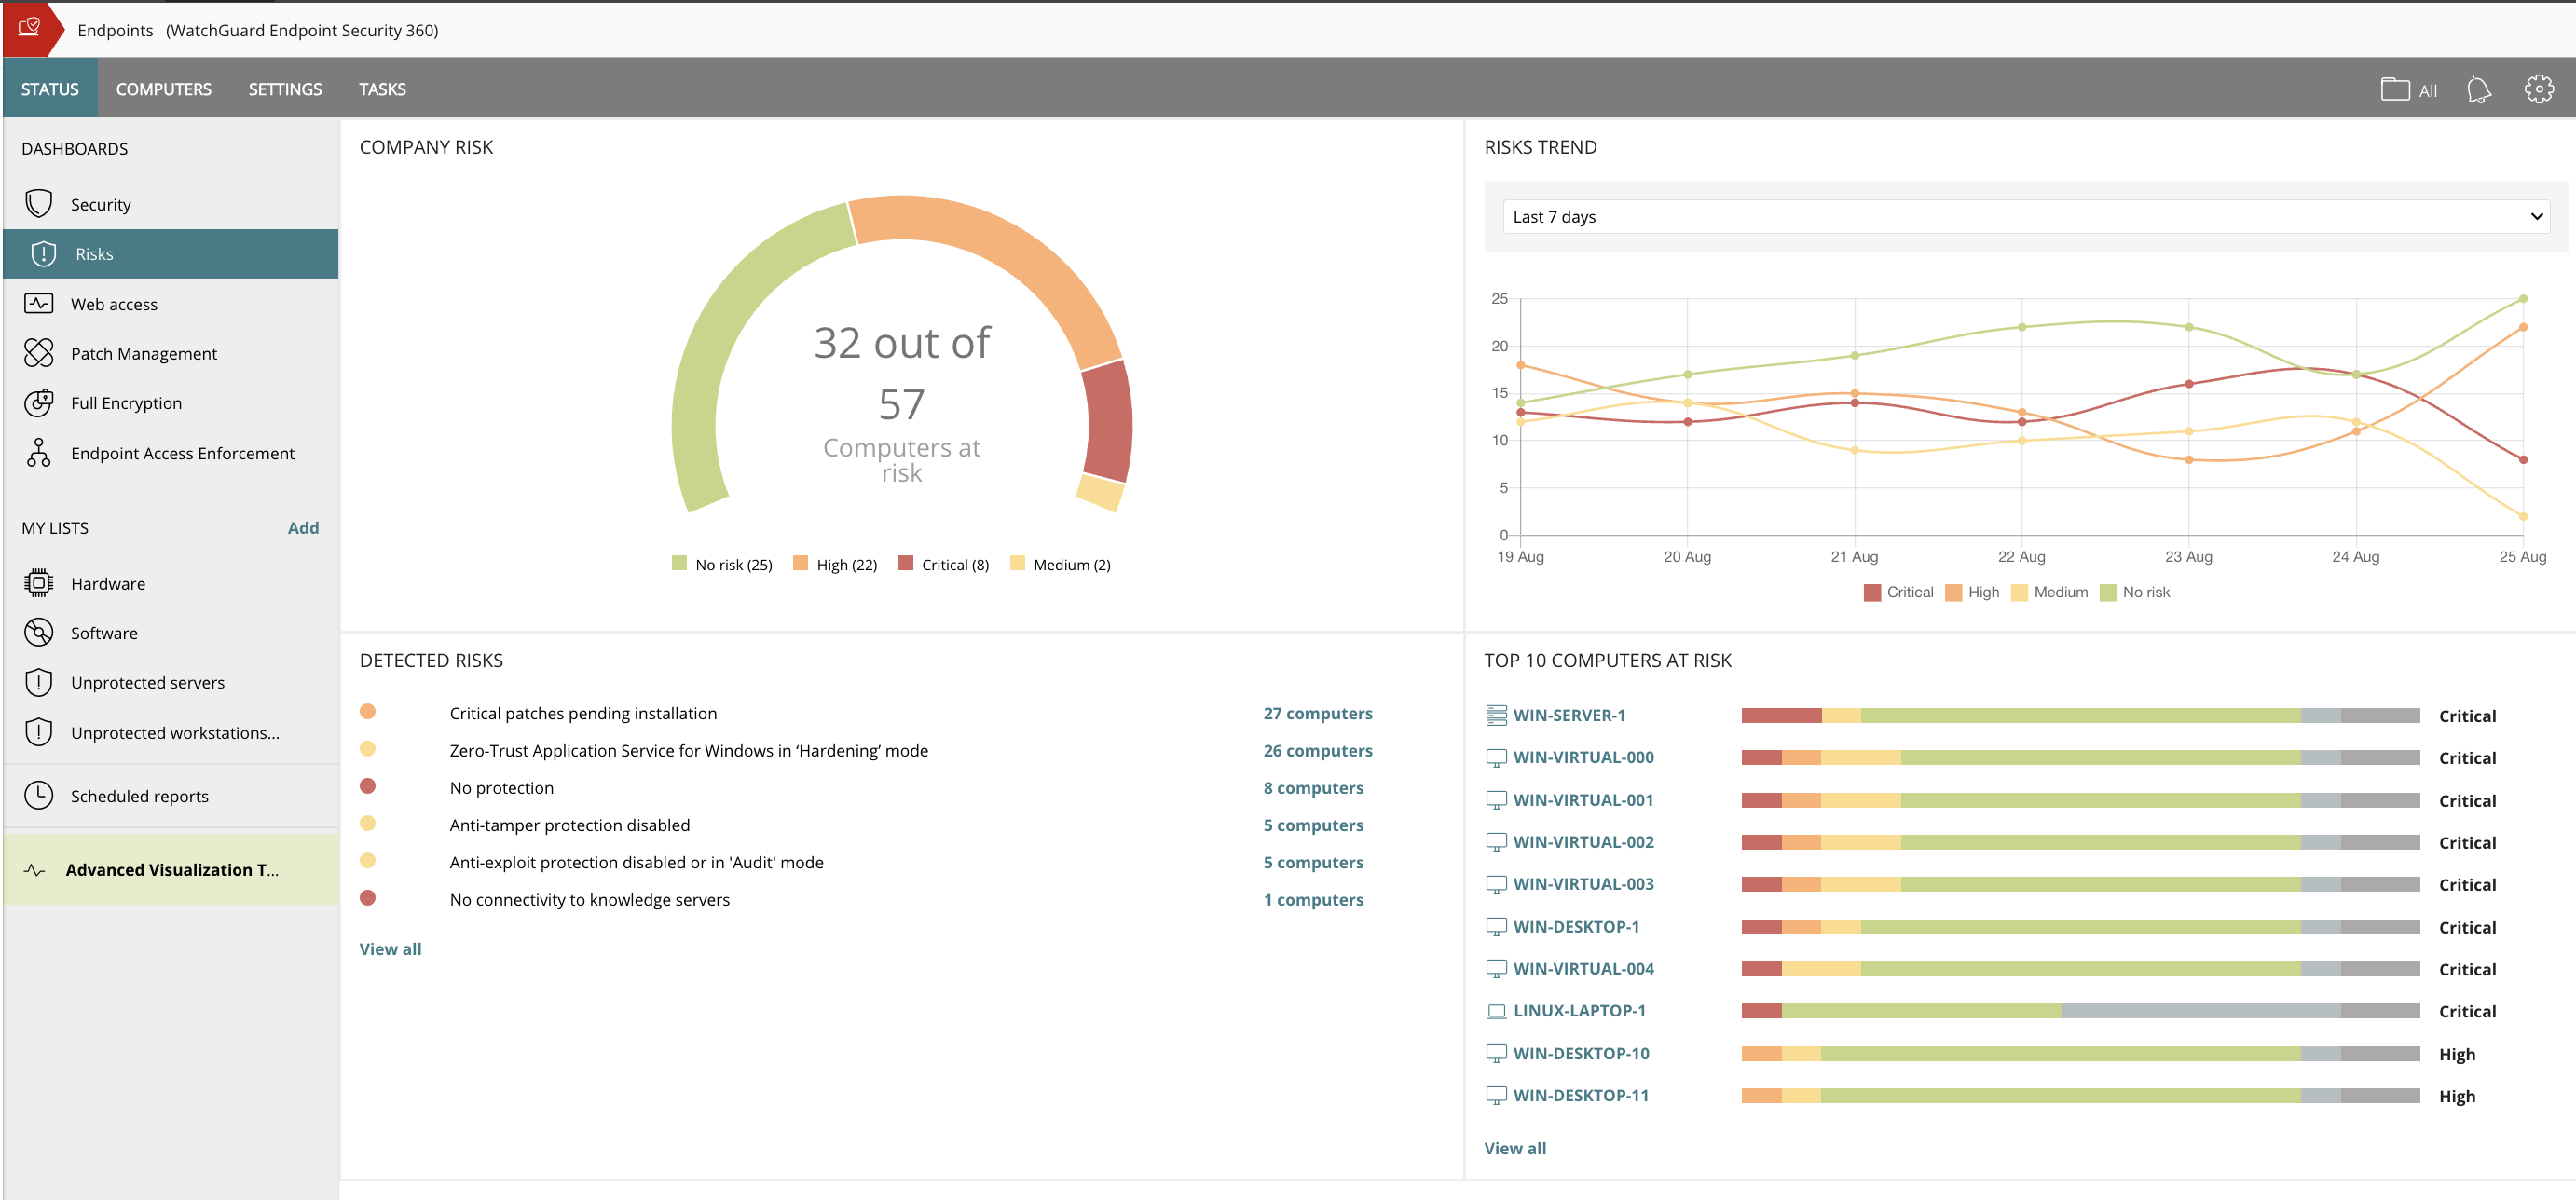
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I would recommend Watchguard Endpoint Security to organizations that are already using WatchGuard Firebox with the Total Security suite or those looking for an additional layer of endpoint protection. The bundled licensing provides strong value and makes it easy to extend protection from the network level to the endpoint. In our case, we primarily use it as a supplement to SentinelOne, and it integrates well in that role. The agent has been stable, the cloud management is straightforward, and it has not caused operational issues in our environment. For businesses that want added visibility and layered security alongside their primary endpoint solution, Watchguard Endpoint Security is a solid option.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Once we, I guess one turned out that path because we have a small IT team, one of the big factors that came into play is how easy it was to deploy and the kind of security it provides for your endpoint devices. For us, it's got all those AI capabilities that really help. So traditionally when there was an incident on Alert on an antivirus program, you'd have a couple of guys run across the office to try to pull a plug. One of the awesome features with Secure Endpoint is its isolation mode that clamps down endpoint devices and then just isolate it. It's connected to, I think Cisco's tell us the threat intel environment. So they've got up-to-date metrics and fixes on threats out in the wild. And once they detect that, they apply it across your whole brand. So yeah, really effective for us.
One of the things that really stands out is the retrospective detections. So say something's detected two weeks later of a product that you had on your system. Initially it scanned it past, but then they discover vulnerability. The product has the ability to come back and retrospectively apply restrictions on specific applications you have on your environment. So I think that's one key winner.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Some of the reports that get sent are very high-end reports with lots of information. It would be nice if there was a simplified report that could be sent automatically when an issue is identified on a computer
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
EndPoint has an optional feature for automatic and remote software updates on endpoints, a handy option for keeping computers up-to-date and secure. However, it is not used to install new software but only to update it. We believe that this part is instrumental, but it is somewhat incomplete.
Another drawback is that some complementary functions to the antivirus, such as the one above, are optional and require a separate subscription.
The implementation of EndPoint requires some planning, especially the time required to harden and learn the system. This is not critical and is typical for this type of system, but it is necessary to plan it well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The ease of use, pricing, support, reliability, and quality of the product. Panda / WatchGuard products are highly rated, priced right and easy to maintain. All of this make it very easy to renew and purchase new licenses for us and our clients.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The interface is extremely difficult to navigate, even for a moderately familiar user. All the dashboards look the same, but have different functionalities. It looks like the place where you performed that task last time, but in fact the option you want is on a different dashboard. The menu is hard to navigate because the menu items are labeled with misleading descriptions or jargon specific to the product. This makes it even harder to find what you need. On the other hand, it does most of what you need it to do automatically, which helps the usability dramatically.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Easy and intuitive MSP management portal to manage all of your clients from a single pane of glass. Policies can be pushed down globally or individually based on needs. The client portal allows access to their tenant information and installs only which is nice if you are working with clients who might have an internal person or an IT team that also wants access to things to manage themself.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The software is 100% managed on a cloud platform that can be managed via an account even if they are not present within the company network where the software is installed, I even always opened the control panel on the browser of my smartphone to monitor the situation.I have never experienced any abnormal software crashes
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The only annoyance I complain, if we want to be picky, is the fact of the constant disconnections from the control panel.Every about 4 hours the account logs out even if I set the "remember this device" flag; having said that I have not noticed neither slowdowns nor conflicts with other software
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
In terms of technical support for Cisco Secure Endpoint, the support has been pretty good. All the cases I submitted were solved in a reasonable time frame, and it was a good experience. However, I find that not as many vendors have the expertise I would expect.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I gave it a 10 because I compare it to air conditioning. I need it to work every day, 24/7. I need it to be reliable and not something that requires a ton of interaction from staff to make sure it works every day. In addition, I should be able to run other things at my house when the AC is on. Panda fits that description.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The training was very helpful. It demonstrated how to configure the service for initial install, items to monitor, and how to set up for ongoing protection. Hands on training is more helpful but this is a good starting point
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Implementation shouldn't present any problems in standard office environments. In environments with development teams, however, caution is needed. If zero trust is enabled, mechanisms must be in place to ensure that internal software isn't classified as a false positive (software certificate, exception folder, etc.)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco Secure Endpoint is an advanced EDR solution that is highly effective and scalable. Our experience previously with MalwareBytes and Microsoft Defender was not horrible, but these products were not as effective and did not integrate well with our other security products to allow us to monitor and react quickly to address threats that were within our network. Key to any security effort is mitigation and the ability to quickly identify and respond so any damage can be avoided or limited.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We didn't spend much time looking into Symantec - but it was the software of choice for the district before I joined. That said, we were pretty easily talked into Watchguard Endpoint Security as we were already in the Watchguard world of products. Moving to their EDR just seemed to make sense for our organization
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
With the implementation of watchguard (at the beginning Panda Endpoint, but it is the same) I was able to insert in the control panel all the unauthorized software previously installed by colleagues without any authorization from the various department heads.Now any licensed software goes into lockdown and can be unlocked from the control panel
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
By committing to go all in on Watchguard Advanced EPDR across our whole client base, we maximized our price position - enabling us to offer the best endpoint security at a price better than what lesser competitive products cost.
Leveraging Watchguard Endpoint Security as part of our unified platform strategy provides better integrated security, managed through Watchguard's cloud architecture. This significantly reduces our cost to deploy, manage, and support our client's. Our improved security offering, better delivery, and stronger price position has helped us achieve 56% growth in our managed services business over the past 18-months.
Organizations that have disparate cyber security products often require specialists for each solution in their stack. Watchguard provides outstanding training resources that equip our entire technical staff - significantly improving our service delivery while lowering our overall cost of business.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info