Cisco now offers OpenDNS Umbrella Web Filtering. Cisco acquired OpenDNS in August 2015, and rebranded the product as Cisco Umbrella.
N/A
Malwarebytes
Score8.8 out of 10
N/A
Malwarebytes is a antimalware application for home and small businesses, which blocks viruses, malware, hackers, viruses, and malicious websites.
$119.99
per year 3 devices
Sophos Intercept X
Score8.9 out of 10
N/A
Sophos Endpoint Protection (Sophos EPP) with Intercept X is an endpoint security product providing an antivirus / antimalware solution that when upgraded with Intercept X or Intercept X Advanced provides advanced threat detection and EDR capabilities.
$28
per year per user
Pricing
Cisco Umbrella
Malwarebytes
Sophos Intercept X
Editions & Modules
No answers on this topic
Teams - Sole proprietor
$119.99
per year 3 devices
Teams - Boutique business
$399.99
per year 10 devices
Teams - Small office
$799.99
per year 20 devices
Intercept X Advanced
$28
per year per user
Intercept X Advanced with XDR
$48
per year per user
Sophos Managed Threat Response
$79
per year per user
Offerings
Pricing Offerings
Cisco Umbrella
Malwarebytes
Sophos Intercept X
Free Trial
Yes
No
No
Free/Freemium Version
Yes
No
No
Premium Consulting/Integration Services
Yes
No
No
Entry-level Setup Fee
No setup fee
No setup fee
No setup fee
Additional Details
—
All plans include a 60-day money back guarantee. 1st year discount available for the Small office plan.
Pricing is for a 3-year commitment. Government and Education pricing available.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Director Of Information Technology in Information Technology at Alicart Restaurant Group (Food & Beverages, 201-500 employees)
Chose Malwarebytes
I found Sophos to be more resource intensive, scans take longer and affect the end user experience more. Building policies and customizations is not as intuitive with Sophos.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Information Technology and Web Support Specialist in Information Technology at Tax Executives Institute (Non-Profit Organization Management, 11-50 employees)
Chose Malwarebytes
We found Malwarebytes to be much easier to use than Kaspersky. I also think that Malwarebytes is better supported and has a better reputation for protecting its clients. We found the interface of Malwarebytes to be more intuitive. We also liked the central server software to …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Chief Information Officer in Information Technology at Pikes Peak Library District (Libraries, 201-500 employees)
Chose Malwarebytes
Malwarebytes was in place prior to my hire. Malwarebytes has successfully protected the Information Technology (IT) infrastructure in the two years I have led the IT department. There is no desire to replace Malewarebytes at this time. Other vendors have contacted us, but their …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Senior Associate in Information Technology at Stir Architecture (Architecture & Planning, 11-50 employees)
Chose Malwarebytes
When compared to Microsoft built-in Windows Defender, Malwarebytes edges it out because it's in the business of detecting malware and not working with the operating system. Malwarebytes is constantly updating its definition files to make sure all potential worms are caught …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Senior Web Developer in Engineering at WebpageFX (Information Technology and Services, 51-200 employees)
Chose Malwarebytes
Malwarebytes has an effective free version (some of the others do, some don't). Malwarebytes has a slightly different focus on the type of malware it looks for. As opposed to picking one winner, I would suggest selecting a well-reviewed paid AV, and possibly supplementing …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Systems Support Engineer in Information Technology at College of William & Mary (Higher Education, 1001-5000 employees)
Chose Sophos Intercept X
I preferred the management console of Malwarebytes Endpoint Protection and the deployment capabilities of both were very similar. However, it was not my decision to make on which product to implement. I was only a tester of the product and reported back my preferences. …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Sophos Intercept X
Sophos Intercept X is one of the industry leaders for a reason. Apart from integration issues, Sophos Intercept X stands above the rest when it comes to protection and usability. I have used at least 30 different antiviruses, antimalware, and antiransomeware programs and none …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
IT Specialist in Information Technology at Zoom Drain (Consumer Services, 51-200 employees)
Chose Sophos Intercept X
Sophos Intercept X is easy to manage and deploy under your business. I think it is comparable to BitDefend with the ability to send out deployment via email or directly add it to the computer. I have noticed that Bitdefender seems to eat a lot of resources during its scans …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Sophos Intercept X
Trend Micro offered similar protection, however at the time did not offer EDR as a solution. The big benefit to Trend Micro was the capability to push out the installation of the agent to assets within the Trend Micro console, eliminating the need for a GPO or deployment …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Information Technology and Web Support Specialist in Information Technology at Tax Executives Institute (Non-Profit Organization Management, 11-50 employees)
Chose Sophos Intercept X
We used to use Symantec Endpoint Protection. At the time we were using it (it may very well be different by now), it required a bit more maintenance and we were constantly having issues with definitions not being downloaded as well as issues updating the software itself. We …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Sophos Intercept X
We were looking at both 4 years ago before we chose Sophos. We picked Sophos because of the full breadth of the products they offer and how involved they are with the security community. The product is a stable and reliable software that protects us well from advanced threats
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
IT Support Specialist in Information Technology at Loenbro (Construction, 501-1000 employees)
Chose Sophos Intercept X
Sophos's shields are more powerful than both McAfee's and Symantec's while using less system resources doing its active scans. It does use more power while performing a manual scan than either, but nothing that cripples the system or leaves it unusable while it is running. The …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Systems Engineer in Information Technology at NativeX (Marketing and Advertising, 51-200 employees)
Chose Sophos Intercept X
I did not have an influence on the purchase of Sophos. However, from past experience with other antivirus products, Sophos doesn't seem to bog down the systems. It scans the second a file is touched, and is great at quarantining harmful files before they can become a problem. …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
When a company has a distributed workforce, the produce works very well to unify a set of policies to apply against web bound traffic. Areas we have struggled with is getting value out of our cloud delivered firewall due to requirements to fully use it
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Now, I gave it that rating because it's a handy tool for diagnosing issues. Quarantining them, and most of the time, it does fix the problem. Though with rootkits, it's been hit or miss, and sometimes perfectly valid software gets flagged erroneously. However, once you've run it, it tends to run continuously, consuming far too many resources and being a real pain to uninstall, sometimes even causing issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
To be frank, this product is fairly expensive. So I would recommend this to companies that are mid-sized or larger to condone the cost of the purchase. It does save me a significant amount of time in my day - being able to glance at the dashboard and see if there are any outstanding issues that require my attention, as not much digging must be done to accomplish this. So for our company, with a short-staffed IT department, it's incredibly helpful to us. We also qualify for Educational pricing which brings the cost down - which helps tremendously
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
As many companies think—they’re afraid of firewalls, but they want to keep something secure—and what it does best is it simplifies the approach from a cybersecurity perspective, especially from the user perspective. Users spend a lot of time on the web, trying to access sites, clicking links, scanning QR codes, and doing whatever. You can’t really stop them unless you have something in between that can check whether those links lead somewhere safe, or potentially run them in a sandbox if there are threats or specific use cases.
So I think one of its strongest points is that it’s very simple, and it’s not expensive compared to if you buy a firewall and licenses from other brands, where you have to configure it and spend engineer work hours or outsource the work. It’s the simplicity, and I think it just works. I had some issues five years ago, four years ago, but now it just works. I’m pretty happy.
Low system resources, it does not slow down the whole computer when scanning or when real-time protection is enabled
Quick and frequent updates, usually people hate updating, but for malware/viruses, you want to be updated as possible. It takes less than 15 seconds and usually does it automatically. They usually send a few updates a day as they find more.
Protection features actually work when visiting known bad websites. The page will be blocked and nothing will be downloaded. It may not be what the user wants, but it's what the user needs (as the user can't know every bad website)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sophos Intercept X is great at preventing malware infections and rolling back their effects. I have seen this happen hundreds of times since we installed it
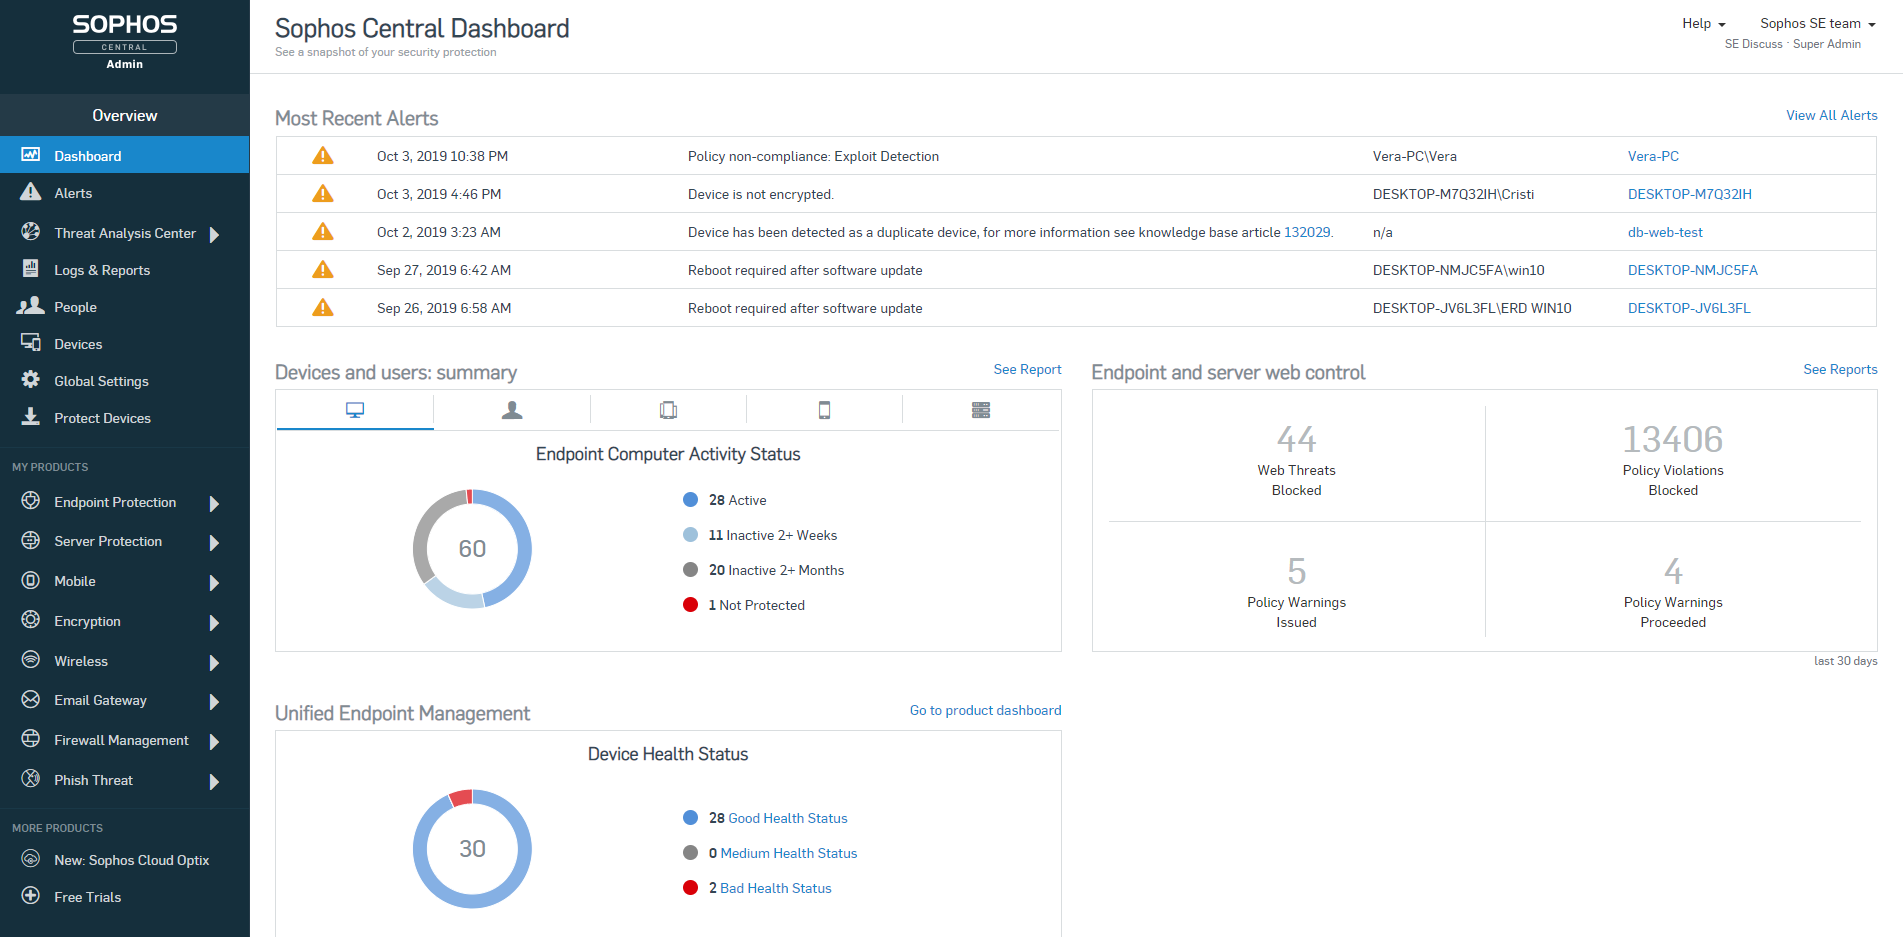
When combined with Sophos Central, you have an easy to use dashboard where you can manage all installations from a single pane of glass.
It's easy to deploy on machines and stays updated.
Good reporting features including alerts sent to the admin if there's ever something wrong with it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
So we had in the past very general rule sets, very detailed rule sets for security rules. Like you can access this page but not this IP range and so on. So hundreds of specific rules for specific machines and the rule management in Cisco Umbrella is not that granular. So it was not possible to build up these rule sets in Cisco Umbrella, but now we see to access it's much better already. So that's why one reason why we are migrating to CQ access to have better API based possibility to manage these rule sets and synchronize them between different products that we are using and in the cloud. So yeah, we hope that with secure access it's a little bit more granular like with Cisco Umbrella currently.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One of the main things that malwarebytes is missing as a company, is phone support for its clients. All support questions has to go thru email only. This is not acceptable for issues that needs to be resolved quickly.
There is an issue when installing the client on a machine, it has a set amount of time where the software can register with the management server. The issue with this is, with machines that are over a wide area network, slow connection speeds can cause the software not to register. When that happens, it never re attempts to register in the future.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sophos OOTB policies are very strict and they don't offer anything less strict without you creating new custom policies. I'm sure this is deliberate because the product starts you out in the safest way possible but it means that you will have lots of calls to your tech support desk when you first deploy it unless you do somewhat extensive testing beforehand.
Sophos Intercept X is currently broken (at least the DLP component) by having secure boot turned on in the UEFI/BIOS. If any user wants to be able to write data to a USB drive or floppy from their PC (yes we still have a couple users who need to use floppies) we have to turn off secure boot on their PC, even if the DLP policy for that user/PC combination specifies that the user and PC are allowed to write to USB/floppy. This would be a very serious problem if it weren't for the fact that we have very few users who need to write files to USB. For us it's OK but I bet it would be a deal-breaker for others.
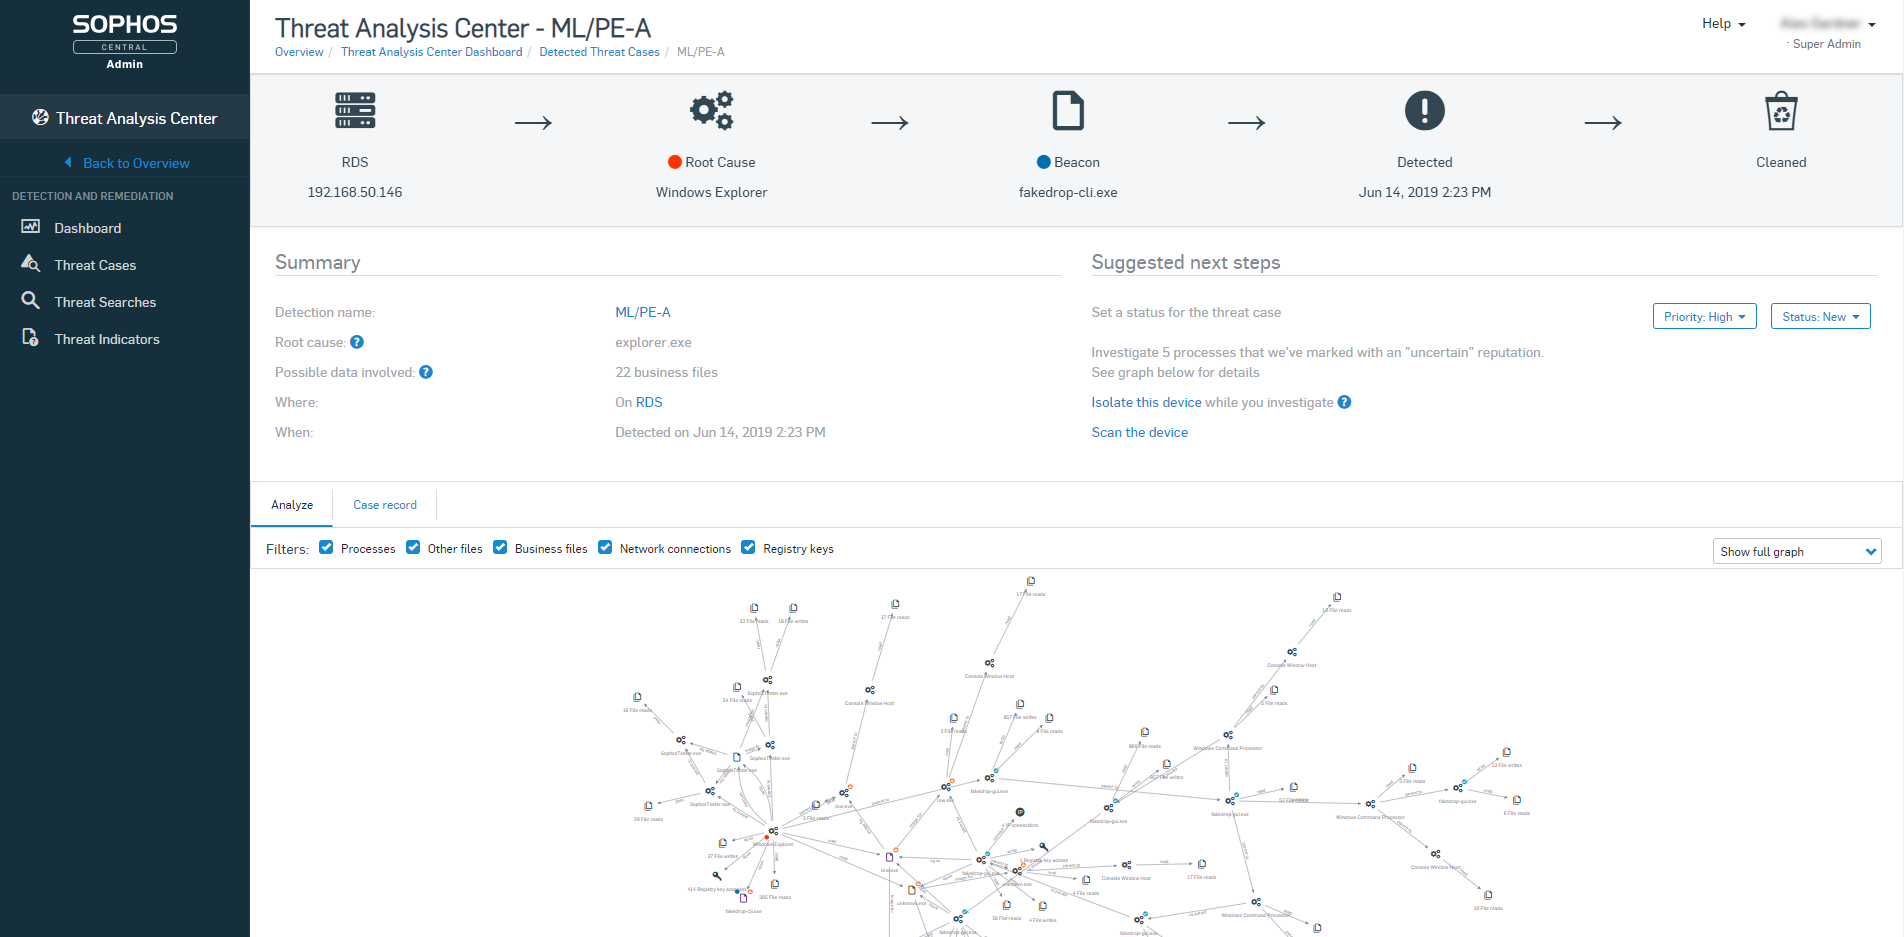
I don't see a whole lot of evidence that Intercept X is any different than any other anti-virus, so maybe their admin alerts just don't clearly identify when they have identified a zero-day threat or maybe we just haven't had any zero-day threats.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
First off I never give anything a "10" unless it's perfect. LOL - I grade on the curve. I think OpenDNS/Umbrella is a very good product. I think that fact that Cisco absorbed them is one of the proofs of that. I have used the product back when it was free for companies our size. I have not always appreciated the cost - but in the post pandemic cyber chaos, I believe the cost benefit ratio is still very high. I have honestly not looked at other products because Umbrella continues to work to my satisfaction. I consider Umbrella to be one of the key layers in my cyber security strategy.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The last time we renewed Malwarebytes, we renewed for a 3 year renewal. That should describe the confidence we have in the product. Plus the cost savings impact year after year.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Better features and easy to manage system with great customer support and overall usability is great as it works for hybrid environment with ease as it is having features for on prem users as wells as cloud users with great customer support and great team of trained engineers to support our opeartions.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Usability-wise, it's pretty good, and it gets the job done. But once that's finished, the nags, the pop-ups, and the fact that it slows older systems down recklessly really cost it rating points. It becomes a clutter, and one of the first things we check when we receive reports that a PC is slow is whether it's running malware. Once we uninstall it, the PC is usually easily 40-50% faster. That's too much in the way of resources for something that wants to always run in the background.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The usability has never been a problem. Sophos Intercept X is a program you can install and let protect your company without much intervention. Apart from a few policies, Sophos will keep you protected better than most any product on the market. Sophos Intercept X works quite well when you are looking to "tighten your grip" on user's access to websites, programs, and add-ons.
Cisco umbrella services in the cloud are always available. However, the weakness is the VM installed in the data center that are the first resolvers. If the VMs become unavailable for any reason or the vSphere goes down, then all DNS is affected
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
our experience with cisco products has always been awesome and same is the case with cisco umbrella .Under umbrella cisco provides flexible and scalable software solution to use across different dept and sites . These softwares are very user friendly ,pages load quickly as these applications are designed for minimum latency and reports are also provided quickely
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Whilst the support is good once you get through to them, it's email only and the response is slow. This is a issue, because its a core system that needs to work. We have had issues in the past where several of our companies have gone down due to Umbrella and support is nowhere to be seen. It is very difficult to know whether Umbrella is having service issues, since they do not regularly update customers on the status of their services, such as is seen by providers such as Microsoft (status.umbrella.com just seems to show up all of the time, I'm not sure it's even updated)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The Malwarebytes customer support team is awesome! They really go above and beyond to help you with whatever issue you may experience. It is not that we need to contact their support team often, but the few times we did, we would speak to someone who knew what they were talking about and able to solve our problem. It is a comfort knowing that aside from a great product, you are getting a reliable support structure.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Most of the support reps are fantastic. There have been a few though that have had to be escalated via Account Manager when they haven't followed up but this is a rare instance, and often followed up by the Support Manager for APAC.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Quite easy to understand training modules prepared by knowledgeable trainers. Training modules have included all the desired features of these softwares and the content delivery is very good from the respective module trainers and it explains in details the features and apart from that further training material support is also provided if needed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
At the time we were forced to move from Cloud Web Security to Cisco Umbrella, Cisco Umbrella was far from being a direct replacement. It was frustrating and difficult to migrate due to the lack of functionality. This has since been addressed, however we now have legacy rulesets that were built as bandaids that cannot be removed. Hopefully the migration to Secure Access will address this.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Umbrella checked all the boxes for us (at the time) because it supported multiple domains and multiple IPs to protect (we have 20+ offices), and its configuration and policies cover a lot of different options for us. We used another product prior, and it worked well, but it didn't have all the features we needed at the time.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Avast and Norton's products were part of the testing for us but the cost was very high for them and the products were not light on the machine. They took up a lot of memory and slowed the computers down. Malwarebytes although may lack some feature, is a very light software.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Webroot Endpoint Protection is not even in the same league as Sophos Intercept-X. I have tested and compared both sides by side, run simulations and it's not even close. Plus the Sophos central management is so much better. Easier to view user activities and apply policies and remediate threats. Sophos is the clear winner between these two products.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cisco umbrella provides fleaxible and scalable software solutions which are easy deploy across multiple departments and sites wherever needed and this softwares are very easy to use and provides the best interface along with cisco support for other devices apart from cisco infrastructure but still there is scope for improvement on the inclusion of latest features
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's a costly product and we have to admit that, but security breaches are costlier, and they can take more than we can afford so we always had positive mindset over our security purchase and Cisco Umbrella had overall positive impact.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive Impact: Have not had to remediate malware/virus infections since installed.
Positive impact: As far as browsing goes, we can boldly go where no man has gone before. No, really, I am confident when I am clicking on search engine results that if something get past my trained eye, Malwarebytes will pick of the slack.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Once our technical and commercial areas got certified, the ROI over the time spent, is great. Actual customers, and/or new ones with other tools, feel safe and advised, once they get in touch with us.
When Sophos EndPoint is being compared against Web Management Tools (competitors), we have failed to deliver, nevertheless, there is a version of Sophos Central (Cloud) which achieves this requirement at 100% and more, since is Cloud Based (on AWS).
We are grateful to be on Sophos "Radar" as a Platinum Partner, and "The Americas" valued partner, we have seen our business grow, thanks to this kind of technology, throughout the years.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info