A solution to operationalize actionable data and insights to secure any organization. Anomali ThreatStream provides curated access to the a global repository of threat intelligence, delivering enrichment, contextualization, and detection of known and emerging threats.
N/A
IntSights Cyber Intelligence, from Rapid7
Score7.7 out of 10
Enterprise companies (1,001+ employees)
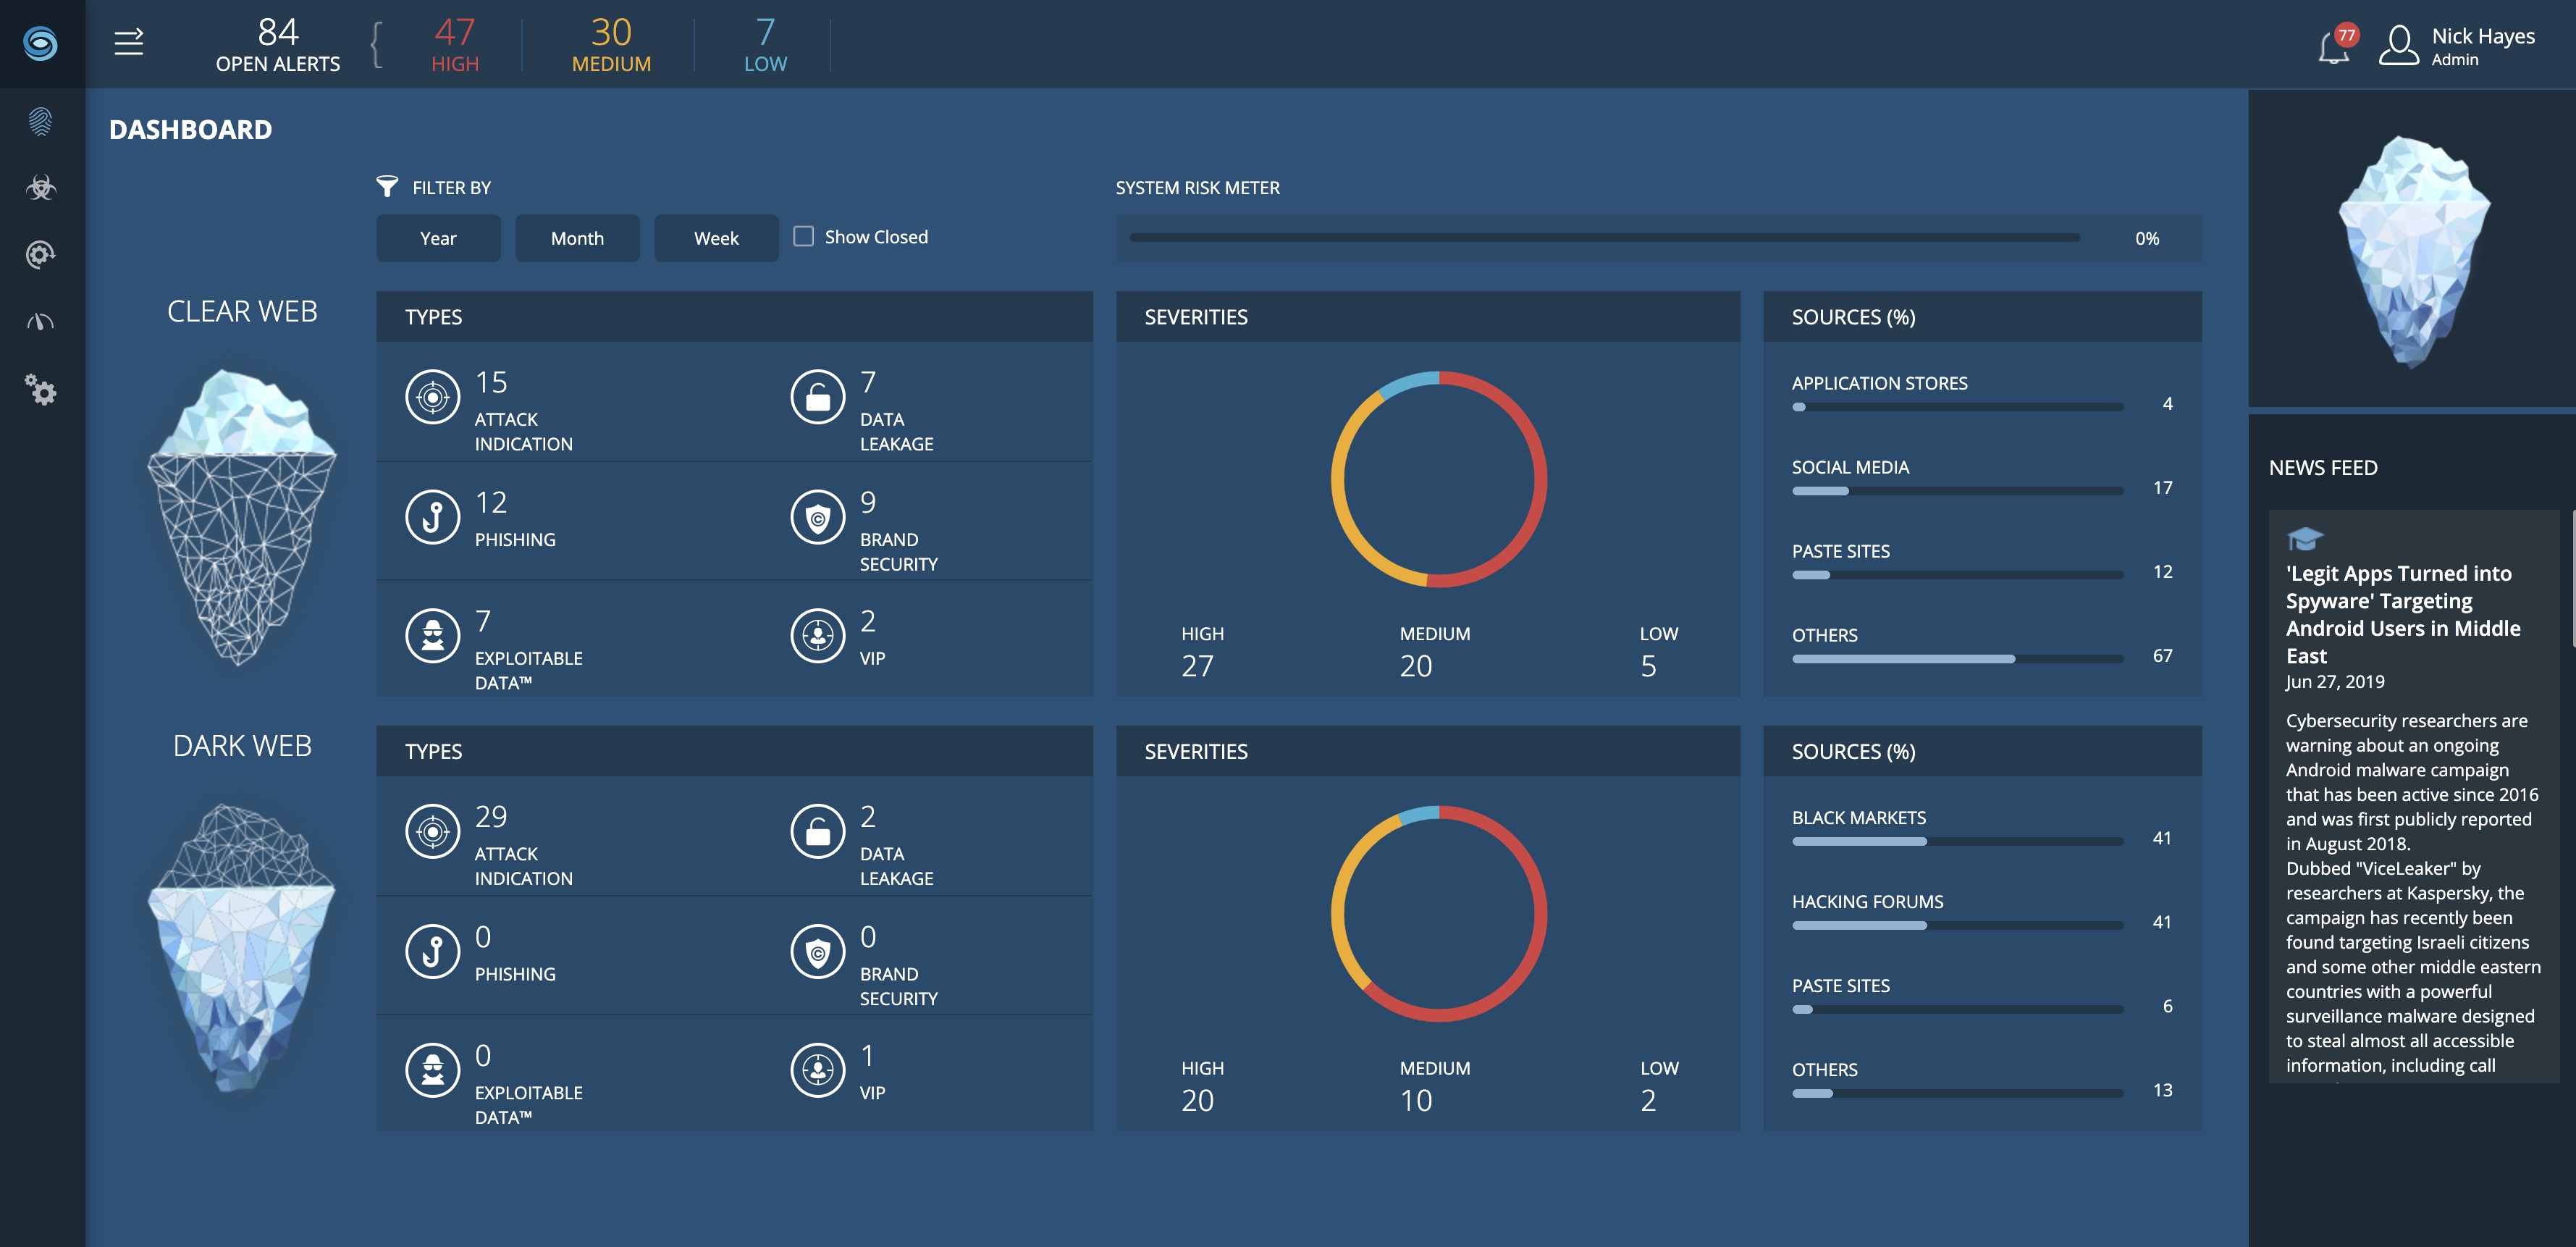
IntSights is an all-in-one external threat intelligence and protection platform, purpose-built to neutralize threats outside the wire. According to the vendor, it is the only solution of its kind. IntSights solution suite's goal is to equip cybersecurity teams worldwide to more effectively detect, assess, and mitigate threats externally from the source, well-before before they reach the perimeter. IntSights four core offerings are: Threat Command™ Threat Intelligence…
Anomali ThreatStream is excellent in scenarios where we deliver Managed Security Services to customers. It offers exhaustive volumes of information in the form of threat bulletins, IOCs, Threat Actor profiling, and details related to campaigns in the wild which can be used to a great extent by MSSPs. For an enterprise SOC, I believe it is a little less suited purely because of the pricing aspect as it is slightly towards the expensive side of the spectrum.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It has been a brilliant tool and we have harnessed it for so many applications - Threat intelligence, Risk Analysis, Automation, Endpoint protection, Vulnerability Management, Application Security, Protecting all our Cloud Applications. We love the fact that we only have to see those threats that are meaningful to us. We don't need clutter and endless dashboards with information that just gets in the way and makes things complicated. By having this full, crisp, easily discernible visibility, our decision-making is enhanced and we can see clearly what's happening in real time. We also love the fact that if a dashboard isn't proving to be productive, then we can go ahead and scrap it, and create another one. The tailor made/bespoke aspect of the Application is the thing that really sets it apart. By having all our dashboards aligned, our teams are all working from the same page and it means we are safe in the knowledge that our systems and applications are being monitored in the most effective and efficient ways. There haven't been any real scenarios where it has been ineffective. - perhaps just In-depth Risk Vulnerability Analytics are a bit lacking. However, I'm probably just picking hairs there.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The user interface, perhaps there is some room for improvement although it is good already.
Confidence assigning process for IOCs needs to be more robust and transparent.
While integration with SIEM solutions is a cakewalk, there is definitely added value if SIGMA rule conversion and YARA rule creation are provided from the platform.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Many of the products that can be used to be ingested into a security event management software can be cumbersome with threat streamThere are many opportunities to continue fine-tuning the environment and providing great context in regards to threat research. When compared to other products threat stream stands out from usability and features.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
IntSights Cyber Intelligence, from Rapid7 was by far the clear winner, in terms of seamless integration with our exisitng systems, deployment, cleaner User Interface, ease of operation, better for monitoring Indicators of compromise and dark web information, having more features etc.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have seen a positive ROI as the security monitoring is taken to the next level when it is augmented with threat intel data that Anomali provides.
Our customers are very satisfied with the periodic threat reports that we send, which are created using Anomali ThreatStream.
The overall business objectives are met as Threat Intel is one of the most important pillars when it comes to providing security services, and we use Anomali ThreatStream extensively for that.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info