Malwarebytes is a antimalware application for home and small businesses, which blocks viruses, malware, hackers, viruses, and malicious websites.
$119.99
per year 3 devices
Microsoft Defender for Endpoint
Score8.8 out of 10
N/A
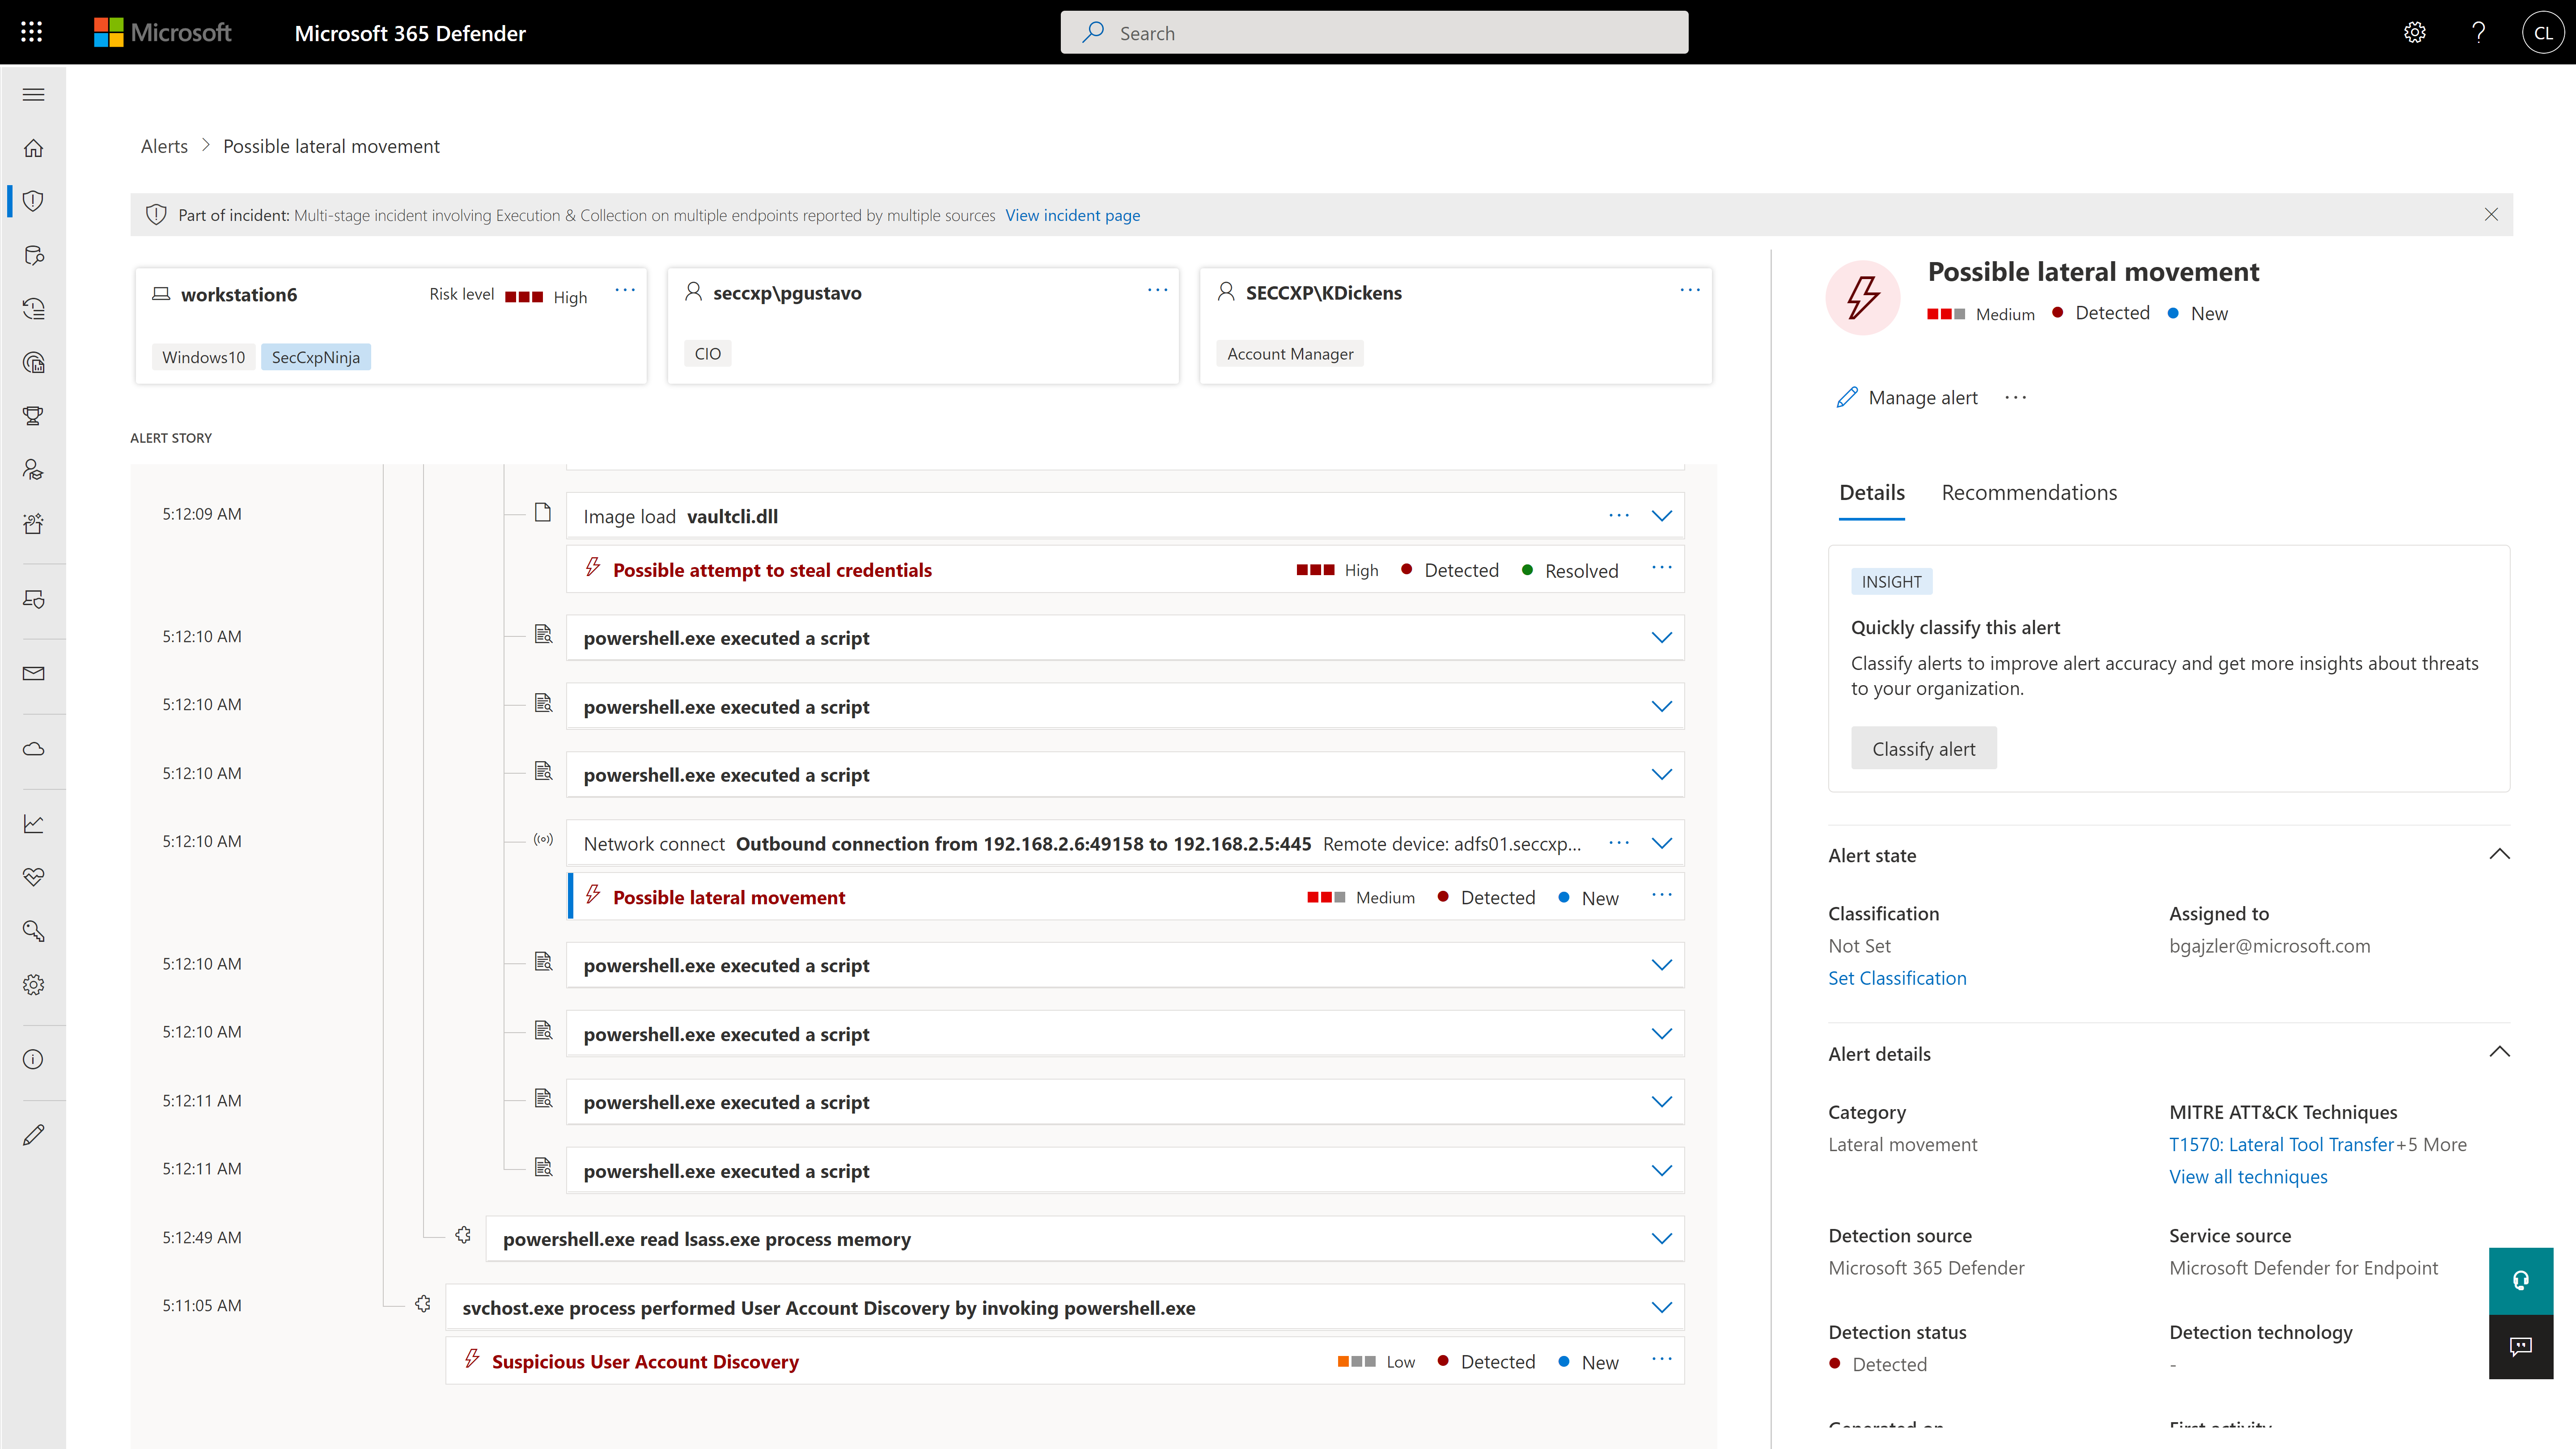
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Pricing
Malwarebytes
Microsoft Defender for Endpoint
Editions & Modules
Teams - Sole proprietor
$119.99
per year 3 devices
Teams - Boutique business
$399.99
per year 10 devices
Teams - Small office
$799.99
per year 20 devices
Academic
$2.50
per user/per month
Standalone
$5.20
per user/per month
Offerings
Pricing Offerings
Malwarebytes
Microsoft Defender for Endpoint
Free Trial
No
Yes
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
All plans include a 60-day money back guarantee. 1st year discount available for the Small office plan.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Malwarebytes
Proven to be one of the best in detecting malware that is otherwise undetected by other solutions. When a user gets hit by certain malware, many other tools do not even detect them as malware, while with Malwarebytes, you can rest assured that if it states that a computer is …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Malwarebytes
Have also used the following malware/spyware protection/removal tools: SuperAntiSpyware Spybot Search & Destroy
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Content writer and programmer in Information Technology at Ethical Hacking Online (Computer Software, 11-50 employees)
Chose Malwarebytes
It is also a very good option to consider as an antivirus system. But, it is not effective against the rootkits; that's why I selected Malwarebytes over it. Malware bytes has a more powerful and effective scanning mechanism than Norton. If I compare the free versions of the …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Now, I gave it that rating because it's a handy tool for diagnosing issues. Quarantining them, and most of the time, it does fix the problem. Though with rootkits, it's been hit or miss, and sometimes perfectly valid software gets flagged erroneously. However, once you've run it, it tends to run continuously, consuming far too many resources and being a real pain to uninstall, sometimes even causing issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Low system resources, it does not slow down the whole computer when scanning or when real-time protection is enabled
Quick and frequent updates, usually people hate updating, but for malware/viruses, you want to be updated as possible. It takes less than 15 seconds and usually does it automatically. They usually send a few updates a day as they find more.
Protection features actually work when visiting known bad websites. The page will be blocked and nothing will be downloaded. It may not be what the user wants, but it's what the user needs (as the user can't know every bad website)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One of the main things that malwarebytes is missing as a company, is phone support for its clients. All support questions has to go thru email only. This is not acceptable for issues that needs to be resolved quickly.
There is an issue when installing the client on a machine, it has a set amount of time where the software can register with the management server. The issue with this is, with machines that are over a wide area network, slow connection speeds can cause the software not to register. When that happens, it never re attempts to register in the future.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The last time we renewed Malwarebytes, we renewed for a 3 year renewal. That should describe the confidence we have in the product. Plus the cost savings impact year after year.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Usability-wise, it's pretty good, and it gets the job done. But once that's finished, the nags, the pop-ups, and the fact that it slows older systems down recklessly really cost it rating points. It becomes a clutter, and one of the first things we check when we receive reports that a PC is slow is whether it's running malware. Once we uninstall it, the PC is usually easily 40-50% faster. That's too much in the way of resources for something that wants to always run in the background.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The Malwarebytes customer support team is awesome! They really go above and beyond to help you with whatever issue you may experience. It is not that we need to contact their support team often, but the few times we did, we would speak to someone who knew what they were talking about and able to solve our problem. It is a comfort knowing that aside from a great product, you are getting a reliable support structure.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Avast and Norton's products were part of the testing for us but the cost was very high for them and the products were not light on the machine. They took up a lot of memory and slowed the computers down. Malwarebytes although may lack some feature, is a very light software.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive Impact: Have not had to remediate malware/virus infections since installed.
Positive impact: As far as browsing goes, we can boldly go where no man has gone before. No, really, I am confident when I am clicking on search engine results that if something get past my trained eye, Malwarebytes will pick of the slack.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info