Microsoft 365 Defender combines SIEM and XDR capabilities for Microsoft 365 environments, encompassing threat detection, post-breach detection, automated investigation, and response for endpoints. Additionally, it protects cloud apps, emails and documents, and employee identities.
N/A
Sophos Intercept X
Score8.9 out of 10
N/A
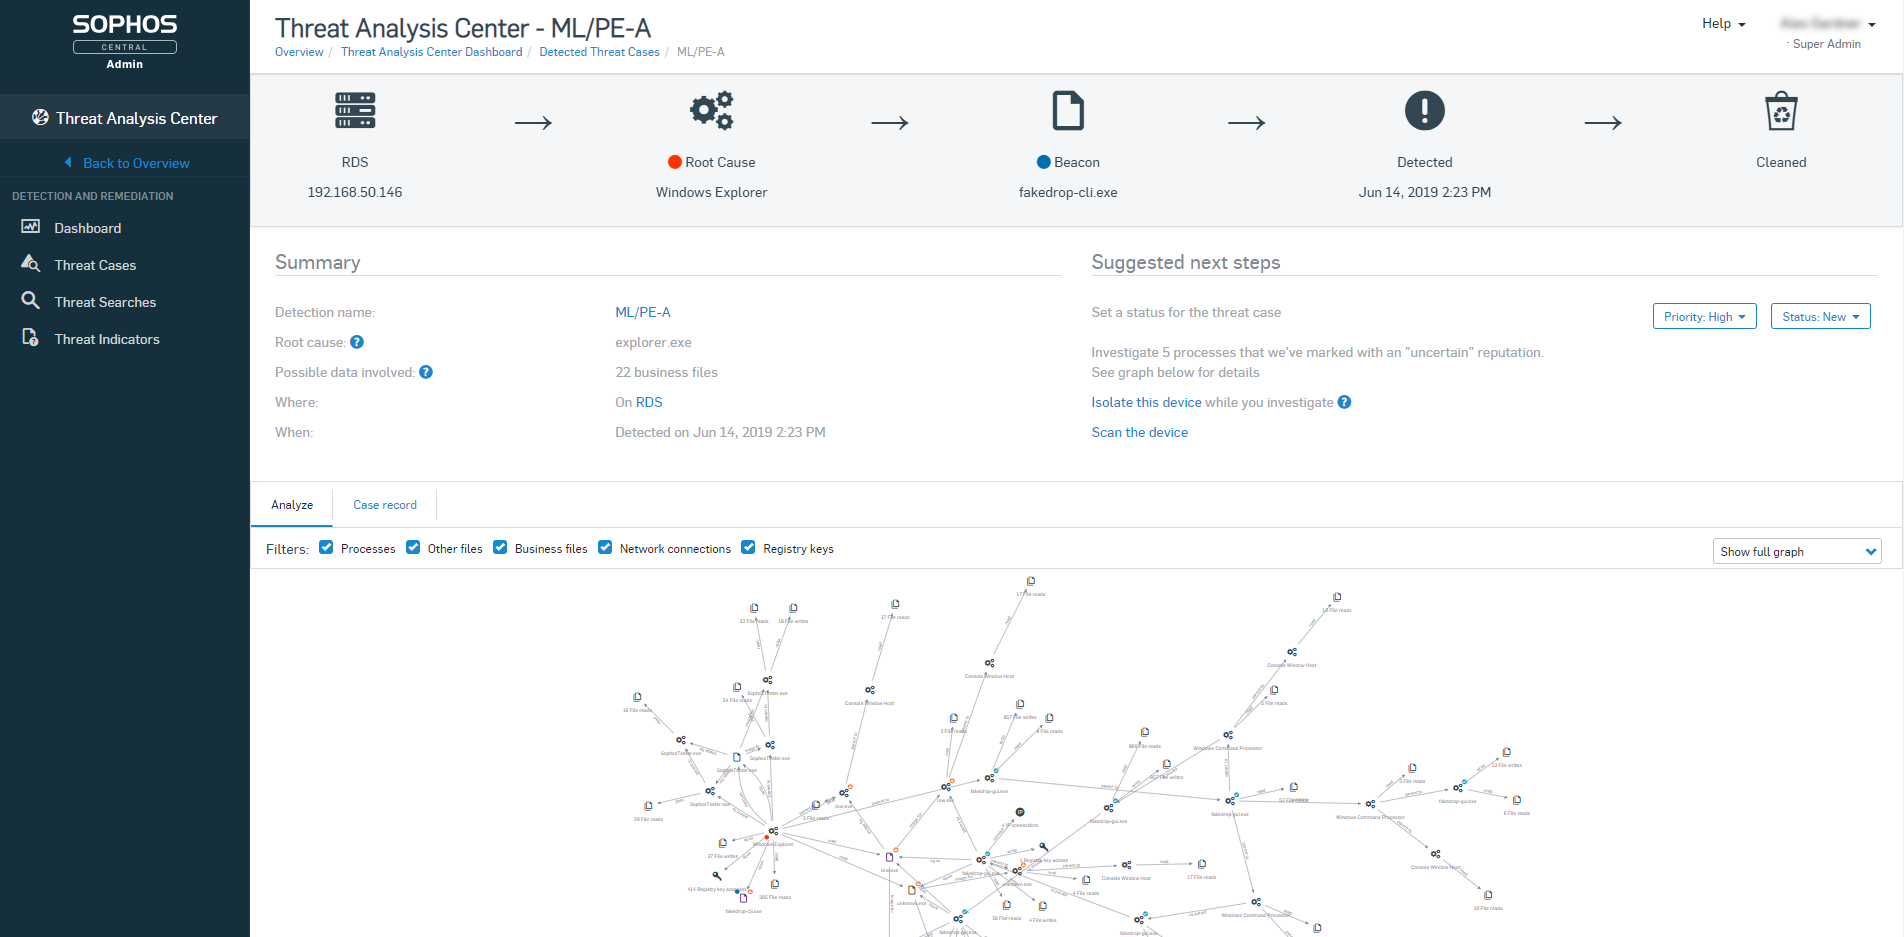
Sophos Endpoint Protection (Sophos EPP) with Intercept X is an endpoint security product providing an antivirus / antimalware solution that when upgraded with Intercept X or Intercept X Advanced provides advanced threat detection and EDR capabilities.
$28
per year per user
Pricing
Microsoft Defender XDR
Sophos Intercept X
Editions & Modules
No answers on this topic
Intercept X Advanced
$28
per year per user
Intercept X Advanced with XDR
$48
per year per user
Sophos Managed Threat Response
$79
per year per user
Offerings
Pricing Offerings
Microsoft Defender XDR
Sophos Intercept X
Free Trial
Yes
No
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
—
Pricing is for a 3-year commitment. Government and Education pricing available.
Microsoft Defender XDR is more seamless than Sophos Intercept X as it is better integrated into the Microsoft 365 suite. Sophos Intercept X is a little bit cheaper per year than Microsoft Defender XDR though, and definitely worth looking into if you are looking for a security …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender XDR
It provides additional protection and also integrates better with other Microsoft programs and operating systems.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender XDR
We use Microsoft products and have a large group of users. It works easily with our system. There is a great deal of knowledge base out there, often a little overwhelming. But we feel it's the best tool for our network to use parallel to the rest of our back-end.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Network Engineer in Information Technology at National Aviation Services (Aviation & Aerospace, 1001-5000 employees)
Chose Microsoft Defender XDR
We selected the Microsoft 365 Defender as we using Microsoft environment and integration with Microsoft 365 Services. Also its provide single dashboard from where we can manage and monitor security across different services, Which streamlines our security operations and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender XDR
We've compared the solution to probably 5-10 others having selected just a handful of the more recent ones. Using this with one other, we feel like we've covered most areas as possible. The integration with the Microsoft stack cannot be beaten and it just feels natural to use …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender XDR
We liked the deep device integration and active threat monitoring for Sophos but ultimately we went with Microsoft 365 Defender integrated into our Microsoft 365 tenant because we could negotiate favorable pricing along with our 365 licensing. The additional expense of Sophos …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
In our experience, Microsoft Defender XDR has been fantastic for phishing and account compromise scenarios, Endpoint Security, Automated threat detection and response and just generally giving a great overview through their dashboard, meaning the IT team doesn't need to switch between multiple tools to understand the full scope of an incident. In mostly remote organization like ours, it really helps to keep on top of any potential threats that we don't have the opportunity to spot in person. While it works great for us in a mostly Microsoft 365 environment, I can see how it would be less appropriate in an organization that is less integrated in the Microsoft ecosystem or uses a large number of third party tools.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
To be frank, this product is fairly expensive. So I would recommend this to companies that are mid-sized or larger to condone the cost of the purchase. It does save me a significant amount of time in my day - being able to glance at the dashboard and see if there are any outstanding issues that require my attention, as not much digging must be done to accomplish this. So for our company, with a short-staffed IT department, it's incredibly helpful to us. We also qualify for Educational pricing which brings the cost down - which helps tremendously
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One of the greatest strength of Microsoft Defender XDR has the ability to convey alert and signal in the closing point, email, identity and cloud applications in an event. Instead of obtaining isolated alert from each tool, Microsoft Defender XDR consolidates them in a full attack story, which helps the security teams to understand the scope and impact of a danger very fast.
If a user clicks on the fishing link, Microsoft Defender XDR automatically can associate malicious emails with lateral movement efforts, suspected sine-in, and endpoint activity-to protect against hours of manual probes.
The defender uses AI-powered automation for investigating and treatment of Microsoft Defender XDR events. It can separate the infected closing points, can cancel the compromised tokens, or remove malicious email - without the need for human intervention.
When malware is detected on a device, the defender can separate the device, kill malicious processes, and automatically flag the same files throughout the environment, which can spread.
Because it is integrated deeply with Microsoft 365 defender, Entra ID (Azure Ad), Intune, and PurView, the defender provides native safety in the XDR Microsoft Stack. It simplifies deployment and maintenance, offering deep visibility in user activity and cloud data.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sophos Intercept X is great at preventing malware infections and rolling back their effects. I have seen this happen hundreds of times since we installed it
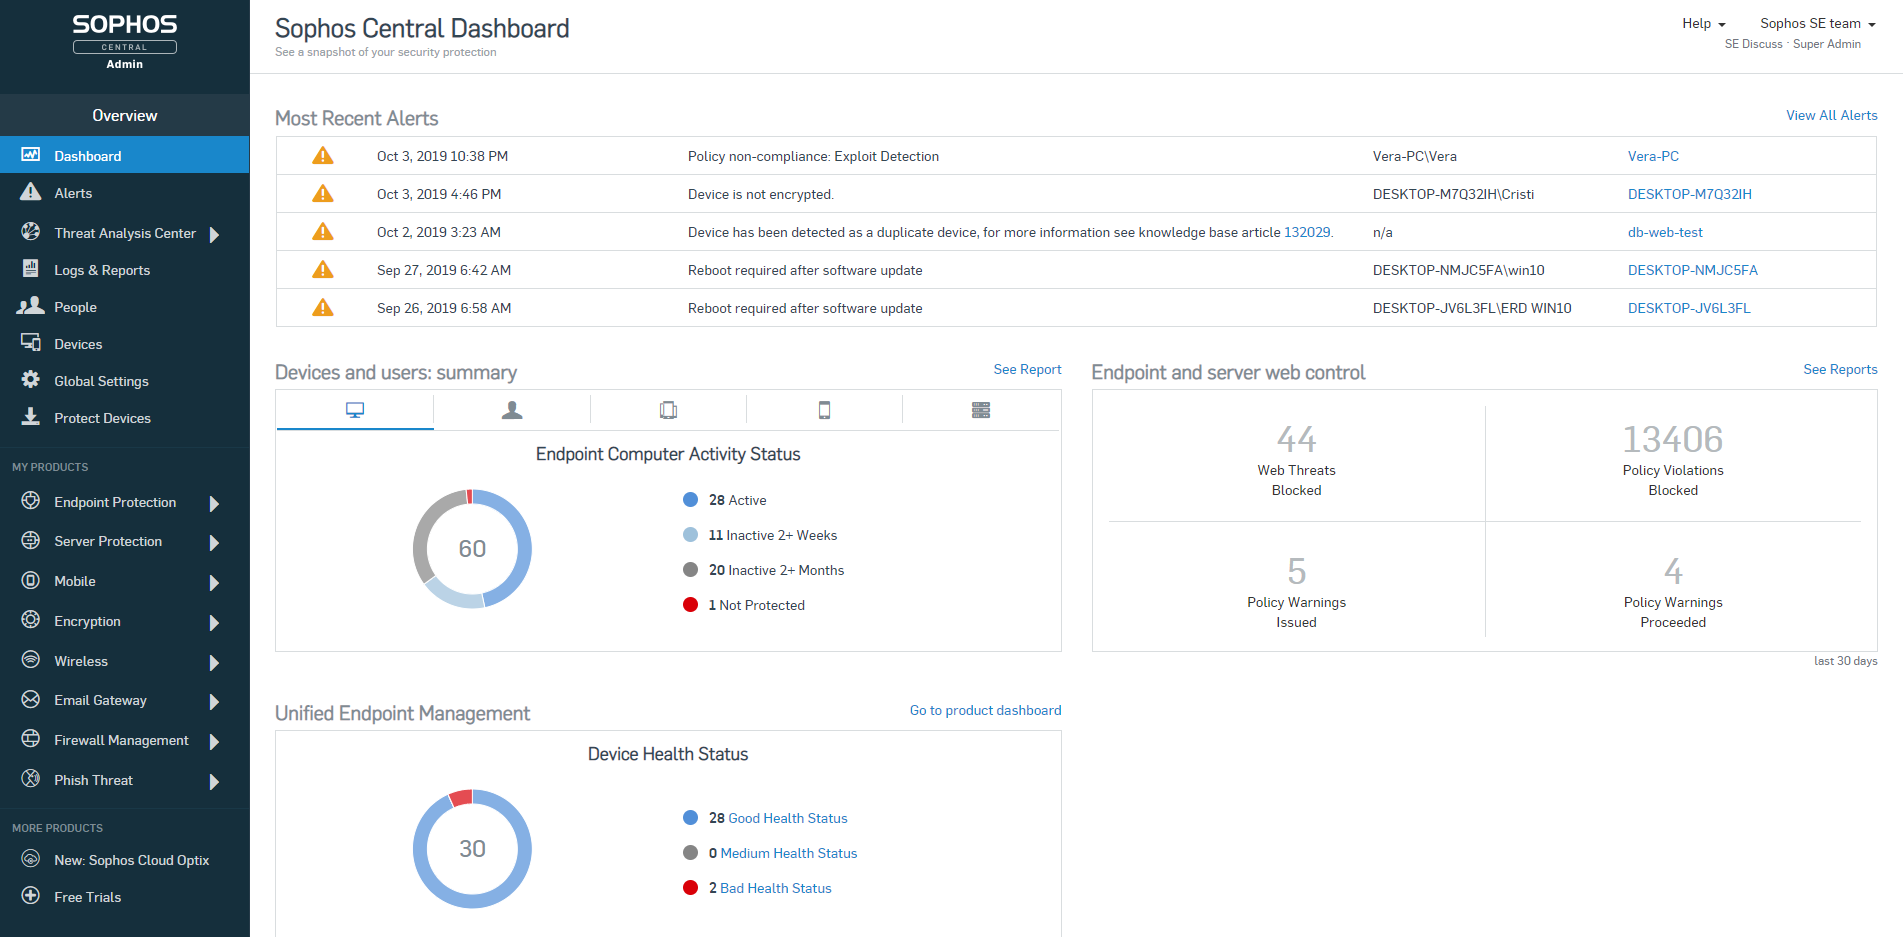
When combined with Sophos Central, you have an easy to use dashboard where you can manage all installations from a single pane of glass.
It's easy to deploy on machines and stays updated.
Good reporting features including alerts sent to the admin if there's ever something wrong with it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Improved algorithms to minimize false positives in threat detection, reducing the impact on security teams and preventing unnecessary investigations into non-threatening incidents.
Advanced User-Friendly Interface:
Streamlined and intuitive user interface for the centralized dashboard, making it more accessible for security professionals with varying levels of expertise.
Greater Third-Party Integration:
Increased compatibility and integration capabilities with a broader range of third-party security tools
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sophos OOTB policies are very strict and they don't offer anything less strict without you creating new custom policies. I'm sure this is deliberate because the product starts you out in the safest way possible but it means that you will have lots of calls to your tech support desk when you first deploy it unless you do somewhat extensive testing beforehand.
Sophos Intercept X is currently broken (at least the DLP component) by having secure boot turned on in the UEFI/BIOS. If any user wants to be able to write data to a USB drive or floppy from their PC (yes we still have a couple users who need to use floppies) we have to turn off secure boot on their PC, even if the DLP policy for that user/PC combination specifies that the user and PC are allowed to write to USB/floppy. This would be a very serious problem if it weren't for the fact that we have very few users who need to write files to USB. For us it's OK but I bet it would be a deal-breaker for others.
I don't see a whole lot of evidence that Intercept X is any different than any other anti-virus, so maybe their admin alerts just don't clearly identify when they have identified a zero-day threat or maybe we just haven't had any zero-day threats.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We are pleased with the product and have no plans to look for alternatives. We are deeply invested in Microsoft ecosystem and Defender XDR provides seamless integration to other Microsoft products. For academic institution pricing is also quite affordable. In the contrary, we hope to extend the scope of the product for our entire environment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Once configured, it's very usable for any security team or IT Analyst. It'll give you everything you need to know in a single consolidated dashboard, and while you can certainly dive deeper with a very feature rich platform, generally it's very usable. I gave it an 8 as some of the advanced features do have a very strong learning curve, while routine tasks are quite straightforward, some of the features such as threat hunting, custom detections and automated response workflows do have a bit of a learning curve and will require some research and experience to get to grips with
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The usability has never been a problem. Sophos Intercept X is a program you can install and let protect your company without much intervention. Apart from a few policies, Sophos will keep you protected better than most any product on the market. Sophos Intercept X works quite well when you are looking to "tighten your grip" on user's access to websites, programs, and add-ons.
In our experience there has been very little downtime for Microsot Defender XDR. For us there hasn’t been any single incident where we needed the product and it was not available.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Most of the time the product is as responsive as you might expect from cloud product. Occasionly the product is little slugish, this has been at most a slight irritation. Reports generate quickly ennough for our needs. We also not have found that Defender XDR slows down systems that it is integrated with
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Their support throughout our onboarding of the product was fabulous. They not only took the time to carefully explain to teams not as well equipped with the lingo but explained to the tech team how to teach the other teams to be successful. They never once seemed impatient or annoyed with basic questions and didn’t pretend to know something when they needed to research an answer
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Most of the support reps are fantastic. There have been a few though that have had to be escalated via Account Manager when they haven't followed up but this is a rare instance, and often followed up by the Support Manager for APAC.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Provides a good training for the Microsoft 365 Defender and has a good learning paths to learn and take the exams and get your Certifications.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
seemless and almost transparent. can be deployed by script if needed so every endpoint on our system get's it. if you have intune it gets dumped on the the endpoint by policy so nothing escapes it
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Our product in that area, for instance as a security platform and for us it is for the moment really bad point. We started to move in that direction that there is that disconnect from the client management. So if there is some action that needs to be executed detected by security team, there is not an easy way to make that available to the team that is responsible for managing the identities as users, as the devices
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Webroot Endpoint Protection is not even in the same league as Sophos Intercept-X. I have tested and compared both sides by side, run simulations and it's not even close. Plus the Sophos central management is so much better. Easier to view user activities and apply policies and remediate threats. Sophos is the clear winner between these two products.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Azure cloud provides techical power to scale the product for whole organization. From organizational point of view scaling Defender XDR for various IT teams needs good collaboration and clear norms that all teams must agree to and follow.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Once our technical and commercial areas got certified, the ROI over the time spent, is great. Actual customers, and/or new ones with other tools, feel safe and advised, once they get in touch with us.
When Sophos EndPoint is being compared against Web Management Tools (competitors), we have failed to deliver, nevertheless, there is a version of Sophos Central (Cloud) which achieves this requirement at 100% and more, since is Cloud Based (on AWS).
We are grateful to be on Sophos "Radar" as a Platinum Partner, and "The Americas" valued partner, we have seen our business grow, thanks to this kind of technology, throughout the years.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info